
 Do Son
CVE-2022-22630 (CVSS score 8.1), exists in the Apple Remote Events results from the lack of proper validation of user-supplied data
Vulnerability
CVE-2022-2856, was submitted by Ashley Shen and Christian Resell. Google is aware that an exploit for CVE-2022-2856 exists in the wild
CVE-2022-28756 affects the Zoom Client for Meetings for macOS can be could be exploited to gain root access in macOS.
Apple warned that a threat actor can exploit the CVE-2022-32787 flaw to execute arbitrary code and urges users to install patches immediately

security personnel discovered a vulnerability called "SQUIP", which will threaten the security of AMD Zen series architecture processors

an attacker could exploit CVE-2022-34713 by sending the specially crafted file to the user and convincing the user to open the file.

CVE-2022-2586 allows a local, privileged attacker to cause a use-after-free problem at the time of table deletion, possibly leading to LPE
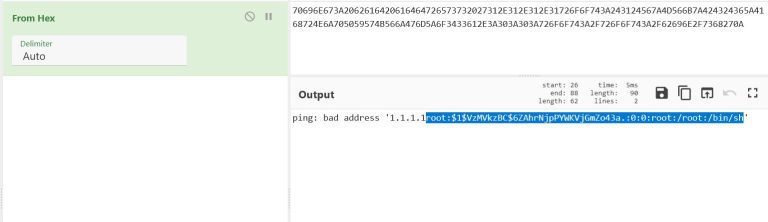
if successfully exploited, CVE-2022-36267 could lead to full compromise of the devices and unauthorized access to the broader network
Tracked as CVE-2022-2590, the vulnerability allows a local, unprivileged attacker to gain write access to read-only memory mappings
The flaw tracked as CVE-2022-37452, classified as critical, is a heap-based buffer overflow for the alias list in host_name_lookup

Track as CVE-2022-35924, the flaw is an authentication bypass bug with a CVSS score of 9.1. Rated as critical severity

an attacker could exploit this vulnerability to inject arbitrary commands and thus achieve remote code execution. Track as CVE-2022-25168

Rsync developers informed users recently that all versions of Rsync prior to 3.2.5 was affected by the CVE-2022-29154 vulnerability
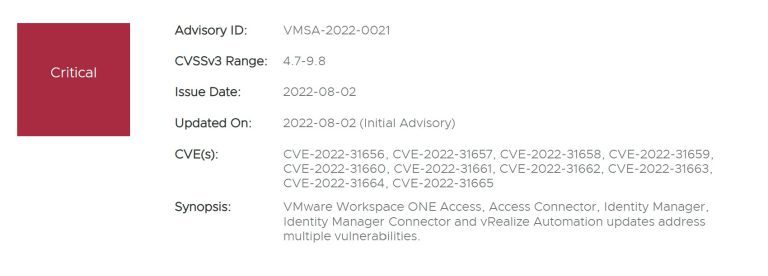
Tracked as CVE-2022-31656 (CVSS scores: 9.8), the issues impact VMware Workspace ONE Access, Identity Manager, and vRealize Automation
The bug tracked as CVE-2022-35918 can be exploited by an attacker to grant data from web servers file systems such as server logs

A high EnterpriseDT CompleteFTP vulnerability (CVE-2022-2560) just goes public today by the Zero Day Initiative (ZDI) website.

Linux kernel is affected by potentially serious vulnerability (CVE-2022-36946) that can be exploited by a remote attacker to DoS attacks

Samba developers informed users this week that all versions of Samba prior to 4.16.4 was affected by CVE-2022-32744 vulnerability
A security researcher has discovered that the Linux kernel is affected by a potentially serious vulnerability (CVE-2022-36123)
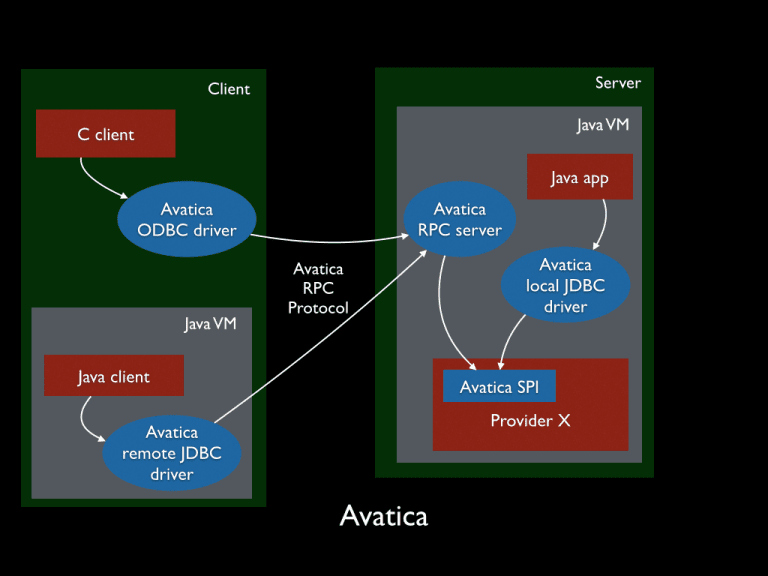
Apache Calcite Avatica released the latest security bulletin on July 28, which contains a RCE vulnerability (CVE-2022-36364)
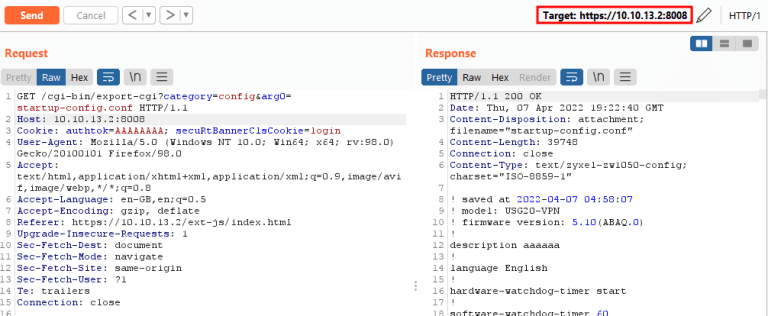
Recently, security researcher Maurizio Agazzini from HN Security shared the CVE-2022-0342 PoC with the detailed technique

CVE-2022-36408 which could be exploited remotely is the result of a lack of proper validation of user-supplied input in SQL queries