
 Do Son
Google rolled out patches for the Chrome browser for desktops to contain an actively exploited high-severity zero-day flaw (CVE-2022-3075)
Vulnerability
iOS 12.5.6 is a version that fixes a security vulnerability. This version fixes the high-risk vulnerability of CVE-2022-32893
CVE-2022-37021 is the "deserialization of untrusted data flaw when using JMX over RMI on Java 8," and affects Apache Geode versions

Tracked as CVE-2022-2992 (CVSS 9.9/10 severity), the security flaw can be exploited via the Import from GitHub API endpoint

Linux kernel is affected by a potentially serious flaw (CVE-2022-2961) that can be exploited by attackers to grant elevated privileges
By sending a specially crafted request, an attacker could exploit the CVE-2022-25625 flaw to gain elevated privileges on the affected system.
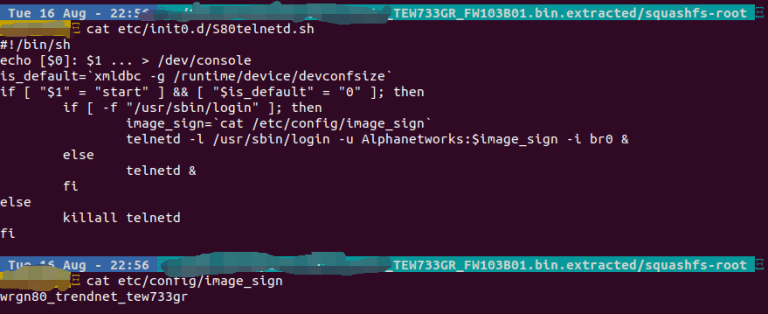
CVE-2022-38556 can allow an unauthenticated, remote attacker to take full control of the device to take control vulnerable devices
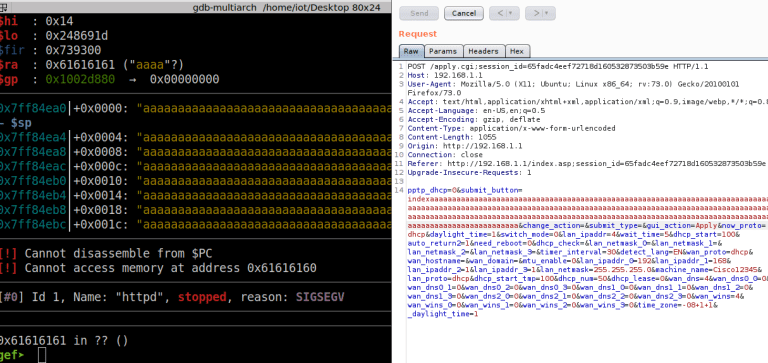
The buffer overflow security vulnerability, tracked as CVE-2022-38555, is related to the ej_get_web_page_name function
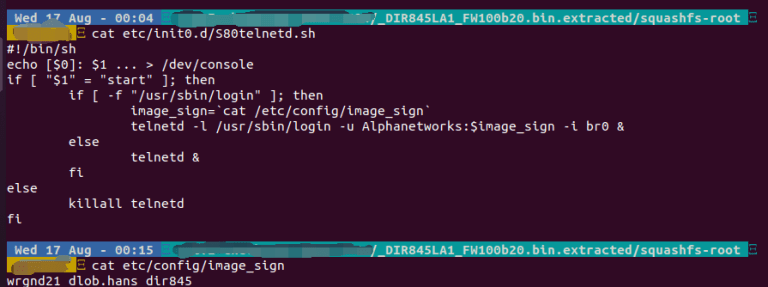
CVE-2022-38557 credential flaw exists in the Telnet service of D-Link DAP1522. The expert has published detailed technical information

an attacker could exploit this vulnerability to execute arbitrary commands as a YARN user on the system, track as CVE-2021-25642

CVE-2022-36804 affects Bitbucket Server and Data Center, allows attackers can execute arbitrary code by sending a malicious HTTP request
Cisco has addressed a high severity privilege escalation vulnerability (CVE-2022-20921) found in the API implementation of the Cisco MSO

@Enesdex found a privilege escalation flaw (CVE-2022-2959) in the Linux kernel that can be exploited by attackers for privilege escalation

Discovery Protocol is enabled by default globally and on all interfaces in FXOS and NX-OS, CVE-2022-20824 impacts numerous products

CVE-2021-36260 is a command injection vulnerability in the web server of some Hikvision products, due to the insufficient input validation
CVE-2022-38477 is a high-severity memory safety bugs within the browser engine, which could have been exploited to run arbitrary code
GitLab issued a security notice to fix a flaw (CVE-2022-2884) in the Community Edition and Enterprise Edition, with a CVSS score of 9.9.
Apache Flume released the latest security bulletin on August 21, which contains a remote code execution vulnerability (CVE-2022-34916)
Derek Abdine, a security researcher, disclosed multiple vulnerabilities in Arris routers, the most critical being CVE-2022-31793.
To exploit the CVE-2022-38392 bug first, the target device must meet the trigger conditions, and second, the attacker must also play an unfiltered song
Apache ActiveMQ Artemis released the latest security bulletin on August 18, which contains an HTML injection vulnerability (CVE-2022-35278)

An out-of-bounds write issue (CVE-2022-32893) in WebKit allows hackers to execute arbitrary code and this vulnerability is being exploited