
 Do Son
CVE-2022-3210 vulnerability affects the D-Link DIR-2150 hardware revision R with firmware version v4.01 & below
Vulnerability

Security researcher released CVE-2022-37706 PoC exploit code and write-up for privilege escalation flaw in Enlightenment Desktop for Linux
CVE-2022-40283 impacts dozens of devices in the various models, including Lenovo L14 Gen 2, Lenovo L15 Gen 2, Lenovo P1 Gen 4,
78researchlab released CVE-2022-34721 PoC exploit code for critical remote code execution vulnerability affecting multiple Windows versions.

Tracked as CVE-2022-40137 and affecting Lenovo Desktop, Desktop AIO, Smart Edge, Smart Office, ThinkStation, and ThinkSystem models
CVSS score: 9.8, CVE-2022-3180 allows unauthenticated attackers to add a malicious user with admin privileges to completely take over sites.
By sending a specially crafted request, an attacker could exploit the CVE-2022-37969 vulnerability to gain elevated privileges.

an attacker could exploit the CVE-2022-32917 vulnerability to execute arbitrary code with kernel privileges.

Apache Calcite released the latest security bulletin on September 11, which contains an XML External Entity (XEE) vulnerability (CVE-2022-39135)

an attacker could exploit the CVE-2022-2964 vulnerability to execute arbitrary code or cause a denial of service condition on the system
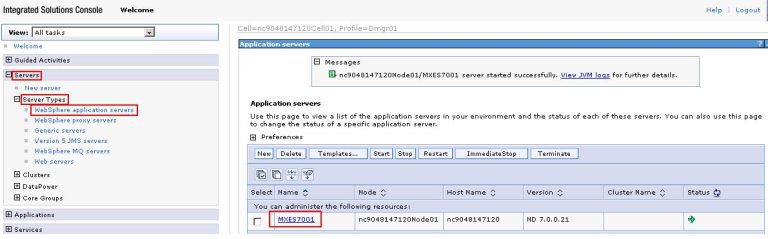
The security hole that allows HTTP header injection is tracked as CVE-2022-34165, and this is "caused by improper validation."
CVE-2022-31474 allows an attacker to view the contents of any file on your server that can be read by your WordPress installation

CISA this week added 12 new actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog
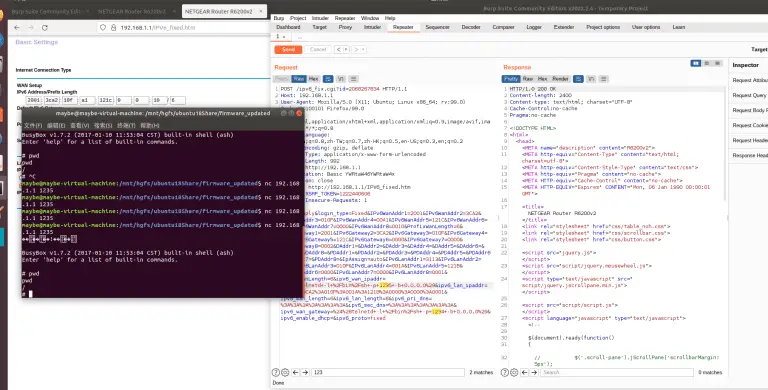
Traced as CVE-2022-30078, the security weakness impacts the Netgear R6200_v2 and R6300v2 routers with the latest firmware

CVE-2022-20923 affects Cisco Small Business RV110W, RV130, RV130W, RV215W Routers and it can be exploited by remote, unauthenticated attacker
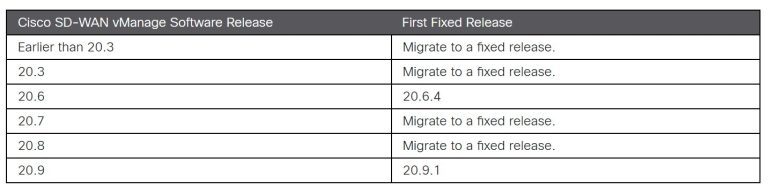
The CVE-2022-20696 hole can impact several Cisco products if they are running a Cisco SD-WAN vManage Software prior to 20.9.1.
CVE-2022-26447 allows a remote attacker to execute arbitrary code on the system, caused by an out-of-bounds write
CVE-2022-34747 could allow an attacker to achieve unauthorized remote code execution via a crafted UDP packet
Researchers recently disclosed clipboard security issues found in major browsers, including Chromium, Firefox, and Apple Safari

NodeBB announced two security advisories to reveal information on the underlying security vulnerability, CVE-2022-36076, and CVE-2022-36045

CVE-2022-25371, Apache OFBiz could allow a remote attacker to traverse directories on the system, caused by a flaw in the Birt viewer

CVE-2022-38054 affects Apache Airflow versions 2.2.4 through 2.3.3. Apache Airflow could allow a remote attacker to hijack a user's session