
 Do Son
Discover the Cisco Webex vulnerability impacting user credentials in Release 45.2 and how to protect your data effectively.
Vulnerability

Learn about CVE-2025-27507 vulnerabilities in ZITADEL's Admin API that could compromise user accounts and settings.

Learn about CVE-2025-1080 and its impact on LibreOffice security. Find out how to protect your system from vulnerabilities.

Learn about CVE-2025-1393 and its critical security implications for the PROCON-WIN industrial tool. Protect your systems!
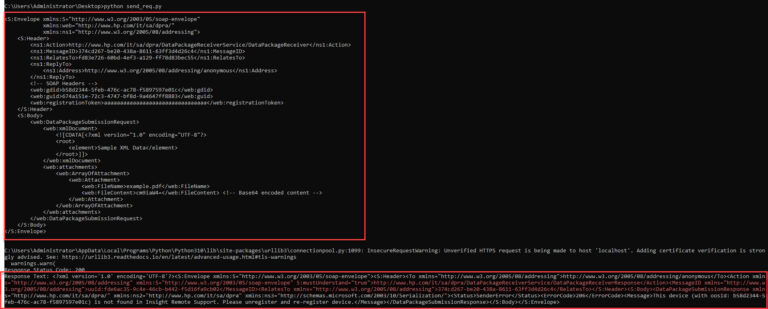
Explore CVE-2024-53676 PoC and its implications for HPE Insight Remote Support security vulnerabilities and remote code execution risks.

CVE-2025-1723 poses a significant risk for Zoho ADSelfService Plus users. Discover how to secure your data and avoid account takeover.

Explore CVE-2025-27423, a Vim vulnerability that allows arbitrary code execution. Learn how to protect your systems.

Learn about CVE-2024-0114, a high-severity vulnerability in Nvidia's Hopper HGX, risking code execution and privilege escalation.

Discover how CVE-2025-1914 impacts Google Chrome and the urgent security patches included in the latest Chrome 134 update.

Learn about CVE-2025-0912, a severe security vulnerability in GiveWP affecting over 100,000 WordPress sites.

These flaws—CVE-2025-22224, CVE-2025-22225, and CVE-2025-22226—pose serious security risks, with some already being exploited in the wild

The bulletin confirms that CVE-2024-43093 and CVE-2024-50302 have been under limited, targeted exploitation.

CVE-2025-0364 is a critical RCE vulnerability in BigAntSoft Server. Learn how it allows unauthenticated privilege escalation.

Learn about CVE-2025-0159, a critical vulnerability in IBM Storage Virtualize products that allows authentication bypass.
CISA has issued an urgent warning for federal agencies to mitigate flaws being actively exploited in Cisco routers, Windows systems, and Hitachi and Progress WhatsUp Gold software

These flaws, identified as CVE-2025-23388 and CVE-2025-23389, could allow attackers to launch denial-of-service (DoS) attacks and impersonate users

Explore CVE-2025-0289 vulnerabilities in Paragon Partition Manager and their impact on ransomware attacks targeting privilege escalation.
Explore Qualcomm's March 2025 Security Bulletin addressing critical vulnerabilities in automotive systems and mobile chipsets.

Three vulnerabilities are flagged with a High severity rating: CVE-2025-20644, CVE-2025-20645, and CVE-2025-20646.

Explore the CVE-2025-21333 PoC exploit revealing a zero-day vulnerability in Windows Hyper-V that allows SYSTEM privilege escalation.

Explore CVE-2025-27154 and its implications for Spotipy users. Learn how the vulnerability affects authentication security.

Extreme Networks has recently released security advisories to address three critical vulnerabilities affecting its IQ Engine (HiveOS) product line.