
 Do Son
Urgent security update: Apple patches zero-day vulnerability (CVE-2025-24200) actively exploited in targeted attacks.
Vulnerability
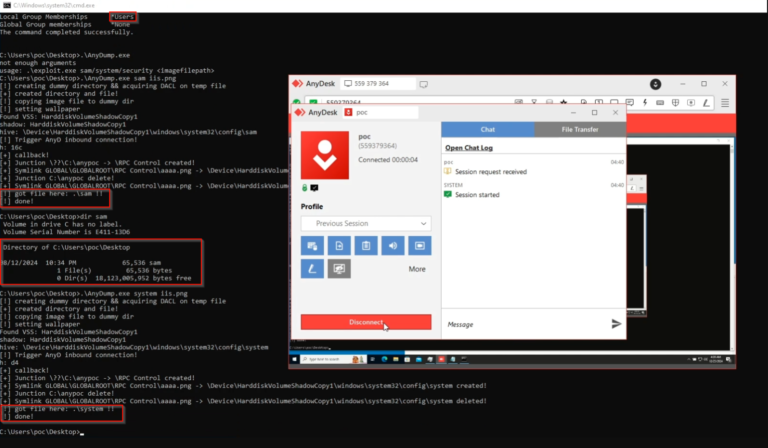
Discover the security flaw, CVE-2024-12754, found in AnyDesk. Find out how this vulnerability could grant unauthorized access and complete control of a system.

Protect your business from Zimbra Collaboration vulnerabilities. Learn about the recently discovered CVE-2025-25064 SQL injection vulnerability and its potential impact.

Critical vulnerabilities in Elber communications equipment: Learn about the urgent warning from CISA and the potential risks of CVE-2025-0674 and CVE-2025-0675.

Field Effect reveals a cyberattack that used newly discovered SimpleHelp RMM software vulnerabilities to deploy the Sliver backdoor and establish persistence mechanisms.

Discover the critical path traversal vulnerability (CVE-2024-48510) in ABB Drive Composer software. Find out the potential consequences and security risks.
Discover the CVE-2025-0896 flaw in Orthanc, a popular DICOM server, which could allow unauthorized access to medical images and patient data.

Get insights into the cyber onslaught of Abyss Locker. Sygnia's report uncovers their calculated attacks and the methods they use to cripple organizations.

Critical security vulnerabilities discovered in WhoDB - CVE-2025-24786 (CVSS 10.0) and CVE-2025-24787 (CVSS 8.6). Protect your sensitive data and system files.
Stay informed about the critical hard-coded credentials vulnerability (CVE-2024-51547) in ABB's ASPECT Energy Management System and the potential risks it poses.

Learn about the recent vulnerabilities in IBM Security Verify Directory Server Container and the potential risks they pose. Find out how to mitigate CVE-2024-49814 and CVE-2024-51450.
Take action now to secure your systems from CVE-2025-0994, a critical deserialization vulnerability in Trimble's Cityworks software.

Uncover the severity of the CVE-2024-21413 exploit in Microsoft Outlook. Understand the implications and take necessary steps to secure your organization from possible cyber threats.
NETGEAR Patches Critical Security Vulnerabilities in WiFi Routers (CVE-2025-25246) and Access Points

NETGEAR Patches Critical Security Vulnerabilities in WiFi Routers (CVE-2025-25246) and Access Points
NETGEAR warns of security vulnerabilities in WiFi routers and access points. Take action to secure your devices from remote code execution and unauthorized access.
Critical vulnerabilities in Four-Faith F3x36 routers running v2.0.0 firmware. Learn about CVE-2024-9643 and CVE-2024-9644 and their severity.
Discover the vulnerabilities affecting the Apache James mail server. Learn about CVE-2024-45626 and CVE-2024-37358 and how they can lead to denial of service attacks.

Learn about the high-severity vulnerabilities in HPE Aruba Networking's ClearPass Policy Manager (CPPM) software, including CVE-2025-23058, and how to secure your network.
Learn about a critical security vulnerability (CVE-2025-24964) in Vitest. Discover how attackers can execute arbitrary code through a Cross-site WebSocket Hijacking issue.

Explore the benefits of running Arch Linux on Windows Subsystem for Linux (WSL2) and how it provides seamless access to the latest updates.

Discover CVE-2025-20124 and CVE-2025-20125 in Cisco's Identity Services Engine (ISE) and learn how to protect your network from potential attacks.

Understanding the latest security advisory from F5. Learn about CVE-2025-23419 and how it could potentially allow unauthorized access to sensitive resources in NGINX.
Discover the evolving threat of XE Group: from credit card skimming to zero-day vulnerabilities, this notorious cybercriminal organization is targeting organizations across industries.