
 Do Son
CVE-2025-24479 and CVE-2025-24480 could potentially allow attackers to execute malicious code and compromise affected systems.
Vulnerability

Critical vulnerabilities discovered in Voyager, an open-source Laravel admin panel. Learn about the CVE-2024-55417 flaws and their impact on website security.

Learn about the critical out-of-bounds write vulnerability affecting Moxa PT switches (CVE-2024-7695) and the potential impact on industrial infrastructure operations.

To extract the victim's session, researchers release a Ruby proof-of-concept (PoC) exploit code for CVE-2024-53704 , which is available here.

Learn about the critical vulnerability affecting D-Link DSL-3788 router and how it can allow attackers to take complete control of affected devices.

Critical zero-day vulnerability on Zyxel CPE devices (CVE-2024-40891): Unauthenticated remote attackers can execute arbitrary commands. Stay protected!
Protect your data lake systems from potential security threats. Understand the impact of CVE-2024-23953 and CVE-2024-29869 on Apache Hive and take necessary precautions.

Critical vulnerabilities in BIND DNS software: CVE-2024-11187 and CVE-2024-12705. Understand the risks of denial-of-service attacks on DNS servers and resolvers.

Learn about the security risks in VMware Aria Operations and Logs. Discover the potential consequences and how to mitigate the threats.
Mitel SIP phones under active exploitation by Aquabotv3, a new variant of the Mirai-based botnet. Learn about the undisclosed vulnerability CVE-2024-41710.

Discover the security vulnerabilities in DeepSeek R1, a new AI model developed in China. Learn about its potential for misuse and implications for cybersecurity.

Uncover the latest Linux kernel vulnerabilities affecting eBPF framework with AF_XDP sockets. Learn about CVE-2024-56614 and CVE-2024-56615 and their potential security risks.

Find out about the high-severity vulnerabilities CVE-2024-12647, CVE-2024-12648, and CVE-2024-12649 in Canon Laser Printers and Small Office Multifunction Printers. Take action to secure your devices.

Discover the cybersecurity advisory addressing critical vulnerabilities in ABB FLXeon controllers, including CVE-2024-48841 for remote code execution.

Critical vulnerabilities discovered in Vaultwarden expose organizations to unauthorized access and privilege escalation. Learn more about CVE-2025-24364 and other security flaws.

Discover how Google's Agentic AI Security Team is combating prompt injection attacks on AI systems like Gemini with a new framework.
This vulnerability, identified as CVE-2025-22217 and given a CVSSv3 base score of 8.6, could allow attackers to gain unauthorized access to sensitive data
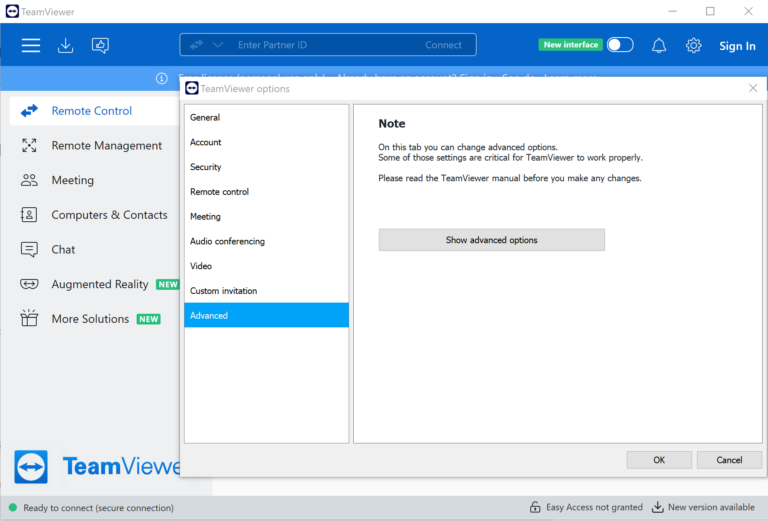
The vulnerability, tracked as CVE-2025-0065 and assigned a CVSS score of 7.8 (High), affects TeamViewer Clients for Windows prior to version 15.62.
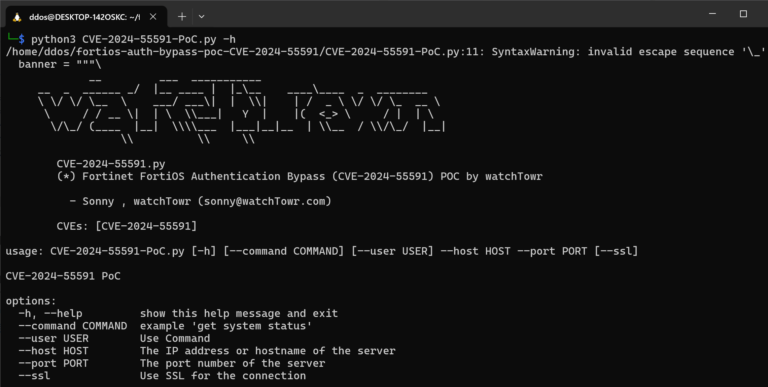
Learn about a 0day flaw in Fortinet's FortiOS and FortiProxy products. Explore the technical details and PoC exploit code for CVE-2024-55591
Stay informed about the critical vulnerability CVE-2025-22604 in Cacti network monitoring software. Learn how this flaw could allow code execution and compromise sensitive data.
Discover the severe threat of CVE-2025-22612, CVE-2025-22611, and CVE-2025-22609 in Coolify. Secure your servers, applications, and databases.
Authentication Bypass in Deepin D-Bus Proxy Service (CVE-2025-23222): A Critical Design Flaw Exposed

Authentication Bypass in Deepin D-Bus Proxy Service (CVE-2025-23222): A Critical Design Flaw Exposed
Find out how the authentication design flaw in Deepin desktop environment's dde-api-proxy service (CVE-2025-23222) enables local users to bypass authentication and execute unauthorized operations.