
 Do Son
Critical vulnerabilities in Contiki-NG: Researchers discover flaws that can crash devices or execute malicious code in popular IoT operating system.
Vulnerability

Urgent security updates released for Zabbix monitoring tool to address critical vulnerability (CVE-2024-42330) that could lead to code execution.

Learn about the critical SQL injection flaw (CVE-2024-42327) in Zabbix and its potential impact on monitoring data and system security.

Unveiling the Matrix DDoS campaign: Aqua Nautilus researchers reveal a new threat actor leveraging accessible tools to launch large-scale cyberattacks.

Learn about the new Elpaco ransomware variant and its sophisticated customization features. Discover how it exploits vulnerabilities and leverages legitimate software tools.

Urgent security bulletin: Critical vulnerabilities in HPE Insight Remote Support service (CVE-2024-53676). Stay protected from unauthorized access and remote code execution.

Stay secure with Jenkins: Learn about the latest security advisory addressing multiple vulnerabilities impacting Jenkins and its plugins.

Discover the resurgence of the XorBot botnet, a potent threat to IoT devices worldwide. Learn about its advanced anti-detection mechanisms and wide range of exploits.

Critical vulnerability in ProjectSend (CVE-2024-11680) actively exploited. Learn how to protect your instance from unauthorized access and potential abuse.

Stay informed about the high-severity vulnerability CVE-2024-0130 affecting NVIDIA's UFM products. Find out how the recent firmware update can help mitigate the risk.
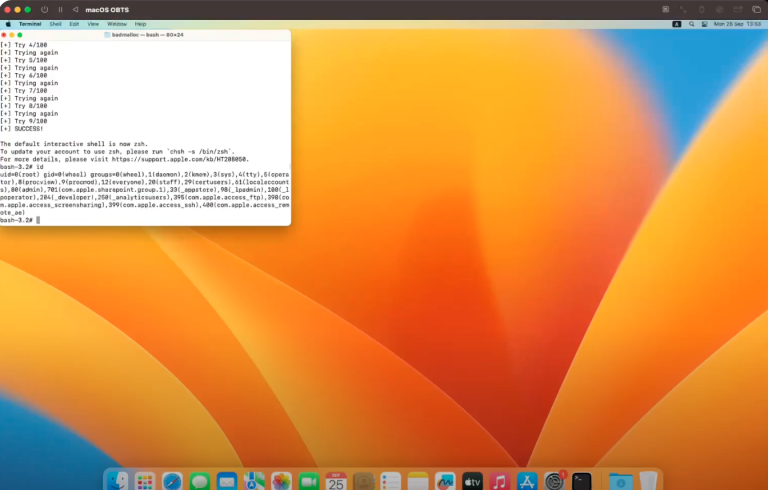
Learn about CVE-2023-32428, a high-severity vulnerability in Apple's MallocStackLogging framework that allows local privilege escalation on macOS systems.

Stay informed about the latest NTLM Privilege Escalation concerns. Discover the unpatched vulnerabilities and potential risks.

Protect your GitLab installations from critical vulnerabilities. Upgrade to the latest version to mitigate the risks of CVE-2024-8114 and other security issues.

Discover the important security updates for VMware Aria Operations. Patch your system to address vulnerabilities, including local privilege escalation and stored cross-site scripting (XSS).

Learn about the Earth Estries APT group, a significant cyber espionage actor targeting critical sectors and industries worldwide.

Stay informed about the critical vulnerability CVE-2024-41779 in IBM Engineering Systems Design Rhapsody - Model Manager (RMM) and learn how to protect your systems.
Stay informed about the latest Keycloak vulnerabilities and security updates. Learn about the risks and critical issues affecting the open-source IAM platform.

Stay protected from CVE-2024-5921 vulnerability in Palo Alto Networks' GlobalProtect app. Learn how attackers can exploit this issue and how to prevent it.

Learn about the critical vulnerabilities in PHP versions prior to 8.1.31, 8.2.26, and 8.3.14. CVE-2024-8932 enables attackers to execute arbitrary code.

Stay secure with QNAP's security advisory on critical vulnerabilities in Notes Station 3. Learn about the risks and how to protect your data.
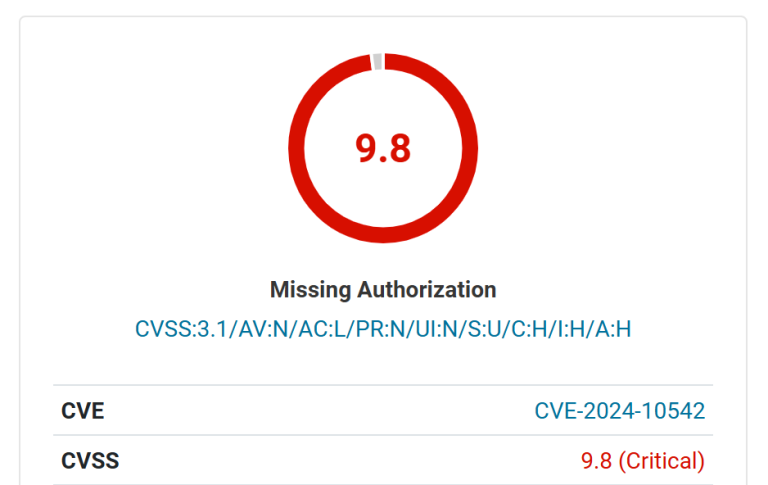
CVE-2024-10542 and CVE-2024-10781 could allow unauthenticated attackers to compromise websites by installing malicious plugins & executing arbitrary code

Discover the urgent threat posed by CVE-2023-28461, a critical security flaw in Array Networks AG and vxAG ArrayOS. Find out how to secure your devices now.