
 Do Son
Read our weekly threat intelligence briefing. Discover active exploits, critical CVEs, and the latest CISA KEV additions for May 18–24, 2026.
Weekly Recap
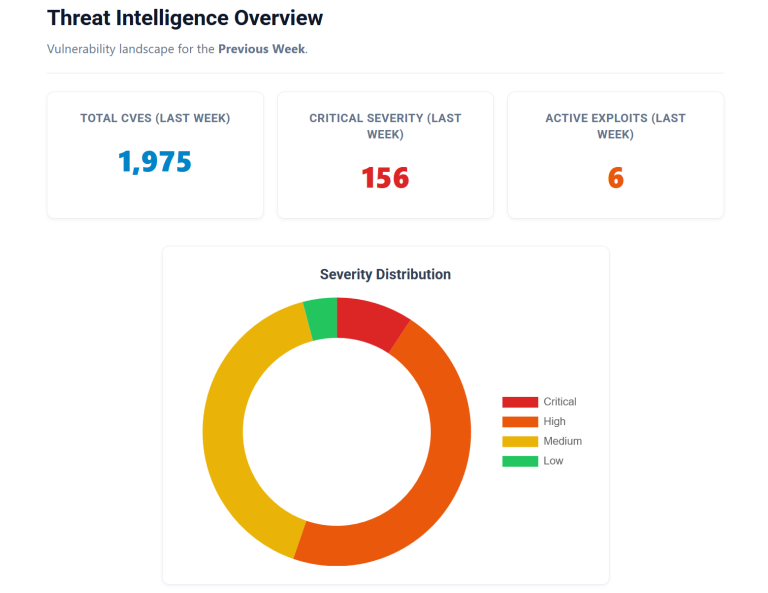
Cisco SD-WAN (CVE-2026-20182) and Exchange Server (CVE-2026-42897) are actively exploited in the wild! Discover the top threats you must patch now.
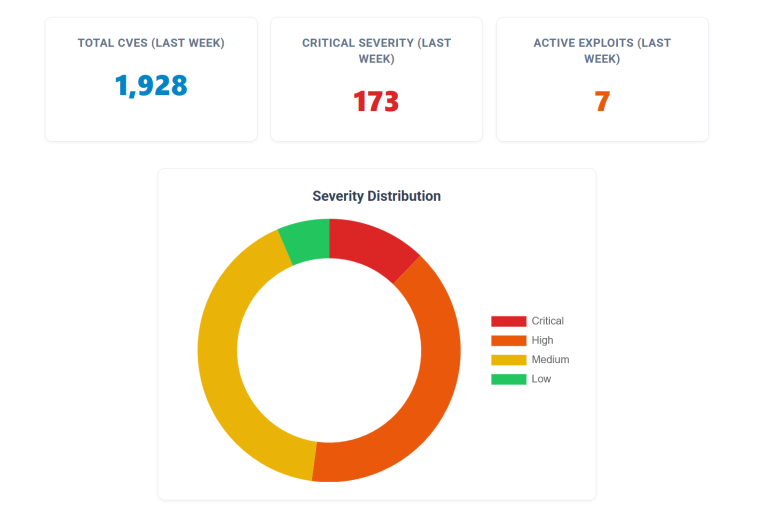
Weekly Security Digest: 1,928 new vulnerabilities hit the wire. From Palo Alto firewalls to LiteLLM AI gateways, here is how to prioritize your defense.
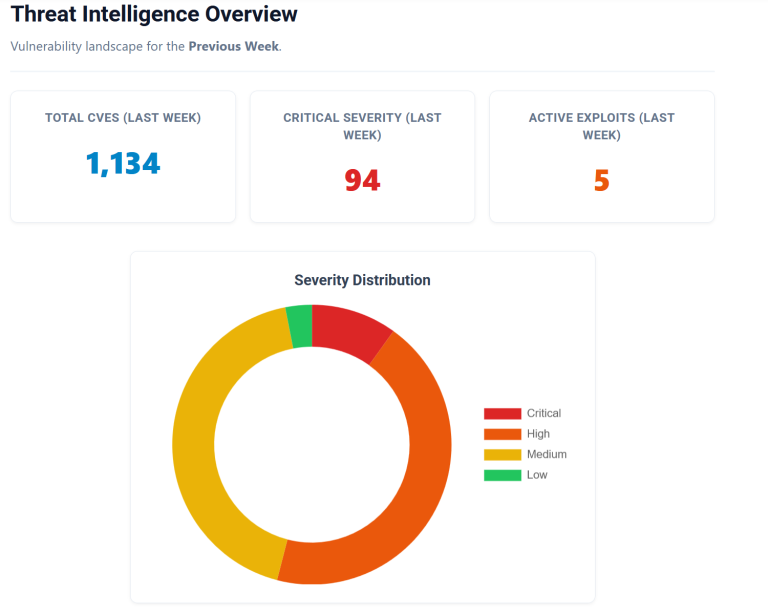
Weekly Triage: 1,134 new vulnerabilities found, including a 9.8 critical bypass in cPanel/WHM and active Express.js logic flaws. Patch your systems now.
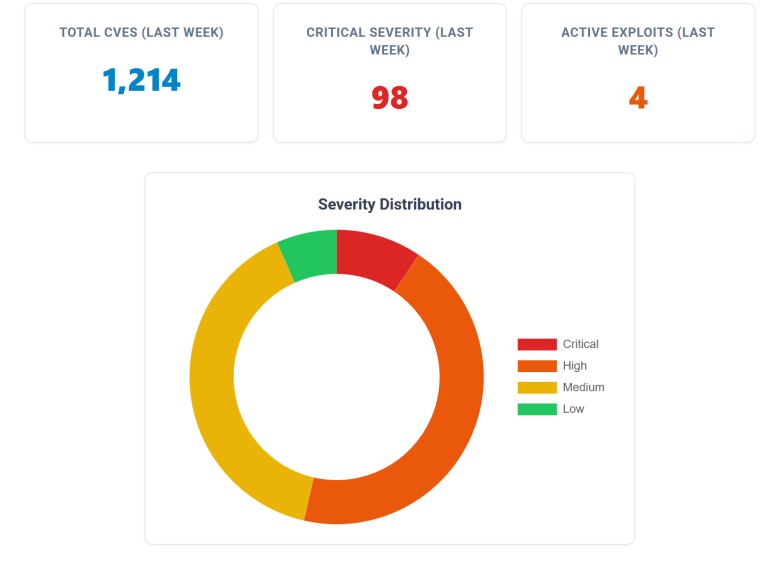
This week's digest: 1,214 new bugs, including active exploits on 2009 Excel fossils and critical 10.0 flaws in new AI/MCP infrastructure. Priority: Patch now.
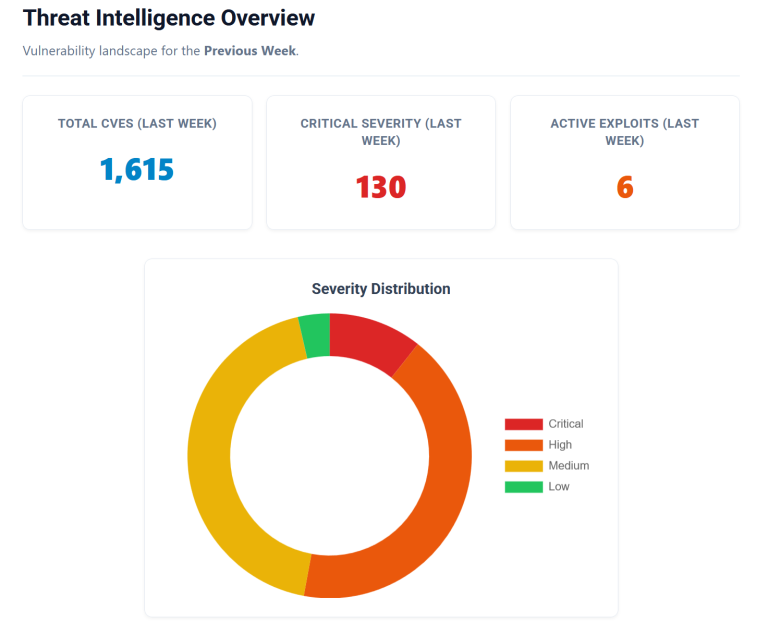
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.

1,361 vulnerabilities found this week: 129 are critical. Prioritize Chrome’s Dawn exploit, FortiClient EMS, and new AI pipeline attacks. Get the full list.
1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.

This week in cybersecurity: 1,348 new vulnerabilities discovered, including seven critical 10.0 CVSS flaws and the highly active DarkSword exploit chain.
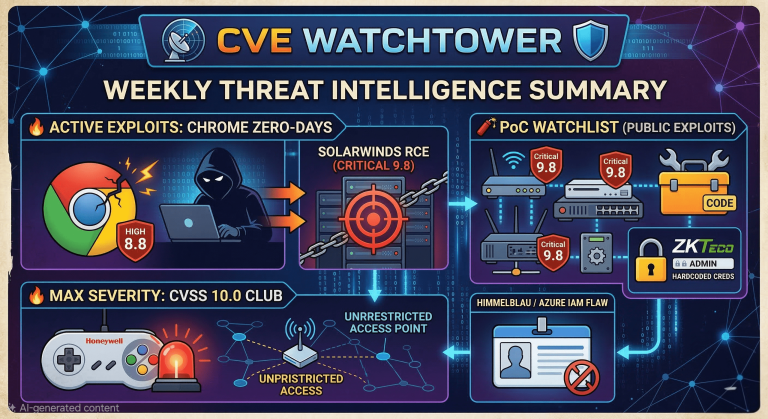
Google Chrome zero-days and a CVSS 10.0 building controller flaw top this week's 1,388 new CVEs. Patch the perimeter before threat actors automate the exploit.

Week of April 7-13 saw critical Ivanti, WordPress, & Windows vulnerabilities exploited, plus major data breaches impacting millions.

Stay informed about the latest cybersecurity event, including new malware threats and critical vulnerabilities being exploited.