 Do Son
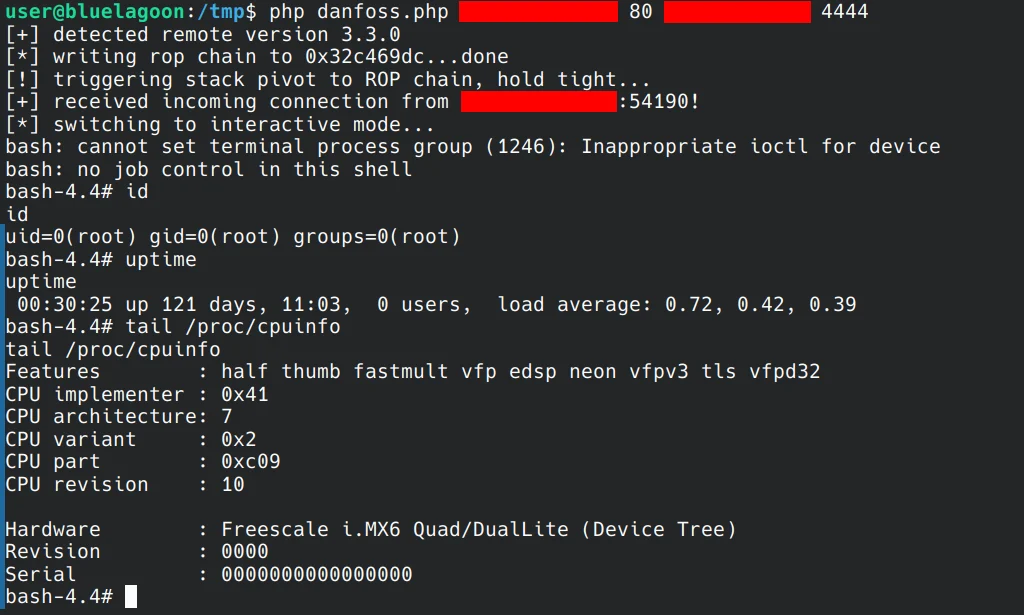
Achieving full RCE as root on Danfoss SM-800A | Image: Midnight Blue
TL;DR
Researchers at Midnight Blue found six pre-authentication remote code execution flaws in the latest Danfoss AK-SM800A firmware, version 5.3.2. It took them about an hour of manual review. These Danfoss AK-SM800A vulnerabilities have no patches and no CVE IDs yet. Coordinated disclosure with Danfoss is still under way.
All six bugs are stack-based buffer overflows that an unauthenticated attacker can reach over the network. Midnight Blue says one even works with Danfoss’s “strict” session control turned on. Until fixes arrive, the researchers urge owners to cut these refrigeration controllers off from the internet.
Why It Matters
Controllers Already Under Attack
The AK-SM800A is a Danfoss controller for refrigeration systems. Attackers targeted such controllers in France starting on October 11, 2026. Danfoss systems were among those hit. A second wave followed on November 2.
Midnight Blue notes that older Danfoss flaws are “shockingly trivial to find and exploit.” The first public exploits for them appeared within 48 hours of the French attacks.
Still Exposed Online
According to Censys data cited by Midnight Blue, hundreds of Danfoss systems remain reachable online. The researchers add that “no doubt a sizeable chunk are by now honeypots.” More than 1,000 Copeland and Dixell controllers are also exposed.
How the Attack Works
Unsafe Code, No Mitigations
The Midnight Blue report points to “hundreds of strcpy invocations” in unauthenticated handler functions. The strcpy function copies data without checking its size, so long input can overflow a buffer.
Moreover, the main application runs as root and lacks stack canaries and PIE. These are standard defenses against memory corruption. The researchers say enabling them “is simply a matter of setting the right compiler flag.”
Strict Mode Is Not Enough
Since firmware 4.0, Danfoss has set a “strict” session control level by default. CERT-FR lists it among its official mitigations. It blocks most of the web interface from users who are not logged in.
However, the component that enforces strict mode has its own pre-authentication memory corruption bug. Midnight Blue says that, “with some additional effort,” it “can be turned into yet another pre-authentication RCE.”
Details Withheld
Midnight Blue showed a private demo of root code execution on an older firmware version. It says the bugs are present in 5.3.2 as well. The team has not released the endpoints or exploit code while disclosure continues. As a result, no public proof-of-concept exists for these flaws. No exploitation of them has been reported.
Potential Impact
Beyond taking over a device, an attacker could change settings or start unwanted defrost cycles. In addition, the controllers do not use the processor’s secure boot features. Midnight Blue therefore warns that an implant could survive a factory reset. Alternatively, attackers could brick the device for good. Without deep forensics, the report says, spotting a firmware implant “is infeasible.”
Affected Versions
- Danfoss AK-SM800A, all firmware up to and including 5.3.2
- CVE IDs: pending
- Fixed version: none yet
Patch and Mitigation
Do Not Rely on Patching Alone
Midnight Blue calls piecemeal patching or enabling strict mode “a misallocation of scarce security and personnel resources.” Instead, it recommends network isolation for all Danfoss, Copeland and Dixell controllers.
Recommended Steps
- List every internet-exposed controller, including those behind system integrators’ 4G modems.
- Allow management access only through a VPN, a private APN, or a strict firewall IP allowlist.
- Do not rely on geofencing or IP blocklists, which the researchers call insufficient.
- Treat IP allowlisting as a stopgap, as CERT-FR advises, because rules drift over time.
Until Danfoss ships fixes, network isolation remains the main defense against these Danfoss AK-SM800A vulnerabilities.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
