Skip to content
October 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Linux
  • GNU Guix & GuixSD 0.15.0 Release: advanced distribution of the GNU operating system
  • Linux

GNU Guix & GuixSD 0.15.0 Release: advanced distribution of the GNU operating system

Do Son July 13, 2018 3 minutes read
GuixSD
Add Daily CyberSecurity as a preferred source on Google

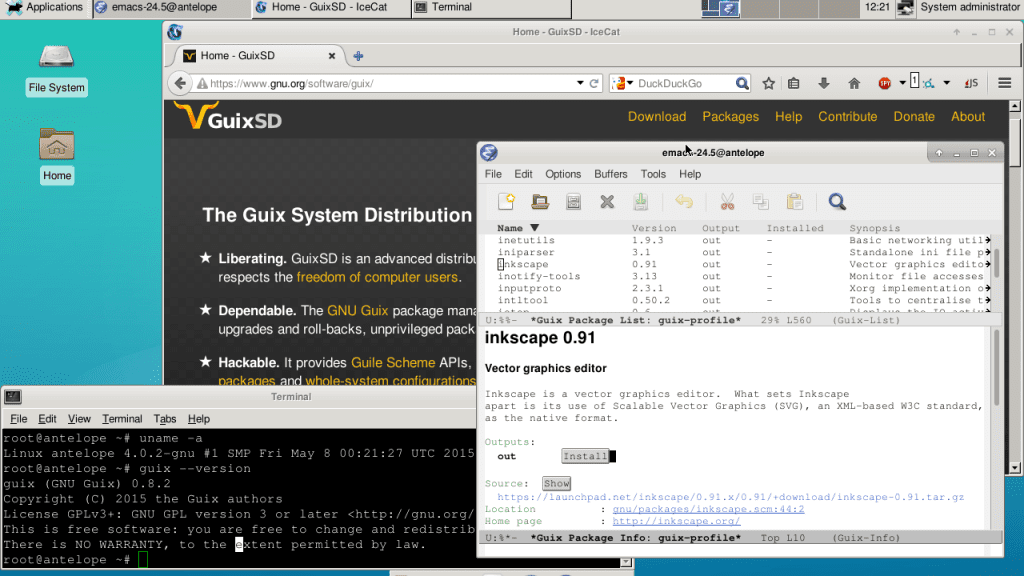
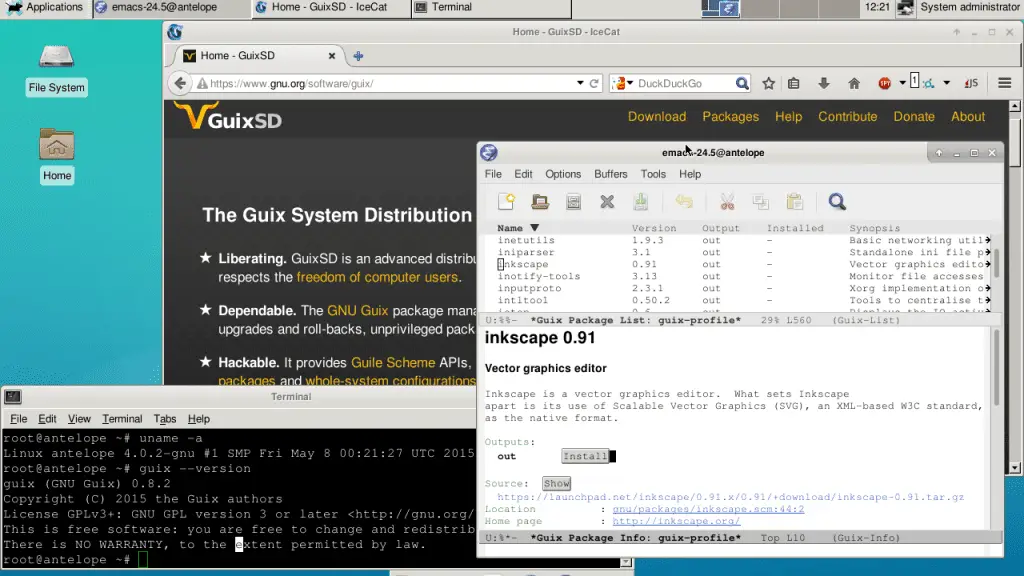
GNU Guix is a transactional package manager for the GNU system. The Guix System Distribution or GuixSD is an advanced distribution of the GNU system that relies on GNU Guix and respects the user’s freedom.

In addition to standard package management features, Guix supports transactional upgrades and roll-backs, unprivileged package management, per-user profiles, and garbage collection. Guix uses low-level mechanisms from the Nix package manager, except that packages are defined as native Guile modules, using extensions to the Scheme language. GuixSD offers a declarative approach to operating system configuration management, and is highly customizable and hackable.

GuixSD can be used on an i686, x86_64, ARMv7, and AArch64 machines. It is also possible to use Guix on top of an already installed GNU/Linux system, including on mips64el and aarch64.

The Guix System Distribution (GuixSD) is an advanced distribution of the GNU operating system developed by the GNU Project—which respects the freedom of computer users.
The project released the 0.15.0 version of GNU Guix (Package Manager) and GuixSD (Distribution). This release contains most of the features that the team expects to include in 1.0, so it will probably be the last release of the 0.x series.
This release includes the GuixSD ISO-9660 installation image, the GuixSD virtual machine image, and the tarball (from source or binary) for installing Guix on other GNU/Linux distributions.
Changelog
  • The unloved guix pull command, which allows users to upgrade Guix and its package collection, has been overhauled and we hope you will like it. We’ll discuss these enhancements in another post soon but suffice to say that the new guix pull now supports rollbacks (just like guix package) and that the new --list-generations option allows you to visualize past upgrades. It’s also faster, not as fast as we’d like though, so we plan to optimize it further in the near future.
  • guix pack can now produce relocatable binaries. With -f squashfs it can now produce images stored as SquashFS file systems. These images can then be executed by Singularity, a “container engine” deployed on some high-performance computing clusters.
  • GuixSD now runs on ARMv7 and AArch64 boxes! We do not provide an installation image though because the details depend on the board you’re targeting, so you’ll have to build the image yourself following the instructions. On ARMv7 it typically uses U-Boot, while AArch64 boxes such as the OverDrive rely on the EFI-enabled GRUB. Bootloader definitions are available for many boards—Novena, A20 OLinuXino, BeagleBone, and even NES.
  • We further improved error-reporting and hints provided by guix system. For instance, it will now suggest upfront kernel modules that should be added to the initrd—previously, you could install a system that would fail to boot simply because the initrd lacked drivers for your hard disk.
  • OS configuration has been simplified with the introduction of things like the initrd-modules field and the file-system-label construct.
  • There’s a new guix system docker-image command that does exactly what you’d expect. 🙂
  • There’s a dozen new GuixSD services: the Enlightenment and MATE desktops, Apache httpd, support for transparent emulation with QEMU through the qemu-binfmt service, OpenNTPD, and more.
  • There were 1,200 new packages, so we’re now close to 8,000 packages.
  • Many bug fixes!
  • The manual is now partially translated into French and you can help translate it into your native language by joining the Translation Project.

Download

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: GuixSD

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 19, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 19, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 19, 2026
  • CVE-2026-111862CVSS 9.8
    Rank Math SEO PRO for WordPress is affected by a supply-chain compromise in a subset of version 3.0.123...
    Admin intel📅 Updated: Oct 17, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2025-61624CVSS 6.0
    An Improper Limitation of a Pathname to a Restricted Directory (\'Path Traversal\') [CWE-22] vulnerability in Fortinet FortiOS 7.6.0...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-102764CVSS 9.3
    The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-106931CVSS 8.5
    SiteGuard Server Edition contains an OS command injection vulnerability, which may allow an attacker to execute arbitrary OS...
    Admin intel📅 Updated: Oct 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-103091CVSS 9.3
    Missing Authorization (CWE-862) and Initialization of a Resource with an Insecure Default (CWE-1188) in the MCP proxy (HandleStreamPassThrough...
    📅 Updated: Oct 19, 2026
  • CVE-2026-102503CVSS 9.3
    Missing Authentication for Critical Function (CWE-306) and Missing Authorization (CWE-862) in the /libp2p-http ingress server (StartIngressServer in cmd/sam-node/node.go)...
    📅 Updated: Oct 19, 2026
  • CVE-2026-108983CVSS 9.8
    A vulnerability is in Web Server default connection ports under the process name GeoWebServer.exe .
    📅 Updated: Oct 19, 2026
  • CVE-2025-39496CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in WBW WooBeWoo Product Filter...
    📅 Updated: Oct 18, 2026
  • CVE-2025-48100CVSS 9.1
    Improper Control of Generation of Code ('Code Injection') vulnerability in extremeidea bidorbuy Store Integrator bidorbuystoreintegrator allows Remote Code...
    📅 Updated: Oct 18, 2026
  • CVE-2025-49387CVSS 10.0
    Unrestricted Upload of File with Dangerous Type vulnerability in add-ons.org Drag and Drop File Upload for Elementor Forms...
    📅 Updated: Oct 18, 2026
  • CVE-2025-49388CVSS 9.8
    Incorrect Privilege Assignment vulnerability in kamleshyadav Miraculous Core Plugin miraculouscore allows Privilege Escalation.This issue affects Miraculous Core Plugin:...
    📅 Updated: Oct 18, 2026
  • CVE-2025-52761CVSS 9.8
    Deserialization of Untrusted Data vulnerability in manfcarlo WP Funnel Manager wp-funnel-manager allows Object Injection.This issue affects WP Funnel...
    📅 Updated: Oct 18, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.