Skip to content
November 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Android
  • Google adds a vulnerability mitigation solution for Android P to prevent certain types of attacks
  • Android

Google adds a vulnerability mitigation solution for Android P to prevent certain types of attacks

Do Son July 4, 2018 1 minute read
Android P security

Google blogs have revealed that the Android P version has a built-in mitigation vulnerability that can defeat certain types of exploits.

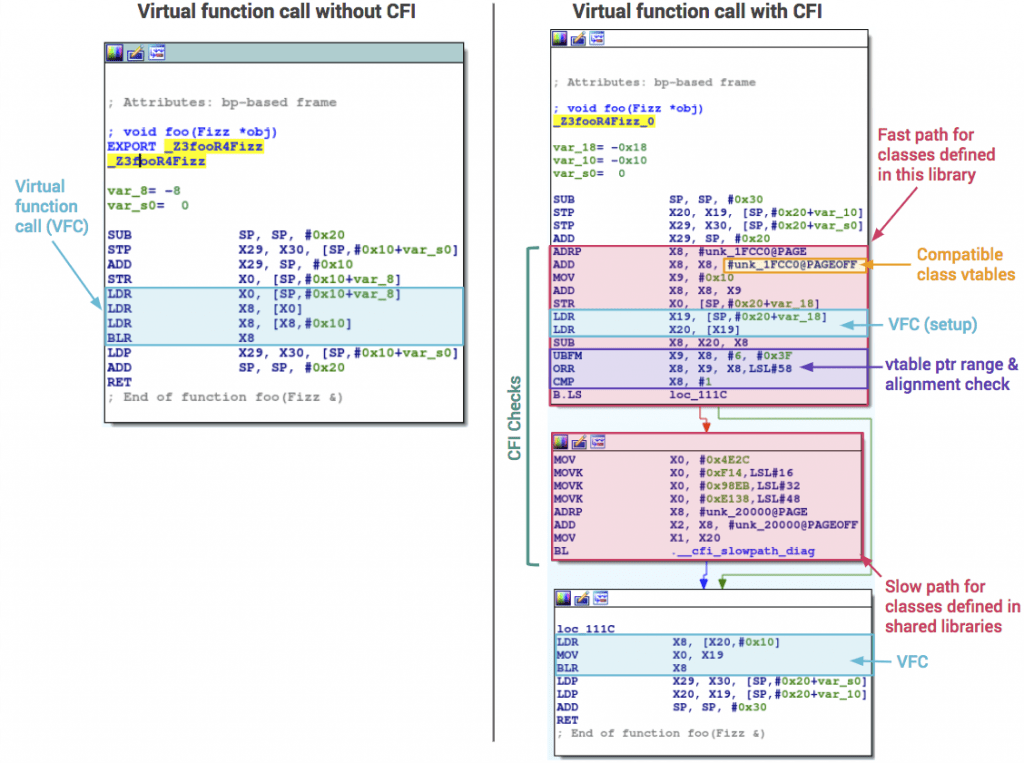
The mitigation scheme directly blocks the operation when the application has undefined behaviour to prevent re-use of the program code and data leakage issues. Google said that since the Android N version, the company has preset LLVM/Clang as a platform compiler to gain more depth security defences.
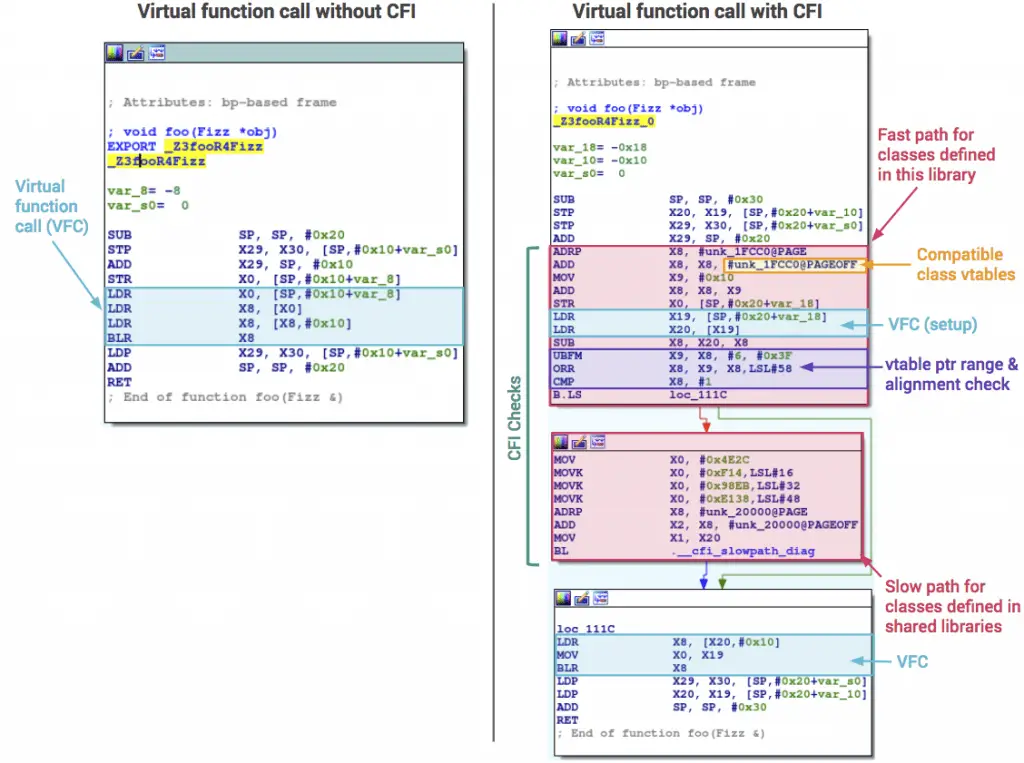
In common attack scenarios, hackers often control program flow by destroying functions or returning locations, and hackers use this executable code fragment to cause malicious purposes. The latest mitigation scheme is to use indirect jumps to prevent control flow operations, and eventually, the system will check for illegal functions by verifying the signature.

Also, the Google Media Services Framework, which often has vulnerabilities, is currently being expanded to use LLVM-based cleaners to remove unnecessary checks.

Google said that after testing, it found that the improved cleanup process would reduce the performance impact by 75%, and for some programs, it would improve the response speed.

Add Daily CyberSecurity as a preferred source on Google
Why add Daily CyberSecurity as a preferred source?
  • See our zero-day and actively exploited CVE coverage more often in Google Top Stories.
  • Catch breaking security news from us as soon as it is published.
  • One click, free, and you can change or remove it anytime in your Google settings.
  • Your other sources stay. We only add ours.

Related coverage

  • Google adds DRM verification to Android APK to ensure authenticity of Play Store app
  • Google began to block uncertified devices from running GApps
  • Android Updates: 7 Years Now? Honor Joins Google, Samsung
  • Google Offers Free Repairs for Swollen Pixel 7a Batteries
  • Privacy First: Google’s AI Detects Fraud, No Cloud Storage
  • Google Registered App Stores Launch for Android
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Android P security

🚨 Active Exploits in the Wild

  • CVE-2026-133968CVSS 9.8
    monailabel (aka MONAI Label) through 0.8.5 allows directory traversal, with resultant remote code execution, via the image parameter...
    Watchtower Verified📅 Updated: Nov 21, 2026
  • CVE-2025-42884CVSS 6.5
    SAP NetWeaver Enterprise Portal allows an unauthenticated attacker to inject JNDI environment properties or pass a URL used...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-76466CVSS 9.8
    A vulnerability in the database service feature of Cisco Expressway Series could allow an unauthenticated, remote attacker with...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-129448CVSS 9.8
    Deserialization of Untrusted Data in Apache Roller versions 4.0.0 through 6.1.4 allows an unauthenticated remote attacker to execute...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-125294CVSS 9.8
    The Nexter Blocks Pro plugin for WordPress is vulnerable to Privilege Escalation in all versions up to, and...
    📅 Updated: Nov 21, 2026
  • CVE-2026-133993CVSS 10.0
    A security flaw has been discovered in D-Link DIR-600L 2.17b02. This affects the function FUN_0040efb0 of the file...
    📅 Updated: Nov 21, 2026
  • CVE-2026-133867CVSS 9.1
    @fastify/express is a compatibility layer that lets Express middleware run inside the Fastify web framework. In versions 4.0.7...
    📅 Updated: Nov 21, 2026
  • CVE-2026-133250CVSS 9.1
    @fastify/middie is the middleware engine for the Fastify web framework. In versions up to and including 9.3.7, middie...
    📅 Updated: Nov 21, 2026
  • CVE-2026-133120CVSS 9.1
    @fastify/express is a compatibility layer that lets Express middleware run inside the Fastify web framework. In versions before...
    📅 Updated: Nov 21, 2026
  • CVE-2026-124626CVSS 9.1
    @fastify/express is a compatibility layer that lets Express middleware run inside the Fastify web framework. In versions 4.0.5...
    📅 Updated: Nov 21, 2026
  • CVE-2026-129504CVSS 9.1
    @fastify/express is a compatibility layer that lets Express middleware run inside the Fastify web framework. In versions 4.0.0...
    📅 Updated: Nov 21, 2026
  • CVE-2026-134258CVSS 9.3
    Admidio 5.0.0 before 5.0.18 contains a path traversal vulnerability in the Documents & Files renameFile() action that allows...
    📅 Updated: Nov 21, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.