Skip to content
November 15, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • Google Image Search Results Remove “View Image” button
  • Technology

Google Image Search Results Remove “View Image” button

Do Son February 16, 2018 1 minute read
View Image

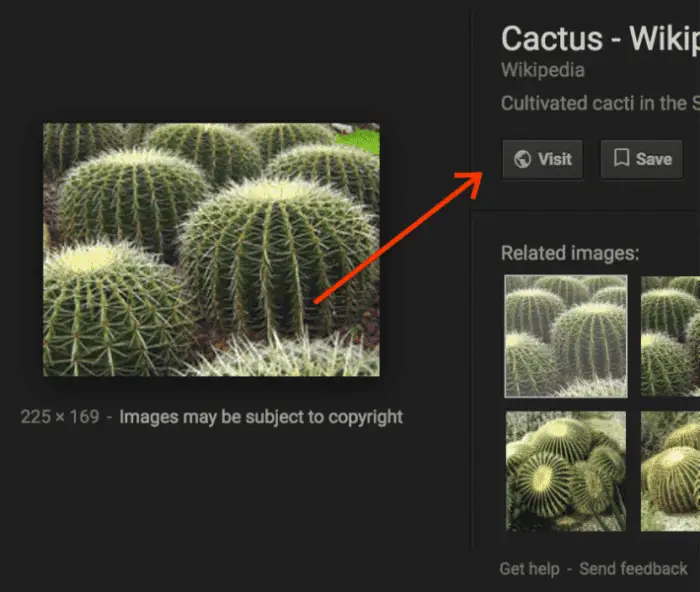
Following an agreement with Getty Images, Google recently made detailed adjustments to its image search capabilities and user experience. Recently, Google has removed the “View Image” button, as well as in the search results browse a specific photo removed when the map search function.

Google today announced these changes in the tweet. Tweets wrote:

Today we're launching some changes on Google Images to help connect users and useful websites. This will include removing the View Image button. The Visit button remains, so users can see images in the context of the webpages they're on. pic.twitter.com/n76KUj4ioD

— Google SearchLiaison (@searchliaison) February 15, 2018

In addition, the “copyright” disclaimer is placed in a more prominent position in search results.

The Search by Image button is also being removed. Reverse image search *still works* through the way most people use it, from the search bar of Google Images.

— Google SearchLiaison (@searchliaison) February 15, 2018

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • The $3 Trillion Tidal Wave: SpaceX, OpenAI, and Anthropic Gear Up for 2026 IPOs
  • Switching Teams: iOS 26.3 Beta Adds Official “Transfer to Android” Data Migration Option
  • OpenAI Math Model Breakthroughs: AI Solves Centennial Enigmas
  • Pixel Reboot Loop Bug Hits Devices After Update
  • Cloud Under Fire: Unidentified “Objects” Strike AWS Data Center in UAE Amid Regional Tensions
  • Google to Invest $40 Billion in Texas for Next-Gen Cloud and AI Data Centers
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: View Image

🚨 Active Exploits in the Wild

  • CVE-2024-58406CVSS 8.7
    Huatian Dynamic OA8000 collaborative office system contains an unauthenticated path traversal vulnerability in /OAapp/jsp/trace/ntkodownload.jsp, where the filename request...
    Watchtower Verified📅 Updated: Nov 13, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    CISA KEV📅 Added to KEV: Nov 13, 2026
  • CVE-2026-123039CVSS 7.8
    The Gaia OS DynamicCLI daemon runs as root and listens on a world-writable local socket (/tmp/dynamic_socket) without authenticating...
    CISA KEV📅 Added to KEV: Nov 13, 2026
  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-129483CVSS 9.3
    Cyrus SASL through 2.1.28 contains an authentication bypass vulnerability in the SRP server mechanism because srp_server_mech_step2 does not...
    📅 Updated: Nov 15, 2026
  • CVE-2026-129453CVSS 9.4
    A vulnerability was found in DrayTek Vigor2960 1.5.1.6. This issue affects the function check_file_exist of the file /cgi-bin/mainfunction.cgi...
    📅 Updated: Nov 15, 2026
  • CVE-2026-124560CVSS 9.3
    A vulnerability was found in D-Link DIR-878 1.20B05. This affects the function GetCAPTCHAsetting of the file bin/prog.cgi of...
    📅 Updated: Nov 15, 2026
  • CVE-2026-129452CVSS 9.4
    A vulnerability has been found in DrayTek Vigor2960 1.5.1.6. This vulnerability affects the function set_table of the file...
    📅 Updated: Nov 15, 2026
  • CVE-2026-129451CVSS 9.4
    A flaw has been found in DrayTek Vigor2960 up to 1.5.1.6. This affects the function app_guest_export of the...
    📅 Updated: Nov 15, 2026
  • CVE-2026-129450CVSS 9.4
    A vulnerability was detected in DrayTek Vigor2960 1.5.1.6. Affected by this issue is the function sub_1E084 of the...
    📅 Updated: Nov 15, 2026
  • CVE-2026-129449CVSS 9.4
    A security vulnerability has been detected in DrayTek Vigor2960 up to 1.5.1.6. Affected by this vulnerability is the...
    📅 Updated: Nov 15, 2026
  • CVE-2026-129349CVSS 9.1
    When authentication caching is enabled on DefaultLdapRealm, after a user logs in successfully once, subsequent logins for that...
    📅 Updated: Nov 15, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.