Skip to content
October 23, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Cyber Security
  • Hackers hijack bitcoin wallet TREZOR to a phishing website
  • Cyber Security

Hackers hijack bitcoin wallet TREZOR to a phishing website

Do Son July 4, 2018 2 minutes read
hijack bitcoin wallet TREZOR
Add Daily CyberSecurity as a preferred source on Google

The popular Bitcoin wallet TREZOR team recently published a blog saying that hackers have attacked the company’s wallet address and directed to the phishing website of the cottage.

The hacker did not choose to attack the TREZOR Bitcoin wallet server but hijacked some regional routes to direct users to the phishing site to defraud the key.

After analysis, the company team confirmed that the hacker hijacked the BGP gateway and tampered with the DNS server, but the attack was generally very unsuccessful.

Because the hacker does not have a corresponding HTTPS certificate, and the browser directly intercepts the access when the user accesses, no user leaks his or her key.
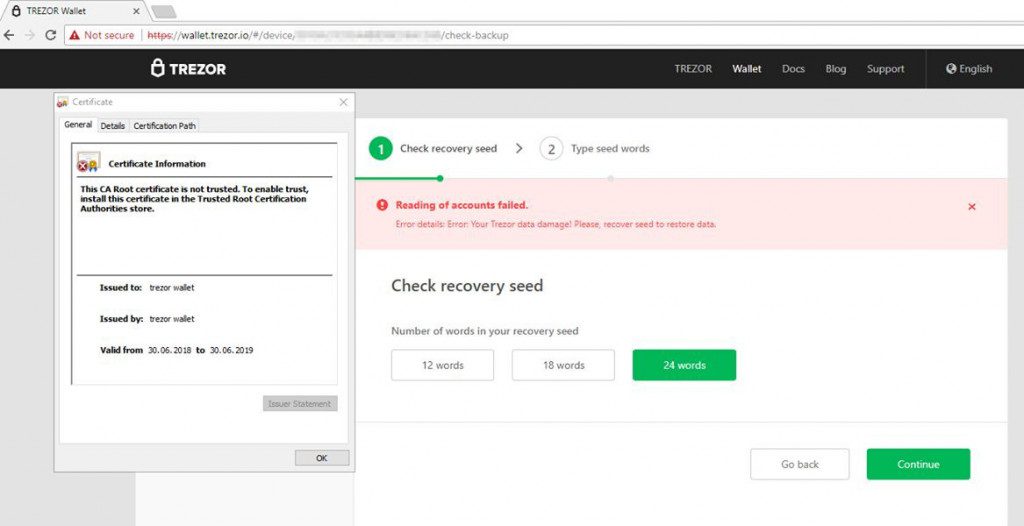
 

Of course, this also highlights the importance of deploying HTTPS encrypted connections. The importance of HTTPS in preventing man-in-the-middle hijacking and data leakage is irreplaceable.

This is the second time in recent years that hijacking MySQL gateways to hijack virtual currency wallets has occurred. Fortunately, neither attack caused any significant losses.

In fact, hijacking a BGP gateway is no less challenging than directly attacking a server on a website so that a hacker may have successfully invaded a BGP server before.

At the same time, hijacking the BGP gateway and then hijacking the DNS server can hijack any website, so the problem of BGP server being compromised is also more significant.

Source, Image: trezor

Related coverage

  • Kaspersky Highlights Key Trends in Financial Cybersecurity for 2024
  • Nigerian National Receives 5-Year Sentence for Multi-Million Dollar BEC Fraud
  • TA4903 – A Cybercriminal Group with a Focus on Financial Gain
  • From Sellers to Reviewers: Exposing the Fake Review Network
  • US/UK warn Russia to hack into global routers
  • Threat Actors Exploit SimpleHelp Vulnerabilities to Deploy Sliver Backdoor
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: hijack bitcoin wallet TREZOR

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2017-20287CVSS 8.7
    Javo Spot theme for WordPress before 3.0.0 contains a path traversal vulnerability that allows unauthenticated attackers to read...
    Watchtower Verified📅 Updated: Oct 23, 2026
  • CVE-2017-20288CVSS 5.1
    QCubed 2.2.0 through 3.1.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject scripts through...
    Watchtower Verified📅 Updated: Oct 23, 2026
  • CVE-2017-20289CVSS 7.7
    Broadstreet Ad Widget plugin for WordPress 2.2.0 before 2.12.0 contains a local file inclusion vulnerability that allows authenticated...
    Watchtower Verified📅 Updated: Oct 23, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 23, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 23, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 23, 2026
  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-113678CVSS 9.4
    Froxlor before 2.3.15 contains a symlink following vulnerability in Statistics::makeChownWithNewStats that allows authenticated customers to take ownership of...
    📅 Updated: Oct 23, 2026
  • CVE-2026-19677CVSS 9.3
    An authentication bypass vulnerability in the public onPhase/ frevvo registration form version 11.0.14 allows an unauthenticated remote attacker to...
    📅 Updated: Oct 23, 2026
  • CVE-2026-92559CVSS 9.8
    IBM App Connect Enterprise 13.0.1.0 through 13.0.8.2 could allow a remote attacker to obtain sensitive information due to...
    📅 Updated: Oct 22, 2026
  • CVE-2026-91305CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Installation Security). Supported versions that...
    📅 Updated: Oct 22, 2026
  • CVE-2026-91665CVSS 9.8
    Vulnerability in Oracle Essbase (component: Security). The supported version that is affected is 21.8.3.0.0. Easily exploitable vulnerability allows...
    📅 Updated: Oct 22, 2026
  • CVE-2026-91265CVSS 9.1
    Vulnerability in the JD Edwards EnterpriseOne Tools product of Oracle JD Edwards (component: Enterprise Infrastructure SEC). Supported versions...
    📅 Updated: Oct 22, 2026
  • CVE-2026-91299CVSS 10.0
    Vulnerability in the JD Edwards EnterpriseOne Orchestrator product of Oracle JD Edwards (component: E1 IOT Orchestrator Security). Supported...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76466CVSS 9.8
    A vulnerability in the database service feature of Cisco Expressway Series could allow an unauthenticated, remote attacker with...
    📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.