Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Cyber Security
  • Hackers sell multiple international airports access for only $10
  • Cyber Security

Hackers sell multiple international airports access for only $10

Do Son July 15, 2018 3 minutes read
international airports access

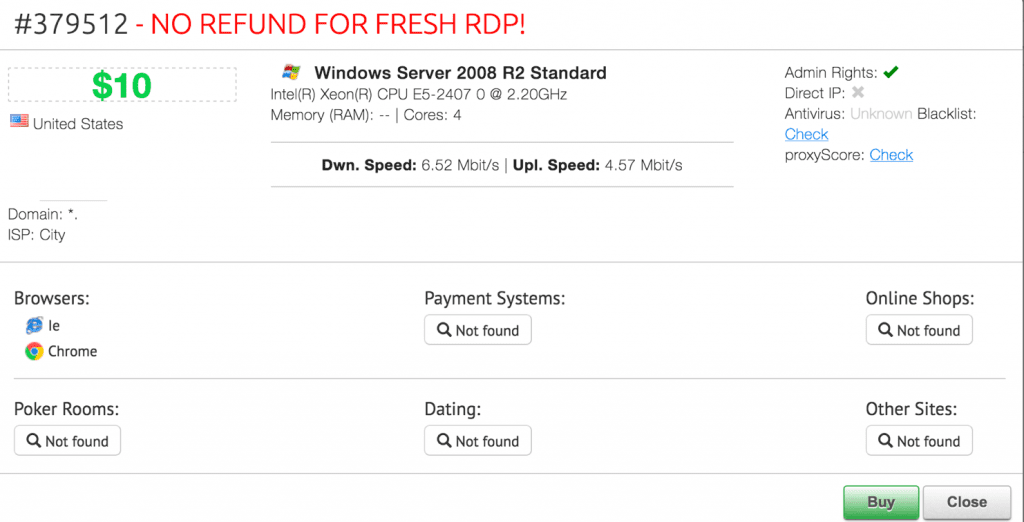
The airport should be a public place with a very high-security level in the eyes of ordinary people, but it is not known that you can black into the airport system for only $10.

The well-known security company McAfee found in the daily inspections that hackers sold server remote desktop connection credentials at multiple international airports in the dark market.

Anyone who spends tens of dollars can easily purchase these server passwords and then log in to the corresponding server with any hacking technology.
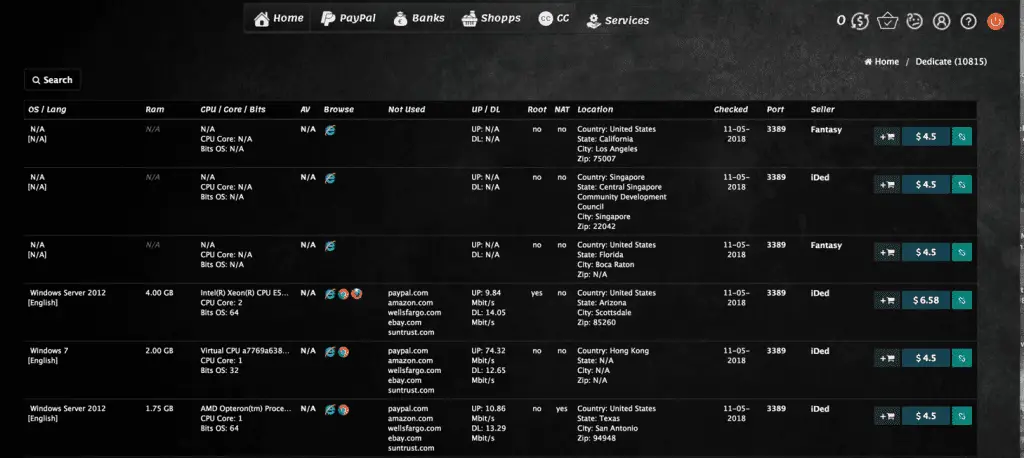
The Remote Desktop Protocol is mainly used by Microsoft to facilitate the operation and maintenance personnel to connect to the server. You can log in to the server remotely as long as you have the address and password.

After tracking, McAfee found that many sellers are selling such certificates in the dark market black market. For example, a dark market in Russia sells 40,000 server certificates.

For example, the researcher purchased several server credentials for an international airport for testing. After verification, the researchers confirmed that the data was all valid.

The airport’s security and building automation systems, monitoring and video analysis systems, and automated transportation system accounts outside the airport are all sold on the dark.

Besides, the researchers found that server credentials from multiple hospitals, nursing, and medical device manufacturers were leaked, which could pose a significant safety hazard.
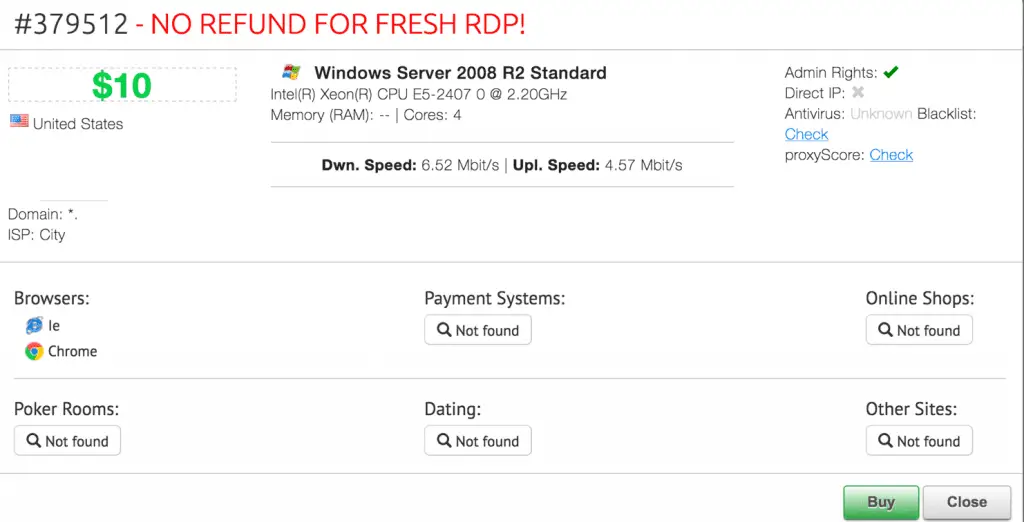
Under normal circumstances, hackers who want to obtain remote desktop credentials mainly rely on zero-day exploits, malware phishing or social engineering attacks.

But being able to get so many remote desktop credentials is not possible with cumbersome social engineering attacks, so it’s likely to be through vulnerabilities and phishing attacks.

It is worth noting that most of these hacked servers are Windows Server 2008 and 2012. It is possible that these servers are not updated.

The most significant hazard in this security incident is the clear division of hackers. For example, the sellers of the dark network only sell data, but they do not attack themselves.

For other hackers, it only takes ten dollars to purchase account credentials and does not require extremely tedious work through zero-day vulnerabilities and social engineering.

Therefore, even a script kid with no hacking skills can purchase credentials to destroy, but the damages found at present are mainly mine mining.

Therefore, please use the high-strength password after the remote desktop protocol is enabled on the server and replace it regularly to avoid the broiler in the black market after the leak.

Source, Image: mcafee

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • U.S. ​​aid to Ukraine’s cybersecurity to $10 million
  • Critical Magento Flaw Exploited: CosmicSting (CVE-2024-34102) Strikes Global Brands
  • Sneaky 2FA: A New Adversary-in-the-Middle Phishing-as-a-Service Threat
  • Bondnet Threat Actor Still Active, Using Bots as C2 Servers
  • GoTitan Botnet Emerges Amidst Active Exploitation of Apache Vulnerability
  • Cybercriminals Target LatAm Banks: Mekotio, BBTok Lead the Charge
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Hackers international airports access

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-77876CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.16 contains an OS command injection vulnerability in the protected_directory user panel...
    📅 Updated: Nov 2, 2026
  • CVE-2026-79873CVSS 9.3
    Authentication bypass vulnerabilities in the PAPI protocol of AOS-10 could allow an unauthenticated adjacent attacker to circumvent existing...
    📅 Updated: Nov 2, 2026
  • CVE-2026-79874CVSS 9.3
    An authentication bypass in the API of AOS-10 allows an unauthenticated adjacent attacker to circumvent existing authentication controls....
    📅 Updated: Nov 2, 2026
  • CVE-2026-79872CVSS 9.4
    A buffer overflow vulnerability exists in the underlying operating system of AOS that could lead to unauthenticated remote...
    📅 Updated: Nov 2, 2026
  • CVE-2026-55981CVSS 9.6
    A firmware verification vulnerability in Creative Sound Blaster Katana could allow an attacker to modify a legitimate firmware...
    📅 Updated: Nov 2, 2026
  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Nov 2, 2026
  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.