 Do Son
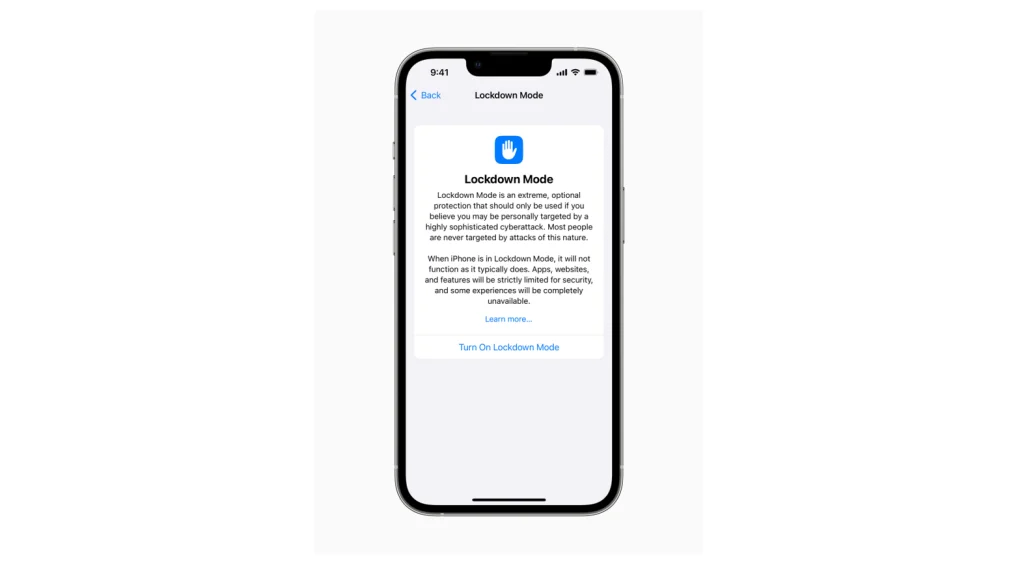
Security research firm Calif revealed an unprecedented exploit chain targeting Apple mobile devices. Specifically, researchers achieved a persistent iOS Lockdown Mode jailbreak on an iPhone 18 Pro. The attack triggers instantly when the target accepts a malicious PDF document over AirDrop. Furthermore, the elevated root privileges survive subsequent operating system updates to iOS 27.2. Consequently, this breakthrough confirms that advanced malware can establish deep persistence across modern Apple devices.
AirDrop PDF Delivery Bypasses Extreme Protection
Apple designed Lockdown Mode to protect vulnerable individuals from sophisticated state-sponsored intrusions. When active, this hardened defensive profile disables numerous system capabilities to shrink the attack perimeter. However, the demonstration exposes critical architectural blind spots within native document handling parsers.
During the execution sequence, researchers transmitted a weaponized PDF payload directly to the receiver. The user simply accepted the incoming AirDrop prompt on the screen. Immediately upon file receipt, background parsing engines triggered an automated exploitation sequence. Therefore, this vector functions as an efficient one-click compromise without requiring user interaction inside the document.
Firmware Persistence Across System Updates
The most alarming aspect of the research involves root persistence across system resets. In the video demonstration released by Calif on X, the device retained root access after updating from iOS 27 to version 27.2. Consequently, traditional remediation methods like simple reboots fail to eradicate the underlying compromise. This survivability indicates that the exploit achieves stable low-level system execution.
Disclosure Timeline and Defensive Recommendations
Calif withheld explicit technical mechanics while coordinating remediation with Apple security teams. Although security enthusiasts eagerly anticipate potential jailbreak utilities, researchers confirmed they will not release public toolkits. Nevertheless, device owners should remain cautious when navigating untrusted wireless environments.
Recent attack campaigns such as DarkSword highlight expanding threats against consumer hardware. Therefore, security professionals strongly advise users to install future iOS security patches promptly. Ultimately, prompt firmware upgrades remain the best protection against covert mobile threats.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
