Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Cyber Security
  • Iranian APT hacker organisation falsifies Israeli security companies official website to implement phishing activities
  • Cyber Security

Iranian APT hacker organisation falsifies Israeli security companies official website to implement phishing activities

Do Son July 5, 2018 2 minutes read
Iranian APT hacker organisation

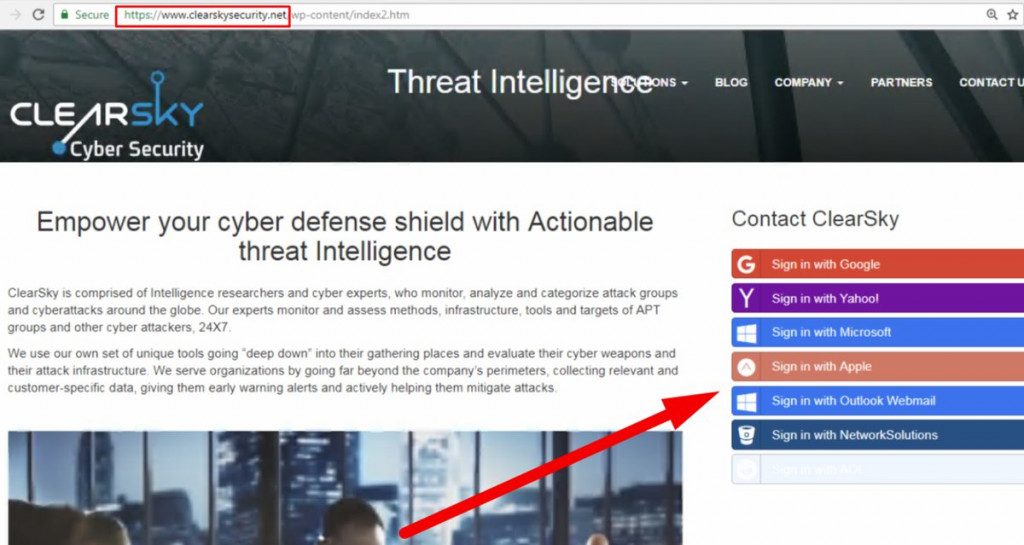
Israeli security company ClearSky Security recently released a report saying that the Iranian APT hacker group Charming Kitten was discovered by the company’s official website for phishing activities, thus revealing its traces.

Charming Kitten is also commonly referred to as Newscaster or Newsbeef, and the associated malicious activities can be traced back to 2014. The organisation was also one of the first Iranian national hacking organisations detected in actual attacks and has been active in recent years. It has launched hacking activities such as Saffron Rose, Newscaster and StoneDrill.

#CharmingKitten built a phishing website impersonating our company. The fake website is clearskysecurity.net (the real website is https://t.co/kdF5RfVA83). They copied pages from our public website and changed one of them to include a "sign in" option with multiple services. pic.twitter.com/3fETo2GTuJ

— ClearSky Cyber Security (@ClearskySec) July 1, 2018

In the early days, the organisation used spear phishing as its attack method and sent attacks against targets located in Iran and the United States. The organisation showed a significant technology upgrade last year. They created a hard disk eraser called “StoneDrill” and used it for attack activities, which means that their attack methods may change significantly in the future.

The last time Charming Kitten appeared in our field of vision was last year when an Iranian named Behzad Mesri sued in the United States for allegedly invading the US cable network media company HBO and stealing the hit TV series “Power The drama resources do not officially broadcast the game. It is worth noting that Behzad Mesri is considered to be a member of Charming Kitten.

Back in this incident, ClearSky pointed out that the organisation cloned its official website and hosted it on clearskysecurity[.]net, while the real ClearSky official website is located on ClearSky[.]com. The organization copied the page from the actual ClearSky official webpage and changed one of the pages to a page with multiple service login options (there is no such option on the real website), and these login options are undoubtedly all connected to the phishing website, which can send the victim’s credentials to the attacker.
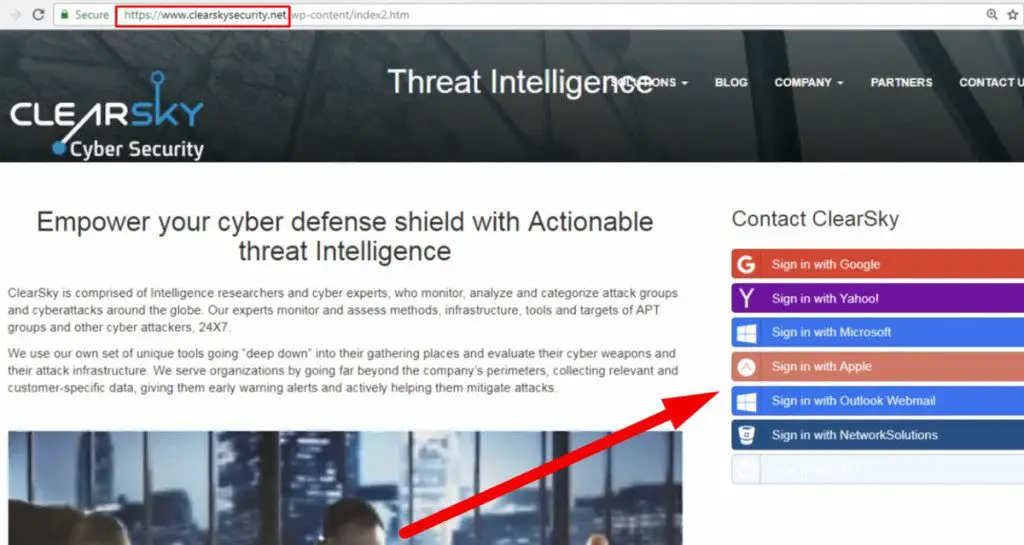
 

Researchers at ClearSky said that when they found the site, it was still under construction, and clicking on specific pages might even bring up an error message. Therefore, the researchers believe that the fishing of Charming Kitten has not been successful. Also, the site did not survive for a long time, it was marked as suspicious by Google’s Safe Browsing API, and was forced to go offline after a few hours.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Spyware Targets MEP Daniel Freund Before EU Elections
  • 100GB of Secrets Seized: Akira Claims Responsibility for Nissan Cyberattack
  • Record Cyberattack: Suffolk County’s $25.7M Recovery Plan
  • MATA Malware Cluster Targets Eastern European Corporations
  • Omani Government Targeted in Blatant Iranian-Nexus Cyberespionage
  • Ongoing Phishing Attack in LATAM Region
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Iranian APT hacker organisation

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-83770CVSS 9.8
    Heap-based buffer overflow in Windows Text Shaping allows an unauthorized attacker to execute code over a network.
    📅 Updated: Nov 2, 2026
  • CVE-2026-83780CVSS 9.8
    Use after free in Windows CCFFilter Driver allows an unauthorized attacker to execute code over a network.
    📅 Updated: Nov 2, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    📅 Updated: Nov 2, 2026
  • CVE-2026-83782CVSS 9.8
    Heap-based buffer overflow in Windows Shell allows an unauthorized attacker to execute code over a network.
    📅 Updated: Nov 2, 2026
  • CVE-2026-19677CVSS 9.3
    An authentication bypass vulnerability in the public onPhase/ frevvo registration form version 11.0.14 allows an unauthenticated remote attacker to...
    📅 Updated: Nov 2, 2026
  • CVE-2026-111594CVSS 9.2
    InterSystems IRIS for Health has TLS/SSL encryption turned off by default, which may enable an attacker to view...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120213CVSS 9.1
    @fastify/http-proxy is a Fastify plugin that proxies HTTP requests to an upstream server under a configured prefix. In...
    📅 Updated: Nov 2, 2026
  • CVE-2026-102435CVSS 9.8
    The Ultra Addons for Contact Form 7 plugin for WordPress is vulnerable to arbitrary file deletion due to...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.