Skip to content
October 24, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • July PYPL PopularitY of Programming Language: Python and Java gradually widened the gap
  • Technology

July PYPL PopularitY of Programming Language: Python and Java gradually widened the gap

Do Son July 5, 2018 1 minute read
PYPL PopularitY python
Add Daily CyberSecurity as a preferred source on Google

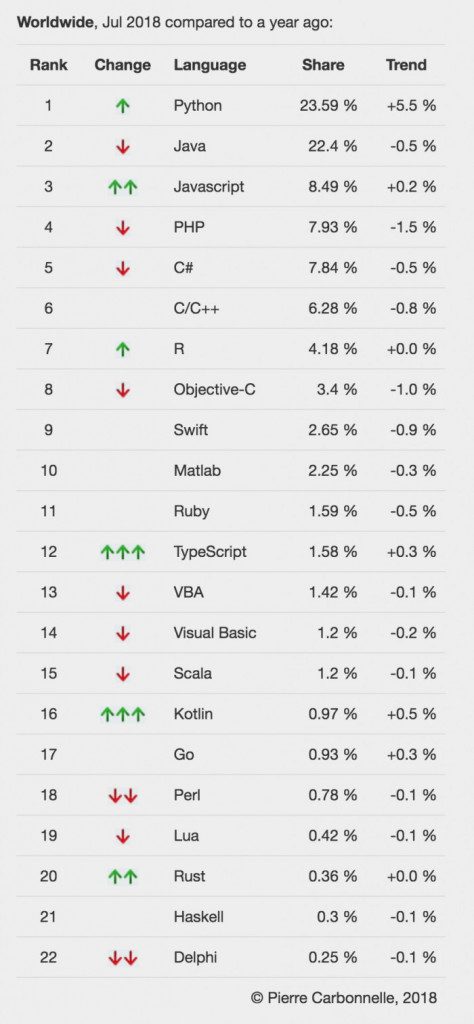
PYPL has released the July programming language index list. Python has maintained its upward trend after surpassing Java for the first time in May this year and is gradually opening a gap with Java. Also, JavaScript and PHP are also very competitive in the third place. The two scores are very close in the first half of the index, but this month due to a 1.5 percentage point drop in PHP, the status is a bit dangerous.

The PYPL index raw data bases on Google trends, which assesses the popularity of the language based on the frequency (number of times) of programming languages on Google.

Python and Java trends:


JavaScript and PHP trends:


Related coverage

  • Apache Foundation Announces Annual Report 2018FY: Most Java Projects
  • Another Reprieve for TikTok: A Fourth Deadline Extension Is Expected
  • Microsoft Unveils the Next Generation of Copilot
  • OpenAI & Oracle Join Forces for 4.5 GW “Stargate” AI Data Center: Fueling the Next Generation of AI
  • Meta Reverses Course: Strikes Deals with CNN, Le Monde to Feed Licensed News to Meta AI
  • Local-First & Secure: A New Open-Source Password Manager Enters the Scene
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS Β· Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: PYPL PopularitY Python

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2014-125133CVSS 8.7
    NativeChurch theme for WordPress before 1.6.2 contains a path traversal vulnerability that allows unauthenticated attackers to download arbitrary...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2015-20128CVSS 8.8
    FooSun DotNetCMS 1.0 and 2.0 contains an SQL injection vulnerability that allows unauthenticated attackers to manipulate MSSQL queries...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2016-20104CVSS 8.7
    EyeLock nano NXT 3.05.1193, 3.04.1108, 3.03.944, and 3.01.646 contain a path traversal vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2026-110447CVSS 9.2
    Collabora Online Built-in CODE Server before 26.4.303 (richdocumentscode), a Nextcloud app, allows remote code execution, as exploited in...
    CISA KEV📅 Added to KEV: Oct 23, 2026
  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    CISA KEV📅 Added to KEV: Oct 23, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115806CVSS 9.8
    The Prime Mover – Backup and Migration plugin for WordPress is vulnerable to PHP Object Injection in all...
    📅 Updated: Oct 24, 2026
  • CVE-2026-79855CVSS 9.8
    An authentication bypass vulnerability in the SSH daemon of AOS-8 allows an unauthenticated remote attacker to circumvent existing...
    📅 Updated: Oct 24, 2026
  • CVE-2026-79856CVSS 9.8
    A buffer overflow vulnerability exists in the PAPI protocol of AOS-8 that could allow an unauthenticated remote attacker...
    📅 Updated: Oct 24, 2026
  • CVE-2026-79857CVSS 9.8
    There is a command injection vulnerability in the PAPI protocol (Aruba's access point management protocol) of AOS-8 that...
    📅 Updated: Oct 24, 2026
  • CVE-2026-79858CVSS 9.8
    An unauthenticated SQL injection vulnerability exists in the PAPI protocol in AOS-8. Successful exploitation could allow an unauthenticated...
    📅 Updated: Oct 24, 2026
  • CVE-2026-79852CVSS 9.8
    A vulnerability in the web-based management interface of AOS could allow an unauthenticated remote attacker to conduct SQL...
    📅 Updated: Oct 24, 2026
  • CVE-2026-79854CVSS 9.8
    A vulnerability in the affected interface of AOS-10 could allow an unauthenticated remote attacker to conduct SQL injection...
    📅 Updated: Oct 24, 2026
  • CVE-2026-105014CVSS 9.1
    Improper neutralization of special elements used in a command ('command injection') in Azure Pipelines allows an unauthorized attacker...
    📅 Updated: Oct 24, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.