 Do Son
TL;DR
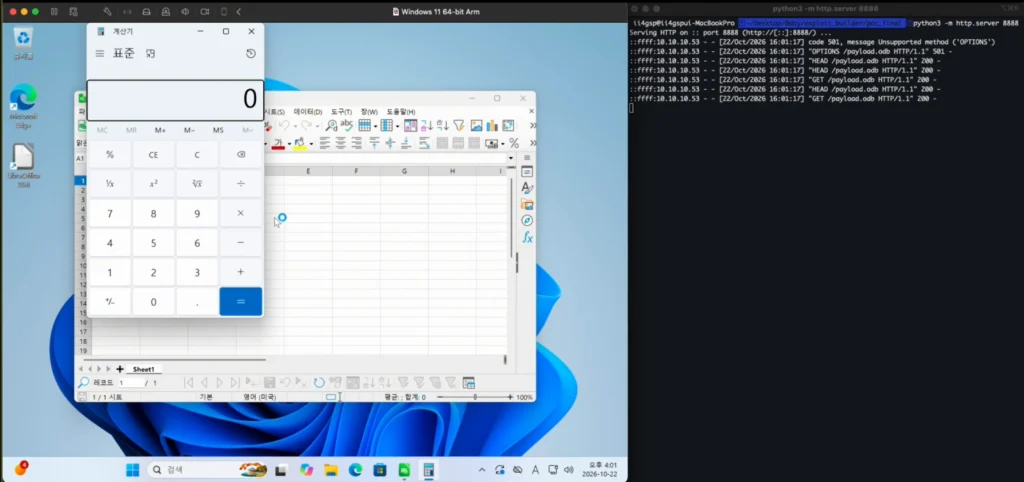
A researcher who goes by ii4gsp has published a full exploit chain for two LibreOffice flaws, CVE-2026-104007 and CVE-2026-104692. The write-up shows LibreOffice remote code execution on macOS, Windows and Linux when a victim opens a crafted spreadsheet. LibreOffice fixed both bugs in versions 26.2.7 and 26.8.2.
Opening a booby-trapped spreadsheet can run attacker code, with “no macros, no prompts, no additional interaction required,” according to the researcher. The attack only works when a Java runtime is installed and enabled in LibreOffice. Technical details and a proof-of-concept walkthrough are now public, though no attacks have been confirmed.
- Product: The Document Foundation LibreOffice
- Vulnerabilities: 2 flaws (CVE-2026-104007, CVE-2026-104692)
- Highest severity: 8.5 (High · CVSSv4)
- Worst impact: Code execution through the JDBC driver path of a database document
- Status: No confirmed exploitation yet; patches available
- Action: Update to < 26.2.7, < 26.8.2 now
| CVE | CVSS (CVSSv4) | Type | Fixed in | Status |
|---|---|---|---|---|
| CVE-2026-104007 | 8.5 | Code execution through the JDBC driver path of a database document | < 26.2.7, < 26.8.2 | Not exploited |
| CVE-2026-104692 | 8.5 | Code execution through Java method calls in HSQLDB databases | < 26.2.7, < 26.8.2 | Not exploited |
Why It Matters
Public Exploit Details
The ii4gsp write-up explains each step, includes source code excerpts, and describes how the proof-of-concept files fit together. As a result, attackers no longer need to rediscover the chain themselves.
No Macro Warning
Office users often learn to distrust macro prompts. This attack skips them. The researcher notes that LibreOffice treats database access as a non-macro operation, so macro security never triggers. Notably, the exploit also works when the file carries a .xlsx name, because LibreOffice detects the format by content.
Many Independent Finders
The official CVE records credit several separate researchers, including teams from Codean Labs, NSHC Red Alert Labs and Hacktron AI. In other words, several teams reported the same issues to LibreOffice separately. Collabora’s Caolan McNamara also appears in the credits.
How the Attack Works
CVE-2026-104007: Untrusted Driver Location
LibreOffice can connect to databases through Java (JDBC) drivers. According to the LibreOffice CVE record, “the location the driver was loaded from was taken from the database document itself.” Consequently, “a crafted document could make LibreOffice load and run Java code that the document supplied.”
LibreOffice already stripped that setting when a user opened a database file directly. However, the researcher found the filter did not run when a spreadsheet referenced an external database file. In that case, LibreOffice downloads the database file over HTTP without asking the user. The researcher says this flaw alone is enough for code execution on Linux.
CVE-2026-104692: Disabled Java Method Whitelist
LibreOffice bundles the HSQLDB database engine, which lets SQL statements call approved Java methods. The CVE record explains that “when HSQLDB was used through the generic JDBC driver this limit did not apply.” Therefore, SQL inside a crafted document “could call any Java method and run code.” On macOS and Windows, the published chain combines both bugs.
Exploitation Status
CISA’s assessment in the CVE records lists exploitation as “none.” Neither flaw appears in CISA’s Known Exploited Vulnerabilities catalog. Still, with the LibreOffice remote code execution chain now public, that could change.
Affected Versions
- LibreOffice 26.2 before 26.2.7
- LibreOffice 26.8 before 26.8.2
Both require a Java runtime installed and enabled in LibreOffice.
Patch and Mitigation
Update LibreOffice
Install LibreOffice 26.2.7 or 26.8.2 from the official LibreOffice download page. The researcher describes the fix as “defense-in-depth,” with overlapping layers. “Even if one layer is bypassed, the others” still block the chain, according to the write-up. LibreOffice now always strips the driver location from documents, and the HSQLDB whitelist starts empty instead of disabled.
If You Cannot Patch Yet
- Turn off “Use a Java runtime environment” under Tools, Options, LibreOffice, Advanced.
- Treat unexpected spreadsheets as suspicious, including files with .xlsx names.
- Block outbound connections from LibreOffice to unknown hosts where possible.
Above all, patch quickly. This LibreOffice remote code execution chain needs only one opened file.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
