Skip to content
November 20, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • Linux Foundation: the LibreOffice on the Microsoft Store is not our
  • Technology

Linux Foundation: the LibreOffice on the Microsoft Store is not our

Do Son July 23, 2018 1 minute read
LibreOffice Microsoft Store

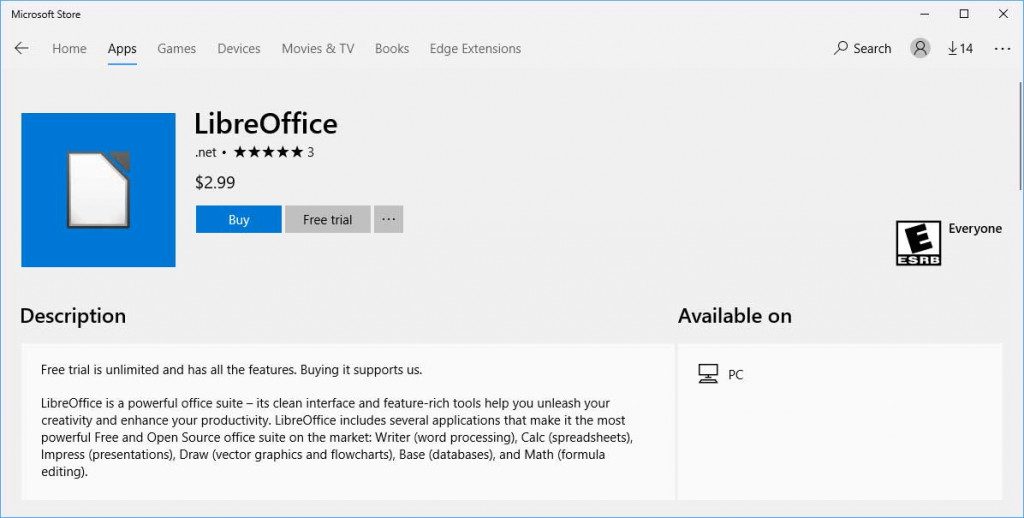
This morning we reported that third-party developers had placed LibreOffice on the Microsoft Store. The Linux Foundation first stated in the tweet that this is not from the official hand. What is even more surprising is that the company may consider bringing LibreOffice to the Microsoft Store. But they first need to check to see if the distribution terms are in line with their license.

@libreoffice Hi, there! I am a journalist and I recently came across LibreOffice in the Microsoft Store for Windows 10 https://t.co/wCuQvkxMd9

Could you please verify and tell us whether this is your official app?

— Mayank Parmar (@mayank_jee) July 22, 2018

https://twitter.com/not_brendon/status/1021195629593231362

This morning, unknown developers released the app on the Microsoft Store. Although users can download the full app for free, they can also choose to purchase the app for $2.99 to support developers.

LibreOffice Microsoft Store

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • The Compute Conundrum: Anthropic Doubles Claude Cowork Window Limits Amid Backlash
  • Google NotebookLM Unleashes “Video Overviews”: AI Transforms Documents into Narrated Presentations
  • Google Chrome 64 automatically cleans up promotional links when you share them
  • SpaceXAI: Elon Musk’s Orbital Data Centers Vision
  • Reddit Blocks Internet Archive to Stop AI Companies from Scraping Data for Free
  • Apple Restores Blood Oxygen Feature to Apple Watch in U.S. After Patent Dispute
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: LibreOffice Microsoft Store

🚨 Active Exploits in the Wild

  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    Watchtower Verified📅 Updated: Nov 19, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-129056CVSS 9.8
    Incorrect Privilege Assignment vulnerability in Paul Ryan Authorizer authorizer allows Privilege Escalation.This issue affects Authorizer: from n/a before...
    📅 Updated: Nov 20, 2026
  • CVE-2026-133493CVSS 10.0
    A vulnerability was identified in D-Link DIR-600L 2.17b02. Affected is the function genacgi_main of the file gena.cgi of...
    📅 Updated: Nov 20, 2026
  • CVE-2026-8467CVSS 9.5
    Code Injection vulnerability in phenixdigital phoenix_storybook allows unauthenticated remote code execution via HEEx template injection in the component...
    📅 Updated: Nov 20, 2026
  • CVE-2026-55953CVSS 9.1
    The Erlang/OTP ssl TLS 1.2 (and earlier) and DTLS client does not verify that the cipher suite selected...
    📅 Updated: Nov 20, 2026
  • CVE-2026-53424CVSS 9.1
    Authentication Bypass by Capture-replay vulnerability in dropbox samly allows an attacker to authenticate as the subject of a...
    📅 Updated: Nov 20, 2026
  • CVE-2026-86533CVSS 9.1
    Insufficient Session Expiration vulnerability in team-alembic AshAuthentication and AshAuthentication Phoenix allows a revoked session to remain fully authenticated....
    📅 Updated: Nov 20, 2026
  • CVE-2026-85500CVSS 9.1
    Authentication Bypass by Primary Weakness vulnerability in team-alembic AshAuthentication allows an unconfirmed user to obtain a session, defeating...
    📅 Updated: Nov 20, 2026
  • CVE-2026-88952CVSS 9.1
    Improper Authentication vulnerability in team-alembic AshAuthentication allows an attacker to be signed in as another user by linking...
    📅 Updated: Nov 20, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.