Skip to content
November 20, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • Unknown developers publish LibreOffice on Microsoft Store
  • Technology

Unknown developers publish LibreOffice on Microsoft Store

Do Son July 23, 2018 2 minutes read
LibreOffice Microsoft Store
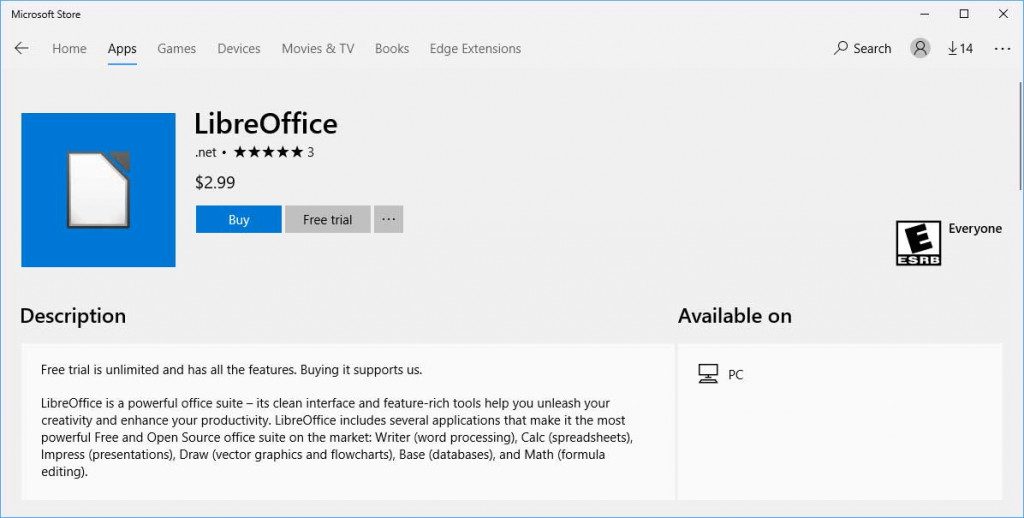
Although Microsoft Office has always been the most powerful productivity suite, LibreOffice has still been considered a strong contender for Microsoft Office with its open source, feature-rich and many other advantages. Recently, third-party developers have released the app on the Microsoft Store. Although users can download the full application for free, they can also choose to purchase the app for $2.99 to support developers.
LibreOffice Microsoft Store
Wrote on the app description page: “Free trial is unlimited and has all the features. Buying it supports us. LibreOffice is a powerful office suite – its clean interface and feature-rich tools help you unleash your creativity and enhance your productivity. LibreOffice includes several applications that make it the most powerful Free and Open Source office suite on the market: Writer (word processing), Calc (spreadsheets), Impress (presentations), Draw (vector graphics and flowcharts), Base (databases), and Math (formula editing).”
The app was submitted by a developer named “.Net” and not in the hands of the official Linux Foundation. Developers seem to be converting Windows desktop applications to Universal Windows platform (UWP) applications through Microsoft’s Project Centennial.

The installed application seems to be LibreOffice. However, since the app is open source, we don’t know if it has tampered with in any way.

Bleeping Computer said it had contacted The Document Foundation to confirm whether its organisation released the application. They have also received a response from The Document Foundation member Italo Vignoli, who said they would investigate it. We will follow up on the follow-up reports.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Unofficial LibreOffice app was removed on the Microsoft Store
  • Linux Foundation: the LibreOffice on the Microsoft Store is not our
  • The End of the Shopping Tab: Google Unveils “Agentic Commerce” and UCP
  • Apple’s “Apple Ring” Rumors Reignite: Mark Gurman Hints at Subtle Wearable Health & Control Device
  • Intel Secures Nearly $8 Billion in CHIPS Act Funding to Boost US Semiconductor Production
  • Wine 10.15: A Major Step Towards Faster Windows Gaming on Linux
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: LibreOffice Microsoft Store

🚨 Active Exploits in the Wild

  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    Watchtower Verified📅 Updated: Nov 19, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-129056CVSS 9.8
    Incorrect Privilege Assignment vulnerability in Paul Ryan Authorizer authorizer allows Privilege Escalation.This issue affects Authorizer: from n/a before...
    📅 Updated: Nov 20, 2026
  • CVE-2026-133493CVSS 10.0
    A vulnerability was identified in D-Link DIR-600L 2.17b02. Affected is the function genacgi_main of the file gena.cgi of...
    📅 Updated: Nov 20, 2026
  • CVE-2026-8467CVSS 9.5
    Code Injection vulnerability in phenixdigital phoenix_storybook allows unauthenticated remote code execution via HEEx template injection in the component...
    📅 Updated: Nov 20, 2026
  • CVE-2026-55953CVSS 9.1
    The Erlang/OTP ssl TLS 1.2 (and earlier) and DTLS client does not verify that the cipher suite selected...
    📅 Updated: Nov 20, 2026
  • CVE-2026-53424CVSS 9.1
    Authentication Bypass by Capture-replay vulnerability in dropbox samly allows an attacker to authenticate as the subject of a...
    📅 Updated: Nov 20, 2026
  • CVE-2026-86533CVSS 9.1
    Insufficient Session Expiration vulnerability in team-alembic AshAuthentication and AshAuthentication Phoenix allows a revoked session to remain fully authenticated....
    📅 Updated: Nov 20, 2026
  • CVE-2026-85500CVSS 9.1
    Authentication Bypass by Primary Weakness vulnerability in team-alembic AshAuthentication allows an unconfirmed user to obtain a session, defeating...
    📅 Updated: Nov 20, 2026
  • CVE-2026-88952CVSS 9.1
    Improper Authentication vulnerability in team-alembic AshAuthentication allows an attacker to be signed in as another user by linking...
    📅 Updated: Nov 20, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.