Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Data Leak
  • OnePlus sends IMEI and the phone manufacturer to a Chinese server
  • Data Leak

OnePlus sends IMEI and the phone manufacturer to a Chinese server

Do Son January 27, 2018 1 minute read
OnePlus

Security researcher Elliot Alderson found a file called badword.txt in OnePlus clipboard application, which contains a large number of Chinese phrases such as “Chairman, Vice President, Deputy Director, Associate Professor, Deputy Heads, General, Private Message, shipping, Address, email, …”. This badword.txt is duplicated in a zip file called pattern. This archive contains 7 files: – badword.txt – brackets.txt – end.txt – follow.txt – key.txt – start.txt . All these files are used in an obfuscated package which seems to be an Android library from teddymobile. TeddyMobile is a Chinese company, they worked with a lot of manufacturers including Oppo.

The @OnePlus #clipboard app contains a strange file called badword.txt 🤔

In these words, we can find: Chairman, Vice President, Deputy Director, Associate Professor, Deputy Heads, General, Private Message, shipping, Address, email, …https://t.co/ePQvD1citn pic.twitter.com/3dCh0joVkH

— Baptiste Robert (@fs0c131y) January 25, 2018

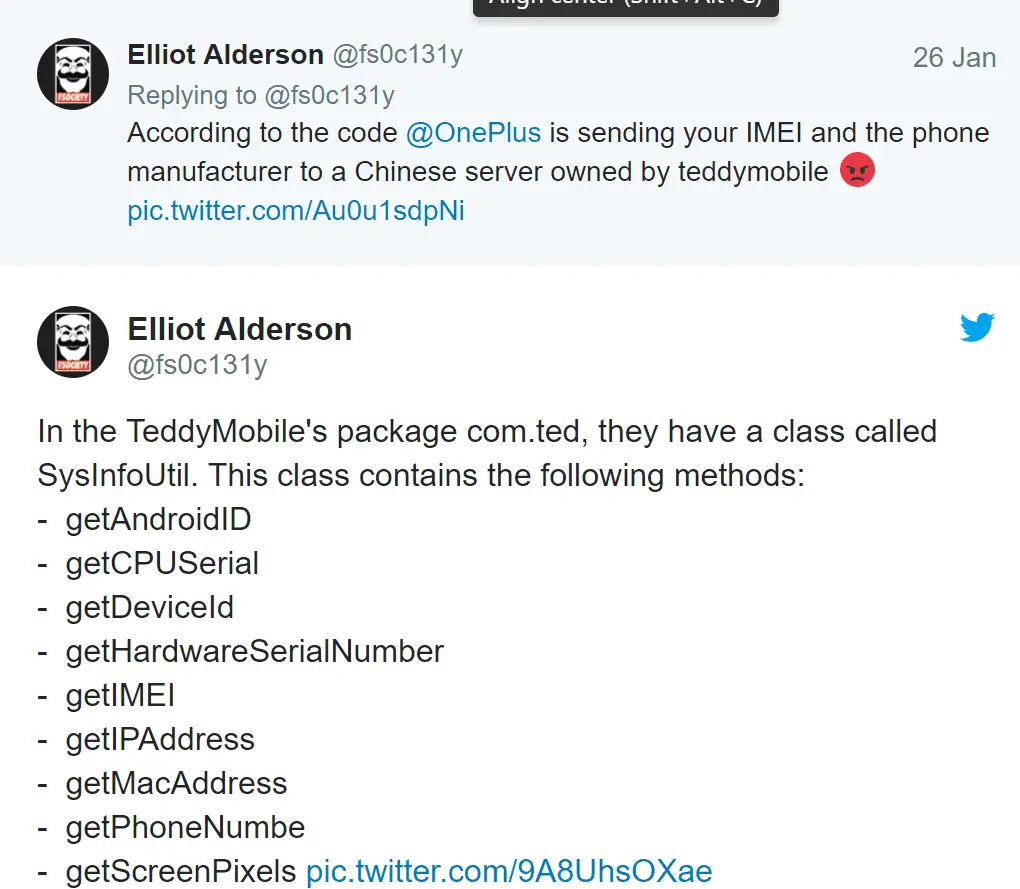
Researchers suspect that one plus one sends the user’s various data to the servers of Chinese companies without the user’s consent.

TeddyMobile package might be able to grab all sorts of data from a phone.

In the TeddyMobile's package com.ted, they have a class called SysInfoUtil. This class contains the following methods:
– getAndroidID
– getCPUSerial
– getDeviceId
– getHardwareSerialNumber
– getIMEI
– getIPAddress
– getMacAddress
– getPhoneNumbe
– getScreenPixels pic.twitter.com/9A8UhsOXae

— Baptiste Robert (@fs0c131y) January 25, 2018

One plus soon responded in an official forum, denying the claim that the keywords were used to filter out data that was not uploaded.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • CAPCOM ID Data Breach Exposes 11.77 Million Records
  • Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications
  • The Next.js Nightmare? Vercel Investigates “Critical” Internal Breach and Supply Chain Threat
  • JetBrains Cadence Server Compromised
  • Tea Dating App Hacked: 72,000 Images, Including Selfies & IDs, Leaked on 4Chan
  • Malicious Twitch Extension Steals 30,000 User Tokens
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: OnePlus

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 8.7
    WooThemes Diarise through 1.5.9 contains a file read vulnerability that allows unauthenticated attackers to read arbitrary files through...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 5.1
    WPML Multilingual CMS plugin for WordPress before 4.6.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121609CVSS 10.0
    A vulnerability was identified in Qihoo 360 Whole Home Router M5 4.0.17.1566. This issue affects the function Home...
    📅 Updated: Nov 4, 2026
  • CVE-2026-51912CVSS 9.8
    OpenBMB XAgent v1.0.0 contains directory traversal vulnerability in main-upload_file-the-preserved-live-upload-file-witness-directly-reaches (ToolServer/ToolServerNode/main.py:46).
    📅 Updated: Nov 4, 2026
  • CVE-2026-107056CVSS 9.1
    Insecure permissions in the io.file.importer.ImportActivity component of OpenTracks versionCode 6751 allows unauthorized attackers to inject crafted tracking data...
    📅 Updated: Nov 4, 2026
  • CVE-2026-107050CVSS 9.8
    An issue in libretro RetroArch v1.22.2 allows attackers to force another user into loading attacker-supplied code in their...
    📅 Updated: Nov 4, 2026
  • CVE-2026-107040CVSS 9.1
    Insecure permissions in MBasov OMN-Go versionCode 26080824 allows unauthorized attackers to invoke an exported component, leading to arbitrary...
    📅 Updated: Nov 4, 2026
  • CVE-2026-107045CVSS 9.1
    Insecure permissions in the CitrineContentProvider component of Citrine v3.1.0 (versionCode 62) allows unauthorized attackers to arbitrarily read another's...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121607CVSS 10.0
    A vulnerability was found in Qihoo 360 D603-2, D600-2, D606-6 and D706 up to 6.4.9. This affects the...
    📅 Updated: Nov 4, 2026
  • CVE-2026-119050CVSS 9.2
    Agno through 3.1.11 contains an unsafe reflection vulnerability in PandasTools that allows attackers to invoke arbitrary pandas functions...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.