Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Google Uncovers UNC6508 Cyber Espionage Campaign Diagram showing UNC6508 cyber espionage attack flow and INFINITERED malware.
  • Cybercriminals

Google Uncovers UNC6508 Cyber Espionage Campaign

Do Son June 22, 2026 0

Google uncovers UNC6508 cyber espionage using INFINITERED malware to target US medical and defense research. Learn how to protect your organization.

QNAP Patches QuMagie Flaws Exposing Private Media Files QNAP QuMagie vulnerabilities allowing unauthenticated information disclosure of media files in QSA-26-35
  • Vulnerability Report

QNAP Patches QuMagie Flaws Exposing Private Media Files

Do Son June 22, 2026 0

QNAP QuMagie vulnerabilities let unauthenticated attackers access media files, causing information disclosure. Patch QuMagie and License Center now.

Malicious Steam Wallpapers Spread Malware to Gamers Malicious Steam wallpapers targeting the Wallpaper Engine app
  • Malware

Malicious Steam Wallpapers Spread Malware to Gamers

Do Son June 22, 2026 0

Hackers are hiding malware inside malicious Steam wallpapers. Learn how the Wallpaper Engine app exposes gamers to account hijacking and crypto miners.
Pre-emptive AI cybersecurity: what it takes to prioritize risk before attackers act Salesforce vulnerability CVE-2025-9844 Salt Typhoon cyberattack
  • Technique

Pre-emptive AI cybersecurity: what it takes to prioritize risk before attackers act

Joe Pettit June 22, 2026 0
There is no shortage of vulnerabilities for security teams to deal with. FIRST forecasts up to 59,000...
Read More Read more about Pre-emptive AI cybersecurity: what it takes to prioritize risk before attackers act
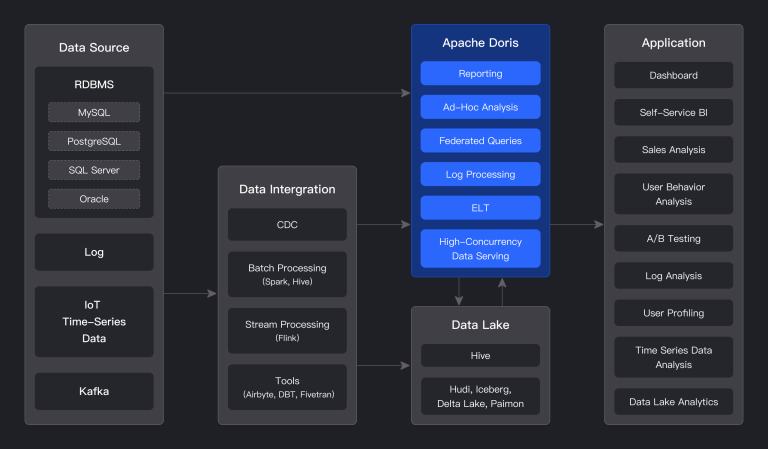
Apache Doris SQL Injection Vulnerability CVE-2025-66336 Apache Doris SQL injection diagram showing CVE-2025-66336 metadata query path bypass
  • Vulnerability Report

Apache Doris SQL Injection Vulnerability CVE-2025-66336

Do Son June 22, 2026 0

A critical Apache Doris SQL injection vulnerability identified as CVE-2025-66336 allows attackers to bypass authentication. Upgrade your servers now.

Microsoft Edge Google Account Login Coming Soon Microsoft Edge Google account login interface and synchronization settings Browser Choice Alliance letter Microsoft Edge cleartext credentials memory dump Microsoft Edge auto-startup Microsoft Edge Collections sunset, export Edge Collections CSV Edge IE Mode Zero-Day, Chakra Exploit Windows Search, Microsoft Edge AI video translation, Edge browser Microsoft Editor, Edge Edge Developer tools Windows 10 ESU, Microsoft Edge Microsoft Edge, FCP Optimization CVE-2023-36735 Edge, AI Search
  • Technology

Microsoft Edge Google Account Login Coming Soon

Do Son June 22, 2026 0

Discover how the upcoming Microsoft Edge Google account login feature will simplify authentication without directly syncing your data back to Chrome.
SHEETCREEP Malware Abuses Google Sheets API for Command-and-Control DCMTK vulnerabilities enabling path traversal file write in the DICOM toolkit (CVE-2026-50003)
  • Malware

SHEETCREEP Malware Abuses Google Sheets API for Command-and-Control

Do Son June 22, 2026 0

SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.

Google Tests reCAPTCHA Hand Gesture Verification reCAPTCHA hand gesture verification scanning process and biometric CAPTCHA security reCAPTCHA Data
  • Technology

Google Tests reCAPTCHA Hand Gesture Verification

Do Son June 22, 2026 0

Google is testing a new reCAPTCHA hand gesture verification system to combat AI bots. Discover how this camera-based authentication protects user privacy.
Microsoft Details Support Lifecycle for Windows 11 Version 26H2 Windows 11 version 26H2 support lifecycle and deployment roadmap for enterprise environments Windows 11 update anomaly Windows 11 context menu Windows 11 KB5089549 update error 0x800f0922 Windows 11 taskbar relocation
  • Windows

Microsoft Details Support Lifecycle for Windows 11 Version 26H2

Do Son June 22, 2026 0

Microsoft outlines the official support lifecycle and deployment guidelines for Windows 11 version 26H2, urging IT admins to prepare.

Gemini CLI Deprecation: Google Moves Developers to Antigravity CLI Gemini CLI deprecation notice as Google moves developers to the Antigravity CLI terminal tool Google Antigravity 2.0 release
  • Technology

Gemini CLI Deprecation: Google Moves Developers to Antigravity CLI

Do Son June 22, 2026 0

Google's Gemini CLI deprecation took effect on June 18, 2026. Personal accounts must now migrate to Antigravity CLI. See who's affected and why.

Windows Recycle Bin Bug Surfaces After the June 2026 Update Windows Recycle Bin bug showing an internal $Rxxxxx filename in the delete confirmation dialog after the June 2026 update
  • Windows

Windows Recycle Bin Bug Surfaces After the June 2026 Update

Do Son June 22, 2026 0

Microsoft confirms a Windows Recycle Bin bug in the June 2026 update that shows internal $R filenames when you delete a single file.

DragonForce Hides Backdoor C2 Inside Microsoft Teams TURN Relays North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Malware

DragonForce Hides Backdoor C2 Inside Microsoft Teams TURN Relays

Do Son June 22, 2026 0

DragonForce ransomware deployed Backdoor.Turn, a Microsoft Teams backdoor that hides C2 in Teams TURN relays. Symantec details the novel technique.

2,060 New CVEs and 4 Actively Exploited Flaws (June 15-21, 2026) Weekly CVE report dashboard showing 2,060 new vulnerabilities and 4 actively exploited CVEs in CISA KEV
  • Weekly Recap

2,060 New CVEs and 4 Actively Exploited Flaws (June 15-21, 2026)

Do Son June 22, 2026 0

This weekly CVE report covers 2,060 new vulnerabilities from June 15-21, including 358 critical flaws and 4 actively exploited CVEs now in CISA KEV.
Four undici Vulnerabilities Affect a Package With 133M Weekly Downloads undici vulnerabilities in the Node.js HTTP client affecting a package with 133M weekly downloads
  • Vulnerability Report

Four undici Vulnerabilities Affect a Package With 133M Weekly Downloads

Do Son June 22, 2026 0

Four undici vulnerabilities (CVE-2026-6734, CVE-2026-9697) affect the Node.js HTTP client, which sees 133M weekly downloads. Update undici now.

ErrTraffic Malware Spreads ClickFix Lures via Hacked WordPress Sites Spirals ransomware double extortion attack chain from IIS web shell to network encryption
  • Malware

ErrTraffic Malware Spreads ClickFix Lures via Hacked WordPress Sites

Do Son June 22, 2026 0

ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.
Avo Flaw CVE-2026-55518 Enables Privilege Escalation in Rails Apps Avo authorization bypass CVE-2026-55518 enabling privilege escalation in a Ruby on Rails admin panel
  • Vulnerability Report

Avo Flaw CVE-2026-55518 Enables Privilege Escalation in Rails Apps

Do Son June 22, 2026 0

CVE-2026-55518 is a critical Avo authorization bypass flaw enabling privilege escalation in Ruby on Rails admin panels. Update to Avo 3.32.1 now.

Three Critical pgAdmin 4 Vulnerabilities Patched: XSS, Auth Bypass, and AI Assistant SQLi pgAdmin 4 vulnerabilities CVE-2026-12046 stored XSS and RCE in PostgreSQL admin tool
  • Vulnerability Report

Three Critical pgAdmin 4 Vulnerabilities Patched: XSS, Auth Bypass, and AI Assistant SQLi

Do Son June 22, 2026 0

Three critical pgAdmin 4 vulnerabilities (CVE-2026-12046, CVE-2026-12048, CVE-2026-12045) risk XSS and RCE. Update to pgAdmin 4 9.16 now.

Public Exploit Released for FreeBSD kTLS Local Root Flaw CVE-2026-45257 FreeBSD kTLS vulnerability CVE-2026-45257 public PoC exploit enabling local privilege escalation to root
  • Vulnerability Report

Public Exploit Released for FreeBSD kTLS Local Root Flaw CVE-2026-45257

Do Son June 22, 2026 0

A public PoC exploit for the FreeBSD kTLS vulnerability (CVE-2026-45257) enables local privilege escalation to root. Patch your FreeBSD systems now.
QNAP Patches 14 Vulnerabilities in QTS, QuTS hero, and QVP Devices QNAP NAS vulnerabilities in QTS and QuTS hero firmware including command injection flaws from QSA-26-10
  • Vulnerability Report

QNAP Patches 14 Vulnerabilities in QTS, QuTS hero, and QVP Devices

Do Son June 21, 2026 0

QNAP patched 14 NAS vulnerabilities in QTS, QuTS hero, and QVP, including command injection and credential-theft flaws. Update your QNAP NAS now.

NPM Package Tests AI Malware Scanner Evasion Spirals ransomware double extortion attack chain from IIS web shell to network encryption
  • Malware

NPM Package Tests AI Malware Scanner Evasion

Do Son June 21, 2026 0

A new npm package uses prompt injection and token flooding for AI malware scanner evasion. Discover how attackers disrupt AI-assisted malware review.

Critical ArcGIS Account Recovery Targeted in Active Attacks Illustration of ArcGIS Account Recovery attacks highlighted in the latest security bulletin
  • Cybercriminals

Critical ArcGIS Account Recovery Targeted in Active Attacks

Do Son June 20, 2026 0

Attackers exploit ArcGIS Account Recovery flaws. Read this security bulletin to secure your enterprise by disabling default accounts and enabling SMTP.
Workplace Safety Checks Before Choosing a Laser Cleaning Machine Manufacturer dy
  • Technique

Workplace Safety Checks Before Choosing a Laser Cleaning Machine Manufacturer

Do Son June 20, 2026 0

Learn safety checks before choosing a laser cleaning machine manufacturer for rust removal, paint stripping, oxide removal, and industrial cleaning.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.