Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Device Code Phishing: Microsoft 365 Attack That Steals No Passwords Head Mare TrueConf attack PhantomCore backdoor diagram
  • Cybercriminals

Device Code Phishing: Microsoft 365 Attack That Steals No Passwords

Do Son June 20, 2026 0

A new device code phishing campaign abuses Microsoft's OAuth flow to hijack Microsoft 365 accounts, no password stealing needed. How to spot it.

GlassWASM Malware Hidden in Open VSX Extensions code
  • Malware

GlassWASM Malware Hidden in Open VSX Extensions

Do Son June 20, 2026 0

GlassWASM malware hides WebAssembly payloads in trojanized Open VSX extensions, abusing Solana memos for stealthy command-and-control.
How to Choose an HDD Transmitter for Deep and Complex Bores tech-pass
  • Technique

How to Choose an HDD Transmitter for Deep and Complex Bores

Do Son June 19, 2026 0
A transmitter with the highest advertised depth isn’t automatically the right choice for a difficult bore. Deep...
Read More Read more about How to Choose an HDD Transmitter for Deep and Complex Bores
Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections fi_5_e3ed09ff94_1_1781877042S8sPtX4e3f
  • Press Release

Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections

cybernewswire June 19, 2026 0
Luxembourg, Luxembourg, 19th June 2026, CyberNewswire
Read More Read more about Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections
eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks ChatGPT_Image_12__2026__14_15_31_1781266554PR1huQkj8c
  • Press Release

eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks

cybernewswire June 19, 2026 0
New York, USA, 19th June 2026, CyberNewswire
Read More Read more about eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks
UNC1151 ‘Ghostwriter’ Phishing Campaign Hijacks Gmail Accounts and 2FA Codes UNC1151 Gmail phishing fake Google login page stealing 2FA codes by Ghostwriter
  • Cybercriminals

UNC1151 ‘Ghostwriter’ Phishing Campaign Hijacks Gmail Accounts and 2FA Codes

Do Son June 19, 2026 0

The UNC1151 Gmail phishing campaign by Ghostwriter steals passwords and 2FA codes from Polish targets via fake Google login pages. Stay alert.

Interlock and Rhysida Ransomware: IBM X-Force Maps a Shared Ecosystem malware
  • Malware

Interlock and Rhysida Ransomware: IBM X-Force Maps a Shared Ecosystem

Do Son June 19, 2026 0

IBM X-Force links the Interlock and Rhysida ransomware ecosystem through shared malware like Supper, NodeSnake, and overlapping crypters.
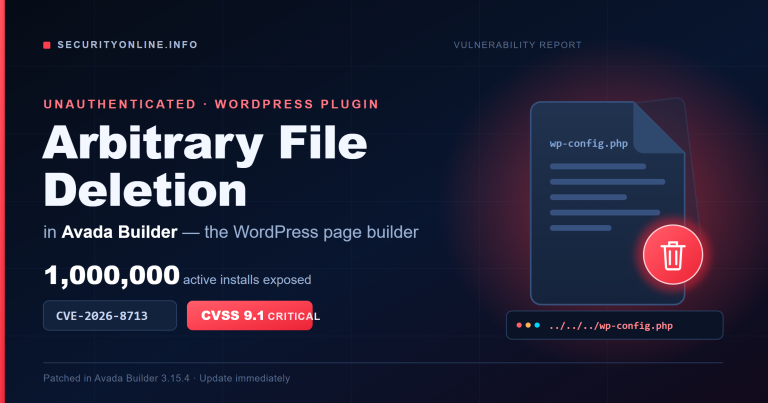
1M WordPress Sites at Risk: Critical Unauthenticated Arbitrary File Deletion in Avada Builder (CVSS 9.1) Avada Builder vulnerability CVE-2026-8713 unauthenticated arbitrary file deletion in WordPress
  • Vulnerability Report

1M WordPress Sites at Risk: Critical Unauthenticated Arbitrary File Deletion in Avada Builder (CVSS 9.1)

Do Son June 19, 2026 0

CVE-2026-8713 is a critical Avada Builder vulnerability enabling unauthenticated arbitrary file deletion on 1M WordPress sites. Update to 3.15.4 now.

APT37 NarwhalRAT Malware: A Python Backdoor Threat APT37 NarwhalRAT malware diagram
  • Malware

APT37 NarwhalRAT Malware: A Python Backdoor Threat

Do Son June 19, 2026 0

Discover how APT37 NarwhalRAT malware uses MS-themed phishing and a dead-drop C2 to target users with a sophisticated Python backdoor.

Google Calendar Adds 200 Custom Colors and a Full RGB Picker Google Calendar custom colors RGB picker event organization
  • Technology

Google Calendar Adds 200 Custom Colors and a Full RGB Picker

Do Son June 19, 2026 0

Google Calendar now offers 200 custom colors and a full RGB picker, replacing its old 11-color limit for events.

Claude Code Quota Reset Follows Morning Outage Claude Code quota reset notification displayed on a developer workstation screen
  • Technology

Claude Code Quota Reset Follows Morning Outage

Do Son June 19, 2026 0

Anthropic initiates a Claude Code quota reset for premium subscribers affected by a morning server glitch that erroneously blocked message transmissions.

Chrome Extension Vulnerabilities: Millions at Risk Illustration of Chrome extension vulnerabilities and hacker exploiting MaXSS and Spyder flaws
  • Vulnerability Report

Chrome Extension Vulnerabilities: Millions at Risk

Do Son June 19, 2026 0

Discover how the MaXSS and Spyder Chrome extension vulnerabilities in MaxAI and SiderAI put millions at risk. Protect your browser sessions today.

Apple Opens iOS to Third-Party App Stores in Brazil Under CADE Settlement iOS third-party app stores Brazil Apple CADE settlement
  • Technology

Apple Opens iOS to Third-Party App Stores in Brazil Under CADE Settlement

Do Son June 19, 2026 0

Apple now allows iOS third-party app stores in Brazil under a CADE settlement, alongside new fees and a Notarization review process.

F5 Patches Two Critical NGINX Flaws in HTTP/3 and HTTP/2 Modules (CVE-2026-42530, CVE-2026-42055) NGINX vulnerabilities CVE-2026-42530 HTTP/3 use-after-free and HTTP/2 buffer overflow
  • Vulnerability Report

F5 Patches Two Critical NGINX Flaws in HTTP/3 and HTTP/2 Modules (CVE-2026-42530, CVE-2026-42055)

Do Son June 19, 2026 0

Two critical NGINX vulnerabilities, CVE-2026-42530 and CVE-2026-42055, let remote attackers crash workers and possibly run code. Patch NGINX now.

Critical iba Deserialization Vulnerability Exposes ibaPDA and ibaDatCoordinator to RCE (CVE-2026-8024) iba deserialization vulnerability enabling remote code execution in ibaPDA and ibaDatCoordinator (CVE-2026-8024)
  • Vulnerability Report

Critical iba Deserialization Vulnerability Exposes ibaPDA and ibaDatCoordinator to RCE (CVE-2026-8024)

Do Son June 19, 2026 0

A critical iba deserialization vulnerability (CVE-2026-8024) lets unauthenticated attackers gain remote code execution on ibaPDA and ibaDatCoordinator.

27-Year-Old OpenBSD Authentication Bypass: Details and PoC Exploit Publicly Disclosed OpenBSD authentication bypass PoC exploit for the PPP PAP CVE-2026-55706 vulnerability
  • Vulnerability Report

27-Year-Old OpenBSD Authentication Bypass: Details and PoC Exploit Publicly Disclosed

Do Son June 19, 2026 0

A 27-year-old OpenBSD authentication bypass (CVE-2026-55706) is now public, with full details and a working PoC exploit for the PPP PAP flaw.
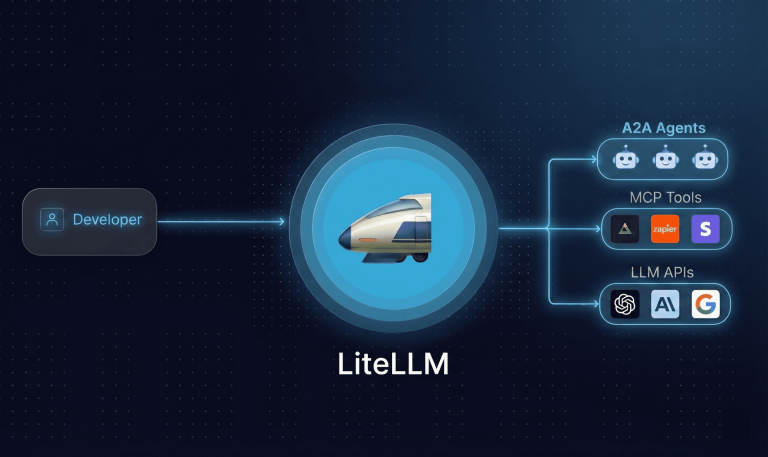
LiteLLM Authentication Bypass via Host Header Injection (CVE-2026-49468) LiteLLM authentication bypass via Host Header Injection in the AI Gateway proxy (CVE-2026-49468)
  • Vulnerability Report

LiteLLM Authentication Bypass via Host Header Injection (CVE-2026-49468)

Do Son June 19, 2026 0

A critical LiteLLM authentication bypass (CVE-2026-49468) lets crafted Host Header Injection reach protected AI Gateway routes. Patch in 1.84.0.

Langflow File Upload Flaw: Details and PoC Exploit Publicly Disclosed (CVE-2026-55450) Langflow file upload flaw enabling unauthenticated denial-of-service and path leak (CVE-2026-55450)
  • Vulnerability Report

Langflow File Upload Flaw: Details and PoC Exploit Publicly Disclosed (CVE-2026-55450)

Do Son June 19, 2026 0

A critical Langflow file upload flaw (CVE-2026-55450) is public with a PoC, enabling unauthenticated denial-of-service and path disclosure. Patch 1.9.1.

Rockwell Automation patches multiple ICS flaws Rockwell Automation vulnerabilities in FactoryTalk Historian and FLEX I/O EtherNet/IP adapters
  • Vulnerability Report

Rockwell Automation patches multiple ICS flaws

Do Son June 19, 2026 0

Rockwell Automation vulnerabilities affect FactoryTalk Historian and FLEX I/O adapters, including a critical unauthenticated password-change flaw.

Splunk CVE-2026-20253: CVSS 9.8 RCE Exploited in the Wild Splunk CVE-2026-20253 remote code execution vulnerability diagram
  • Vulnerability Report

Splunk CVE-2026-20253: CVSS 9.8 RCE Exploited in the Wild

Do Son June 18, 2026 0

CISA warns of Splunk CVE-2026-20253, a CVSS 9.8 Splunk Enterprise vulnerability exploited in the wild allowing pre-authenticated remote code execution.

Node.js Security Updates: Urgent Action Required Node.js security updates patch critical vulnerabilities
  • Vulnerability Report

Node.js Security Updates: Urgent Action Required

Do Son June 18, 2026 0

Protect your servers with the latest Node.js security updates. Patch critical vulnerabilities like CVE-2026-48933 to secure your infrastructure today.

Velvet Ant’s Operation Highland: A Decade Inside Critical Infrastructure Conti ransomware developer sentenced for extortion and wire fraud
  • Cybercriminals

Velvet Ant’s Operation Highland: A Decade Inside Critical Infrastructure

Do Son June 18, 2026 0

Velvet Ant ran Operation Highland for nearly a decade, backdooring PAM and OpenSSH to hide inside an isolated critical infrastructure network.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.