Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Apple Container 1.0: Native Linux VMs on Apple Silicon Apple Container 1.0, Apple Silicon Linux containers, lightweight virtual machines, OCI container images
  • Technology

Apple Container 1.0: Native Linux VMs on Apple Silicon

Do Son June 13, 2026 0

Apple releases the open-source Container 1.0.0 tool on GitHub, giving Apple Silicon Macs native, lightweight per-container Linux virtual machines.

Important Apache CXF Vulnerabilities Demand Immediate Action Apache CXF vulnerabilities, JNDI injection flaws, CVE-2026-50634, CVE-2026-50633, CVE-2026-50628 Apache CXF vulnerabilities
  • Vulnerability Report

Important Apache CXF Vulnerabilities Demand Immediate Action

Do Son June 13, 2026 0

Discover important Apache CXF vulnerabilities, including severe JNDI injection flaws. Patch CVE-2026-50634 and secure your network endpoints today.

Conti Ransomware Guilty Plea Marks Major Victory Against Cybercrime Conti ransomware guilty plea, ransomware attacks Deniss Zolotarjovs Sentencing Karakurt Ransomware Leader
  • Cybercriminals

Conti Ransomware Guilty Plea Marks Major Victory Against Cybercrime

Do Son June 12, 2026 0

A massive Conti ransomware guilty plea reveals how these devastating ransomware attacks extorted $150 million from thousands of global victims.
International Takedown Smashes Massive Crypto Laundering Service crypto laundering service ransomware gangs
  • Cybercriminals

International Takedown Smashes Massive Crypto Laundering Service

Do Son June 12, 2026 0

Authorities dismantled a major crypto laundering service used by ransomware gangs to wash millions. Read about the global AudiA6 dark web takedown.

Seizing Deepfake Porn Websites: Feds Disrupt Major Global Exploitation Ring seizing deepfake porn websites TAKE IT DOWN Act
  • Cybercriminals

Seizing Deepfake Porn Websites: Feds Disrupt Major Global Exploitation Ring

Do Son June 12, 2026 0

Federal authorities are seizing deepfake porn websites. This historic bust marks a massive win for enforcement of the new TAKE IT DOWN Act.

Operation TaxShadow: Tax Phishing Hides In-Memory Malware Operation TaxShadow, tax phishing malware, in-memory malware, WebSocket C2
  • Malware

Operation TaxShadow: Tax Phishing Hides In-Memory Malware

Do Son June 12, 2026 0

Operation TaxShadow uses fake tax notices to spread in-memory tax phishing malware with WebSocket C2, per CYFIRMA's new report.

Apple Removes the AFP Protocol in macOS 27 Apple AirPort Utility deprecated notice on legacy wireless routers AFP protocol macOS 27, SMB3 protocol, Apple Filing Protocol, file sharing protocol Apple WWDC 2026 announcements
  • Technology

Apple Removes the AFP Protocol in macOS 27

Do Son June 12, 2026 0

Apple removes the AFP protocol in macOS 27 after 40 years and urges users to switch to the modern SMB3 standard for secure, cross-platform file sharing.

iOS 27 AirDrop Speed Jumps 220% in New Tests iOS 27 AirDrop speed, AirDrop transfer speed, AirDrop file transfer, AWDL protocol iPhone 17e rumors iPhone Air 2 Roadmap Apple Launch Cadence Shift iPhone Air sales collapse Apple iPhone Fold iPhone Air, thinnest iPhone camera flaw
  • Technology

iOS 27 AirDrop Speed Jumps 220% in New Tests

Do Son June 12, 2026 0

Developers testing iOS 27 found AirDrop transfer speed up 220%, cutting a 3.5GB file transfer from 2 minutes 11 seconds down to just 41 seconds.

Pixel Reboot Loop Bug Hits Devices After Update Pixel reboot loop bug, Pixel factory reset, Pixel software update issue, Pixel boot loop fix Google Pixel 10a pre-order
  • Technology

Pixel Reboot Loop Bug Hits Devices After Update

Do Son June 12, 2026 0

Google confirms a Pixel reboot loop bug after March, April, and May updates, with no fix yet and support suggesting a factory reset that wipes user data.

Multiple Security Flaws Fixed in Major Framework Release CVE-2024-22257 Spring security vulnerabilities, cross-site scripting, CVE-2026-41003, CVE-2026-40999, CVE-2026-40998
  • Vulnerability Report

Multiple Security Flaws Fixed in Major Framework Release

Do Son June 12, 2026 0

New updates patch critical Spring security vulnerabilities, mitigating cross-site scripting and server-side request forgery risks across multiple versions.

Chrome 149 Patches 28 Flaws, Several Critical UAF Bugs Chrome security update, CVE-2026-12007, CVE-2026-12008, CVE-2026-12010 Chrome Security Update CVE-2026-1504 Chrome WebGPU Overflow, V8 RCE
  • Vulnerability Report

Chrome 149 Patches 28 Flaws, Several Critical UAF Bugs

Do Son June 12, 2026 0

Chrome security update to version 149 patches 28 flaws, including critical CVE-2026-12007, CVE-2026-12008, and CVE-2026-12010 bugs.
Critical 9.9 CVSS Ubiquiti UniFi OS Vulnerabilities Exposed UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Critical 9.9 CVSS Ubiquiti UniFi OS Vulnerabilities Exposed

Do Son June 12, 2026 0

Critical UniFi OS vulnerabilities boast a 9.9 CVSS score. Patch these Ubiquiti security flaws to prevent command injection and secure your network today.

ShinyHunters Strikes with Oracle PeopleSoft Exploit Oracle PeopleSoft exploit, CVE-2026-35273
  • Cybercriminals

ShinyHunters Strikes with Oracle PeopleSoft Exploit

Do Son June 12, 2026 0

ShinyHunters leverages a zero-day Oracle PeopleSoft exploit to compromise higher education systems, exposing sensitive data via the CVE-2026-35273 flaw.

New Patches Fix Broad AMD Security Vulnerabilities AMD security vulnerabilities, hardware security flaws, CVE-2025-54509, CVE-2025-10263 AMD GPU Price Hike GDDR Memory Costs CPU burnout, BIOS issues SQUIP AMD Ryzen AI vulnerability
  • Vulnerability Report

New Patches Fix Broad AMD Security Vulnerabilities

Do Son June 12, 2026 0

Fix critical AMD security vulnerabilities and hardware security flaws now. Learn about CVE-2025-54509 and CVE-2025-10263 updates.
Apache Answer Vulnerabilities and Security Flaws Fixed Apache Answer vulnerabilities, security flaws, CVE-2026-25688, CVE-2026-25700, CVE-2026-25699
  • Vulnerability Report

Apache Answer Vulnerabilities and Security Flaws Fixed

Do Son June 12, 2026 0

Fix critical Apache Answer vulnerabilities and security flaws today. Upgrade your platform to stay safe from unauthorized access and server crashes.

Millions at Risk: 9.8 CVSS Remote Code Execution in HTTP.sys HTTP.sys RCE vulnerability, Windows HTTP stack exploit, CVE-2026-47291 Netlogon RCE vulnerability Exploited in the wild Secure Boot certificate renewal 2026, Windows 11 UEFI update Community-First AI Infrastructure, Microsoft self-funding energy mandate aka.ms/aoh online portal CVE-2025-55681, Windows DWM Elevation Windows Administrator Protection, CVE-2025-60718 Microsoft AI Compute, IREN Infrastructure Microsoft Japan PPA, Renewable Energy Microsoft AI Investment, Cloud Expansion Microsoft Azure, Startup Credits Infinite Workday, AI in Work Microsoft Russia, Bankruptcy AI code generation, Microsoft AI Microsoft Layoffs, Restructuring
  • Vulnerability Report

Millions at Risk: 9.8 CVSS Remote Code Execution in HTTP.sys

Do Son June 12, 2026 0

A critical 9.8 CVSS HTTP.sys RCE vulnerability (CVE-2026-47291) threatens millions of users. Secure your Windows HTTP stack exploit risks now.

New Patches Secure Critical Spring HATEOAS Flaws Spring HATEOAS flaws, CVE-2026-41006, CVE-2026-41007 CVE-2024-22243 Spring CLI Vulnerability CVE-2026-22718
  • Vulnerability Report

New Patches Secure Critical Spring HATEOAS Flaws

Do Son June 12, 2026 0

New patches fix critical Spring HATEOAS flaws including CVE-2026-41006 and CVE-2026-41007 to prevent heap exhaustion and bypasses.
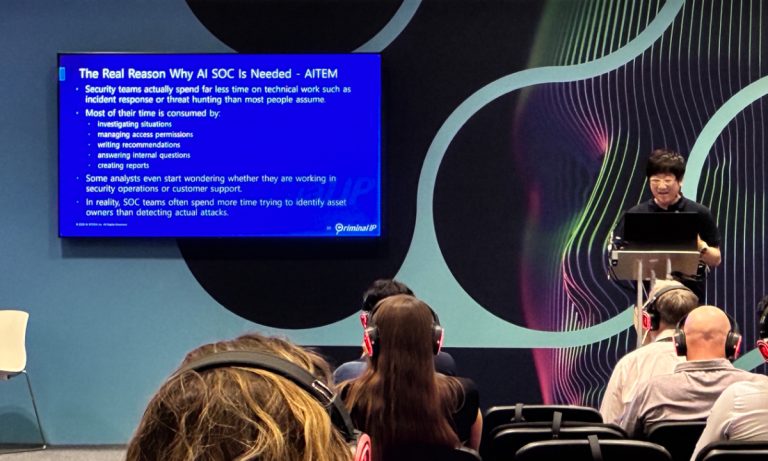
Criminal IP at Infosecurity Europe 2026: Introducing AITEM, the Next Chapter of Attack Surface Management Untitled_design_17810711059KKOaaIKEm
  • Press Release

Criminal IP at Infosecurity Europe 2026: Introducing AITEM, the Next Chapter of Attack Surface Management

cybernewswire June 11, 2026 0
Torrance, United States / California, 11th June 2026, CyberNewswire
Read More Read more about Criminal IP at Infosecurity Europe 2026: Introducing AITEM, the Next Chapter of Attack Surface Management
Top Custom Real Estate CRM Software Development Companies in the US tech-pass
  • Technique

Top Custom Real Estate CRM Software Development Companies in the US

Do Son June 11, 2026 0

Curated shortlist of 7 top custom real estate CRM software development companies in the US market in 2026. Picks for enterprise, mid-market, AI, and CRE.
Automated Remediation: Microsoft Resolves Cumulative Update Rollback Failures Windows 11 version 26H2 support lifecycle and deployment roadmap for enterprise environments Windows 11 update anomaly Windows 11 context menu Windows 11 KB5089549 update error 0x800f0922 Windows 11 taskbar relocation
  • Windows

Automated Remediation: Microsoft Resolves Cumulative Update Rollback Failures

Do Son June 11, 2026 0

Discover how to resolve the Windows 11 update anomaly. Learn how Microsoft updates trigger installation loops and how to fix them using manual DISM tools.
Parallel Diffusion: Google Unveils DiffusionGemma to Revolutionize On-Device Intelligence Google DiffusionGemma open framework
  • Technology

Parallel Diffusion: Google Unveils DiffusionGemma to Revolutionize On-Device Intelligence

Do Son June 11, 2026 0

Discover the new Google DiffusionGemma open framework. Learn how text diffusion bypasses memory limits to accelerate local inference benchmarks.
Multiple Security Flaws Addressed in Core Java Application Subsystems Spring GraphQL security patches, unsafe deserialization flaws, CVE-2026-41699, CVE-2026-41700, CVE-2026-41856 CVE-2023-34050
  • Vulnerability Report

Multiple Security Flaws Addressed in Core Java Application Subsystems

Do Son June 11, 2026 0

Deploy the latest Spring GraphQL security patches to remediate critical unsafe deserialization flaws and cross-site WebSocket hijacking vulnerabilities.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-77876CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.16 contains an OS command injection vulnerability in the protected_directory user panel...
    📅 Updated: Nov 3, 2026
  • CVE-2026-73696CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.12 contains an execution after redirect vulnerability in the user panel authentication...
    📅 Updated: Nov 3, 2026
  • CVE-2026-58256CVSS 9.1
    GRR is a resource management and reservation application. Prior to the advisory-reported fixed version 4.5.0, an administrator can...
    📅 Updated: Nov 3, 2026
  • CVE-2026-115904CVSS 9.6
    Topluyo is a social networking platform. A vulnerability exists in Topluyo Desktop for Linux prior to version 2026.9.2410...
    📅 Updated: Nov 3, 2026
  • CVE-2026-118375CVSS 9.2
    llama.cpp b8841 before b11865 contains an out-of-bounds write vulnerability in the ggml-rpc RDMA transport rdma_recv() function that allows...
    📅 Updated: Nov 3, 2026
  • CVE-2026-54749CVSS 9.4
    Summary Three custom API-Platform controllers under `src/CoreBundle/Controller/Api/` perform privileged mutations but enforce only a global platform role (`ROLE_TEACHER`)...
    📅 Updated: Nov 3, 2026
  • CVE-2026-89292CVSS 9.2
    In Eclipse Mnestix Browser versions 1.6.0 up until but excluding 2.3.0 it was possible for an unauthenticated attacker...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121022CVSS 9.2
    Use of Default Password (CWE-1393) in the web client in AxxonSoft Axxon One before 3.0.0 on Windows and...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.