
 Do Son
Mandiant details the UNC3753 vishing campaign targeting US law firms with fake IT calls, RMM abuse, and rapid data theft extortion.
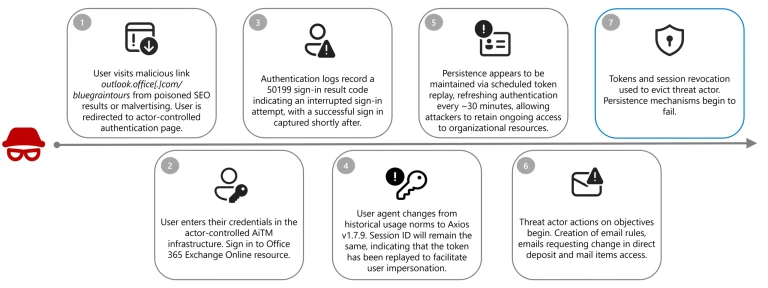
The active Payroll Pirate campaign uses AiTM session hijacking and token replay to target corporate payroll and HR personnel across multiple industries.
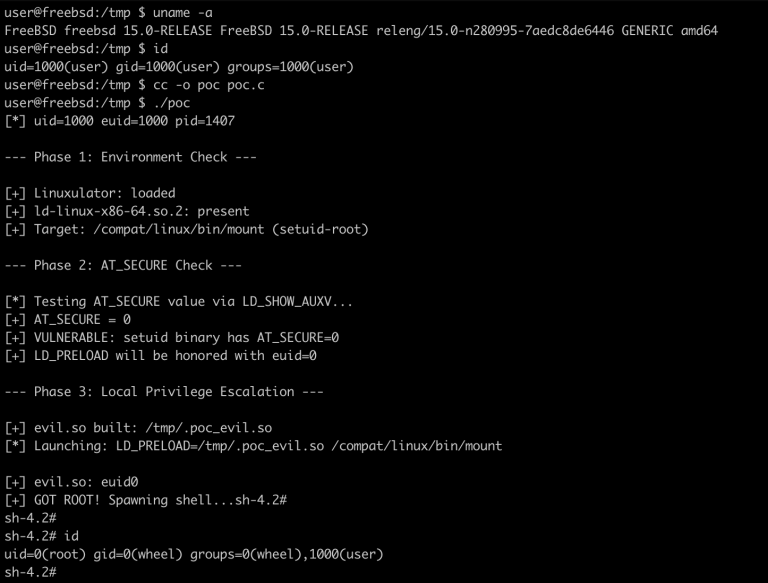
A FreeBSD privilege escalation flaw (CVE-2026-49413) in the Linuxulator lets local users get root. Public PoC exploit code makes patching urgent.

Two critical FreePBX RCE vulnerabilities in Superfecta and UCP modules expose servers to authenticated arbitrary code execution and command injection.

Use our Anthropic Claude refund guide to navigate the recent export ban. Discover eligibility rules, prorated details, and hidden Apple IAP risks.
The official Linux Kernel 7.1 release delivers critical stability enhancements and minor driver fixes. Learn about the new NTFS driver and Zen 6 support.
OpenAI introduces a flexible Codex rate limit reset mechanism for premium subscribers to maximize quotas and counter Claude Code competition.

Microsoft is rolling out Windows 11 app updates via Insider builds, bringing new features to Calculator, Camera, Photos, and more.
Meta is rolling out AI usage limits for employees after token costs threatened to reach billions of dollars in 2026.

Anthropic suspended Claude Fable access due to a strict US export ban. Discover the impact on foreign users and the ongoing debate over AI jailbreaking.

Public details and PoC exploit code expose a critical Wazuh CVSS 10 vulnerability allowing attackers to smuggle OpenSearch bulk operations.

A patched WinRAR vulnerability in Ukraine is still exploited via CVE-2025-8088 to deploy GIFTEDCROOK and espionage tools, says Trend Micro.

Read our weekly threat intelligence briefing. This vulnerability management report covers active exploits in Cisco, Ivanti, and Chrome for June 2026.

Fixes roll out as vulnerable UEFI shim bootloaders allow attackers to achieve a critical Secure Boot bypass prior to OS initialization.

A critical CodeIgniter vulnerability (CVE-2026-48062, CVSS 9.8) lets attackers bypass upload checks and trigger arbitrary code execution. Update now.

A whole class of attacks — DDoS, expired TLS certs, DNS hijacking, dead security jobs — surfaces first as an availability anomaly. How to catch them early.

Financial services companies do not verify identity only to open accounts. They verify identity to protect money...

Discover how the iOS 27 Apple Pay redesign eliminates checkout friction with intuitive gestures, grid layouts, and integrated financial insights.
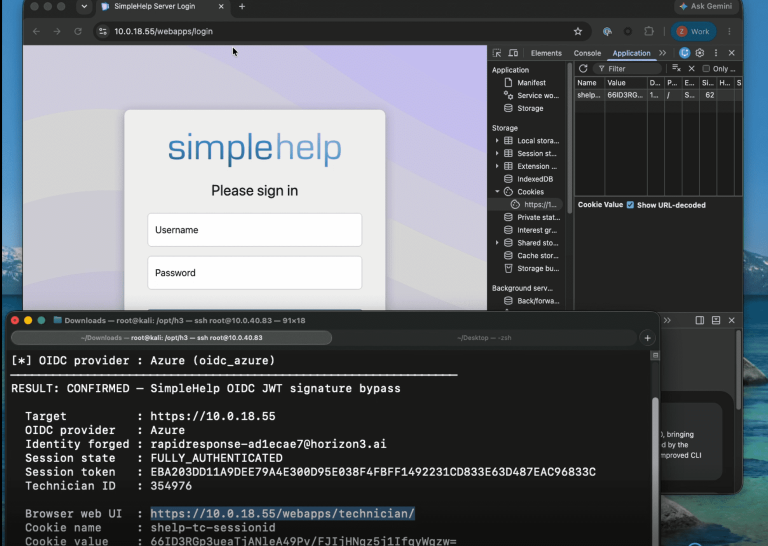
A critical SimpleHelp authentication bypass flaw leaves servers open. Attackers exploit the OIDC authentication flow to gain technician control.

New updates patch critical Squid proxy vulnerabilities. Secure your server against a heap buffer overflow attack and out-of-bounds reads today.

Discover how malicious Chrome extensions engage in traffic laundering while lying to users about collecting data on the official store.
Apple's Craig Federighi and Greg Joswiak discuss Apple Intelligence, agentic password security, child safety, and why Siri won't be a romantic AI companion.