Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Cryptographic Expiration: Microsoft Office 2019 for Mac Faces Imminent Functionality Restrictions Office 2019 Mac read only Microsoft Office Startup Boost Office 2016 update KB5002700
  • Technology

Cryptographic Expiration: Microsoft Office 2019 for Mac Faces Imminent Functionality Restrictions

Do Son June 11, 2026 0

Discover why your Office 2019 Mac read only state triggers in July 2026. Learn about expired licensing tokens and how to migrate your software.
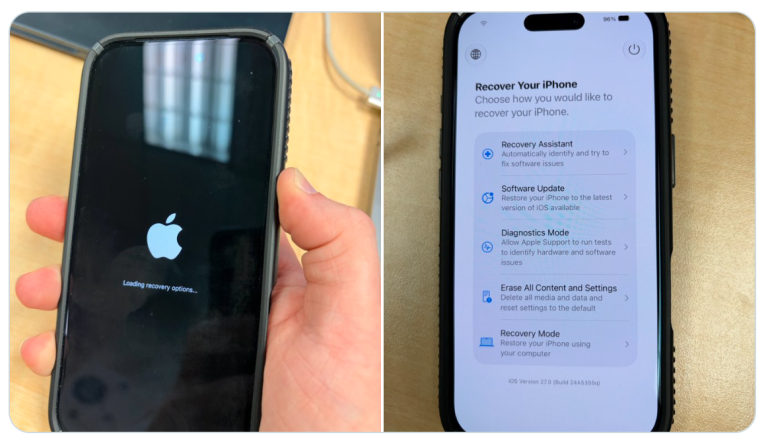
Untethered Diagnostics: iOS 27 Introduces On-Device Recovery Mode iOS 27 Recovery Mode
  • Technology

Untethered Diagnostics: iOS 27 Introduces On-Device Recovery Mode

Do Son June 11, 2026 0

Discover the new iOS 27 Recovery Mode features. Learn how the built-in tools fix software issues without needing a computer connection.

Fiscal Realignment: OpenAI Contemplates Sweeping Price Reductions to Counter Anthropic OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

Fiscal Realignment: OpenAI Contemplates Sweeping Price Reductions to Counter Anthropic

Do Son June 11, 2026 0

Discover the proposed OpenAI token price reduction. Learn how the enterprise plans to cut costs to compete with Anthropic ahead of its upcoming IPO.

Sovereign Intervention: EU Mandates Unhindered Third-Party AI Access to WhatsApp API WhatsApp antitrust API probe India SIM-Binding Mandate Messaging App KYC WhatsApp DMA Interoperability BirdyChat Haiket Denmark Social Media Ban CVE-2025-55177 WhatsApp vulnerability, zero-click flaw npm Malware, System Wipe WhatsApp Windows App, WebView2 Downgrade WhatsApp Ban, US House NSO WhatsApp, Pegasus Spyware WhatsApp iPad iPadOS app
  • Technology

Sovereign Intervention: EU Mandates Unhindered Third-Party AI Access to WhatsApp API

Do Son June 11, 2026 0

Discover the latest WhatsApp antitrust API probe. Learn how the European Union forces Meta to reopen its business network to external AI chatbots for free.
PeopleSoft RCE Security Bug: New Oracle Fix PeopleSoft RCE security bug, unauthenticated HTTP exploit, CVE-2026-35273 Oracle security patch updates critical software vulnerabilities
  • Vulnerability Report

PeopleSoft RCE Security Bug: New Oracle Fix

Do Son June 11, 2026 0

A critical PeopleSoft RCE security bug allows an unauthenticated HTTP exploit to execute code. Learn how to patch CVE-2026-35273 immediately.

Splunk Enterprise Vulnerabilities: Patch CVSS 9.8 Flaws Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Enterprise Vulnerabilities: Patch CVSS 9.8 Flaws

Do Son June 11, 2026 0

A CVSS 9.8 flaw highlights new Splunk Enterprise vulnerabilities. Patch CVE-2026-20253, CVE-2026-20251, and others to prevent remote attacks on your servers.
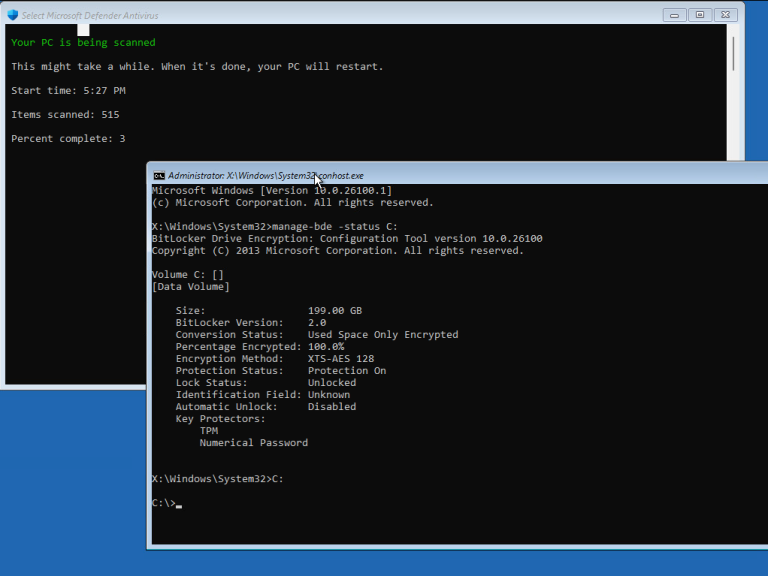
GreatXML BitLocker Bypass: Public PoC Exploit Disclosed GreatXML BitLocker bypass, Windows Defender vulnerability
  • Vulnerability Report

GreatXML BitLocker Bypass: Public PoC Exploit Disclosed

Do Son June 11, 2026 0

A new GreatXML BitLocker bypass PoC exploit is publicly disclosed. Learn how this Windows Defender vulnerability grants unrestricted volume access.

Dahua Product Vulnerabilities: Patch 3 Critical CVEs Dahua product vulnerabilities, Dahua security advisory, CVE-2026-29114, CVE-2026-29115, CVE-2026-29116 Dahua IP Camera, Buffer Overflow Dahua IP cameras vulnerability
  • Vulnerability Report

Dahua Product Vulnerabilities: Patch 3 Critical CVEs

Do Son June 11, 2026 0

A new Dahua security advisory warns of critical Dahua product vulnerabilities, including CVE-2026-29116. Update your IPC and SD devices to prevent DoS attacks.
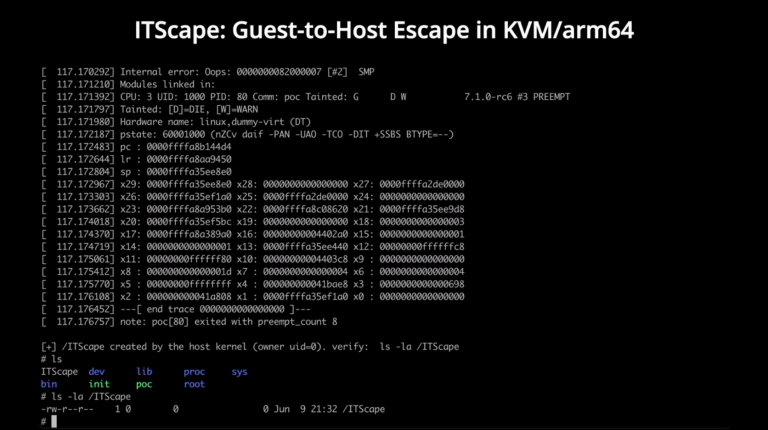
ITScape KVM Escape: Public PoC Exploit Threatens Cloud Hosts ITScape KVM escape vulnerability, guest-to-host escape exploit, CVE-2026-46316
  • Vulnerability Report

ITScape KVM Escape: Public PoC Exploit Threatens Cloud Hosts

Do Son June 11, 2026 0

The ITScape KVM escape vulnerability (CVE-2026-46316) threatens arm64 clouds. Details and a guest-to-host escape exploit PoC are now publicly disclosed.

Critical Jenkins Security Advisory 2026: Patch Multiple Flaws Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability Report

Critical Jenkins Security Advisory 2026: Patch Multiple Flaws

Do Son June 11, 2026 0

A critical Jenkins security advisory 2026 warns of deserialization and XSS flaws like CVE-2026-53435. Patch your CI/CD pipelines immediately!

Important GitLab Security Updates Address 12 Vulnerabilities GitLab security updates, GitLab patch release, CVE-2026-6552, CVE-2026-10087, CVE-2026-7250 GitLab Security Update May 2026 GitLab XSS and DoS Vulnerabilities GitLab Security Session Hijacking GitLab Security Update, CI/CD Vulnerability GitLab DoS, Security Update bypassing SAML - CVE-2024-8312 and CVE-2024-6826
  • Vulnerability Report

Important GitLab Security Updates Address 12 Vulnerabilities

Do Son June 11, 2026 0

Discover the latest GitLab security updates in patch release 19.0.2. Protect your self-managed servers from critical vulnerabilities like CVE-2026-6552.
Critical NVIDIA DALI Vulnerabilities Require Immediate Action NVIDIA NeMo vulnerability CVE-2026-24155, CVE-2026-24252, CVE-2026-24228, code injection NVIDIA DALI vulnerabilities NVIDIA Driver Security Update CVE-2026-24187 Linux
  • Vulnerability Report

Critical NVIDIA DALI Vulnerabilities Require Immediate Action

Do Son June 11, 2026 0

Severe NVIDIA DALI vulnerabilities allow remote code execution and data tampering. Learn how to secure your systems against the CVE-2026-24180 exploit today.

PhpSpreadsheet RCE Vulnerability: PoC Exploit Disclosed for 312 Million Users CVE-2026-45034 exploit PhpSpreadsheet RCE vulnerability PhpSpreadsheet CVE-2025-54370
  • Vulnerability Report

PhpSpreadsheet RCE Vulnerability: PoC Exploit Disclosed for 312 Million Users

Do Son June 11, 2026 0

A critical PhpSpreadsheet RCE vulnerability impacts 312 million users. Learn how the CVE-2026-45034 exploit bypasses patches and triggers code execution.

strongSwan CVE-2026-47895: Double-Free Exploit Explained libstrongswan double-free exploit strongSwan CVE-2026-47895 CVE-2023-41913 strongSwan Vulnerability VPN Denial of Service
  • Vulnerability Report

strongSwan CVE-2026-47895: Double-Free Exploit Explained

Do Son June 11, 2026 0

A new strongSwan CVE-2026-47895 vulnerability allows remote code execution via a libstrongswan double-free exploit. Patch your VPN servers now!

Spring Data Vulnerabilities: Patch Five Critical Flaws Now Spring Data vulnerabilities Spring Cloud Config CVE-2026-22739 Spring Gateway SpEL, STOMP WebSocket CSRF Spring Security, vulnerability CVE-2024-38819 CVE-2025-41243 Spring Cloud Gateway, vulnerability
  • Vulnerability Report

Spring Data Vulnerabilities: Patch Five Critical Flaws Now

Do Son June 11, 2026 0

Five new Spring Data vulnerabilities threaten applications with SpEL expression injection and DoS attacks. Upgrade your Spring frameworks immediately!
Critical UpdraftPlus CVE-2026-10795 Exploit Targets Millions UpdraftPlus CVE-2026-10795, UpdraftPlus authentication bypass, WordPress plugin vulnerability, CVE-2026-10795
  • Vulnerability Report

Critical UpdraftPlus CVE-2026-10795 Exploit Targets Millions

Do Son June 10, 2026 0

A critical UpdraftPlus CVE-2026-10795 vulnerability threatens 3 million sites. Hackers are exploiting this UpdraftPlus authentication bypass in the wild.
Cloud Security Report Finds Fragmented Tools Widening the Cloud Complexity Gap Featured-Image-new_1780946080xcAbTTR9Sc
  • Press Release

Cloud Security Report Finds Fragmented Tools Widening the Cloud Complexity Gap

cybernewswire June 10, 2026 0
Washington D.C., USA, 10th June 2026, CyberNewswire
Read More Read more about Cloud Security Report Finds Fragmented Tools Widening the Cloud Complexity Gap
VerdantBamboo Malware Campaign Targets Edge Devices via Supply Chain Breach VerdantBamboo malware campaign Volexity threat report
  • Cyber Security
  • Malware

VerdantBamboo Malware Campaign Targets Edge Devices via Supply Chain Breach

Do Son June 10, 2026 0

Discover how the stealthy VerdantBamboo malware campaign infiltrates network edge devices in this comprehensive Volexity threat report.

Regulatory Alignment: Let’s Encrypt Amends Subscriber Agreement to Enforce US Sanctions and Export Compliance Let's Encrypt subscriber agreement Let's Encrypt OCSP Support 45-Day Certificate Limit Let's Encrypt Automation
  • Technology

Regulatory Alignment: Let’s Encrypt Amends Subscriber Agreement to Enforce US Sanctions and Export Compliance

Do Son June 10, 2026 0

Discover the new Let's Encrypt subscriber agreement changes. Learn how Version 1.7 integrates U.S. sanctions compliance for global SSL domains.
Algorithmic Acceleration: Microsoft Deploys Low-Latency Core Profiles via KB5094126 Cumulative Update Windows 11 CPU optimization Microsoft Windows user engagement
  • Windows

Algorithmic Acceleration: Microsoft Deploys Low-Latency Core Profiles via KB5094126 Cumulative Update

Do Son June 10, 2026 0

Discover the new Windows 11 CPU optimization in KB5094126. Learn how dynamic frequency scaling reduces interface latency and how to enable it.
Algorithmic Fluency: Google Unveils Gemini 3.5 Live Translate for Real-Time Audiocentric Mediation Gemini Live Translate tool
  • Technology

Algorithmic Fluency: Google Unveils Gemini 3.5 Live Translate for Real-Time Audiocentric Mediation

Do Son June 10, 2026 0

Discover the new Gemini Live Translate tool from Google. Learn how this low-latency vocal model translates over 70 languages seamlessly in real time.

Deprecating the Legacy: Google Chrome Initiates Final Removal of Manifest v2 Architecture Chrome Manifest v3 migration
  • Technology

Deprecating the Legacy: Google Chrome Initiates Final Removal of Manifest v2 Architecture

Do Son June 10, 2026 0

Discover the final Chrome Manifest v3 migration timeline. Learn how Google updates remove legacy MV2 flags and permanently disable classic ad blockers.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-44267CVSS 9.8
    Elo is a purely functional expression language for no-code tools. Prior to 1.0.1, plain Elo strings supplied to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-44266CVSS 9.8
    Elo is a purely functional expression language for no-code tools. Prior to 1.0.1, the Ruby backend in src/compilers/ruby.ts...
    📅 Updated: Nov 3, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 3, 2026
  • CVE-2026-91495CVSS 9.8
    Vulnerability in the Oracle WebCenter Content product of Oracle Fusion Middleware (component: Content Server). Supported versions that are...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64523CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net/handshake: Take a long-lived file reference at submit...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64459CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: tcp: restore RCU grace period in tcp_ao_destroy_sock Commit...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64530CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net/sched: cls_api: Handle TC_ACT_CONSUMED in tcf_qevent_handle tcf_classify() can...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64534CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: nvmet-tcp: check INIT_FAILED before nvmet_req_uninit in digest error...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.