Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Vulnerable UEFI Shim Bootloaders Risk Broad Secure Boot Bypass vulnerable UEFI shim bootloaders, Secure Boot bypass UEFI Secure Boot, Critical Vulnerability CVE-2025-3052
  • Vulnerability Report

Vulnerable UEFI Shim Bootloaders Risk Broad Secure Boot Bypass

Do Son June 15, 2026 0

Fixes roll out as vulnerable UEFI shim bootloaders allow attackers to achieve a critical Secure Boot bypass prior to OS initialization.

CodeIgniter Vulnerability Enables Arbitrary Code Execution (CVSS 9.8) CodeIgniter vulnerability, arbitrary code execution, CVE-2026-48062, CVE-2024-47823 CVE-2023-32692 CodeIgniter RCE, ImageMagick Vulnerability
  • Vulnerability Report

CodeIgniter Vulnerability Enables Arbitrary Code Execution (CVSS 9.8)

Do Son June 15, 2026 0

A critical CodeIgniter vulnerability (CVE-2026-48062, CVSS 9.8) lets attackers bypass upload checks and trigger arbitrary code execution. Update now.

When Downtime Is a Security Signal: Catching Attacks in the Availability Layer Ragic Enterprise Cloud Database - CVE-2024-9983 - CVE-2024-9984 - CVE-2024-9985
  • Technique

When Downtime Is a Security Signal: Catching Attacks in the Availability Layer

Do Son June 14, 2026 0

A whole class of attacks — DDoS, expired TLS certs, DNS hijacking, dead security jobs — surfaces first as an availability anomaly. How to catch them early.

7 Best AI Identity Verification Vendors for Financial Services tech-kyc
  • Technique

7 Best AI Identity Verification Vendors for Financial Services

Do Son June 14, 2026 0
Financial services companies do not verify identity only to open accounts. They verify identity to protect money...
Read More Read more about 7 Best AI Identity Verification Vendors for Financial Services
Elegant Reimagining of Apple Pay in iOS 27 iOS 27 Apple Pay, Apple Pay interface, Apple Wallet update
  • Technology

Elegant Reimagining of Apple Pay in iOS 27

Do Son June 14, 2026 0

Discover how the iOS 27 Apple Pay redesign eliminates checkout friction with intuitive gestures, grid layouts, and integrated financial insights.
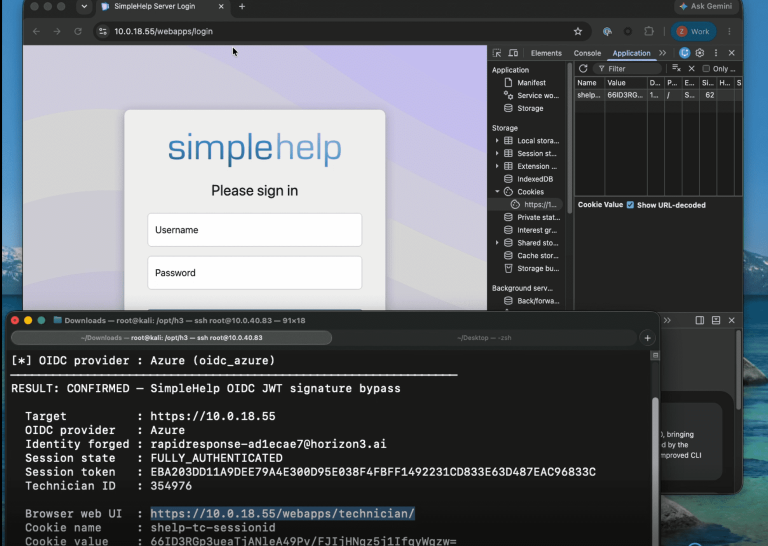
SimpleHelp Authentication Bypass Exploited to Hijack Remote Endpoints SimpleHelp authentication bypass, OIDC authentication flow
  • Vulnerability Report

SimpleHelp Authentication Bypass Exploited to Hijack Remote Endpoints

Do Son June 13, 2026 0

A critical SimpleHelp authentication bypass flaw leaves servers open. Attackers exploit the OIDC authentication flow to gain technician control.

Critical Squid Proxy Vulnerabilities Patched in Latest Release Squid proxy vulnerabilities, buffer overflow attack Squid Credentials Leak, HTTP Authentication Redaction CVE-2024-25111
  • Vulnerability Report

Critical Squid Proxy Vulnerabilities Patched in Latest Release

Do Son June 13, 2026 0

New updates patch critical Squid proxy vulnerabilities. Secure your server against a heap buffer overflow attack and out-of-bounds reads today.

Malicious Chrome Extensions Exposed in Mass Production Traffic Fraud Scheme malicious Chrome extensions, traffic laundering #ChromeExtensions
  • Malware

Malicious Chrome Extensions Exposed in Mass Production Traffic Fraud Scheme

Do Son June 13, 2026 0

Discover how malicious Chrome extensions engage in traffic laundering while lying to users about collecting data on the official store.
Apple Execs Reveal Their AI Philosophy at WWDC 2026 Apple Intelligence philosophy, Craig Federighi interview, Apple AI privacy, Siri AI companion iOS 27 AI Extensions
  • Technology

Apple Execs Reveal Their AI Philosophy at WWDC 2026

Do Son June 13, 2026 0

Apple's Craig Federighi and Greg Joswiak discuss Apple Intelligence, agentic password security, child safety, and why Siri won't be a romantic AI companion.

Apple Container 1.0: Native Linux VMs on Apple Silicon Apple Container 1.0, Apple Silicon Linux containers, lightweight virtual machines, OCI container images
  • Technology

Apple Container 1.0: Native Linux VMs on Apple Silicon

Do Son June 13, 2026 0

Apple releases the open-source Container 1.0.0 tool on GitHub, giving Apple Silicon Macs native, lightweight per-container Linux virtual machines.

Important Apache CXF Vulnerabilities Demand Immediate Action Apache CXF vulnerabilities, JNDI injection flaws, CVE-2026-50634, CVE-2026-50633, CVE-2026-50628 Apache CXF vulnerabilities
  • Vulnerability Report

Important Apache CXF Vulnerabilities Demand Immediate Action

Do Son June 13, 2026 0

Discover important Apache CXF vulnerabilities, including severe JNDI injection flaws. Patch CVE-2026-50634 and secure your network endpoints today.

Conti Ransomware Guilty Plea Marks Major Victory Against Cybercrime Conti ransomware guilty plea, ransomware attacks Deniss Zolotarjovs Sentencing Karakurt Ransomware Leader
  • Cybercriminals

Conti Ransomware Guilty Plea Marks Major Victory Against Cybercrime

Do Son June 12, 2026 0

A massive Conti ransomware guilty plea reveals how these devastating ransomware attacks extorted $150 million from thousands of global victims.
International Takedown Smashes Massive Crypto Laundering Service crypto laundering service ransomware gangs
  • Cybercriminals

International Takedown Smashes Massive Crypto Laundering Service

Do Son June 12, 2026 0

Authorities dismantled a major crypto laundering service used by ransomware gangs to wash millions. Read about the global AudiA6 dark web takedown.

Seizing Deepfake Porn Websites: Feds Disrupt Major Global Exploitation Ring seizing deepfake porn websites TAKE IT DOWN Act
  • Cybercriminals

Seizing Deepfake Porn Websites: Feds Disrupt Major Global Exploitation Ring

Do Son June 12, 2026 0

Federal authorities are seizing deepfake porn websites. This historic bust marks a massive win for enforcement of the new TAKE IT DOWN Act.

Operation TaxShadow: Tax Phishing Hides In-Memory Malware Operation TaxShadow, tax phishing malware, in-memory malware, WebSocket C2
  • Malware

Operation TaxShadow: Tax Phishing Hides In-Memory Malware

Do Son June 12, 2026 0

Operation TaxShadow uses fake tax notices to spread in-memory tax phishing malware with WebSocket C2, per CYFIRMA's new report.

Apple Removes the AFP Protocol in macOS 27 Apple AirPort Utility deprecated notice on legacy wireless routers AFP protocol macOS 27, SMB3 protocol, Apple Filing Protocol, file sharing protocol Apple WWDC 2026 announcements
  • Technology

Apple Removes the AFP Protocol in macOS 27

Do Son June 12, 2026 0

Apple removes the AFP protocol in macOS 27 after 40 years and urges users to switch to the modern SMB3 standard for secure, cross-platform file sharing.

iOS 27 AirDrop Speed Jumps 220% in New Tests iOS 27 AirDrop speed, AirDrop transfer speed, AirDrop file transfer, AWDL protocol iPhone 17e rumors iPhone Air 2 Roadmap Apple Launch Cadence Shift iPhone Air sales collapse Apple iPhone Fold iPhone Air, thinnest iPhone camera flaw
  • Technology

iOS 27 AirDrop Speed Jumps 220% in New Tests

Do Son June 12, 2026 0

Developers testing iOS 27 found AirDrop transfer speed up 220%, cutting a 3.5GB file transfer from 2 minutes 11 seconds down to just 41 seconds.

Pixel Reboot Loop Bug Hits Devices After Update Pixel reboot loop bug, Pixel factory reset, Pixel software update issue, Pixel boot loop fix Google Pixel 10a pre-order
  • Technology

Pixel Reboot Loop Bug Hits Devices After Update

Do Son June 12, 2026 0

Google confirms a Pixel reboot loop bug after March, April, and May updates, with no fix yet and support suggesting a factory reset that wipes user data.

Multiple Security Flaws Fixed in Major Framework Release CVE-2024-22257 Spring security vulnerabilities, cross-site scripting, CVE-2026-41003, CVE-2026-40999, CVE-2026-40998
  • Vulnerability Report

Multiple Security Flaws Fixed in Major Framework Release

Do Son June 12, 2026 0

New updates patch critical Spring security vulnerabilities, mitigating cross-site scripting and server-side request forgery risks across multiple versions.

Chrome 149 Patches 28 Flaws, Several Critical UAF Bugs Chrome security update, CVE-2026-12007, CVE-2026-12008, CVE-2026-12010 Chrome Security Update CVE-2026-1504 Chrome WebGPU Overflow, V8 RCE
  • Vulnerability Report

Chrome 149 Patches 28 Flaws, Several Critical UAF Bugs

Do Son June 12, 2026 0

Chrome security update to version 149 patches 28 flaws, including critical CVE-2026-12007, CVE-2026-12008, and CVE-2026-12010 bugs.
Critical 9.9 CVSS Ubiquiti UniFi OS Vulnerabilities Exposed UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Critical 9.9 CVSS Ubiquiti UniFi OS Vulnerabilities Exposed

Do Son June 12, 2026 0

Critical UniFi OS vulnerabilities boast a 9.9 CVSS score. Patch these Ubiquiti security flaws to prevent command injection and secure your network today.

ShinyHunters Strikes with Oracle PeopleSoft Exploit Oracle PeopleSoft exploit, CVE-2026-35273
  • Cybercriminals

ShinyHunters Strikes with Oracle PeopleSoft Exploit

Do Son June 12, 2026 0

ShinyHunters leverages a zero-day Oracle PeopleSoft exploit to compromise higher education systems, exposing sensitive data via the CVE-2026-35273 flaw.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.