
 Do Son
Security researcher Asim Manizada has released public details and a PoC for the CIFSwitch local root exploit impacting many Linux systems.
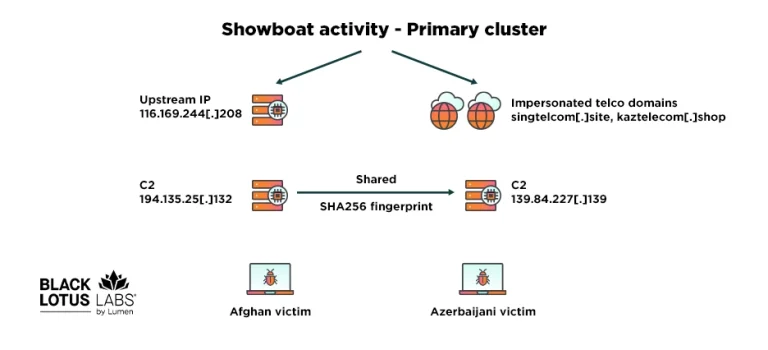
Discover the new Showboat Linux malware framework uncovered by Black Lotus Labs. Learn how PRC threat actors target telecommunications networks.
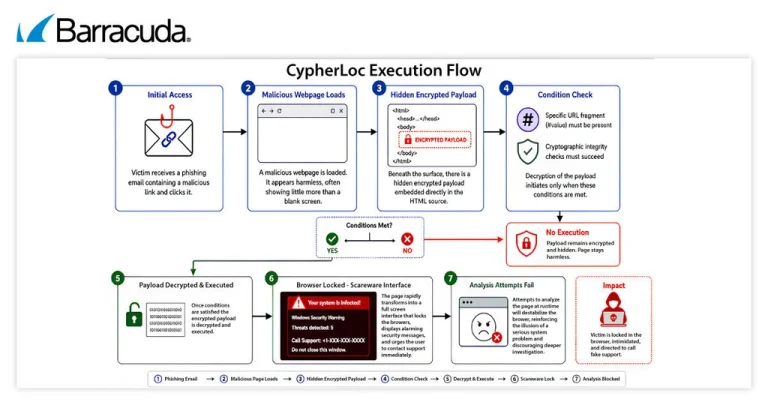
Barracuda Research warns of the CypherLoc scareware kit. Learn how this browser-locking threat uses psychological manipulation to scam users.
OpenAI confirms an upcoming legacy model deprecation on June 2, retiring GPT-5.2 and GPT-5.3-Codex from ChatGPT while forcing a shift to GPT-5.5.

Arctic Wolf warns of a new FortiClient EMS exploitation campaign using CVE-2026-35616 to deploy the stealthy EKZ Infostealer malware.

Users uncover a weird Motorola Smart Feed redirect that forces the Amazon app through third-party tracking links. Motorola claims it was a glitch and fixed it.
A critical Windows DNS Client RCE vulnerability (CVE-2026-41096) with a 9.8 CVSS has public PoC exploit code. Learn how to detect and patch it.
IBM patched a critical IBM Jazz Foundation vulnerability (CVE-2026-3660) with a 9.8 CVSS score. Learn how to secure your property files now.
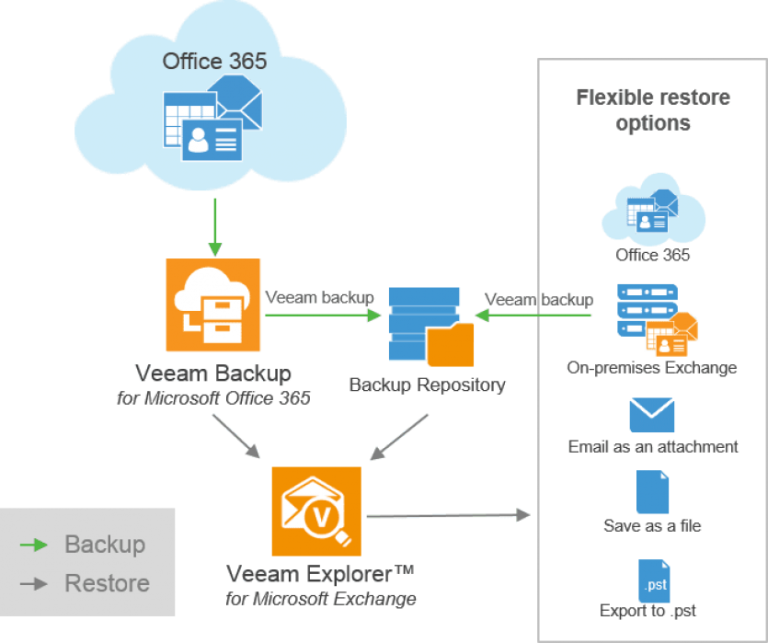
Learn about the new Veeam security vulnerabilities, including a critical 9.4 RCE flaw in Service Provider Console, and how to patch your systems.

OpenAI subscription quota changes take effect June 2026 as the double-allocation promo ends. Learn how your Codex limits and tier allocations will shift.
New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.

CVE-2026-9277 (CVSS 9.2) lets attackers inject commands via the shell-quote npm package. Check your dependencies and upgrade now.
Explore the critical Kata Containers container escape vulnerability (CVE-2026-47243). Technical details and PoC exploit code are now fully public.
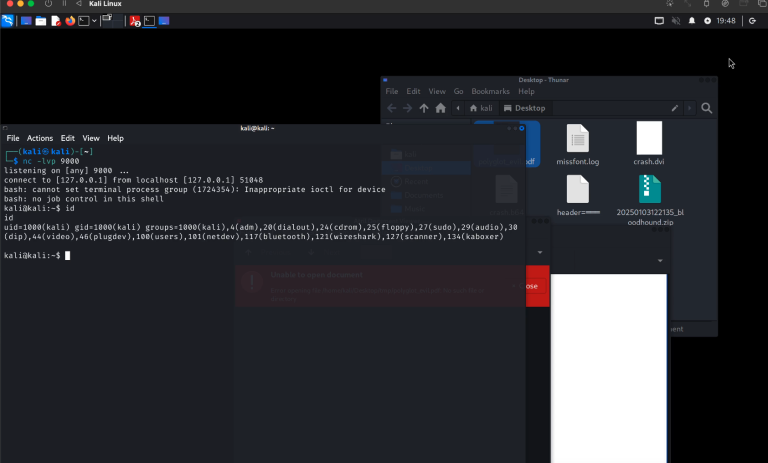
Learn about the critical Atril single-click RCE vulnerability (CVE-2026-46529). Public details and exploit code are now fully disclosed.

Learn about the latest Screening Serpens cyberattacks exposed by Unit 42. Discover their new RAT variants and advanced defensive evasion tactics.

 cybernewswire
Frankfurt am Main, Germany, 27th May 2026, CyberNewswire

The FBI issued an alert on the new Kali365 phishing platform. Learn how this PhaaS kit steals Microsoft 365 tokens and bypasses MFA.

Learn about the new Moxa Linux kernel vulnerabilities (CVE-2026-43284). Discover how to apply interim mitigations to prevent privilege escalation.
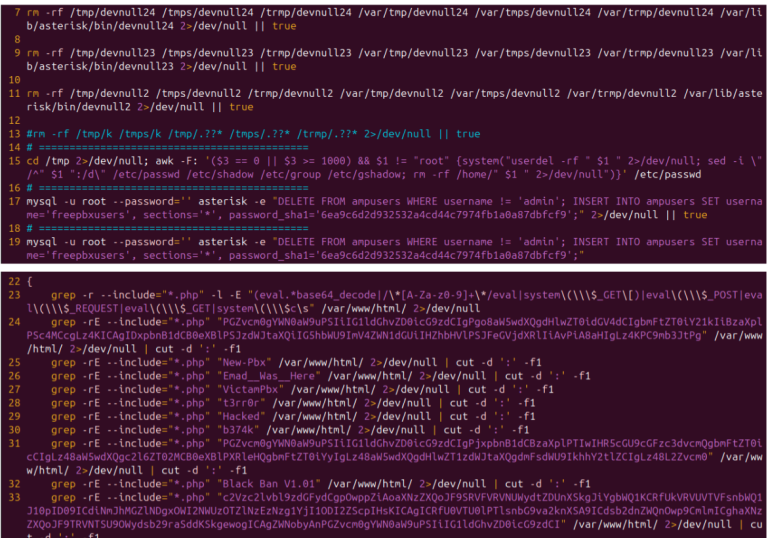
Cyble researchers uncover a widespread FreePBX exploitation campaign by INJ3CTOR3 deploying the novel JOMANGY webshell for toll fraud.

NVIDIA released updates fixing severe NVIDIA TensorRT-LLM vulnerabilities and Isaac Launchable flaws. Patch your active systems today.
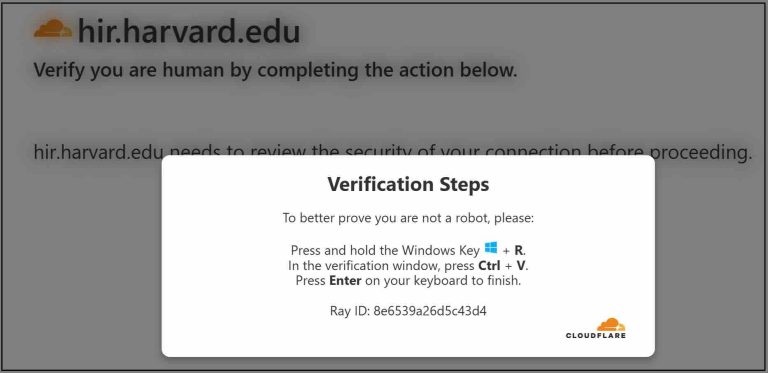
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.

EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.