
 Do Son
EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.

Google CEO Sundar Pichai reveals how Gemini-powered Agentic AI search will shift the web from traditional link clicks to autonomous background task execution.

A major Gemini resource quotas error is rapidly draining developers' weekly usage limits in minutes. Learn about the token tracking bug and Google's resets.
Discover how CVE-2026-48207, a critical PyFory deserialization policy bypass flaw, lets attackers execute remote code, and learn how to patch it now.

Concrete CMS dropped critical Concrete CMS security fixes in version 9.5.1 to eliminate remote code execution vulnerabilities. Update now.

A critical Fission router vulnerability (CVE-2026-46614) allows unauthenticated function invocation in Kubernetes. Learn how to patch it now.

GitHub patches critical GitHub Enterprise Server vulnerabilities (CVE-2026-9312). Learn about key rotation and critical SSRF fixes.
Twig project maintainers patched critical Twig RCE flaws allowing arbitrary code execution via sandbox bypasses. Update to 3.26.0.

A dangerous Windows Kernel EoP vulnerability allows browser sandbox escapes. Public PoC exploit code is available on GitHub.
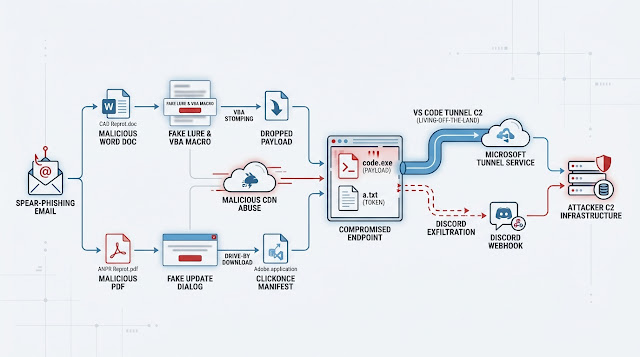
Learn how a sophisticated phishing campaign leverages VS Code Remote Tunnels abuse to bypass security and control enterprise networks.

Internet Systems Consortium released patches fixing six critical BIND 9 flaws that cause memory exhaustion and unexpected daemon crashes.

A sophisticated Android carrier billing fraud campaign hit users worldwide. Learn how fake apps trigger premium SMS abuse and how to stay safe.

Researchers uncover the Tampered Chef malware cluster disguised as PDF editors and tools. Learn how these stealthy threats bypass corporate defenses.
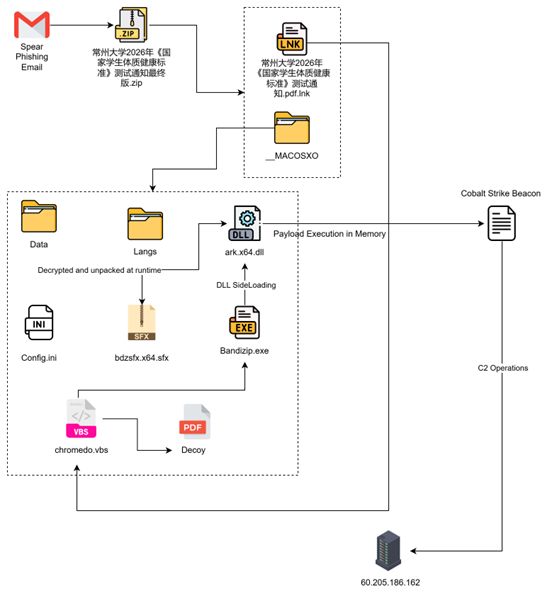
Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.

Fix the critical Dell Container Storage Modules vulnerability (CVE-2026-40710). Learn how hardcoded credentials expose systems and update now.

Discover the latest critical Apache CXF vulnerabilities, including RCE and XXE flaws, and learn how to secure your open source services framework.

Learn about the critical Memcached SASL vulnerability flaws fixed in version 1.6.42. Discover how timing side channels impacted authentication.
Learn about the Apache ECharts XSS vulnerability (CVE-2026-45249) in the Lines series tooltip rendering logic and find out how to secure your code.

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

Read our weekly threat intelligence briefing. Discover active exploits, critical CVEs, and the latest CISA KEV additions for May 18–24, 2026.

Learn how Mandiant uncovered the critical Knowledge Deliver RCE vulnerability (CVE-2026-5426) and how to protect your systems today.

Security researchers have exposed a malicious Go module backdoor hidden inside the shopsprint/decimal package that executes code using stealthy DNS TXT records.