
 Do Son
HUMAN's Satori team disrupted Trapdoor, an Android ad fraud ring using 455 apps and hidden WebViews to fake 659 million daily ad bids.
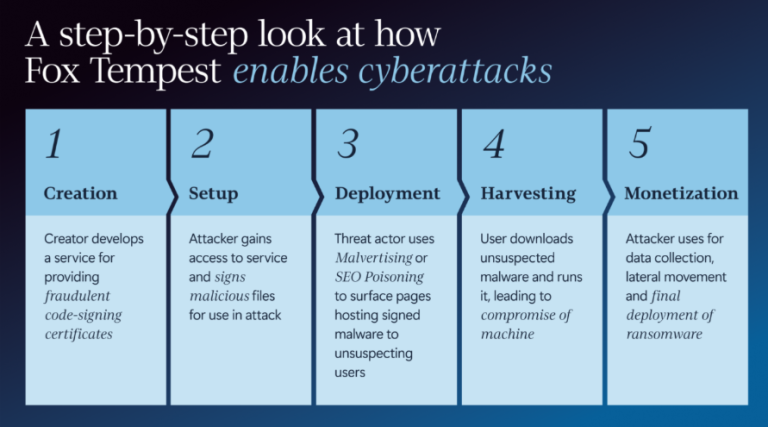
Microsoft's DCU and Resecurity have disrupted Fox Tempest, a major MSaaS ring that forged code-signing certificates for ransomware delivery.

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.

NLnet Labs patches a critical Unbound DNSSEC validation vulnerability allowing unauthenticated remote code execution. Update to 1.25.1.

A critical unauthenticated RCE flaw (CVE-2026-45695) impacts Kopia backup servers. Learn how the Kopia SSH ProxyCommand injection exploit operates and how to patch it.

Urgent: TYPO3 patches a critical 9.2 CVSS flaw (CVE-2026-46725) in Content Element Selector plugin. Unauthenticated attackers can achieve full server RCE.

The FreeBSD Project fixes seven vulnerabilities, including a zero-interaction Wi-Fi shell expansion RCE (CVE-2026-45255) and severe kernel leaks.

An NGINX heap buffer overflow vulnerability known as poolslip allows remote code execution. Learn how to secure your network servers now.
Code security is becoming one of the most difficult operational problems in modern software development, not because...

ConnectWise released a fix for a ConnectWise Automate vulnerability (CVE-2026-9089). Learn about the code download flaw and how to patch it now.

A recent report shows persistent P2Pinfect botnet activity inside Google Kubernetes Engine via exposed Redis instances. Learn how to secure your network.

A critical Angular hostname hijacking vulnerability allows SSRF attacks. Discover the impact on platform-server and how to patch your apps.
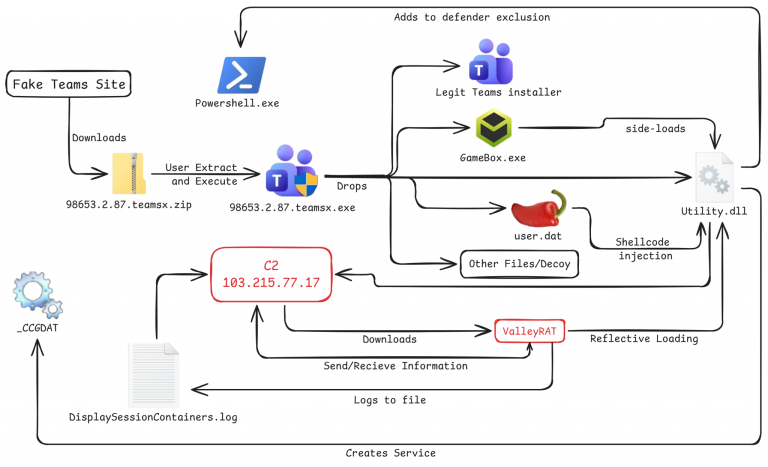
A sophisticated ValleyRAT malware campaign uses fake Microsoft Teams installers and DLL sideloading to evade Windows Defender detection.

Europol completely dismantles 'First VPN,' seizing 33 servers and uncovering an underground database used by thousands of global ransomware operators.

Anthropic’s secret "Mythos" model found 10,000+ bugs in one month for partners like Cloudflare and Mozilla. Discover why this tech remains top-secret.

Socket exposes a clever cross-ecosystem supply chain attack targeting PHP packages by hiding a malicious JS postinstall backdoor inside package.json.
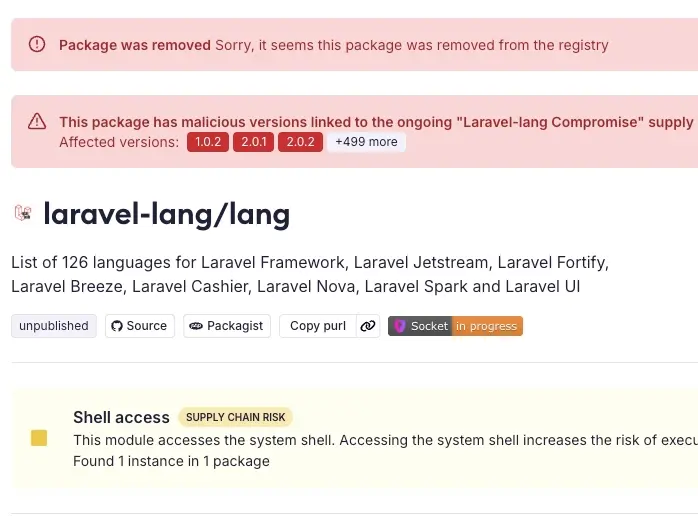
DevOps Alert: Over 700 laravel-lang localization package versions have been backdoored with a cross-platform 17-collector info-stealer. Audit your logs.
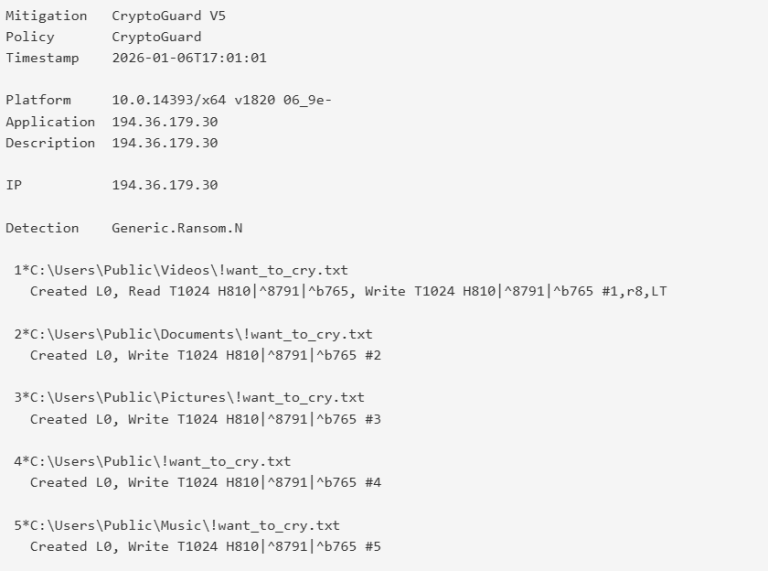
Sophos exposes WantToCry, a remote ransomware campaign that avoids EDR by using brute-forced SMB shares to read, encrypt, and rewrite files from afar.
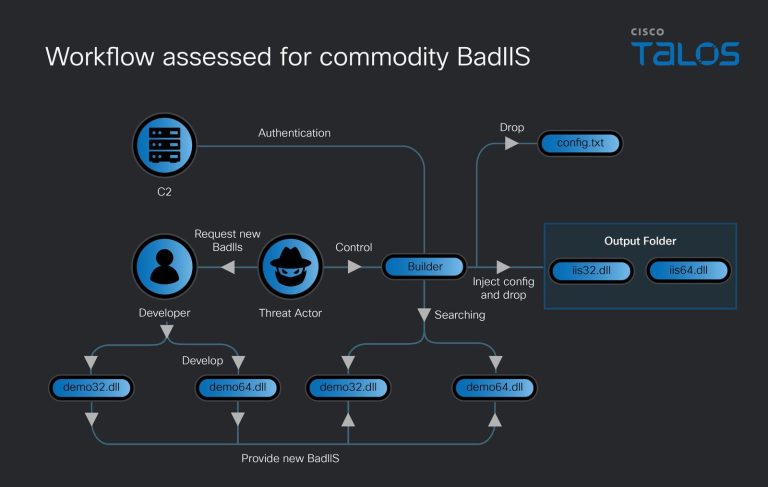
Cisco Talos exposes a commodity BadIIS variant sold as a service by dev "lwxat," featuring automated builders for traffic hijacking and reverse proxying.
Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints

Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints
SentinelOne exposes the SHub Stealer "Reaper" variant. It bypasses Apple's latest Terminal paste mitigations to hijack crypto wallets and corporate documents.

Microsoft exposes Storm-2949, a cloud-native threat group abusing Azure management features and SSPR to hijack Key Vaults, App Services, and SQL databases.

Urgent: Active attacks target the LiteSpeed User-End cPanel Plugin (CVE-2026-48172). Learn how to detect the exploit and secure your server root today.