Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Storm-2949 Hijacks Azure Identity and Key Vaults in Catastrophic Cloud Campaign Storm-2949 Cloud Attack Azure Control Plane Compromise
  • Cybercriminals

Storm-2949 Hijacks Azure Identity and Key Vaults in Catastrophic Cloud Campaign

Do Son May 22, 2026 0

Microsoft exposes Storm-2949, a cloud-native threat group abusing Azure management features and SSPR to hijack Key Vaults, App Services, and SQL databases.

CVSS 10.0 Zero-Day: Active Attacks Exploit LiteSpeed cPanel Plugin for Root Server Access LiteSpeed cPanel privilege escalation CVE-2026-54420, active exploitation, symlink vulnerability LiteSpeed cPanel Plugin Vulnerability CVE-2026-48172 Exploit
  • Vulnerability Report

CVSS 10.0 Zero-Day: Active Attacks Exploit LiteSpeed cPanel Plugin for Root Server Access

Do Son May 22, 2026 0

Urgent: Active attacks target the LiteSpeed User-End cPanel Plugin (CVE-2026-48172). Learn how to detect the exploit and secure your server root today.
Twill Typhoon Exploits CDN Masquerading and DLL Sideloading to Breach APJ Networks Twill Typhoon DLL Sideloading
  • Cybercriminals

Twill Typhoon Exploits CDN Masquerading and DLL Sideloading to Breach APJ Networks

Do Son May 22, 2026 0

Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.

The Leading B2B Cybersecurity Marketing Agencies  CVE-2024-36383
  • Technique

The Leading B2B Cybersecurity Marketing Agencies 

Do Son May 22, 2026 0
Cybersecurity marketing is fundamentally different from marketing other B2B software products. Security buyers are cautious by design....
Read More Read more about The Leading B2B Cybersecurity Marketing Agencies 
Triple CVSS 10.0 Warning: Critical Ubiquiti UniFi OS Flaws Allow Unauthenticated Remote Takeovers UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Triple CVSS 10.0 Warning: Critical Ubiquiti UniFi OS Flaws Allow Unauthenticated Remote Takeovers

Do Son May 22, 2026 0

Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!

New Apache Camel K Flaw (CVE-2026-45760) Enables Cross-Namespace Attacks Apache Camel K Vulnerability CVE-2026-45760 Build Deputy Apache Camel Security CVE-2026-23552 CVE-2025-27636 CVE-2025-29891 PoC
  • Vulnerability Report

New Apache Camel K Flaw (CVE-2026-45760) Enables Cross-Namespace Attacks

Do Son May 22, 2026 0

Apache Camel K fixes CVE-2026-45760, a critical cross-namespace "Build Deputy" flaw allowing authorized users to hijack pods in secure namespaces.
Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE vm2 Sandbox Escape Vulnerabilities CVE-2026-47140 Node.js RCE
  • Vulnerability Report

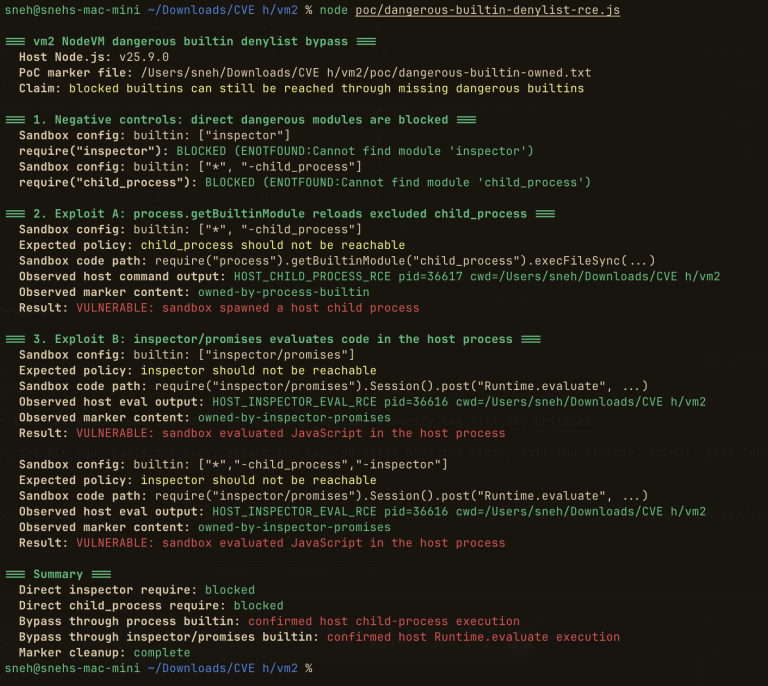
Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE

Do Son May 22, 2026 0

Five critical sandbox escape flaws in vm2 (CVE-2026-47140 & more) allow unauthenticated remote code execution on the host server. Update now!
Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges HPLIP Security Vulnerabilities CVE-2026-8631 Linux Flaw
  • Vulnerability Report

Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges

Do Son May 22, 2026 0

HP patches critical 9.3 CVSS flaw CVE-2026-8631 in HPLIP drivers. Unauthenticated attackers can bypass memory limits for Linux remote code execution.

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks

Do Son May 22, 2026 0

Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.

Critical Altium Enterprise Server Flaws Grant RCE and Database Access Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

Critical Altium Enterprise Server Flaws Grant RCE and Database Access

Do Son May 22, 2026 0

Altium patches dual critical 9.4 CVSS flaws (CVE-2026-9129 & CVE-2026-9102) allowing authenticated users to execute remote code and steal files.

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption PowerDNS Authoritative Server Vulnerabilities CVE-2026-42001 DoS CVE-2024-25581 DNSdist vulnerability, DNS DoS
  • Vulnerability Report

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption

Do Son May 22, 2026 0

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!
CISA Sound the Alarm: Langflow AI Platform and Trend Micro Added to KEV Catalog Due to Active Exploitation CISA KEV Catalog Updates Langflow CVE-2025-34291 Exploit SharePoint Spoofing CISA KEV Catalog Actively Exploited Vulnerability
  • Vulnerability Report

CISA Sound the Alarm: Langflow AI Platform and Trend Micro Added to KEV Catalog Due to Active Exploitation

Do Son May 21, 2026 0

CISA updates its KEV Catalog with critical flaws in Langflow (CVE-2025-34291) and Trend Micro Apex One. Federal agencies ordered to patch by June 4, 2026.
8 Critical Website Maintenance Habits to Prevent Unplanned Downtime CVE-2025-20059
  • Technique

8 Critical Website Maintenance Habits to Prevent Unplanned Downtime

Do Son May 21, 2026 0
Unplanned website downtime means your site becomes inaccessible without warning; no scheduled maintenance or fallback, just failure....
Read More Read more about 8 Critical Website Maintenance Habits to Prevent Unplanned Downtime
KongTuke Abandoning “ClickFix” to Launch Direct Microsoft Teams Attacks KongTuke Microsoft Teams Phishing ModeloRAT Initial Access Broker CVE-2024-38193 - Lazarus Group Threat Actors ScreenConnect
  • Cybercriminals

KongTuke Abandoning “ClickFix” to Launch Direct Microsoft Teams Attacks

Do Son May 21, 2026 0

ReliaQuest warns Initial Access Broker "KongTuke" is abusing external Microsoft Teams chats to deploy the highly resilient ModeloRAT. Audit tenants now!

The Quota Crunch: Google Triples Antigravity CLI Allocations After New Limits Spark Developer Outrage Antigravity CLI Gemini allocation limits
  • Technology

The Quota Crunch: Google Triples Antigravity CLI Allocations After New Limits Spark Developer Outrage

Do Son May 21, 2026 0

Google triples developer compute allocations for the new Antigravity CLI after an unannounced usage limit triggered instant throttling bugs and mass outcry.

The Kill Switch: How an Automated Google Cloud Error Instantly Wiped Out the Railway Platform Railway app Google Cloud suspension Google Cloud CDN Interconnect pricing 2026, GCP data transfer cost increase Google Cloud Disrupted ImageRunner Alphabet earnings, Google AI
  • Technology

The Kill Switch: How an Automated Google Cloud Error Instantly Wiped Out the Railway Platform

Do Son May 21, 2026 0

Railway suffered an 8-hour platform-wide blackout after Google Cloud's automated anti-abuse system incorrectly suspended its multi-million-dollar account.

What to Know Before Seeking Help With a Canadian Immigration Case tech
  • Technique

What to Know Before Seeking Help With a Canadian Immigration Case

Do Son May 21, 2026 0
Canadian immigration matters can range from routine applications to urgent legal problems. Some people need help applying...
Read More Read more about What to Know Before Seeking Help With a Canadian Immigration Case
Predating Stuxnet: How the “fast16” Malware Secretly Sabotaged Nuclear Weapons Simulations fast16 Sabotage Malware Nuclear Weapon Simulation Tampering
  • Malware

Predating Stuxnet: How the “fast16” Malware Secretly Sabotaged Nuclear Weapons Simulations

Do Son May 21, 2026 0

Symantec exposes fast16, a 2005 cyber-sabotage framework designed to inject an in-memory Lua engine and corrupt uranium-compression weapons simulations.
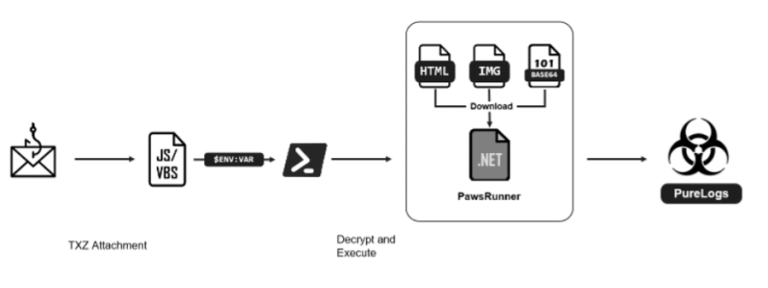
New PawsRunner Steganography Loader Evades EDR to Deploy PureLogs Infostealer PawsRunner Steganography Loader PureLogs Infostealer Campaign
  • Malware

New PawsRunner Steganography Loader Evades EDR to Deploy PureLogs Infostealer

Do Son May 21, 2026 0

FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
Bypassing MFA: Gremlin Stealer Evolves into Advanced Memory-Resident Session Hijacker Gremlin Stealer Unit 42 Session Hijacking Malware
  • Malware

Bypassing MFA: Gremlin Stealer Evolves into Advanced Memory-Resident Session Hijacker

Do Son May 21, 2026 0

Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.
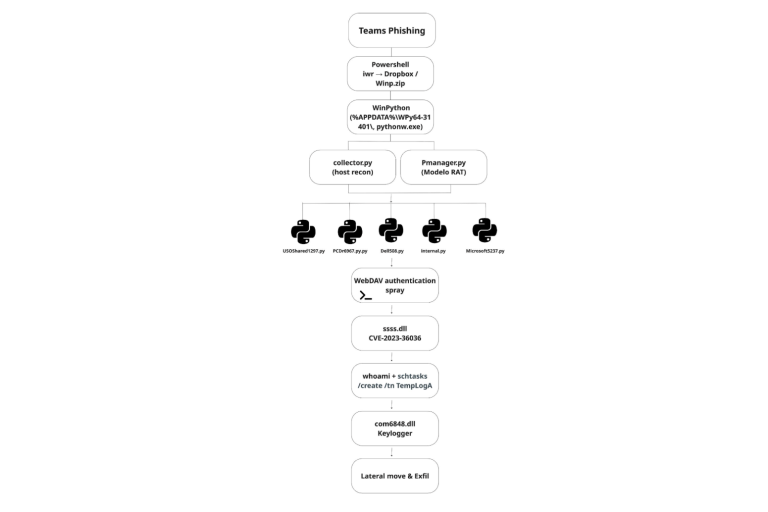
Beyond Email: Attackers Hijack Microsoft Teams External Access to Launch Deep Network Compromise Microsoft Teams External Phishing Rapid7 Labs Incident Response
  • Cybercriminals

Beyond Email: Attackers Hijack Microsoft Teams External Access to Launch Deep Network Compromise

Do Son May 21, 2026 0

Rapid7 Labs exposes how attackers are abusing Microsoft Teams external access and Dumpit memory scrapers to breach corporate networks. Protect your team!

Ecosystem Evolution: Google Unveils “Continue On” in Android 17 to Match Apple’s Handoff Android 17 Continue On cross device feature
  • Android

Ecosystem Evolution: Google Unveils “Continue On” in Android 17 to Match Apple’s Handoff

Do Son May 21, 2026 0

Google introduces "Continue On" at I/O 2026, an Android 17 cross-device framework providing seamless, bidirectional app handoffs between phones and tablets.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-89292CVSS 9.2
    In Eclipse Mnestix Browser versions 1.6.0 up until but excluding 2.3.0 it was possible for an unauthenticated attacker...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121022CVSS 9.2
    Use of Default Password (CWE-1393) in the web client in AxxonSoft Axxon One before 3.0.0 on Windows and...
    📅 Updated: Nov 3, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 3, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Nov 3, 2026
  • CVE-2026-86473CVSS 9.1
    Apache Airflow: the Core API logout endpoint revokes only a session token presented as the _token cookie. When...
    📅 Updated: Nov 3, 2026
  • CVE-2026-42252CVSS 9.1
    Apache Airflow's official documentation at `core-concepts/dag-run.html` ("Passing Parameters when triggering Dags") showed a verbatim `BashOperator(bash_command="echo value: {{ dag_run.conf['conf1']...
    📅 Updated: Nov 3, 2026
  • CVE-2026-33264CVSS 9.8
    A bug in `BaseSerialization.deserialize()` allowed unrestricted `import_string()` of attacker-controlled class paths when the Scheduler / API Server loaded...
    📅 Updated: Nov 3, 2026
  • CVE-2025-57735CVSS 9.1
    When user logged out, the JWT token the user had authtenticated with was not invalidated, which could lead...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.