Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
APT37’s New “Python-in-a-Cat” Malware Uses Environment Variable Obfuscation APT37 Phishing Campaign Python Malware Obfuscation
  • Malware

APT37’s New “Python-in-a-Cat” Malware Uses Environment Variable Obfuscation

Do Son May 12, 2026 0

Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.

Critical 9.6 Severity: SAP May 2026 Patch Day Fixes Dangerous S/4HANA and Commerce Cloud Flaws SAP Security Patch May 2026 CVE-2026-34260 S/4HANA CVE-2024-22127 - CVE-2025-27434 SAP Solution Manager Code Injection, Critical SAP Patch
  • Vulnerability Report

Critical 9.6 Severity: SAP May 2026 Patch Day Fixes Dangerous S/4HANA and Commerce Cloud Flaws

Do Son May 12, 2026 0

SAP’s May 2026 Patch Day fixes two 9.6 severity flaws in S/4HANA and Commerce Cloud. Prevent SQL injection and RCE by updating your SAP landscape today.
DRM Disaster: How a Massive Forza Horizon 6 Leak Led to Permanent “9999” Hardware Bans Forza Horizon 6 DRM leak
  • Data Leak

DRM Disaster: How a Massive Forza Horizon 6 Leak Led to Permanent “9999” Hardware Bans

Do Son May 12, 2026 0

Playground Games accidentally leaked Forza Horizon 6 without DRM. Now, Microsoft is issuing "permanent" hardware bans for early access. Is your PC blacklisted?
“Lorem Ipsum” Loader Weaponizing Microsoft Teams via SEO Poisoning Lorem Ipsum Malware Microsoft Teams SEO Poisoning
  • Malware

“Lorem Ipsum” Loader Weaponizing Microsoft Teams via SEO Poisoning

Do Son May 12, 2026 0

BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.

The 2029 Lifeline: Why the FCC Just Postponed the “Death Sentence” for Millions of Drones and Routers FCC drone router firmware extension 2029 CVE-2024-21833 FCC foreign router ban 2026
  • Technology

The 2029 Lifeline: Why the FCC Just Postponed the “Death Sentence” for Millions of Drones and Routers

Do Son May 12, 2026 0

The FCC extends firmware update deadlines to Jan 1, 2029, for foreign drones and routers. Discover how this shift impacts DJI, TP-Link, and US cyber defense.

The $97 Billion Moat: Microsoft’s Historic Discount to OpenAI Redefines the Race for AGI Microsoft OpenAI $97 billion savings Microsoft Developer Account Suspension Microsoft Managed Desktop
  • Technology

The $97 Billion Moat: Microsoft’s Historic Discount to OpenAI Redefines the Race for AGI

Do Son May 12, 2026 0

Microsoft grants OpenAI a staggering $97B discount on Azure costs through 2030. Discover how this massive capital move secures the lead in the AGI race.
OpenAI Launches Project Daybreak and GPT-5.5-Cyber to Counter Anthropic’s Glasswing OpenAI Project Daybreak GPT-5.5
  • Technology

OpenAI Launches Project Daybreak and GPT-5.5-Cyber to Counter Anthropic’s Glasswing

Do Son May 12, 2026 0

OpenAI unveils Project Daybreak, utilizing the GPT-5.5 lineage and Codex to automate vulnerability patching and Red Teaming in a direct challenge to Anthropic.

OpenAI’s $10B Power Play: Inside “DeployCo” and the Acquisition of Tomoro to Conquer Enterprise IT OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

OpenAI’s $10B Power Play: Inside “DeployCo” and the Acquisition of Tomoro to Conquer Enterprise IT

Do Son May 12, 2026 0

OpenAI launches DeployCo, a $10B subsidiary to embed "AI Special Forces" into legacy corporate systems. Discover how the Palantir model is changing AI.
Vidar Stealer Weaponizes AutoIt and Masqueraded Scripts Vidar Stealer AutoIt File Extension Masquerading
  • Malware

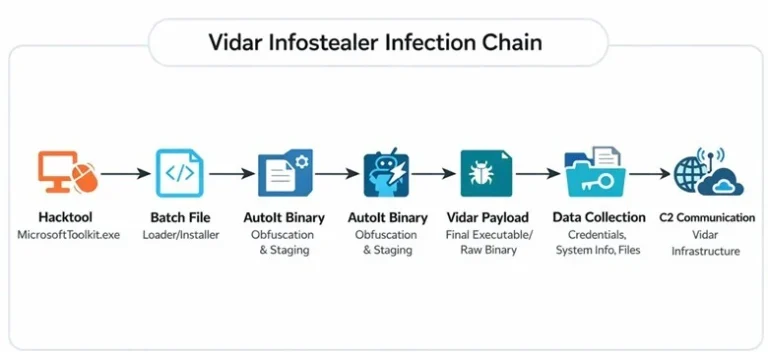
Vidar Stealer Weaponizes AutoIt and Masqueraded Scripts

Do Son May 12, 2026 0

LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?

Apache Tomcat RCE Details and Exploit Code Now Public Apache Tomcat RCE CVE-2026-34486
  • Vulnerability

Apache Tomcat RCE Details and Exploit Code Now Public

Do Son May 12, 2026 0

Apache Tomcat RCE alert: CVE-2026-34486 exploit code and details are now public. A "fail-open" flaw enables RCE via Tribes clustering. Update immediately.
Critical PrestaShop Flaw Allows Hijacking via “Contact Us” Form PrestaShop XSS Vulnerability CVE-2026-44212
  • Vulnerability Report

Critical PrestaShop Flaw Allows Hijacking via “Contact Us” Form

Do Son May 12, 2026 0

Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!

Supply Chain Siege: 84 TanStack Packages Compromised to Steal GitHub Secrets GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Malware

Supply Chain Siege: 84 TanStack Packages Compromised to Steal GitHub Secrets

Do Son May 12, 2026 0

Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.
9.6 Severity: Critical “Cline” AI Agent Flaw Allows Stealthy RCE via Your Browser Cline AI Vulnerability Cross-Origin WebSocket Hijacking
  • Vulnerability Report

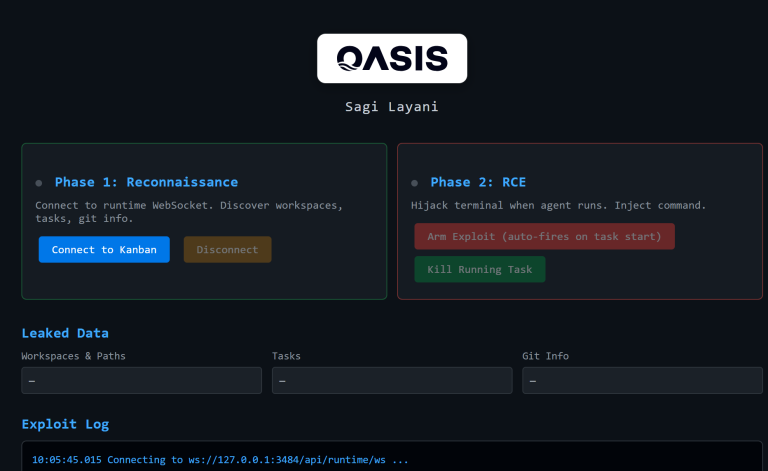
9.6 Severity: Critical “Cline” AI Agent Flaw Allows Stealthy RCE via Your Browser

Do Son May 12, 2026 0

Critical Alert: CVE-2026-44211 (CVSS 9.6) in Cline AI allows malicious sites to hijack your terminal and steal data via WebSockets. Update your CLI tools now.
Proof-of-Concept Disclosed: New “BitUnlocker” Attack Bypasses Patched Windows 11 BitLocker via Certificate Downgrade BitUnlocker PoC BitLocker Downgrade Attack
  • Vulnerability Report

Proof-of-Concept Disclosed: New “BitUnlocker” Attack Bypasses Patched Windows 11 BitLocker via Certificate Downgrade

Do Son May 12, 2026 0

Public PoC Alert: The BitUnlocker Downgrade Attack bypasses BitLocker on patched Windows 11 machines in under 5 minutes. Learn how to secure your TPM with a PIN.
Tactical Misdirection: The “Hologram” Malware Framework Hijacking AI Enthusiasts Hologram Malware Framework OpenClaw Malvertising
  • Malware

Tactical Misdirection: The “Hologram” Malware Framework Hijacking AI Enthusiasts

Do Son May 11, 2026 0

Netskope exposes Hologram: a red-team-grade malware framework targeting OpenClaw AI users with CLR injection and WinLogon hijacking to steal crypto wallets.
Lyrie.ai Joins First Batch of Anthropic’s Cyber Verification Program Lyrie_and_Anthropic_1778138816A1kmRs3pAH
  • Press Release

Lyrie.ai Joins First Batch of Anthropic’s Cyber Verification Program

cybernewswire May 11, 2026 0
Dubai, UAE, 11th May 2026, CyberNewswire
Read More Read more about Lyrie.ai Joins First Batch of Anthropic’s Cyber Verification Program
AI Hijacked: Critical Claude Chrome Extension Flaw Allows Malicious Scripts to Control Your AI Claude Extension Vulnerability AI Agent Hijacking
  • Vulnerability Report

AI Hijacked: Critical Claude Chrome Extension Flaw Allows Malicious Scripts to Control Your AI

Do Son May 11, 2026 0

LayerX uncovers a critical flaw in Anthropic’s Claude extension. Learn how attackers can hijack AI agents to steal data and bypass security policies.
The “JobStealer” Trojan Hijacking Crypto Wallets via Fake Meetings JobStealer Trojan Crypto Wallet Theft
  • Malware

The “JobStealer” Trojan Hijacking Crypto Wallets via Fake Meetings

Do Son May 11, 2026 0

Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.
Critical 9.5 Severity: PHP SOAP Extension Flaw Enables Remote Code Execution CVE-2023-0662 PHP RCE Vulnerability CVE-2026-6722
  • Vulnerability Report

Critical 9.5 Severity: PHP SOAP Extension Flaw Enables Remote Code Execution

Do Son May 11, 2026 0

PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!
The Claude AI Trap: Sophos Uncovers Undocumented Backdoor Hiding in Fake “Pro” Lure Claude AI Malware DonutLoader Backdoor
  • Malware

The Claude AI Trap: Sophos Uncovers Undocumented Backdoor Hiding in Fake “Pro” Lure

Do Son May 11, 2026 0

Sophos X-Ops uncovers a fake Claude AI site (claude-pro.com) distributing an undocumented backdoor via DonutLoader. Protect your team from AI-themed lures.

No More KB Math: Windows 11 Finally Adds Adaptive File Sizes to File Explorer Windows 11 File Explorer adaptive size
  • Windows

No More KB Math: Windows 11 Finally Adds Adaptive File Sizes to File Explorer

Do Son May 11, 2026 0

Microsoft updates Windows 11 File Explorer to dynamically show file sizes in MB, GB, and TB. Say goodbye to long KB strings in the latest Insider builds!

The AnimeKai Blackout: Inside the Mysterious Closure of the Web’s Most Visited Anime Portal AnimeKai shutdown
  • Technology

The AnimeKai Blackout: Inside the Mysterious Closure of the Web’s Most Visited Anime Portal

Do Son May 11, 2026 0

AnimeKai is shutting down following a Dutch data center fire. Learn how to export your bookmarks and where the 43 million monthly users are heading next.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124560CVSS 9.3
    A vulnerability was found in D-Link DIR-878 1.20B05. This affects the function GetCAPTCHAsetting of the file bin/prog.cgi of...
    📅 Updated: Nov 9, 2026
  • CVE-2026-82418CVSS 9.8
    IBM Watson Speech Services Cartridge 4.0.0 through 5.4.0 could allow a remote attacker to execute arbitrary code due...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119506CVSS 9.1
    Incorrect Privilege Assignment vulnerability in DynamiApps Frontend Admin by DynamiApps acf-frontend-form-element allows Privilege Escalation.This issue affects Frontend Admin...
    📅 Updated: Nov 9, 2026
  • CVE-2024-47856CVSS 9.8
    In RSA Authentication Agent before 7.4.7, service paths and shortcut paths may be vulnerable to path interception if...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36057CVSS 9.8
    Koha Library before 23.05.10 fails to sanitize user-controllable filenames prior to unzipping, leading to remote code execution. The...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36058CVSS 9.8
    The Send Basket functionality in Koha Library before 23.05.10 is susceptible to Time-Based SQL Injection because it fails...
    📅 Updated: Nov 8, 2026
  • CVE-2024-46636CVSS 9.4
    NASA Earth Observing System Data and Information System (EOSDIS) MODAPS v8.1 was discovered to contain a SQL injection...
    📅 Updated: Nov 8, 2026
  • CVE-2026-64232CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: block: recompute nr_integrity_segments in blk_insert_cloned_request blk_insert_cloned_request() already recomputes...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.