Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
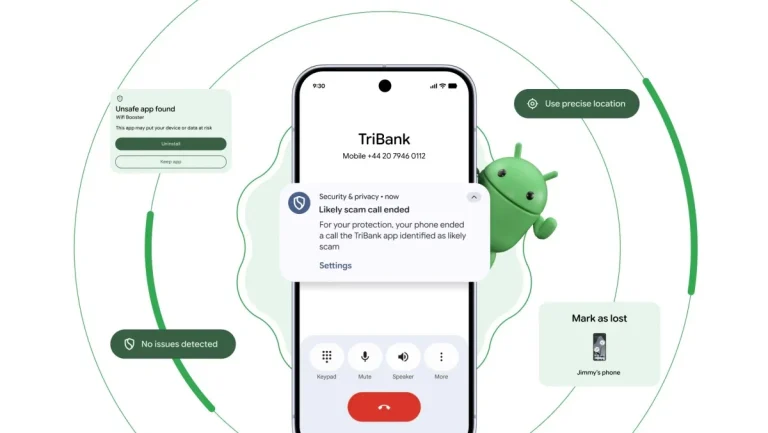
The “Unbreakable” OS: Android 17 Unveils AI-Powered Fraud Defense and Thief-Proof Biometrics Android 17 security features
  • Android

The “Unbreakable” OS: Android 17 Unveils AI-Powered Fraud Defense and Thief-Proof Biometrics

Do Son May 13, 2026 0

Google’s 2026 Android roadmap turns AI into a "Live Threat Detection" sentinel. Explore Android 17’s new anti-theft biometrics and banking fraud intercepts.

Security Alert: Cemu Emulator Linux Releases Compromised via GitHub Backdoor (May 2026) Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

Security Alert: Cemu Emulator Linux Releases Compromised via GitHub Backdoor (May 2026)

Do Son May 13, 2026 0

Critical: Cemu 2.6 Linux binaries were backdoored via a developer's stolen GitHub token. If you downloaded Cemu for Linux between May 6–12, audit your system now.
Agentic AI is Automating Live Intrusions in Latin America Agentic AI Cyber Attacks SHADOW-AETHER Threat Groups
  • Cybercriminals

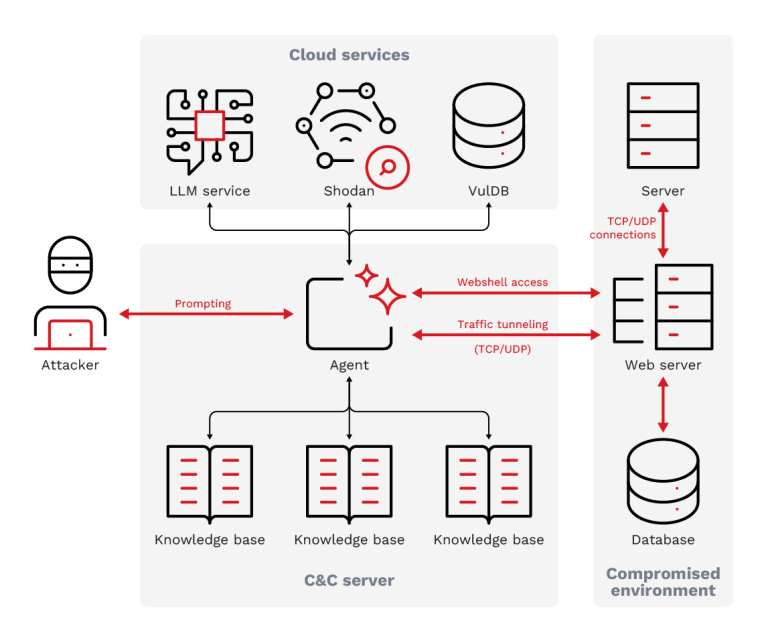
Agentic AI is Automating Live Intrusions in Latin America

Do Son May 13, 2026 0

TrendAI exposes SHADOW-AETHER: threat groups using agentic AI to "vibe code" custom backdoors and automate intrusions across government and financial sectors.

JDownloader Site Breach Installs Rootkits that Kill Your Antivirus Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Malware

JDownloader Site Breach Installs Rootkits that Kill Your Antivirus

Do Son May 13, 2026 0

Gen Digital exposes a JDownloader site breach (May 6-7, 2026). Attackers used WDAC policies to kill antivirus and r77 rootkits for total system invisibility.

GemStuffer: Attackers Weaponize RubyGems as a Covert Data Drop for UK Gov Scraping GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Malware

GemStuffer: Attackers Weaponize RubyGems as a Covert Data Drop for UK Gov Scraping

Do Son May 13, 2026 0

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.

Pre-Auth RCE Exposed: Apache HTTP Server Vulnerability and Exploit Code Hit the Public Apache HTTP Server RCE CVE-2026-23918 PoC
  • Vulnerability

Pre-Auth RCE Exposed: Apache HTTP Server Vulnerability and Exploit Code Hit the Public

Do Son May 13, 2026 0

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.
Exploit Code Released: Public PoC Dumps for Windows BitLocker Bypass and SYSTEM Elevation Zero-Days BitLocker Bypass PoC Windows Zero-Day Exploit 2026
  • Vulnerability Report

Exploit Code Released: Public PoC Dumps for Windows BitLocker Bypass and SYSTEM Elevation Zero-Days

Do Son May 13, 2026 0

Urgent: Public PoC exploit code released for YellowKey (BitLocker bypass) and GreenPlasma (SYSTEM elevation). Windows 11 and Server 2025 are at high risk.

Critical-Severity XSS Flaws Uncovered in Siemens SIMATIC S7 Web Servers Siemens SIMATIC S7 Vulnerability Industrial PLC XSS CVE-2024-44102 - Siemens TeleControl Server Basic
  • Vulnerability Report

Critical-Severity XSS Flaws Uncovered in Siemens SIMATIC S7 Web Servers

Do Son May 13, 2026 0

Critical Siemens Alert: 9.3 severity XSS flaws hit SIMATIC S7 PLCs. Attackers can hijack sessions via web interfaces. Update to V3.1.6 or follow mitigations.
9.8 Severity Alert: Malicious Git Branches Can Hijack Your WebdriverIO Build Servers WebdriverIO Command Injection CVE-2026-25244
  • Vulnerability Report

9.8 Severity Alert: Malicious Git Branches Can Hijack Your WebdriverIO Build Servers

Do Son May 13, 2026 0

Critical Alert: CVE-2026-25244 (CVSS 9.8) in WebdriverIO allows RCE via unsanitized git branch names. Secure your CI/CD pipeline and update to 9.24.0 now.

Microsoft Patch Tuesday May 2026 Fixes 137 Flaws, Including Netlogon RCE and Critical SSO Bypass Microsoft Patch Tuesday May 2026 Netlogon RCE CVE-2026-41089 SharePoint Exploit Patch Tuesday Windows DWM Zero-Day CVE-2026-21519 CVE-2024-49039 Microsoft Patch Tuesday March 2025
  • Vulnerability Report

Microsoft Patch Tuesday May 2026 Fixes 137 Flaws, Including Netlogon RCE and Critical SSO Bypass

Do Son May 13, 2026 0

Microsoft’s May 2026 update fixes 137 vulnerabilities, including 30 Critical RCE and EoP flaws. Prioritize patches for Netlogon, Office, and M365 Copilot now.
CVSS 10 Alert: SandboxJS Critical Escape Vulnerability Enables Host Takeover SandboxJS Sandbox Escape CVE-2026-43898 RCE
  • Vulnerability Report

CVSS 10 Alert: SandboxJS Critical Escape Vulnerability Enables Host Takeover

Do Son May 13, 2026 0

Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.
PraisonAI CVE-2026-44338 Exploited in the Wild Hours After Patch Disclosure PraisonAI Authentication Bypass Exploited in the Wild CVE-2026-44338
  • Vulnerability Report

PraisonAI CVE-2026-44338 Exploited in the Wild Hours After Patch Disclosure

Do Son May 13, 2026 0

Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!
9.8 Critical Alert: One-Byte Heap Corruption in Exim Exposes Global Mail Servers to Takeover Exim RCE Vulnerability CVE-2026-45185 GnuTLS
  • Vulnerability Report

9.8 Critical Alert: One-Byte Heap Corruption in Exim Exposes Global Mail Servers to Takeover

Do Son May 13, 2026 0

Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!

Fortinet Critical Alert: 9.1 Severity Flaws in FortiSandbox and FortiAuthenticator Risk Remote Takeover CVE-2023-36553 Fortinet Critical Vulnerabilities FortiSandbox CVE-2026-26083
  • Vulnerability Report

Fortinet Critical Alert: 9.1 Severity Flaws in FortiSandbox and FortiAuthenticator Risk Remote Takeover

Do Son May 13, 2026 0

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.

Multiple Memory Flaws in Dnsmasq Threaten Millions of Connected Devices dnsmasq Vulnerabilities DNS Cache Poisoning
  • Vulnerability Report

Multiple Memory Flaws in Dnsmasq Threaten Millions of Connected Devices

Do Son May 13, 2026 0

Urgent: dnsmasq patches 6 critical flaws (CVE-2026-2291+) enabling DNS poisoning and root access. Update your router firmware to version 2.92rel2 now!
Critical Casdoor Vulnerability CVE-2026-44213 Allows Arbitrary File Overwrites Casdoor Arbitrary File Write CVE-2026-44213 Path Traversal
  • Vulnerability Report

Critical Casdoor Vulnerability CVE-2026-44213 Allows Arbitrary File Overwrites

Do Son May 13, 2026 0

Urgent: Casdoor IAM platform hit by critical file write flaw (CVE-2026-44213). Attackers can bypass sandboxes to overwrite databases and gain host access.

Critical Siemens ROS# Flaw Enables Arbitrary File Access and Host Takeover ROS# Path Traversal CVE-2026-41551 Siemens SIMATIC Auth Bypass, CVE-2025-40771 CVE-2024-22039 & CVE-2024-49775 CVE-2024-56336
  • Vulnerability Report

Critical Siemens ROS# Flaw Enables Arbitrary File Access and Host Takeover

Do Son May 12, 2026 0

Urgent: Siemens patches a 9.3 severity Path Traversal (CVE-2026-41551) in ROS#. Attackers can read/write arbitrary files on robotics systems. Update to V2.2.2!
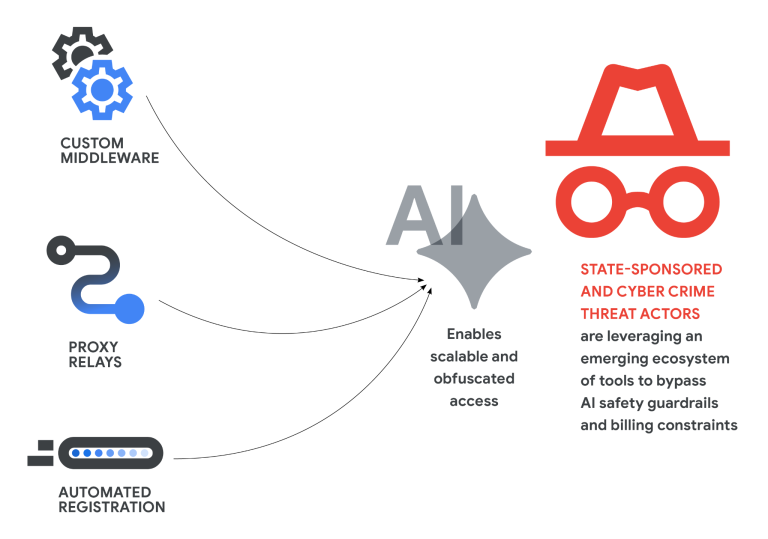
Google Confirms First AI-Generated Zero-Day Exploit Found in the Wild AI-Built Zero-Day Exploit Google Threat Intelligence Report 2026
  • Cybercriminals

Google Confirms First AI-Generated Zero-Day Exploit Found in the Wild

Do Son May 12, 2026 0

Google GTIG confirms the first AI-built zero-day exploit used in the wild. Discover how AI is industrializing cyber warfare and how Big Sleep is fighting back.
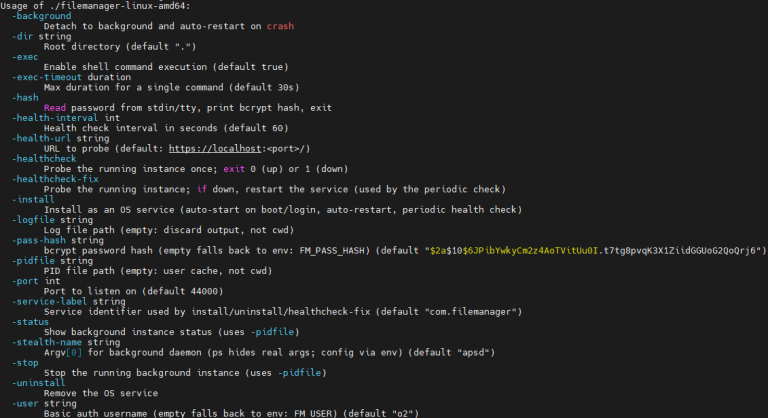
Critical cPanel Auth Bypass CVE-2026-41940 Exploited by Thousands cPanel Authentication Bypass CVE-2026-41940 Exploitation
  • Vulnerability Report

Critical cPanel Auth Bypass CVE-2026-41940 Exploited by Thousands

Do Son May 12, 2026 0

Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!
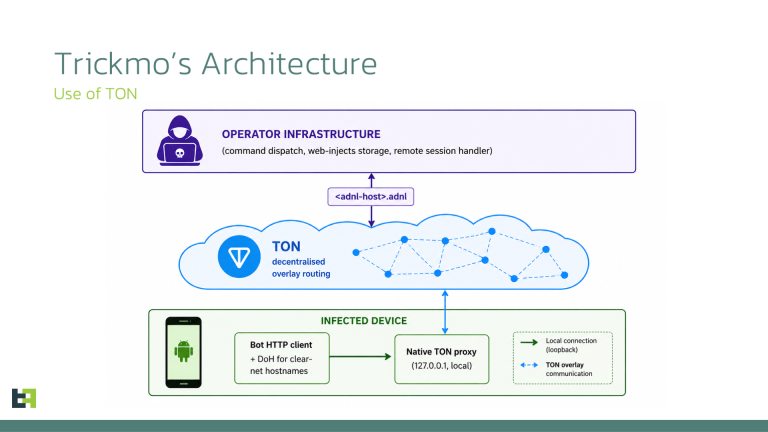
TrickMo’s Stealthy Upgrade: Android Banking Malware is Pivoting to The Open Network TrickMo banking trojan TON network malware
  • Malware

TrickMo’s Stealthy Upgrade: Android Banking Malware is Pivoting to The Open Network

Do Son May 12, 2026 0

ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
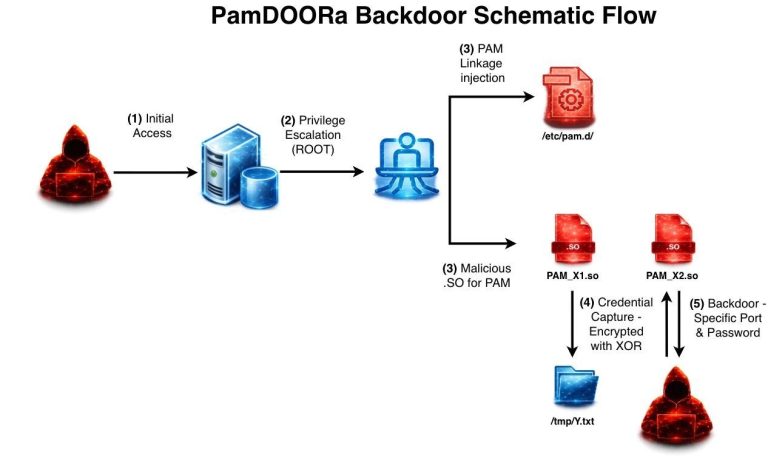
PamDOORa Backdoor Targets Linux PAM Stack to Steal Passwords and Wipe Logs PamDOORa Linux Backdoor PAM Stack Credential Harvesting
  • Malware

PamDOORa Backdoor Targets Linux PAM Stack to Steal Passwords and Wipe Logs

Do Son May 12, 2026 0

Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.

Critical 9.8 Alert: Hard-Coded Credentials in Dell ECS and ObjectScale Leave Filesystems Exposed Dell ECS Security Update CVE-2026-40636 Hard-coded Credentials Dell Business Price Increase, RAM and SSD Shortage 2025 Dell Data Lakehouse, Critical Privilege Escalation Authentication Bypass Vulnerability CVE-2025-22398
  • Vulnerability Report

Critical 9.8 Alert: Hard-Coded Credentials in Dell ECS and ObjectScale Leave Filesystems Exposed

Do Son May 12, 2026 0

Urgent: Dell patches a 9.8 severity credential flaw (CVE-2026-40636) in ECS and ObjectScale. Secure your enterprise storage by upgrading to version 4.3.0.0.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124560CVSS 9.3
    A vulnerability was found in D-Link DIR-878 1.20B05. This affects the function GetCAPTCHAsetting of the file bin/prog.cgi of...
    📅 Updated: Nov 9, 2026
  • CVE-2026-82418CVSS 9.8
    IBM Watson Speech Services Cartridge 4.0.0 through 5.4.0 could allow a remote attacker to execute arbitrary code due...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119506CVSS 9.1
    Incorrect Privilege Assignment vulnerability in DynamiApps Frontend Admin by DynamiApps acf-frontend-form-element allows Privilege Escalation.This issue affects Frontend Admin...
    📅 Updated: Nov 9, 2026
  • CVE-2024-47856CVSS 9.8
    In RSA Authentication Agent before 7.4.7, service paths and shortcut paths may be vulnerable to path interception if...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36057CVSS 9.8
    Koha Library before 23.05.10 fails to sanitize user-controllable filenames prior to unzipping, leading to remote code execution. The...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36058CVSS 9.8
    The Send Basket functionality in Koha Library before 23.05.10 is susceptible to Time-Based SQL Injection because it fails...
    📅 Updated: Nov 8, 2026
  • CVE-2024-46636CVSS 9.4
    NASA Earth Observing System Data and Information System (EOSDIS) MODAPS v8.1 was discovered to contain a SQL injection...
    📅 Updated: Nov 8, 2026
  • CVE-2026-64232CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: block: recompute nr_integrity_segments in blk_insert_cloned_request blk_insert_cloned_request() already recomputes...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.