
 Do Son
Critical CVSS 10 update for Gemini CLI (@google/gemini-cli). Fixes headless RCE and --yolo prompt injection risks. Upgrade to v1.83.7 to secure your pipelines.
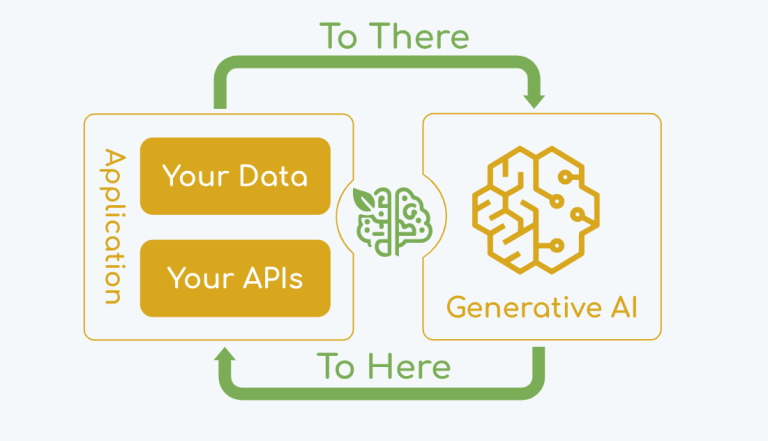
Spring AI discloses two critical injection flaws (CVE-2026-40967 & 40978) in Vector Store implementations. Upgrade to v1.0.6 or v1.1.5 now to prevent data leaks.

PRC national Xu Zewei extradited to the US for HAFNIUM intrusions and targeting COVID-19 research. He faces a 9-count indictment for state-sponsored hacks.
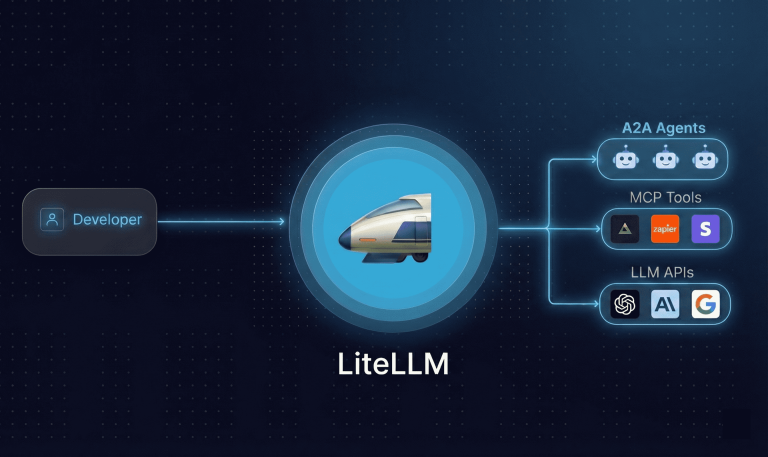
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.

Apache MINA (CVE-2026-41635) suffers a critical 9.8 CVSS RCE flaw. Learn how a deserialization filter bypass puts servers at risk and how to patch today.
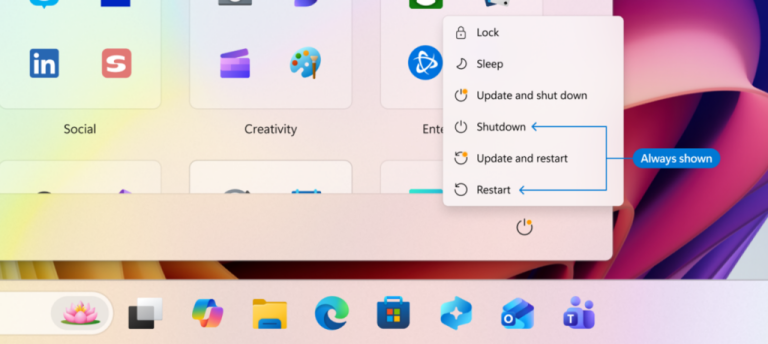
Microsoft is fixing the most frustrating part of Windows 11. Build 26300.8289 separates updates from standard restart/shutdown and allows indefinite pauses.

OpenAI is building an AI-first smartphone with MediaTek and Luxshare. Ditching apps for autonomous agents, this device aims to master the mobile ecosystem.

Amazon launches Claude Platform on AWS. Direct access to Anthropic's native AI features with AWS IAM security and billing—perfect for rapid AI innovation.
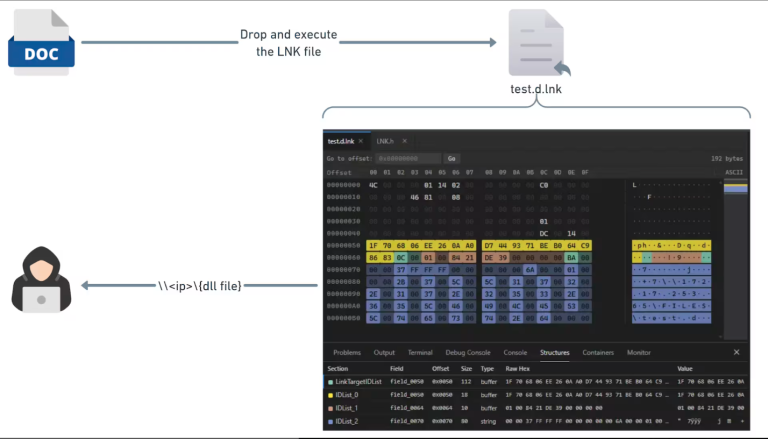
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!
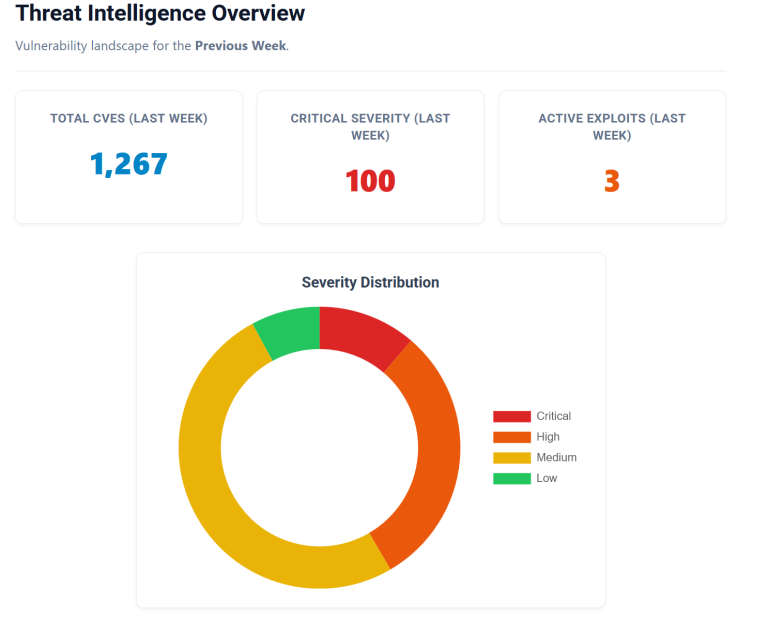
Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20,Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20, 2026. 2026.

Kaspersky reveals PhantomRPC, a novel Windows architectural flaw enabling LPE to SYSTEM. Microsoft denies a patch. Monitor SeImpersonatePrivilege now.

Critical 9.8 CVSS RCE in Pipecat (CVE-2025-62373)! Unsafe pickle deserialization allows remote code execution. Patch to v0.0.94 immediately to secure agents.

Carlson VASCO-B GNSS receivers face a critical 9.4 CVSS flaw with zero authentication. Stop remote attackers from drifting your location data. Update to v1.4.0.

Critical 9.8 CVSS flaw (CVE-2026-6074) in Intrado 911 Gateway allows unauthenticated access to management tools. Protect emergency services and patch today.
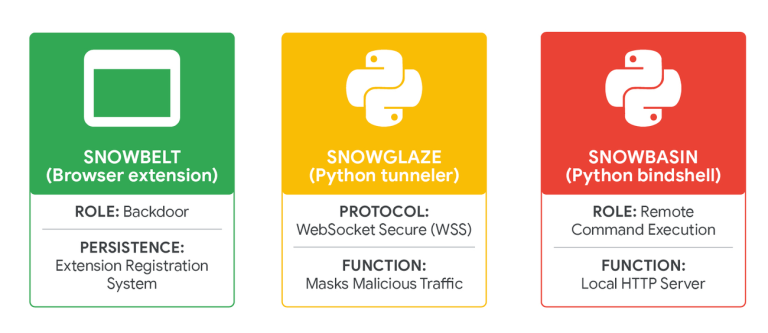
UNC6692 uses MS Teams impersonation to deploy the SNOW suite. Learn how "living off the cloud" bypasses reputation filters to hijack Active Directory.
North Korean group HexagonalRodent stole millions in Q1 2026 using AI-generated lures and backdoored VS Code tasks. Protect your Web3 wallet now.
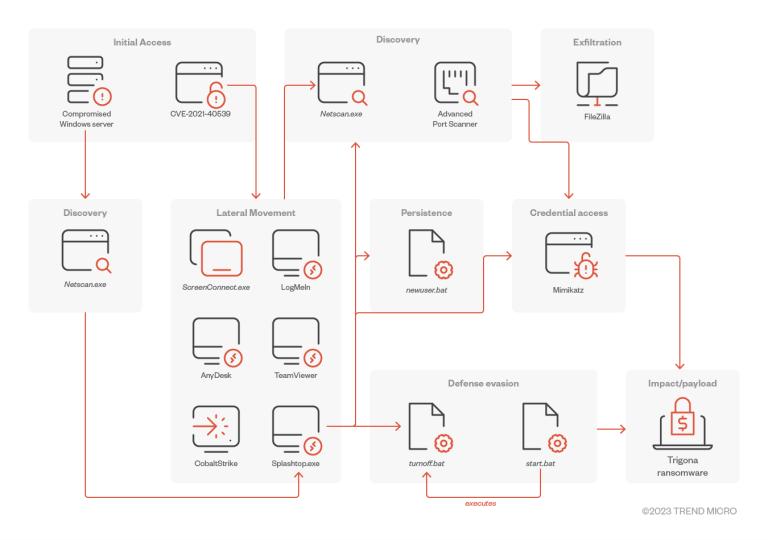
Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.

Unpatched CVE-2026-5756 in DRC INSIGHT allows unauthenticated hijacking of student exam responses and traffic manipulation. Secure your school's network now.
New Spring Boot flaws (CVSS 9.1) bypass security filters and enable RCE via timing attacks. Impacting versions 2.7.x to 4.0.x—secure your Java apps now.
Critical RCE and XSS vulnerabilities hit Apache ActiveMQ (CVE-2026-41044, 40466). Authenticated attackers can hijack the JVM. Update to 5.19.6 or 6.2.5 now.

Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.

Cato Networks reveals 235,500+ Modbus probes on PLCs across 70 countries. Learn how attackers fingerprint and hijack industrial control systems. Patch now.