
 Do Son
Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.

Cato Networks reveals 235,500+ Modbus probes on PLCs across 70 countries. Learn how attackers fingerprint and hijack industrial control systems. Patch now.

SentinelLABS reveals fast16, a 2005 framework that predates Stuxnet. It sabotages high-precision calculations in nuclear research by patching math in memory.

Dabai Guarantee emerges as the new hub for Chinese cybercrime, using Telegram and "ghost-tapping" to coordinate global retail fraud and USDT money laundering.

OpenAI launches GPT-5.5: a revolutionary agentic model co-designed with NVIDIA. Discover how it solves 58% of GitHub issues and automates senior engineering.
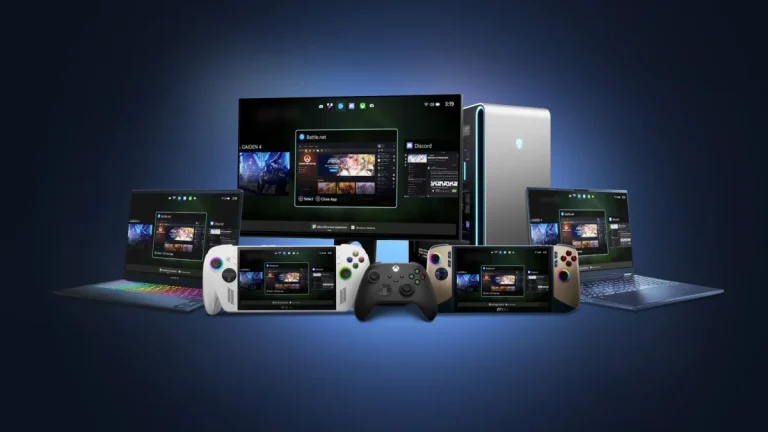
Xbox is back. Microsoft retires the "Microsoft Gaming" name and unveils Project Helix—a radical console-PC hybrid designed to win the living room in 2026.

Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.

OpenAI debuts Workspace Agents: Codex-powered digital laborers that work 24/7 in cloud sandboxes to manage sales, IT audits, and reporting autonomously.

X product lead Nikita Bier debuts Custom Timelines and Snooze Topics. Powered by Grok AI, these Premium-only tools offer 75+ categories for a bespoke feed.

Tropic Trooper's 2026 campaign uses trojanized SumatraPDF and VS Code tunnels for stealthy East Asian espionage. Learn how to defend your infrastructure.

Linux maintainers propose purging 27,646 lines of legacy network code to combat a flood of AI-generated vulnerability reports and focus on modern security.

OpenAI's new 1.5B Privacy Filter uses semantic reasoning to tag sensitive data locally. Run PII protection on consumer hardware with 128K context support.


ClawCloud Run is shutting down. With free tiers ending May 11, 2026, and a strict refund deadline of May 20, users must migrate data immediately to avoid loss.

Critical 9.8 CVSS auth bypass hits Xiongmai IP cameras. Public PoC is live with NO patch available. Secure your live feeds and isolate your devices now!
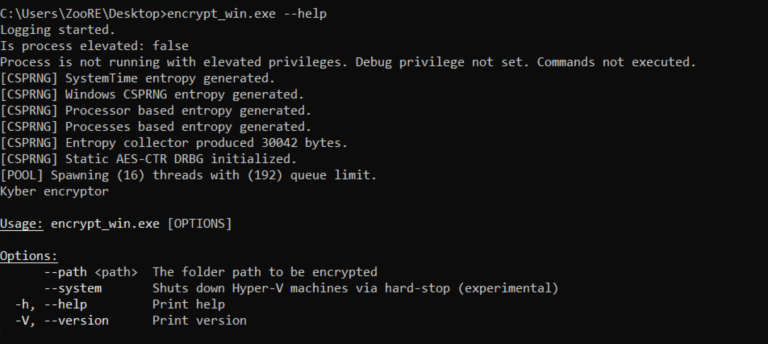
Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.

Bitwarden CLI v2026.4.0 compromised in "Dune"-themed supply chain attack. Malware steals cloud secrets and SSH keys. Rotate your credentials immediately.

Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.

Python’s asyncio on Windows faces a high-severity RCE (CVE-2026-3298). A missing boundary check in ProacterEventLoop risks memory corruption. Update now.

Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.

Unpatched CVE-2026-5757 in Ollama allows unauthenticated heap memory exfiltration via crafted GGUF files. No patch available—secure your LLM servers now.