Skip to content
October 29, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Unpatched Shopware Flaw CVE-2026-104937 Turns Stored XSS Into Admin Takeover and RCE Shopware vulnerability CVE-2026-104937 stored XSS leading to admin token theft and remote code execution
  • Vulnerability Report

Unpatched Shopware Flaw CVE-2026-104937 Turns Stored XSS Into Admin Takeover and RCE

Do Son October 14, 2026 0

An unpatched Shopware vulnerability, CVE-2026-104937, lets stored XSS steal admin tokens and lead to RCE in Shopware 6.7. Restrict media uploads now.
Chrome 155 Security Update Fixes 37 Flaws, Including Seven Critical Bugs Chrome security update 155 fixes use after free and buffer overflow vulnerabilities
  • Vulnerability Report

Chrome 155 Security Update Fixes 37 Flaws, Including Seven Critical Bugs

Do Son October 14, 2026 0

The Chrome security update to version 155 fixes 37 flaws, including seven critical bugs and 25 use after free issues. Update Chrome now.
TanStack CVE-2026-102989 (CVSS 9.3) Reflected XSS Hits Ecosystem With 98M Monthly Downloads TanStack Start vulnerability CVE-2026-102989 reflected XSS in server function responses
  • Vulnerability Report

TanStack CVE-2026-102989 (CVSS 9.3) Reflected XSS Hits Ecosystem With 98M Monthly Downloads

Do Son October 14, 2026 0

A TanStack Start vulnerability, CVE-2026-102989 (CVSS 9.3), allows unauthenticated reflected XSS via crafted links. Upgrade to the patched packages.
NVIDIA Fixes 18 AI Software Flaws, Led by CVSS 10.0 Bug in AIStore NVIDIA AIStore vulnerabilities enabling remote code execution in AI storage and training tools
  • Vulnerability Report

NVIDIA Fixes 18 AI Software Flaws, Led by CVSS 10.0 Bug in AIStore

Do Son October 13, 2026 0

NVIDIA AIStore vulnerabilities, including a CVSS 10.0 flaw enabling remote code execution, lead 18 fixes across NVIDIA AI tools. Upgrade to AIStore 5.0.
Docker Hub Security Advisory: CVE-2026-105445 Token Flaw Docker Hub security advisory for CVE-2026-105445 access token vulnerability
  • Vulnerability Report

Docker Hub Security Advisory: CVE-2026-105445 Token Flaw

Do Son October 13, 2026 0

Read the latest Docker Hub security advisory regarding CVE-2026-105445. Learn how this critical access token vulnerability impacts supply chain security.
Wazuh Fixes 15 Vulnerabilities, Including Two Critical Root Code Execution Flaws Wazuh vulnerabilities enabling remote code execution as root on SIEM managers and agents
  • Vulnerability Report

Wazuh Fixes 15 Vulnerabilities, Including Two Critical Root Code Execution Flaws

Do Son October 13, 2026 0

Fifteen Wazuh vulnerabilities, including two CVSS 9.4 flaws that allow remote code execution as root, are fixed in 4.14.8. Upgrade managers and agents now.
Fortinet Patches Critical FortiSandbox and FortiSIEM Flaws Among 13 Vulnerabilities Fortinet vulnerabilities FortiSandbox authentication bypass and FortiSIEM code execution patched in October 2026
  • Vulnerability Report

Fortinet Patches Critical FortiSandbox and FortiSIEM Flaws Among 13 Vulnerabilities

Do Son October 13, 2026 0

Thirteen Fortinet vulnerabilities are now fixed, including a CVSS 9.6 FortiSandbox authentication bypass and a 9.4 FortiSIEM flaw. Patch now.
Ivanti Connect Secure Zero-Day Chain CVE-2026-104935 Exploited by UTA0576 to Gain Root Access Ivanti Connect Secure zero-day exploit chain CVE-2026-104935 used by UTA0576 to gain root access on a VPN appliance
  • Cybercriminals

Ivanti Connect Secure Zero-Day Chain CVE-2026-104935 Exploited by UTA0576 to Gain Root Access

Do Son October 13, 2026 0

UTA0576 chained an Ivanti Connect Secure zero-day, CVE-2026-104935, with a root exploit to steal AD credentials. Patch now and check memory.
Zoom Patches Four High-Severity Flaws in Workplace Clients, Including Privilege Escalation Bugs Zoom Workplace vulnerabilities enabling privilege escalation and information disclosure
  • Vulnerability Report

Zoom Patches Four High-Severity Flaws in Workplace Clients, Including Privilege Escalation Bugs

Do Son October 13, 2026 0

Four Zoom Workplace vulnerabilities, including privilege escalation and certificate flaws rated up to CVSS 8.1, are now fixed. Update to 7.2.0 or later.
Ivanti Fixes Two CVSS 9.9 Flaws in Neurons Patch for Intune and Xtraction That Leak Credentials Ivanti critical vulnerabilities in Neurons Patch for Intune and Xtraction enabling credential theft
  • Vulnerability Report

Ivanti Fixes Two CVSS 9.9 Flaws in Neurons Patch for Intune and Xtraction That Leak Credentials

Do Son October 13, 2026 0

Two Ivanti critical vulnerabilities rated CVSS 9.9 in Neurons Patch for Intune and Xtraction risk credential theft. Update Xtraction and rotate secrets.
Siemens Warns of Eight Unpatched SIMATIC S7-1500 Web Server Flaws Rated Up to CVSS 9.4 Siemens S7-1500 vulnerabilities cross-site scripting in SIMATIC PLC web server trace files
  • Vulnerability Report

Siemens Warns of Eight Unpatched SIMATIC S7-1500 Web Server Flaws Rated Up to CVSS 9.4

Do Son October 13, 2026 0

Eight unpatched Siemens S7-1500 vulnerabilities enable cross-site scripting in the PLC web server, rated up to CVSS 9.4. Apply Siemens mitigations now.
Ivanti Connect Secure Vulnerability CVE-2026-104935 Exploited in the Wild Ivanti Connect Secure vulnerability CVE-2026-104935 exploited in the wild against VPN gateways
  • Vulnerability Report

Ivanti Connect Secure Vulnerability CVE-2026-104935 Exploited in the Wild

Do Son October 13, 2026 0

Ivanti Connect Secure vulnerability CVE-2026-104935 is exploited in the wild, letting unauthenticated attackers run commands. Update to 25.1.1.2 now.
Criminal IP to Showcase Threat Intelligence and AITEM at Security Days Fall 2026 Tokyo 1_1791335386Gx2p3olWCv
  • Press Release

Criminal IP to Showcase Threat Intelligence and AITEM at Security Days Fall 2026 Tokyo

cybernewswire October 13, 2026 0
Torrance, California, 13th October 2026, CyberNewswire
Read More Read more about Criminal IP to Showcase Threat Intelligence and AITEM at Security Days Fall 2026 Tokyo
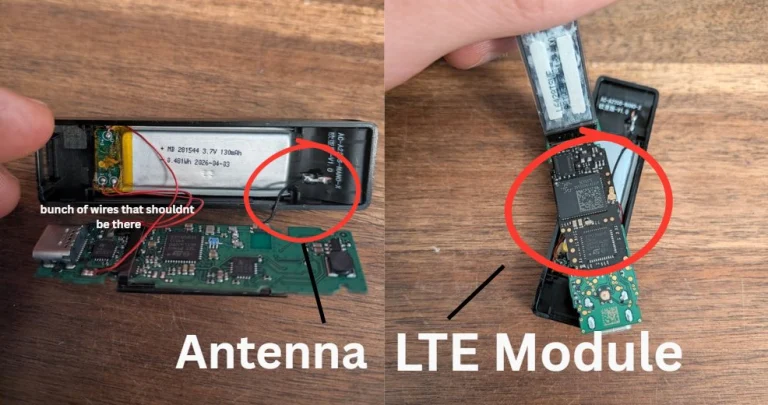
Ledger Supply Chain Attack Hits Europe via Tampered Wallets Ledger Nano X hardware wallet dismantled showing malicious LTE module modification
  • Malware

Ledger Supply Chain Attack Hits Europe via Tampered Wallets

Do Son October 13, 2026 0

A devastating Ledger supply chain attack has reached Europe. Hackers are embedding malicious LTE modules into hardware wallets to steal cryptocurrency.
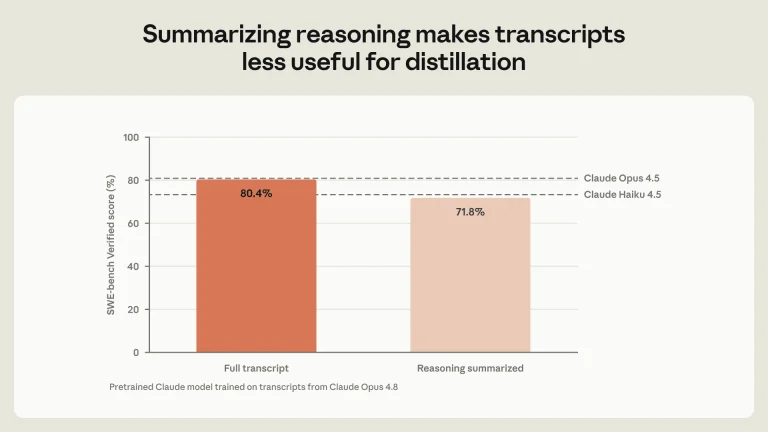
Anthropic Fortifies Claude AI Against Model Distillation Anthropic Claude AI model distillation protection mechanism
  • Technology

Anthropic Fortifies Claude AI Against Model Distillation

Do Son October 13, 2026 0

Discover how Anthropic combats unauthorized AI model distillation. Learn about the new robust protective mechanisms securing Claude AI reasoning outputs.
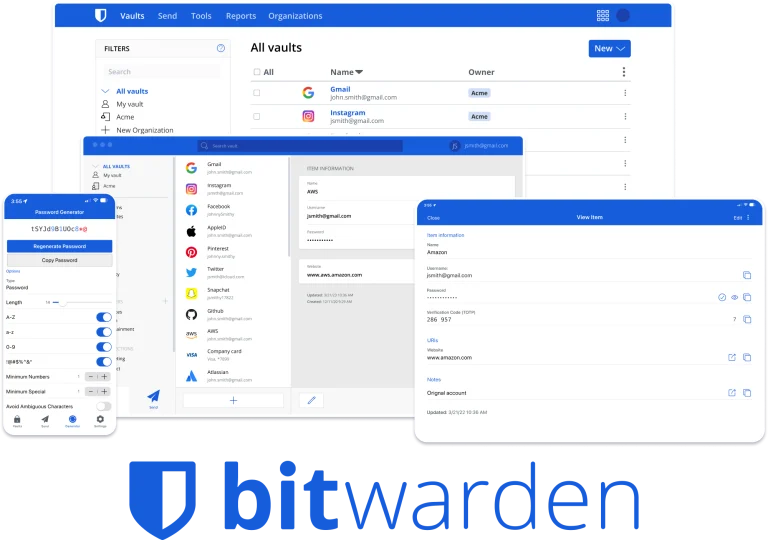
Bitwarden App Store License Changes to Commercial Model Bitwarden application logo and password manager interface on a mobile device
  • Technology

Bitwarden App Store License Changes to Commercial Model

Do Son October 13, 2026 0

Discover the new Bitwarden app store license changes. Learn how the shift from GPLv3 to a commercial model affects future updates and self-hosted versions.
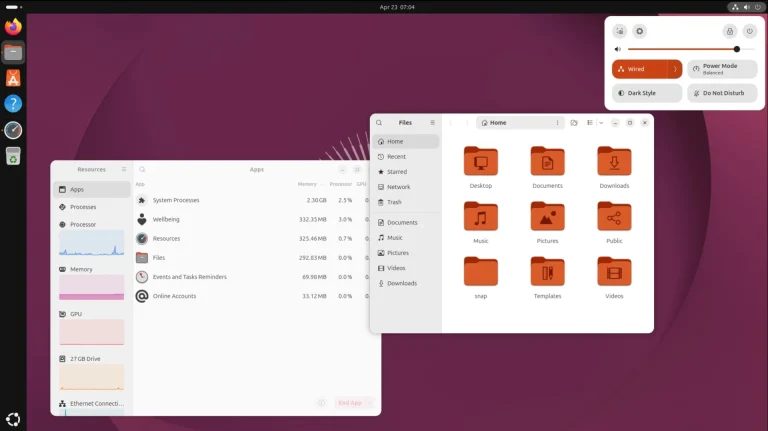
Ubuntu 27.04 Release Schedule: Tenacious T-Rex Ubuntu 27.04 release schedule and Tenacious T-Rex codename details
  • Linux

Ubuntu 27.04 Release Schedule: Tenacious T-Rex

Do Son October 13, 2026 0

Discover the Ubuntu 27.04 release schedule. Code-named Tenacious T-Rex, this interim release brings new features and kernels for desktop enthusiasts.
G2A.COM Reports 35% Growth in Security Software Orders, Outpacing VPN Growth G2A_Logo_RGB_Color_Dark_1791212026FxtySSNVFq
  • Press Release

G2A.COM Reports 35% Growth in Security Software Orders, Outpacing VPN Growth

cybernewswire October 13, 2026 0
Amsterdam, Netherlands, 13th October 2026, CyberNewswire
Read More Read more about G2A.COM Reports 35% Growth in Security Software Orders, Outpacing VPN Growth
Malicious npm Packages From Fake Web3 Accelerator Apex Deliver Stealers and Hijack AI Coding Agents Malicious npm packages from the fake Web3 accelerator Apex delivering CloudSyncD and a Windows infostealer
  • Malware

Malicious npm Packages From Fake Web3 Accelerator Apex Deliver Stealers and Hijack AI Coding Agents

Do Son October 13, 2026 0

A fake Web3 accelerator used malicious npm packages to drop stealers on macOS and Windows and reroute AI coding agent traffic to its servers.
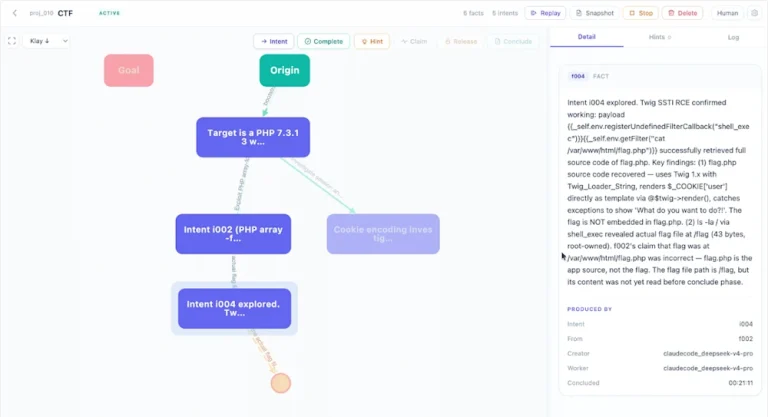
AI Agent Attack Turns One Exposed Endpoint Into a Full Server Takeover in Under 24 Hours AI agent attack using the Cairn orchestration platform to achieve a full server takeover through an exposed job endpoint
  • Malware

AI Agent Attack Turns One Exposed Endpoint Into a Full Server Takeover in Under 24 Hours

Do Son October 13, 2026 0

ReliaQuest details an AI agent attack that used one exposed endpoint and the Cairn platform to achieve a full server takeover in under 24 hours.
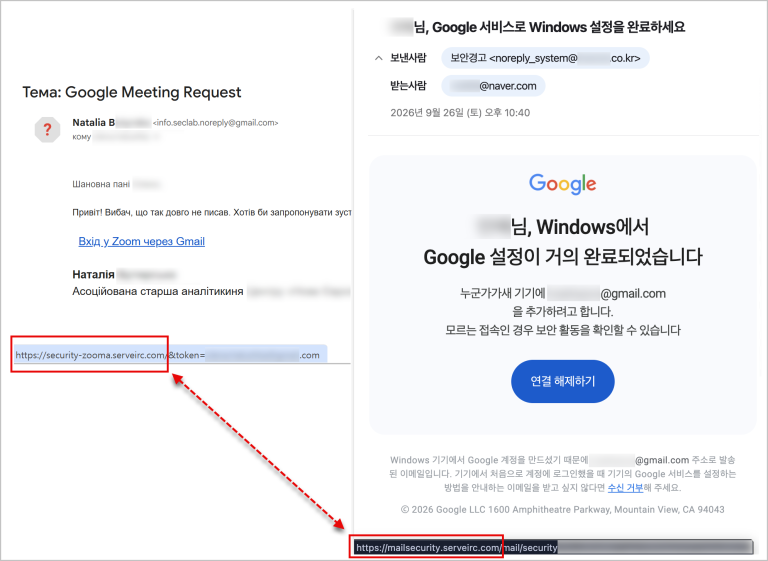
Kimsuky Spear Phishing Targets Ukrainian Diplomacy and Security Experts in Operation GitPower Kimsuky spear phishing email with fake KCSCON speaker invitation targeting Ukrainian experts in Operation GitPower
  • Cybercriminals

Kimsuky Spear Phishing Targets Ukrainian Diplomacy and Security Experts in Operation GitPower

Do Son October 13, 2026 0

Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
Windows 11 23H2 EOL: Enterprise Support Concludes Windows 11 23H2 EOL announcement on a computer screen
  • Windows

Windows 11 23H2 EOL: Enterprise Support Concludes

Do Son October 13, 2026 0

The Windows 11 23H2 EOL date is November 10, 2026. Discover how the end of support affects Enterprise editions and why immediate upgrades are crucial.

❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
  • CVE-2026-101767CVSS 9.8
    Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-83748CVSS 9.8
    Heap-based buffer overflow in Windows Error Reporting allows an unauthorized attacker to execute code over a network.
    📅 Updated: Oct 29, 2026
  • CVE-2026-90531CVSS 9.6
    Adobe Experience Manager is affected by an Improper Restriction of XML External Entity Reference ('XXE') vulnerability that could...
    📅 Updated: Oct 29, 2026
  • CVE-2026-103093CVSS 9.4
    ServiceNow has remediated a sandbox escape security issue that was identified in the ServiceNow AI Platform. This vulnerability...
    📅 Updated: Oct 29, 2026
  • CVE-2026-112380CVSS 9.0
    Missing authorization in the WhatsApp group channel in Kiro Crew might allow a remote actor who is a...
    📅 Updated: Oct 29, 2026
  • CVE-2026-83910CVSS 9.8
    Out-of-bounds write in RPC Runtime allows an unauthorized attacker to execute code over a network.
    📅 Updated: Oct 29, 2026
  • CVE-2026-97406CVSS 9.1
    XERJ Console API bearer tokens can bypass the passkey‑only authentication requirement and directly invoke the API‑token creation endpoint,...
    📅 Updated: Oct 29, 2026
  • CVE-2026-91230CVSS 9.3
    Vulnerability in the Oracle SOA Suite product of Oracle Fusion Middleware (component: Fabric Layer). Supported versions that are...
    📅 Updated: Oct 29, 2026
  • CVE-2026-91231CVSS 10.0
    Vulnerability in the Oracle SOA Suite product of Oracle Fusion Middleware (component: Adapters). Supported versions that are affected...
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.