 Do Son
A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!
Ubiquiti fixes critical 9.8 CVSS RCE flaws in UniFi Play PowerAmp and Audio Port. Don't let attackers control your sound—update your firmware immediately.
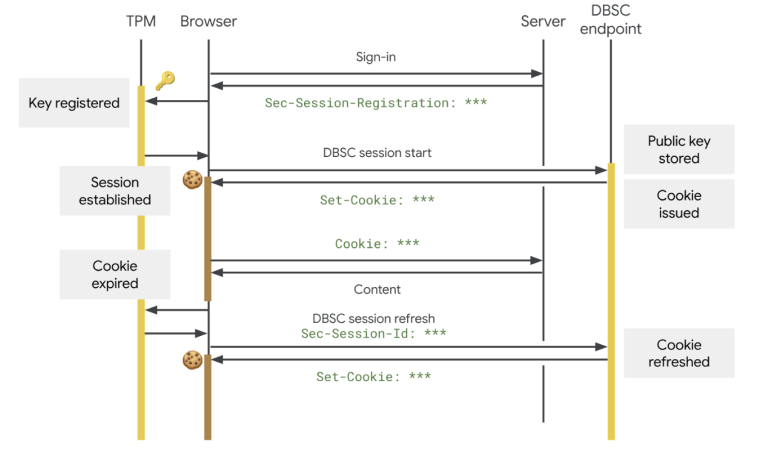
Google launches DBSC in Chrome 146, binding session cookies to hardware like TPM. Neutralize infostealers and stop session hijacking with this new standard.

Apache NiFi 2.9.0 fixes a high-severity RCE (CVE-2026-39816) in the Tinkerpop service. Secure your data pipelines and verify your annotations today!

Trellix ARC reveals Masjesu, a stealthy, professional IoT botnet operational since 2023. Targeted DDoS-for-hire with a low-profile strategy. Patch now!

SAP’s April 2026 updates fix a critical 9.9 CVSS SQL injection in Business Warehouse and 19 other security flaws. Audit your S/4HANA and BPC systems today.

Microsoft warns of a 50M-user flaw in EngageSDK affecting crypto wallets. An intent redirection bug could leak private data. Update to v5.2.1 now!

Kaspersky reveals a fileless Trojan campaign targeting Proxifier searches. Learn how this "ClipBanker" hijacks crypto wallets via search engine poisoning.

Microsoft DART uncovers Storm-2755, a "payroll pirate" using AiTM traps and SEO poisoning to steal salaries. Protect your organization from this MFA bypass.
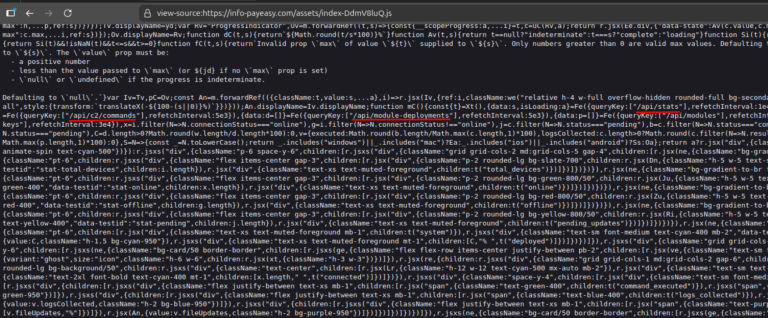
Hunt.io discovers Canis C2, an AI-assisted surveillance framework targeting all major OSs. An exposed API revealed payloads and source code. Read more here.
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!

Synology urges SSL VPN Client users to update to v1.4.5-0684. Fixes critical 8.1 CVSS flaw allowing PIN theft and traffic interception. Secure your data now!

Mitsubishi Electric warns of 9.3 CVSS flaws in GENESIS64 & ICONICS. Attackers can leak SQL credentials to destroy or tamper with industrial data. Patch now!

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!

Apache Log4j 2.25.4 fixes 4 "silent" flaws, including TLS bypasses and log injection. Secure your infrastructure—upgrade now to prevent data loss.
Apache ActiveMQ patches critical TLSv1.3 memory exhaustion (CVE-2026-39304) and an MQTT regression. Upgrade to 6.2.4 or 5.19.5 to secure your broker!

Apache OpenMeetings 9.0.0 fixes critical flaws including hard-coded "remember-me" keys and REST login credential exposure. Secure your video suite today!
Apache Storm patches a critical RCE via unsafe deserialization and a stored XSS in its UI. Secure your data streams—upgrade to version 2.8.6 today!
LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!

Organizations often focus on known assets during security assessments, but many systems and applications exist outside official...

Microsoft has retired its legacy telephone activation system. Learn how to use the new Web Activation Portal to license Windows and Office without an internet connection.

April 2026 Alert: CPUID downloads for CPU-Z and HWMonitor were poisoned with STX RAT via DLL sideloading. Check your systems for CRYPTBASE.dll now!