Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical—9 Vulnerabilities in Orthanc DICOM Servers Threaten Medical Data Integrity CVE-2025-2263 Orthanc Security DICOM Vulnerabilities
  • Vulnerability Report

Critical—9 Vulnerabilities in Orthanc DICOM Servers Threaten Medical Data Integrity

Do Son April 14, 2026 0

Orthanc v1.12.11 patches 9 critical flaws, including RCE risks and "decompression bombs" in DICOM servers. Secure your healthcare data—upgrade now!

Juju’s CVSS 10 Flaw Hands Over Master Cloud Credentials Juju Orchestration Cloud Credential Theft Juju Orchestration Vulnerability CVE-2026-4370
  • Vulnerability Report

Juju’s CVSS 10 Flaw Hands Over Master Cloud Credentials

Do Son April 14, 2026 0

Juju's critical CVSS 10 flaw (CVE-2026-5412) allows low-level users to steal master cloud credentials. Secure your AWS/Azure/GCP environments—upgrade now!
CVE-2026-4810: Critical 9.3 RCE Flaw Hits Google’s AI Agent Development Kit Google ADK Vulnerability AI Agent RCE
  • Vulnerability Report

CVE-2026-4810: Critical 9.3 RCE Flaw Hits Google’s AI Agent Development Kit

Do Son April 14, 2026 0

Google ADK (CVE-2026-4810) faces a critical 9.3 CVSS RCE flaw. Unauthenticated attackers can hijack AI agents on GKE & Cloud Run. Update and redeploy now!
5 Best Autonomous Penetration Testing Tools in 2026 Employees Risk
  • Technique

5 Best Autonomous Penetration Testing Tools in 2026

Do Son April 14, 2026 0
Most pentest reports start losing value the moment the environment changes. That happens fast. New assets appear,...
Read More Read more about 5 Best Autonomous Penetration Testing Tools in 2026
The Final Countdown: Microsoft Sets October 2026 for Office 2021 Support Shutdown Office 2021 End of Life CVE-2024-21413 KB5002700 Office 2016 Update
  • Technology

The Final Countdown: Microsoft Sets October 2026 for Office 2021 Support Shutdown

Do Son April 14, 2026 0

Office 2021 reaches its end of life on October 13, 2026. Learn about the security risks and discover your upgrade paths to Office 2024 or Microsoft 365.
CVE-2026-4631: Critical 9.8 RCE Flaw in Cockpit Allows Unauthenticated Server Takeover Cockpit RCE CVE-2026-4631
  • Vulnerability Report

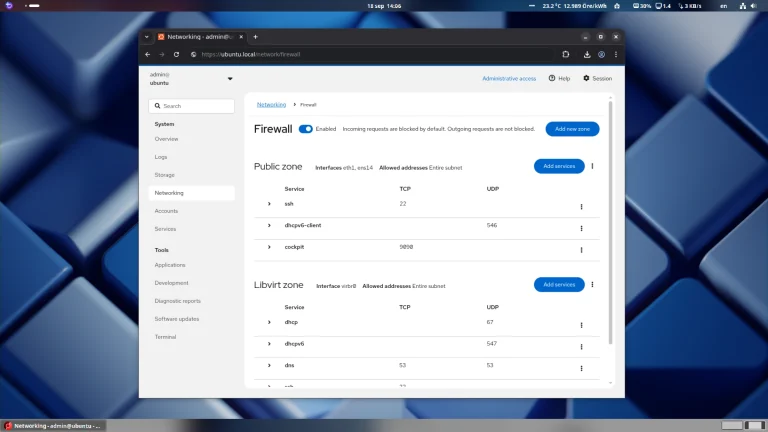
CVE-2026-4631: Critical 9.8 RCE Flaw in Cockpit Allows Unauthenticated Server Takeover

Do Son April 14, 2026 0

Cockpit CVE-2026-4631 allows unauthenticated RCE on Linux servers via SSH injection. Stop the unauthorized takeover—upgrade to Cockpit version 360 now!

The Sunset of Speed: Microsoft Sets Final Shutdown Date for Outlook Lite on Android Outlook Lite Retirement 2026
  • Technology

The Sunset of Speed: Microsoft Sets Final Shutdown Date for Outlook Lite on Android

Do Son April 14, 2026 0

Outlook Lite for Android is officially shutting down on May 25, 2026. Learn how to migrate to the full Outlook Mobile app to keep your emails and calendar safe.

Supply Chain Sabotage: The Critical RCE Flaws Lurking in PHP Composer CVE-2026-40176, CVE-2026-40261 Composer GitHub Token Leak CVE-2026-45793
  • Vulnerability Report

Supply Chain Sabotage: The Critical RCE Flaws Lurking in PHP Composer

Do Son April 14, 2026 0

Critical Remote Command Injection flaws in PHP Composer's Perforce integration (CVE-2026-40176 & CVE-2026-40261) could lead to full system compromise. Patch now.

Breaking the 5-Week Limit: Windows 11 to Finally Grant Users Total Update Autonomy Windows 11 Update Deferral
  • Windows

Breaking the 5-Week Limit: Windows 11 to Finally Grant Users Total Update Autonomy

Do Son April 14, 2026 0

Microsoft is testing a new date-selection tool for Windows 11 that could let you pause updates for years. Say goodbye to forced reboots and the 5-week limit.
Check Your Inbox: Booking.com Forced to Reset PINs After Major Data Leak Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

Check Your Inbox: Booking.com Forced to Reset PINs After Major Data Leak

Do Son April 14, 2026 0

Booking.com confirms a data breach exposing names, emails, and itineraries. Learn how to verify official alerts and protect yourself from new phone scams.

The Archival Crisis: Why The New York Times and Reddit are Purging The Wayback Machine Wayback Machine AI Blockade Internet Archive, FDLP Designation Internet Archive, copyright lawsuit
  • Technology

The Archival Crisis: Why The New York Times and Reddit are Purging The Wayback Machine

Do Son April 14, 2026 0

Major publishers are blocking the Internet Archive to stop AI firms from stealing data. Discover how the "ia_archiver" became collateral damage in the AI wars.

Google’s New Deadline: Why Your Site’s “Back Button” Could Get You De-Indexed by June 15 Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Google’s New Deadline: Why Your Site’s “Back Button” Could Get You De-Indexed by June 15

Do Son April 14, 2026 0

Google formally classifies back-button hijacking as a "malicious practice." Fix your navigation scripts by June 15, 2026, or face total search de-indexing.

Python Under Pressure: Critical Memory Flaws and Command Injection Bypass Uncovered Python Security Memory Safety PLY Vulnerability CVE-2025-56005 Python Software Foundation, NSF DEI CVE-2024-12254
  • Vulnerability

Python Under Pressure: Critical Memory Flaws and Command Injection Bypass Uncovered

Do Son April 14, 2026 0

Python patches a critical 9.1 UAF flaw in decompressors and a browser command injection bypass. Protect your infrastructure—audit your CPython code today!

New Stealth Attack Chain Weaponizes Legitimate Remote Access Software ScreenConnect Hijack In-Memory Attack
  • Malware

New Stealth Attack Chain Weaponizes Legitimate Remote Access Software

Do Son April 14, 2026 0

Zscaler reveals a 2026 attack chain using fake Adobe Reader lures to install ScreenConnect via in-memory execution and UAC bypass. Protect your network now!

Critical wolfSSL Flaw Could Allow Attackers to Spoof Trusted Hosts wolfSSL Vulnerability Certificate Validation Bypass wolfSSH Vulnerability CVE-2025-14942
  • Vulnerability Report

Critical wolfSSL Flaw Could Allow Attackers to Spoof Trusted Hosts

Do Son April 14, 2026 0

wolfSSL (CVE-2026-5194) faces a critical 9.3 CVSS flaw in ECDSA certificate validation. Attackers can bypass security and spoof trusted hosts. Audit today!
CISA Adds 7 Fresh Exploits to KEV Catalog CISA KEV Catalog Active Exploitation CVE-2023-33063 - CVE-2023-34192 and CVE-2024-49035
  • Vulnerability Report

CISA Adds 7 Fresh Exploits to KEV Catalog

Do Son April 14, 2026 0

CISA adds 7 active exploits to the KEV catalog, from legacy Office bugs to 2026 Fortinet zero-days. Patch these high-risk flaws now to secure your network.
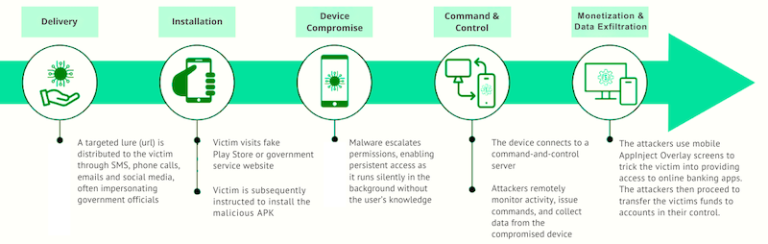
Inside the Global “MaaS” Engine of the K99 Scam Compound K99 Malware Biometric Hijacking
  • Malware

Inside the Global “MaaS” Engine of the K99 Scam Compound

Do Son April 14, 2026 0

Infoblox uncovers the K99 compound: a brutal MaaS operation using human trafficking to power biometric hijacking and global Android banking fraud.
Critical 9.8 RCE Flaw in Qlik Talend Threatens Enterprise Data Pipelines CVE-2023-48365 Talend JobServer RCE JMX Port Vulnerability
  • Vulnerability Report

Critical 9.8 RCE Flaw in Qlik Talend Threatens Enterprise Data Pipelines

Do Son April 14, 2026 0

Qlik issues a critical 9.8 CVSS alert for Talend JobServer and Runtime. Unauthenticated RCE via JMX ports puts data pipelines at risk. Patch immediately.
Maximum Severity RCE Vulnerability Decimating Paperclip AI Instances Paperclip RCE AI Agent Security Paperclip RCE Cross-Tenant AI Takeover
  • Vulnerability Report

Maximum Severity RCE Vulnerability Decimating Paperclip AI Instances

Do Son April 14, 2026 0

A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!
Hijacking the Soundboard: Critical 9.8 RCE Flaws Hit Ubiquiti UniFi Play Audio UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Hijacking the Soundboard: Critical 9.8 RCE Flaws Hit Ubiquiti UniFi Play Audio

Do Son April 14, 2026 0

Ubiquiti fixes critical 9.8 CVSS RCE flaws in UniFi Play PowerAmp and Audio Port. Don't let attackers control your sound—update your firmware immediately.
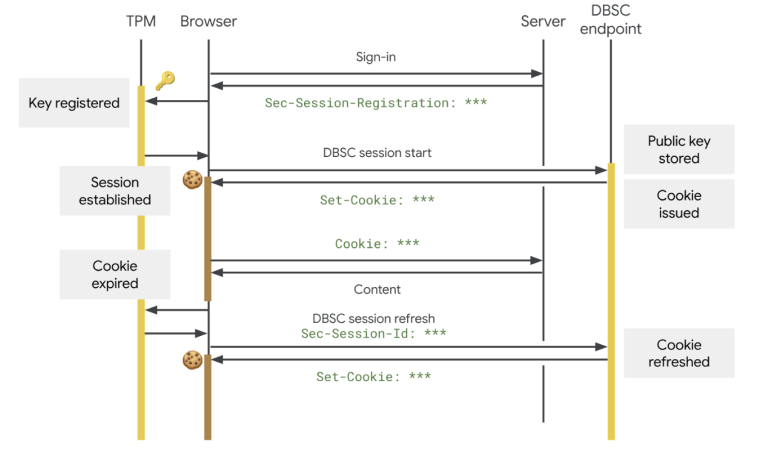
Hardware-Locked: How Chrome’s New DBSC Makes Stolen Cookies Worthless Device Bound Session Credentials (DBSC) Session Hijacking Prevention
  • Technology

Hardware-Locked: How Chrome’s New DBSC Makes Stolen Cookies Worthless

Do Son April 14, 2026 0

Google launches DBSC in Chrome 146, binding session cookies to hardware like TPM. Neutralize infostealers and stop session hijacking with this new standard.

Apache NiFi Patches High-Severity Code Execution Flaw Apache NiFi RCE CVE-2026-39816 Apache NiFi Vulnerability CVE-2026-25903 Apache NiFi Deserialization, GetAsanaObject Vulnerability CVE-2024-52067 - CVE-2024-56512 CVE-2025-27017
  • Vulnerability

Apache NiFi Patches High-Severity Code Execution Flaw

Do Son April 14, 2026 0

Apache NiFi 2.9.0 fixes a high-severity RCE (CVE-2026-39816) in the Tinkerpop service. Secure your data pipelines and verify your annotations today!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-118423CVSS 10.0
    The WP Libre Form WordPress plugin 1.5.0.1 does not validate the type of files uploaded through its form...
    📅 Updated: Nov 6, 2026
  • CVE-2026-88800CVSS 9.1
    The MDJM Event Management and Mobile Events Manager WordPress plugins through 1.7.8.7 act on a role deletion request...
    📅 Updated: Nov 6, 2026
  • CVE-2026-83542CVSS 9.8
    Improper Control of Generation of Code ('Code Injection') in Apache OFBiz 24.09 before 24.09.08 on all platforms allows...
    📅 Updated: Nov 6, 2026
  • CVE-2026-82907CVSS 9.8
    Authentication Bypass by Capture-replay in ExternalLoginKeysManager in Apache OFBiz 24.09 before 24.09.08 on all platforms allows a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102894CVSS 9.1
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. From 0.7.1 until...
    📅 Updated: Nov 6, 2026
  • CVE-2026-86345CVSS 9.0
    A flaw was found in 389-ds-base. The server does not discard plaintext bytes already buffered from a client...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48752CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image or...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.