Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Apache NiFi Patches High-Severity Code Execution Flaw Apache NiFi RCE CVE-2026-39816 Apache NiFi Vulnerability CVE-2026-25903 Apache NiFi Deserialization, GetAsanaObject Vulnerability CVE-2024-52067 - CVE-2024-56512 CVE-2025-27017
  • Vulnerability

Apache NiFi Patches High-Severity Code Execution Flaw

Do Son April 14, 2026 0

Apache NiFi 2.9.0 fixes a high-severity RCE (CVE-2026-39816) in the Tinkerpop service. Secure your data pipelines and verify your annotations today!

Inside the Masjesu IoT Botnet’s 3-Year Stealth Reign Masjesu Botnet IoT DDoS Protection
  • Malware

Inside the Masjesu IoT Botnet’s 3-Year Stealth Reign

Do Son April 14, 2026 0

Trellix ARC reveals Masjesu, a stealthy, professional IoT botnet operational since 2023. Targeted DDoS-for-hire with a low-profile strategy. Patch now!

Critical 9.9 Alert: SAP’s April 2026 Patch Day Targets Major SQL Injection SAP security patch day critical security vulnerabilities SAP SQL Injection April 2026 Patch Day SAP Security, Critical Vulnerabilities Security Patch Day CVE-2025-42944
  • Vulnerability Report

Critical 9.9 Alert: SAP’s April 2026 Patch Day Targets Major SQL Injection

Do Son April 14, 2026 0

SAP’s April 2026 updates fix a critical 9.9 CVSS SQL injection in Business Warehouse and 19 other security flaws. Audit your S/4HANA and BPC systems today.

EngageSDK Flaw Exposes 50 Million Android Users to Data Theft EngageSDK Vulnerability Android Intent Redirection
  • Vulnerability Report

EngageSDK Flaw Exposes 50 Million Android Users to Data Theft

Do Son April 14, 2026 0

Microsoft warns of a 50M-user flaw in EngageSDK affecting crypto wallets. An intent redirection bug could leak private data. Update to v5.2.1 now!

The Proxifier Trap: The “Fileless” Marathon Stealing Your Crypto Proxifier Trojan Crypto ClipBanker
  • Malware

The Proxifier Trap: The “Fileless” Marathon Stealing Your Crypto

Do Son April 14, 2026 0

Kaspersky reveals a fileless Trojan campaign targeting Proxifier searches. Learn how this "ClipBanker" hijacks crypto wallets via search engine poisoning.

Payroll Pirates in the North: Microsoft Unmasks ‘Storm-2755’ and the Theft of Canadian Salaries Storm-2755 Payroll Piracy
  • Cybercriminals

Payroll Pirates in the North: Microsoft Unmasks ‘Storm-2755’ and the Theft of Canadian Salaries

Do Son April 14, 2026 0

Microsoft DART uncovers Storm-2755, a "payroll pirate" using AiTM traps and SEO poisoning to steal salaries. Protect your organization from this MFA bypass.
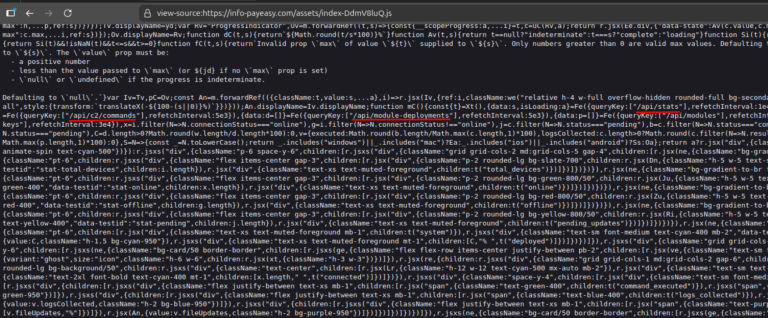
Inside Canis C2: The ‘Wide Open’ Surveillance Engine Targeting Every Major OS Canis C2 Surveillance System
  • Malware

Inside Canis C2: The ‘Wide Open’ Surveillance Engine Targeting Every Major OS

Do Son April 14, 2026 0

Hunt.io discovers Canis C2, an AI-assisted surveillance framework targeting all major OSs. An exposed API revealed payloads and source code. Read more here.
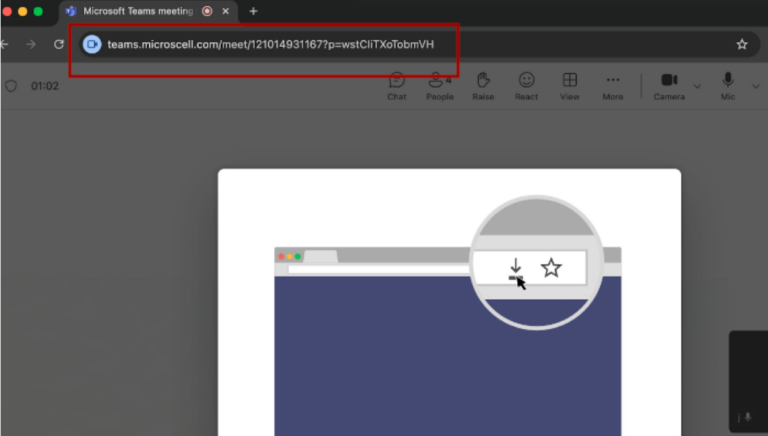
The Billion-Dollar Invite: How UNC1069’s Fake Meetings Hijack Crypto Fortunes UNC1069 Phishing BlueNoroff Crypto Theft
  • Cybercriminals

The Billion-Dollar Invite: How UNC1069’s Fake Meetings Hijack Crypto Fortunes

Do Son April 14, 2026 0

North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!

VPN Security Alert: Synology Patches Flaws in SSL VPN Client Synology Chat Server vulnerabilities Synology security update Synology DSM Update NAS Security Vulnerability Synology VPN Update SSL VPN Vulnerability Synology Telnet Flaw DSM Security Update Synology DSM Telnet vulnerability BeeStation Zero-Day, Pwn2Own RCE CVE-2024-11131 & CVE-2024-10442 CVE-2025-2848 Synology, NAS
  • Vulnerability Report

VPN Security Alert: Synology Patches Flaws in SSL VPN Client

Do Son April 14, 2026 0

Synology urges SSL VPN Client users to update to v1.4.5-0684. Fixes critical 8.1 CVSS flaw allowing PIN theft and traffic interception. Secure your data now!

Industrial Key Leak: Critical 9.3 CVSS Flaws Expose Mitsubishi’s GENESIS64 and ICONICS Suite Mitsubishi GENESIS64 Vulnerability SQL Credential Disclosure
  • Vulnerability Report

Industrial Key Leak: Critical 9.3 CVSS Flaws Expose Mitsubishi’s GENESIS64 and ICONICS Suite

Do Son April 14, 2026 0

Mitsubishi Electric warns of 9.3 CVSS flaws in GENESIS64 & ICONICS. Attackers can leak SQL credentials to destroy or tamper with industrial data. Patch now!

Critical SSRF Flaw Discovered in Axios – CVE-2025-62718 (CVSS 9.3) Axios Vulnerability NO_PROXY Bypass
  • Vulnerability Report

Critical SSRF Flaw Discovered in Axios – CVE-2025-62718 (CVSS 9.3)

Do Son April 14, 2026 0

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!

Log4j’s “Silent” Security Gap: New Advisories Warn of Data Loss and TLS Bypasses CVE-2021-45046 Log4j Security Silent Log Failures
  • Vulnerability Report

Log4j’s “Silent” Security Gap: New Advisories Warn of Data Loss and TLS Bypasses

Do Son April 13, 2026 0

Apache Log4j 2.25.4 fixes 4 "silent" flaws, including TLS bypasses and log injection. Secure your infrastructure—upgrade now to prevent data loss.
Apache ActiveMQ Patches “OOM” and MQTT Protocol Flaws Apache ActiveMQ Memory Exhaustion
  • Vulnerability Report

Apache ActiveMQ Patches “OOM” and MQTT Protocol Flaws

Do Son April 13, 2026 0

Apache ActiveMQ patches critical TLSv1.3 memory exhaustion (CVE-2026-39304) and an MQTT regression. Upgrade to 6.2.4 or 5.19.5 to secure your broker!

Triple Security Advisory Prompts Immediate Upgrade to Apache OpenMeetings Version 9.0.0 CVE-2023-28936 OpenMeetings Security Credential Theft
  • Vulnerability Report

Triple Security Advisory Prompts Immediate Upgrade to Apache OpenMeetings Version 9.0.0

Do Son April 13, 2026 0

Apache OpenMeetings 9.0.0 fixes critical flaws including hard-coded "remember-me" keys and REST login credential exposure. Secure your video suite today!
High-Severity RCE and XSS Vulnerabilities Patched in Apache Storm 2.8.6 Apache Storm RCE Deserialization Vulnerability
  • Vulnerability Report

High-Severity RCE and XSS Vulnerabilities Patched in Apache Storm 2.8.6

Do Son April 13, 2026 0

Apache Storm patches a critical RCE via unsafe deserialization and a stored XSS in its UI. Secure your data streams—upgrade to version 2.8.6 today!
LiteLLM Under Fire: Triple Threat Vulnerabilities Expose AI Gateways to Total Takeover LiteLLM SQL Injection CVE-2026-42208 LiteLLM Vulnerability AI Infrastructure Security
  • Vulnerability Report

LiteLLM Under Fire: Triple Threat Vulnerabilities Expose AI Gateways to Total Takeover

Do Son April 13, 2026 0

LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!

How Shadow IT Expands Attack Surface Between Pentests compagnons-Fa9b57hffnM-unsplash
  • Technique

How Shadow IT Expands Attack Surface Between Pentests

Do Son April 13, 2026 0
Organizations often focus on known assets during security assessments, but many systems and applications exist outside official...
Read More Read more about How Shadow IT Expands Attack Surface Between Pentests
The End of Phone Activation: How to Activate Windows and Office Offline in 2026 Microsoft Developer Account Suspension Microsoft Web Activation Portal Driver Signing Account Suspension Windows 11 Smart App Control Windows 11 SE end of support, Microsoft education hardware pivot Microsoft Product Activation Portal 2025, Windows telephone activation discontinued Windows Update Naming, Microsoft Update Microsoft earnings, OpenAI valuation VBScript deprecation Microsoft Pakistan, Office Closure Microsoft job cuts Microsoft Own AI Models
  • Technology

The End of Phone Activation: How to Activate Windows and Office Offline in 2026

Do Son April 13, 2026 0

Microsoft has retired its legacy telephone activation system. Learn how to use the new Web Activation Portal to license Windows and Office without an internet connection.

The CPUID Watering Hole Attack Turning CPU-Z into a Trojan CVE-2023-22952 CPUID Watering Hole DLL Sideloading
  • Malware

The CPUID Watering Hole Attack Turning CPU-Z into a Trojan

Do Son April 13, 2026 0

April 2026 Alert: CPUID downloads for CPU-Z and HWMonitor were poisoned with STX RAT via DLL sideloading. Check your systems for CRYPTBASE.dll now!

OpenAI’s Silent Breach: Why You Must Update Your macOS ChatGPT App Before May 8 OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Malware

OpenAI’s Silent Breach: Why You Must Update Your macOS ChatGPT App Before May 8

Do Son April 13, 2026 0

OpenAI revokes legacy macOS certificates after a malicious @Axios library incursion. Update ChatGPT and Codex by May 8, 2026, to avoid software failure.

Vanished Without a Trace: Why Microsoft is Secretly Purging Open-Source Developer Accounts Microsoft Developer Account Suspension
  • Technology

Vanished Without a Trace: Why Microsoft is Secretly Purging Open-Source Developer Accounts

Do Son April 13, 2026 0

Microsoft is under fire for "expunging" developer accounts for projects like WireGuard and UTM. Learn how these silent bans are paralyzing open-source drivers.

STX RAT: The New Financial Predator Hiding in the “Start of Text” STX RAT Financial Malware
  • Malware

STX RAT: The New Financial Predator Hiding in the “Start of Text”

Do Son April 13, 2026 0

eSentire TRU uncovers STX RAT, a modular Trojan targeting finance with HVNC, AMSI Ghosting, and advanced encryption. Secure your perimeter—learn how it works.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-88800CVSS 9.1
    The MDJM Event Management and Mobile Events Manager WordPress plugins through 1.7.8.7 act on a role deletion request...
    📅 Updated: Nov 6, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 6, 2026
  • CVE-2026-120844CVSS 9.8
    Incorrect Privilege Assignment vulnerability in miniOrange OAuth Single Sign On – SSO (OAuth Client) miniorange-login-with-eve-online-google-facebook allows Privilege Escalation.This...
    📅 Updated: Nov 6, 2026
  • CVE-2026-118423CVSS 10.0
    The WP Libre Form WordPress plugin 1.5.0.1 does not validate the type of files uploaded through its form...
    📅 Updated: Nov 6, 2026
  • CVE-2026-83542CVSS 9.8
    Improper Control of Generation of Code ('Code Injection') in Apache OFBiz 24.09 before 24.09.08 on all platforms allows...
    📅 Updated: Nov 6, 2026
  • CVE-2026-82907CVSS 9.8
    Authentication Bypass by Capture-replay in ExternalLoginKeysManager in Apache OFBiz 24.09 before 24.09.08 on all platforms allows a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102894CVSS 9.1
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. From 0.7.1 until...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.