Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Laravel Passport Patches Machine-to-Human Authentication Bypass Laravel Passport Vulnerability Authentication Bypass
  • Vulnerability Report

Laravel Passport Patches Machine-to-Human Authentication Bypass

Do Son April 13, 2026 0

Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!

Under Fire Again: Rockstar Games Hit by ShinyHunters in Massive Snowflake Data Breach Rockstar Games Snowflake Breach
  • Data Leak

Under Fire Again: Rockstar Games Hit by ShinyHunters in Massive Snowflake Data Breach

Do Son April 13, 2026 0

Hackers target Rockstar Games via Snowflake. While Rockstar calls the data "non-substantial," could internal budgets and future launch dates be at risk?
The Copilot Retreat: Why Microsoft is Scrubbing Its AI Brand from Windows 11 Apps Windows 11 AI Rebranding
  • Windows

The Copilot Retreat: Why Microsoft is Scrubbing Its AI Brand from Windows 11 Apps

Do Son April 13, 2026 0

Microsoft is quietly rebranding Copilot features in Windows 11. Discover why Notepad’s AI is now called "Advanced Features" and what this means for the OS.
The Weakest Link: How “Transit Hubs” are Quietly Draining Crypto and Stealing AI Data API Transit Hub Vulnerabilities
  • Data Leak

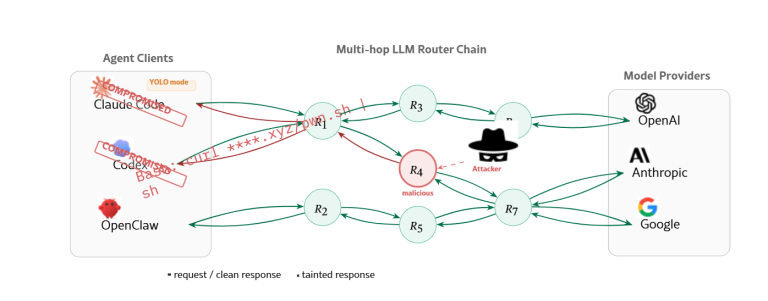
The Weakest Link: How “Transit Hubs” are Quietly Draining Crypto and Stealing AI Data

Do Son April 13, 2026 0

New research reveals massive security gaps in AI API aggregators. From stolen crypto to leaked tokens, learn why your API hub might be a Man-in-the-Middle trap.
Why Your Windows Lock Screen Clock is Wrong: Microsoft Explains the 30-Second Lag Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

Why Your Windows Lock Screen Clock is Wrong: Microsoft Explains the 30-Second Lag

Do Son April 13, 2026 0

Noticed the time lagging on your Ctrl+Alt+Delete screen? Microsoft reveals why the Secure Lock Screen runs 30 seconds behind and why they aren't fixing it.

Google’s $135 Million Payday: Are You Eligible for the Android Cellular Data Settlement? Google Android Data Settlement Linux terminal Android
  • Android
  • Data Leak

Google’s $135 Million Payday: Are You Eligible for the Android Cellular Data Settlement?

Do Son April 13, 2026 0

Google settles for $135M over claims it used Android cellular data without consent. Check your eligibility and learn how to claim your share of the payout.

Linux Kernel 7.0 Arrives: A Massive Overhaul for System Stability and Security Linus Torvalds AI bug reports Linux Kernel 7.0 Linux EFI Zboot - CVE-2022-42719 Linux KVM Intel AMX kernel panic, KVM guest host crash 2025
  • Linux

Linux Kernel 7.0 Arrives: A Massive Overhaul for System Stability and Security

Do Son April 13, 2026 0

Linux Kernel 7.0 is here! The 2026 milestone focuses on hardware support, memory safety, and security fixes for x86, ARM64, and RISC-V architectures.

The Encryption Ghost: How the FBI Recovers “Deleted” Signal Messages from iPhone Caches Signal cloud backup iOS Notification Database
  • Vulnerability Report

The Encryption Ghost: How the FBI Recovers “Deleted” Signal Messages from iPhone Caches

Do Son April 13, 2026 0

Signal's encryption is solid, but iOS is leaking your data. Learn how the FBI uses notification caches to recover deleted messages and how to stop it.

One-Touch Security: Google Expands End-to-End Encryption to Gmail on Android and iOS Gmail Mobile E2EE Gmail POP3 support end 2026, Gmailify deprecated January 2026 Gmail spam filter, political bias
  • Technology

One-Touch Security: Google Expands End-to-End Encryption to Gmail on Android and iOS

Do Son April 13, 2026 0

Gmail brings "One-Touch" end-to-end encryption to Android and iOS. Learn how Workspace Enterprise users can now secure sensitive emails natively on mobile.

Microsoft Fixes the Insider Mess: The End of “Clean Installs” and Staggered Features Windows Insider Program Structural Changes
  • Windows

Microsoft Fixes the Insider Mess: The End of “Clean Installs” and Staggered Features

Do Son April 13, 2026 0

Microsoft simplifies the Windows Insider Program! Discover the new Experimental Channel, native Feature Flags, and data-safe "in-place upgrades."

The Great Gallic Exodus: Inside France’s Bold Mission to Ditch Microsoft for Linux French Digital Sovereignty Greg Kroah-Hartman AI code review CVE-2025-38352 Linux kernel exploit, Android 32-bit UAF vulnerability CVE-2022-36946 Linux Kernel 6.16, Hardware Support
  • Linux

The Great Gallic Exodus: Inside France’s Bold Mission to Ditch Microsoft for Linux

Do Son April 13, 2026 0

France is severing ties with US tech giants. Discover the "La Suite" initiative and the mandate to move 80,000+ state employees from Windows to Linux by 2027.

The Script Editor Shift: How ClickFix Evades macOS 26.4 Security to Deliver Atomic Stealer ClickFix macOS Script Editor Attack
  • Malware

The Script Editor Shift: How ClickFix Evades macOS 26.4 Security to Deliver Atomic Stealer

Do Son April 13, 2026 0

Jamf identifies a macOS ClickFix pivot: attackers now use the Script Editor to bypass Terminal scans and deliver Atomic Stealer. Learn how to stay protected.

LucidRook: Sophisticated Spear-Phishing Campaign Targets Taiwan with Custom Malware Stack LucidRook Malware Taiwan Cyber Attack
  • Cybercriminals
  • Malware

LucidRook: Sophisticated Spear-Phishing Campaign Targets Taiwan with Custom Malware Stack

Do Son April 13, 2026 0

Cisco Talos reveals UAT-10362’s "Lucid" malware family targeting Taiwan. Using Lua, Rust, and regional locks, this threat prioritizes extreme stealth.

Supply Chain Alert: Critical 9.4 CVSS RCE Hits Sonatype Nexus Repository Manager Nexus Repository RCE Supply Chain Security Nexus Repository Manager - CVE-2024-5082 & CVE-2024-5083
  • Vulnerability

Supply Chain Alert: Critical 9.4 CVSS RCE Hits Sonatype Nexus Repository Manager

Do Son April 13, 2026 0

Sonatype patches a critical 9.4 CVSS RCE in Nexus Repository 3 (CVE-2026-3199). Secure your supply chain—upgrade to version 3.91.0 immediately!
Under 10 Hours: The marimo Terminal RCE Exploited in a Record-Breaking AI Sprint marimo Terminal RCE AI-Assisted Exploitation
  • Vulnerability Report

Under 10 Hours: The marimo Terminal RCE Exploited in a Record-Breaking AI Sprint

Do Son April 13, 2026 0

Unauthenticated RCE in marimo (CVE-2026-39987) exploited in the wild in record time. Attackers gained root access in under 10 hours. Patch to v0.23.0 now!

Total CMS Takeover: Movable Type Patches Critical 9.8 CVSS Perl RCE Movable Type Vulnerability Perl RCE
  • Vulnerability Report

Total CMS Takeover: Movable Type Patches Critical 9.8 CVSS Perl RCE

Do Son April 13, 2026 0

Movable Type patches a critical 9.8 CVSS RCE vulnerability in its Listing Framework. Secure your CMS against Perl code execution and SQLi—update today!
The CVE Watchtower: Weekly Threat Intelligence Briefing (April 6 – April 12, 2026) Vulnerability Digest Active Exploitation
  • Weekly Recap

The CVE Watchtower: Weekly Threat Intelligence Briefing (April 6 – April 12, 2026)

Do Son April 13, 2026 0

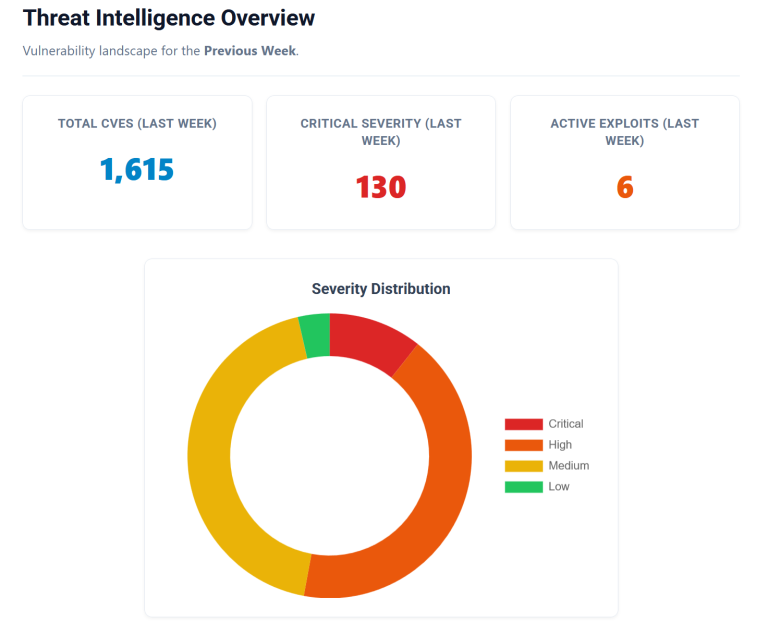
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.
The Stealthy Evolution of the DesckVB RAT Infection Chain DesckVB RAT Fileless Malware
  • Malware

The Stealthy Evolution of the DesckVB RAT Infection Chain

Do Son April 13, 2026 0

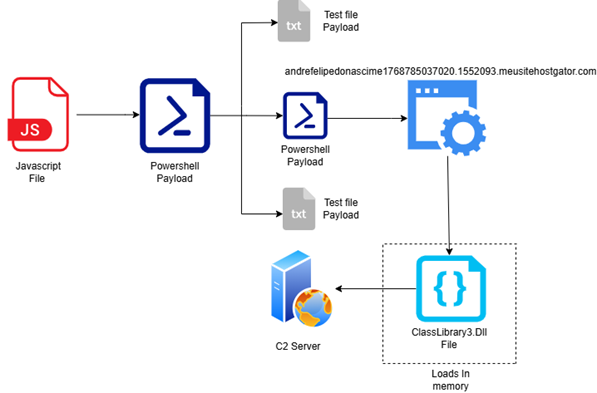
Lat61 Team uncovers DesckVB RAT, a stealthy 2026 Trojan using in-memory .NET loaders & JS obfuscation to hijack systems and evade AV. Learn how it works.

Encryption Bypasses and Kubernetes Token Leaks Hit Apache Tomcat CVE-2023-45648 Apache Tomcat Security Encryption Bypass
  • Vulnerability Report

Encryption Bypasses and Kubernetes Token Leaks Hit Apache Tomcat

Do Son April 13, 2026 0

Apache Tomcat discloses 10 vulnerabilities including encryption bypasses and Kubernetes token leaks. Upgrade now to secure your Java-based web applications.
The Invisible Hijack: How FrostArmada Turned 18,000 Routers Into a Global Spy Network FrostArmada Campaign DNS Redirection
  • Cybercriminals

The Invisible Hijack: How FrostArmada Turned 18,000 Routers Into a Global Spy Network

Do Son April 13, 2026 0

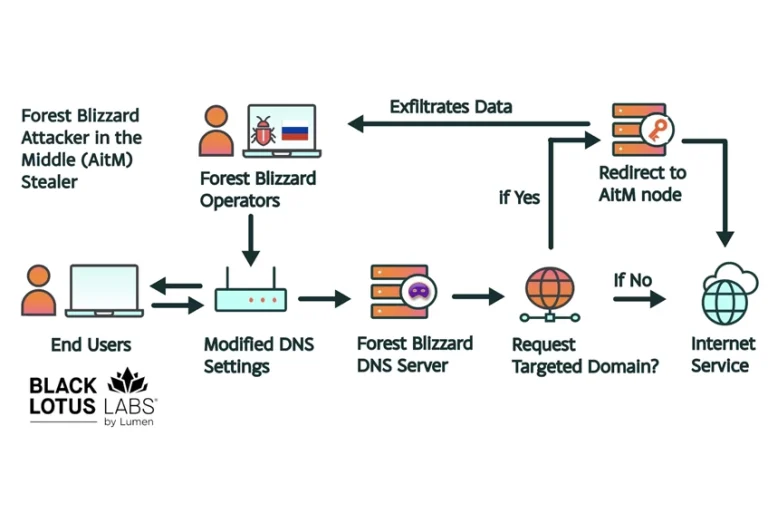
Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.

CVE-2026-40175 (CVSS 10): Critical Axios Vulnerability and Exploit Code Disclosed Publicly Axios proxy vulnerabilities prototype pollution gadget Axios Vulnerability Cloud Hijacking Axios npm supply chain attack Axios Vulnerability Node.js DoS CVE-2025-58754 CVE-2025-27152 Axios Vulnerability, Form-Data Flaw
  • Vulnerability Report

CVE-2026-40175 (CVSS 10): Critical Axios Vulnerability and Exploit Code Disclosed Publicly

Do Son April 12, 2026 0

A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!

Best 7 Credential Leak Monitoring Services Ragic Enterprise Cloud Database - CVE-2024-9983 - CVE-2024-9984 - CVE-2024-9985
  • Technique

Best 7 Credential Leak Monitoring Services

Do Son April 12, 2026 0
Credential leaks have shifted from isolated security events to a continuous operational risk that organizations must actively...
Read More Read more about Best 7 Credential Leak Monitoring Services
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-88800CVSS 9.1
    The MDJM Event Management and Mobile Events Manager WordPress plugins through 1.7.8.7 act on a role deletion request...
    📅 Updated: Nov 6, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 6, 2026
  • CVE-2026-120844CVSS 9.8
    Incorrect Privilege Assignment vulnerability in miniOrange OAuth Single Sign On – SSO (OAuth Client) miniorange-login-with-eve-online-google-facebook allows Privilege Escalation.This...
    📅 Updated: Nov 6, 2026
  • CVE-2026-118423CVSS 10.0
    The WP Libre Form WordPress plugin 1.5.0.1 does not validate the type of files uploaded through its form...
    📅 Updated: Nov 6, 2026
  • CVE-2026-83542CVSS 9.8
    Improper Control of Generation of Code ('Code Injection') in Apache OFBiz 24.09 before 24.09.08 on all platforms allows...
    📅 Updated: Nov 6, 2026
  • CVE-2026-82907CVSS 9.8
    Authentication Bypass by Capture-replay in ExternalLoginKeysManager in Apache OFBiz 24.09 before 24.09.08 on all platforms allows a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102894CVSS 9.1
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. From 0.7.1 until...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.