
 Do Son
Critical 9.3 CVSS flaw (CVE-2026-34078) in Flatpak allows apps to escape sandboxes and access all host files. Secure your Linux system—update to v1.16.4 now!
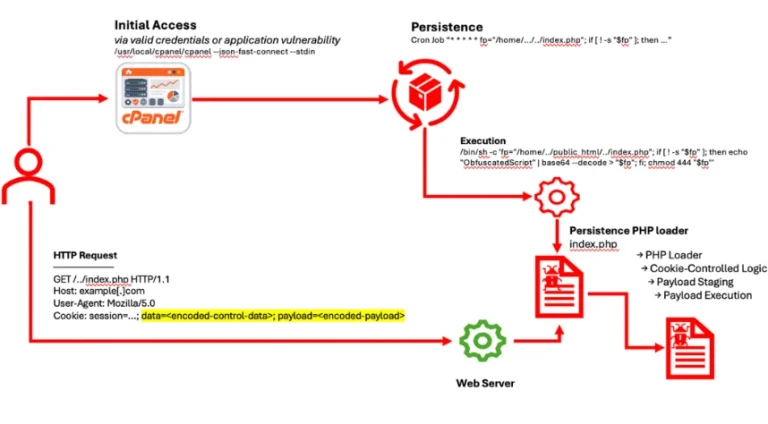
Microsoft Defender unmasks a stealthy PHP web shell hiding C2 logic in HTTP cookies. Learn how "cookie-gating" bypasses logs to maintain persistent RCE.

A developer's "human error" leaked sensitive GitHub tokens in an Apache HTTP Server update. Learn how GitHub's safety nets prevented a major security breach.

Microsoft’s Windows 11 Health Dashboard is officially clear of bugs—for now. Discover the latest fixes and why a mandatory 25H2 update is coming this October.
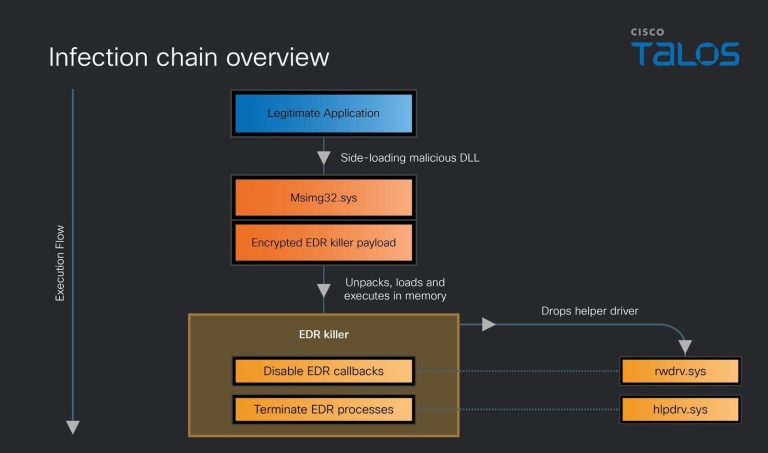
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.

Mandiant uncovers BRICKSTORM, a threat actor hiding in VMware vSphere for 393 days. Learn how to close the visibility gap and harden your ESXi infrastructure.

Microsoft’s sudden suspension of VeraCrypt and WireGuard accounts reveals the dangers of automated bureaucracy in the critical path of security software.

OpenStack Keystone CVE-2026-33551 allows low-privilege users to bypass role restrictions and seize full S3 bucket control. Patch your cloud environment now!

Palo Alto Networks patches critical flaws in Cortex XDR and ADEM, including a SYSTEM-level privilege escalation. Secure your security tools—patch today!

Microsoft has suspended VeraCrypt’s developer account, blocking critical driver signatures. Without a fix, future Windows updates and system boots are at risk.

GitLab releases critical patches (18.10.3+) for WebSocket flaws, Terraform DoS, and unauthorized privilege demotions. Update your self-managed instances!

SonicWall patches critical SMA 1000 flaws, including a 7.2 SQL injection for privilege escalation and Unicode-based MFA bypasses. Secure your VPN—update now!
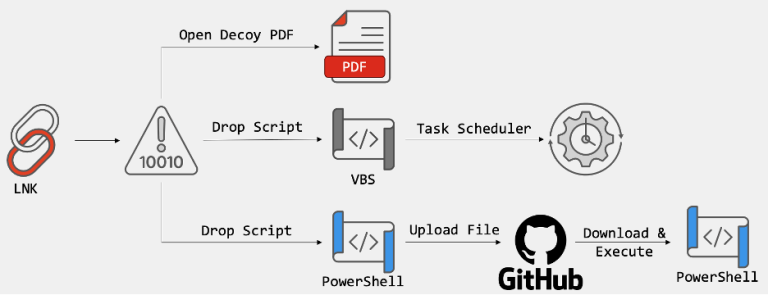
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.
Google Chrome 147 is out with critical security fixes for WebML and V8. Protect your browser from overflows and memory leaks—update to version 147 now!

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!
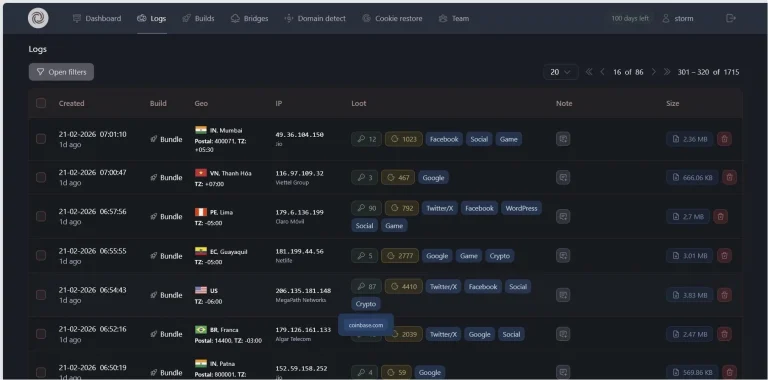
Storm malware bypasses Chrome security by shipping encrypted files for server-side decryption. Learn how it steals session cookies to defeat MFA in 2026.
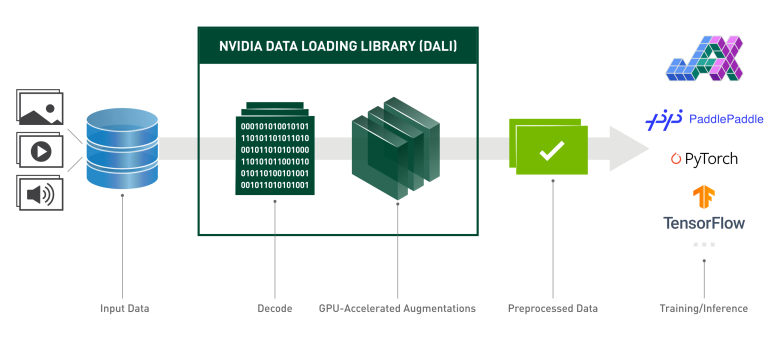
NVIDIA patches high-severity flaws in DALI and Triton Inference Server. Prevent arbitrary code execution and DoS—upgrade to DALI v2.0 and Triton r26.02 now.

AWS patches a high-severity (8.7) Firecracker flaw allowing root guests to trigger memory corruption via the virtio-pci transport. Update your microVMs now.
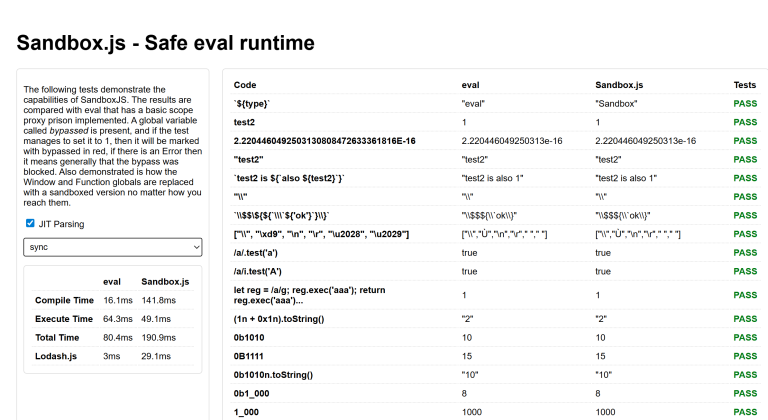
CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!


Weaver E-cology 10.0 faces a critical 9.3 CVSS RCE (CVE-2026-22679). Unauthenticated attackers can hijack servers via a debug endpoint. Patch immediately!

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!