Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Encryption Bypasses and Kubernetes Token Leaks Hit Apache Tomcat CVE-2023-45648 Apache Tomcat Security Encryption Bypass
  • Vulnerability Report

Encryption Bypasses and Kubernetes Token Leaks Hit Apache Tomcat

Do Son April 13, 2026 0

Apache Tomcat discloses 10 vulnerabilities including encryption bypasses and Kubernetes token leaks. Upgrade now to secure your Java-based web applications.
The Invisible Hijack: How FrostArmada Turned 18,000 Routers Into a Global Spy Network FrostArmada Campaign DNS Redirection
  • Cybercriminals

The Invisible Hijack: How FrostArmada Turned 18,000 Routers Into a Global Spy Network

Do Son April 13, 2026 0

Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.

CVE-2026-40175 (CVSS 10): Critical Axios Vulnerability and Exploit Code Disclosed Publicly Axios proxy vulnerabilities prototype pollution gadget Axios Vulnerability Cloud Hijacking Axios npm supply chain attack Axios Vulnerability Node.js DoS CVE-2025-58754 CVE-2025-27152 Axios Vulnerability, Form-Data Flaw
  • Vulnerability Report

CVE-2026-40175 (CVSS 10): Critical Axios Vulnerability and Exploit Code Disclosed Publicly

Do Son April 12, 2026 0

A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!

Best 7 Credential Leak Monitoring Services Ragic Enterprise Cloud Database - CVE-2024-9983 - CVE-2024-9984 - CVE-2024-9985
  • Technique

Best 7 Credential Leak Monitoring Services

Do Son April 12, 2026 0
Credential leaks have shifted from isolated security events to a continuous operational risk that organizations must actively...
Read More Read more about Best 7 Credential Leak Monitoring Services
Root Access at Risk: Critical Nix Sandbox Escape Overwrites Sensitive System Files Nix Sandbox Escape Root Escalation CVE-2024-45593
  • Vulnerability Report

Root Access at Risk: Critical Nix Sandbox Escape Overwrites Sensitive System Files

Do Son April 10, 2026 0

Nix patches a critical 9.0 CVSS sandbox escape. Learn how CVE-2026-39860 allows unprivileged users to seize root control via symlink manipulation. Update now!

Critical Privilege Escalation in Checkmk: Root Access at Risk Checkmk Privilege Escalation
  • Vulnerability Report

Critical Privilege Escalation in Checkmk: Root Access at Risk

Do Son April 10, 2026 0

Checkmk patches a critical 9.3 CVSS local privilege escalation flaw in the 'omd' command. Stop site users from seizing root access—update your sites today!

The “Seal of Approval” Trap: How Hackers are Hijacking GitHub and Jira Notifications phishing-3390518_1280
  • Cybercriminals

The “Seal of Approval” Trap: How Hackers are Hijacking GitHub and Jira Notifications

Do Son April 10, 2026 0

Cisco Talos exposes "Platform-as-a-Proxy" (PaaP). Hackers are abusing GitHub and Jira's trusted mail servers to bypass SPF/DKIM and deliver phishing lures.
New AI-Driven Phishing Campaign Subverts Microsoft’s Device Code Flow EvilToken Device Code Phishing
  • Cybercriminals

New AI-Driven Phishing Campaign Subverts Microsoft’s Device Code Flow

Do Son April 10, 2026 0

Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!
New ClickFix Campaign Unveiled: Modular NodeJS Malware Targets Windows Users Node.js Infostealer ClickFix Campaign
  • Malware

New ClickFix Campaign Unveiled: Modular NodeJS Malware Targets Windows Users

Do Son April 10, 2026 0

Netskope uncovers a Node.js-based ClickFix campaign using gRPC over Tor for stealthy crypto theft. A leaked file exposed their entire MaaS backend.

North Korea’s “Portfolio Model” Shatters Modern Attribution Attribution Resistance DPRK Cyber Portfolio
  • Cyber Security

North Korea’s “Portfolio Model” Shatters Modern Attribution

Do Son April 10, 2026 0

DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.

HPE Aruba Patches High-Severity Credential Theft Flaw CVE-2024-26305 _ CVE-2025-23058 Aruba 5G Core Open Redirect
  • Vulnerability Report

HPE Aruba Patches High-Severity Credential Theft Flaw

Do Son April 10, 2026 0

HPE Aruba Networking patches a critical 8.8 CVSS open redirect in its Private 5G Core. Prevent credential harvesting—update to version 1.25.3.1 immediately.
North Korean Hackers Pivot to AI: New npm Malware Targets Cursor, Claude, and Gemini Tokens AI Tool Targeting Contagious Interview
  • Malware

North Korean Hackers Pivot to AI: New npm Malware Targets Cursor, Claude, and Gemini Tokens

Do Son April 10, 2026 0

North Korean hackers are now targeting AI tools like Cursor and Claude. The OtterCookie malware steals API keys and conversation logs. Is your dev environment safe?

TP-Link Archer AX53 Hit by Multiple High-Severity Vulnerabilities Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

TP-Link Archer AX53 Hit by Multiple High-Severity Vulnerabilities

Do Son April 10, 2026 0

TP-Link urges Archer AX53 v1.0 users to update firmware to fix 5 critical flaws, including OS command injection & file leaks. Secure your network now!
LinkedIn Job Seekers Targeted by Sophisticated “PXA Stealer” Campaign PXA Stealer LinkedIn Job Phishing
  • Cybercriminals

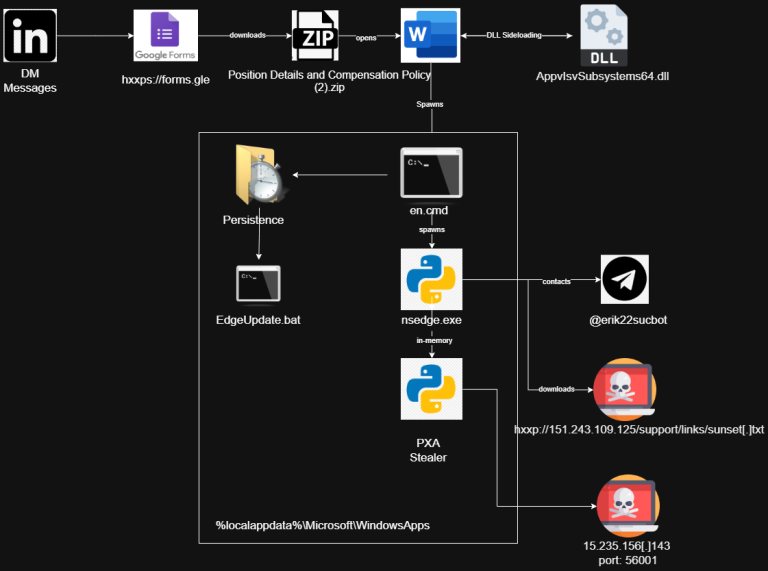
LinkedIn Job Seekers Targeted by Sophisticated “PXA Stealer” Campaign

Do Son April 10, 2026 0

LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.
Cloud Engineering at Risk: AWS Patches Critical Privilege Escalation and RCE Flaws in RES AWS RES Security Cloud Privilege Escalation
  • Vulnerability Report

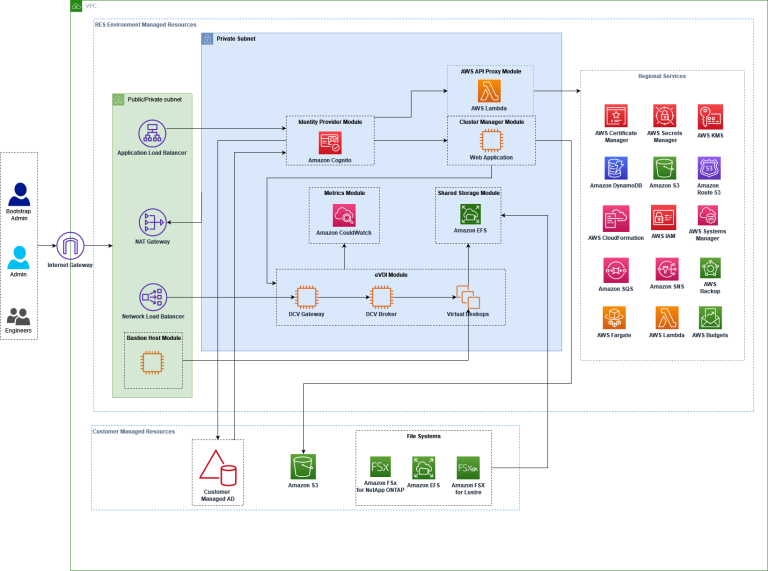
Cloud Engineering at Risk: AWS Patches Critical Privilege Escalation and RCE Flaws in RES

Do Son April 9, 2026 0

AWS patches critical RES flaws (CVE-2026-5707/8/9) allowing root access and instance profile hijacking. Protect your cloud lab—update to v2026.03 now.
Critical 9.8 CVSS Flaws in goshs Exposed goshs Exploit Path Traversal
  • Vulnerability Report

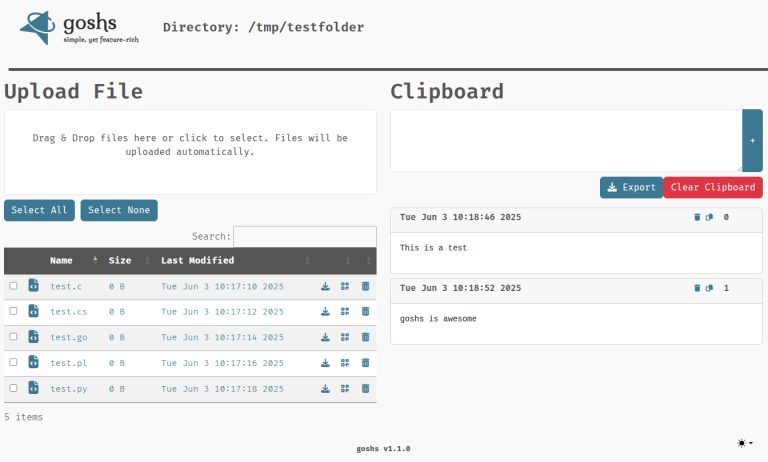
Critical 9.8 CVSS Flaws in goshs Exposed

Do Son April 9, 2026 0

Critical 9.8 flaws in goshs v2.0.0-beta.2 allow unauthenticated attackers to write or delete any file on your system. Update to v2.0.0-beta.3 immediately!

The “Open Door” Vulnerability: Unchanged Default Passwords Put Juniper vLWC at Risk Juniper vLWC Vulnerability Default Password Exploit HPE, Juniper Networks CVE-2024-21611 & CVE-2024-21591 - CVE-2025-21589
  • Vulnerability Report

The “Open Door” Vulnerability: Unchanged Default Passwords Put Juniper vLWC at Risk

Do Son April 9, 2026 0

Juniper warns of a critical 9.8 CVSS flaw in JSI vLWC. A default password allows unauthenticated attackers to take full device control. Update to 3.0.94 now!
100,000+ Sites Exposed: Critical 9.8 CVSS Flaw Hits Everest Forms WordPress Plugin Everest Forms Vulnerability PHP Object Injection
  • Vulnerability Report

100,000+ Sites Exposed: Critical 9.8 CVSS Flaw Hits Everest Forms WordPress Plugin

Do Son April 9, 2026 0

Everest Forms patches a critical 9.8 CVSS PHP Object Injection vulnerability affecting 100,000+ sites. Update to v3.4.4 now to prevent full site takeover!

Mallory Launches AI-Native Threat Intelligence Platform, Turning Global Threat Data Into Prioritized Action ai-native-threat-intelligence-platform_1775675721DIuoj4t7BR
  • Press Release

Mallory Launches AI-Native Threat Intelligence Platform, Turning Global Threat Data Into Prioritized Action

cybernewswire April 9, 2026 0
Austin, Texas, United States, 9th April 2026, CyberNewswire
Read More Read more about Mallory Launches AI-Native Threat Intelligence Platform, Turning Global Threat Data Into Prioritized Action
Frontend Secrets Exposed: Vite Patches Critical Security Bypass in Dev Server Vite Vulnerability Arbitrary File Read
  • Vulnerability Report

Frontend Secrets Exposed: Vite Patches Critical Security Bypass in Dev Server

Do Son April 9, 2026 0

Vite patches critical flaws (CVE-2026-39364 & CVE-2026-39363) allowing arbitrary file reads and .env leaks via WebSockets and query params. Upgrade to 8.0.5!

Mitel Patches Critical SQL Injection and Privilege Escalation in MiCollab Mitel MiCollab SQL Injection MiCollab software - CVE-2024-47223 & CVE-2024-41713
  • Vulnerability

Mitel Patches Critical SQL Injection and Privilege Escalation in MiCollab

Do Son April 9, 2026 0

Mitel patches a critical 9.8 CVSS SQL injection in MiCollab. Learn how this unauthenticated flaw chains to full system takeover. Upgrade to v10.2 SP1 now!

Denial of Service Alert: React Server Components Vulnerability Causes CPU Spikes React Server Components Vulnerability CVE-2026-23870 React Server Components Server-Side DoS React DoS Vulnerability CVE-2026-23864 React Server Components DoS, Source Code Disclosure React RCE, Server Components Deserialization CVE-2025-55182
  • Vulnerability Report

Denial of Service Alert: React Server Components Vulnerability Causes CPU Spikes

Do Son April 9, 2026 0

React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-121952CVSS 9.3
    FreeRDP before 3.32.2 has an out-of-bounds write in the proxy because rdp_read_bitmap_cache_v2_capability_set rejects only numCellCaches values above 5,...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121953CVSS 9.3
    FreeRDP before 3.32.2 has a use-after-free in the client's rdpgfx dynamic virtual channel: a duplicate-name channel with a...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86574CVSS 9.8
    Heap-based Buffer Overflow Vulnerability in JP1/Base. This issue affects JP1/Base: from 11-00 before 12-50-54.
    📅 Updated: Nov 4, 2026
  • CVE-2026-86575CVSS 9.4
    Stack-based Buffer Overflow Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86576CVSS 9.4
    Heap-based Buffer Overflow Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86577CVSS 9.4
    Out-of-bounds Write Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before 13-50-31;...
    📅 Updated: Nov 4, 2026
  • CVE-2026-84539CVSS 9.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in macOS Golden Gate...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.