Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Railway Security Incident Exposes Customer Environment Variables and Pauses All Deployments Railway security incident - attackers may have accessed decrypted Railway environment variables and API keys
  • Data Leak

Railway Security Incident Exposes Customer Environment Variables and Pauses All Deployments

Do Son October 22, 2026 0

Railway security incident: attackers may have decrypted Railway environment variables. Builds are paused. Rotate API keys and credentials now.
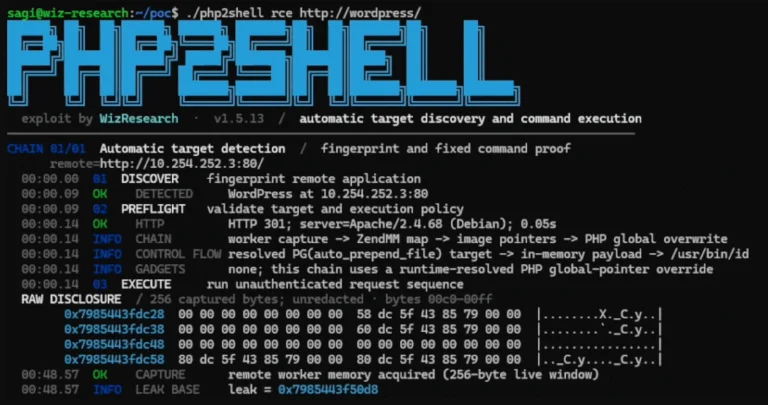
PHP2Shell Exploited in the Wild as PoC Exploits and Full Details Go Public PHP2Shell remote code execution flaws exploited in the wild after PoC release
  • Vulnerability Report

PHP2Shell Exploited in the Wild as PoC Exploits and Full Details Go Public

Do Son October 22, 2026 0

PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
Splunk Fixes 31 Vulnerabilities in Enterprise and SOAR, Three Rated CVSS 9.9 Splunk vulnerabilities in Splunk Enterprise and Splunk SOAR fixed in October 2026 security update
  • Vulnerability Report

Splunk Fixes 31 Vulnerabilities in Enterprise and SOAR, Three Rated CVSS 9.9

Do Son October 22, 2026 0

Splunk fixes 31 Splunk vulnerabilities in Enterprise and Splunk SOAR, including CVSS 9.9 flaws CVE-2026-76531, CVE-2026-76299 and CVE-2026-76302.
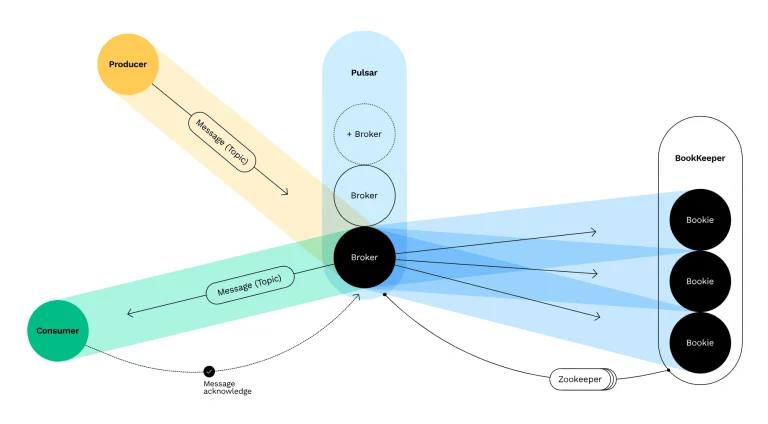
Apache Patches 17 Critical and High Flaws in Pulsar and IoTDB Apache Pulsar vulnerabilities and Apache IoTDB security update diagram for CVE-2026-105944, CVE-2026-105869, and CVE-2026-59229
  • Vulnerability Report

Apache Patches 17 Critical and High Flaws in Pulsar and IoTDB

Do Son October 22, 2026 0

Patch 13 Apache Pulsar vulnerabilities and 4 Apache IoTDB flaws now, including critical bugs CVE-2026-105944, CVE-2026-105869, and CVE-2026-59229.
Cisco Patches Critical Expressway Series Vulnerabilities Including Root RCE Flaw Cisco Expressway vulnerabilities overview showing Cisco security advisory fixes for CVE-2026-76466, CVE-2026-76490, and CVE-2026-76435
  • Vulnerability Report

Cisco Patches Critical Expressway Series Vulnerabilities Including Root RCE Flaw

Do Son October 22, 2026 0

Review the latest Cisco security advisory to patch 10 Cisco Expressway vulnerabilities, including critical 9.8 CVSS root RCE flaw CVE-2026-76466.
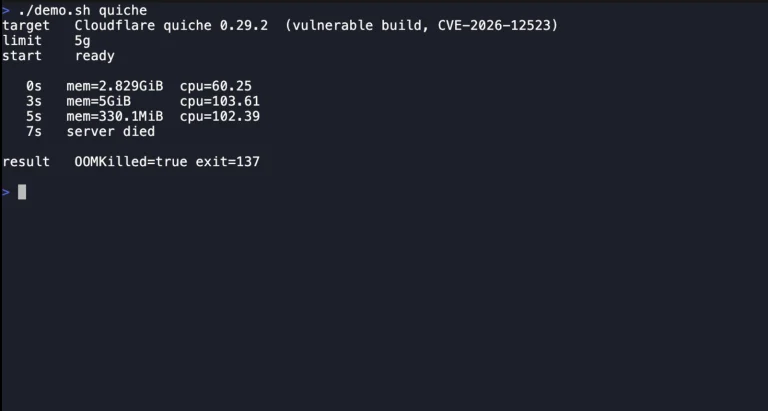
PoC and Full Details Released for QPACK Amplification Attack That Crashes HTTP/3 Servers QPACK amplification attack on HTTP/3 servers with public PoC exploit code
  • Vulnerability Report

PoC and Full Details Released for QPACK Amplification Attack That Crashes HTTP/3 Servers

Do Son October 22, 2026 0

FoxIO released details and PoC code for a QPACK amplification attack that can crash HTTP/3 servers, including quic-go, quiche, lsquic and Bun.
Apache Traffic Server Fixes 15 Flaws, Including CVSS 10.0 Plugin Bug and Cache Poisoning Apache Traffic Server vulnerabilities enable cache poisoning and request smuggling
  • Vulnerability Report

Apache Traffic Server Fixes 15 Flaws, Including CVSS 10.0 Plugin Bug and Cache Poisoning

Do Son October 22, 2026 0

15 Apache Traffic Server vulnerabilities, including CVSS 10.0 CVE-2026-111813, allow cache poisoning and smuggling. Upgrade to 10.2.1.

Top 4 Threat Intelligence Platforms in Middle East CVE weekly roundup dashboard showing 2077 new vulnerabilities and CISA KEV additions
  • Technique

Top 4 Threat Intelligence Platforms in Middle East

Do Son October 22, 2026 0
Based on our research, the top threat intelligence platforms in the Middle East in 2026 are CloudSEK,...
Read More Read more about Top 4 Threat Intelligence Platforms in Middle East
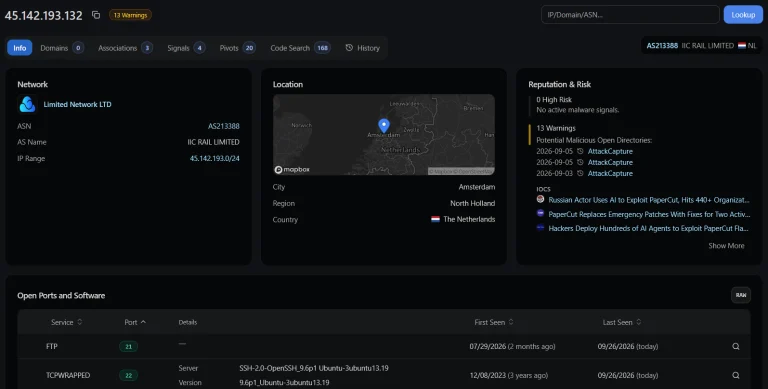
Exposed Attacker Server Reveals AI Agent Toolkit and a Second PaperCut RCE Path PaperCut RCE campaign server exposing an AI-assisted exploitation toolkit and reverse SOCKS5 pivots
  • Malware

Exposed Attacker Server Reveals AI Agent Toolkit and a Second PaperCut RCE Path

Do Son October 22, 2026 0

An exposed server reveals AI-assisted exploitation behind a PaperCut RCE campaign, a second XML-RPC attack path, and 45 live network pivots.
Cisco Fixes Critical Unified CM Flaws Found With Help From AI in Voice Hardening Release Cisco Unified CM vulnerabilities fixed in October 2026 security hardening release
  • Vulnerability Report

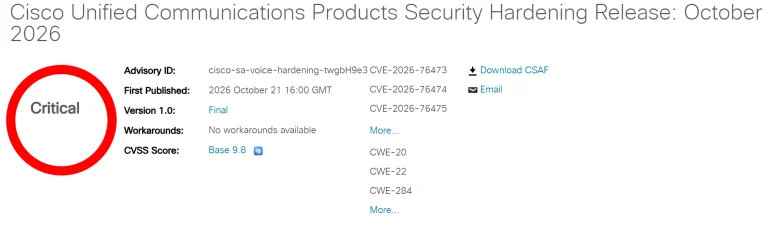
Cisco Fixes Critical Unified CM Flaws Found With Help From AI in Voice Hardening Release

Do Son October 22, 2026 0

Cisco's security hardening release fixes Cisco Unified CM vulnerabilities, including CVSS 9.8 flaws CVE-2026-76473 and CVE-2026-76474.
Oracle Patches 98 MySQL Vulnerabilities in October 2026 Update Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.
  • Vulnerability Report

Oracle Patches 98 MySQL Vulnerabilities in October 2026 Update

Do Son October 22, 2026 0

Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.

Apache bRPC 1.18.0 Patches 35 High and Moderate Vulnerabilities Apache bRPC vulnerabilities overview showing Apache bRPC 1.18.0 fixes for CVE-2026-48830, CVE-2026-54425, and CVE-2026-56388
  • Vulnerability Report

Apache bRPC 1.18.0 Patches 35 High and Moderate Vulnerabilities

Do Son October 22, 2026 0

Upgrade to Apache bRPC 1.18.0 to patch 35 Apache bRPC vulnerabilities, including high-severity flaws CVE-2026-48830 and CVE-2026-56388.
Duplicator WordPress Plugin Patched for High-Severity PHP Object Injection Vulnerability Duplicator WordPress plugin PHP Object Injection diagram showing CVE-2026-82814 impact
  • Vulnerability Report

Duplicator WordPress Plugin Patched for High-Severity PHP Object Injection Vulnerability

Do Son October 22, 2026 0

Update the Duplicator WordPress plugin to 5.0.0 to fix CVE-2026-82814, a high-severity PHP Object Injection flaw risking RCE and site takeover.
GitLab Critical Patch Release Fixes 10.0 CVSS Remote Code Execution Flaw and 11 Other Bugs GitLab critical patch release overview showing GitLab vulnerabilities CVE-2026-110264, CVE-2026-15723, and CVE-2026-112212
  • Vulnerability Report

GitLab Critical Patch Release Fixes 10.0 CVSS Remote Code Execution Flaw and 11 Other Bugs

Do Son October 21, 2026 0

Apply the GitLab critical patch release to fix 12 GitLab vulnerabilities, including 10.0 CVSS RCE flaw CVE-2026-110264 and CVE-2026-15723.
Arrakis Security Report Finds 76% of AI Agents Are Dormant but Keep Their Credentials and Connections Arrakis_cover_flat_1200x720_1792596211ebZpCyz315
  • Press Release

Arrakis Security Report Finds 76% of AI Agents Are Dormant but Keep Their Credentials and Connections

cybernewswire October 21, 2026 0
New York, NY, USA, 21st October 2026, CyberNewswire
Read More Read more about Arrakis Security Report Finds 76% of AI Agents Are Dormant but Keep Their Credentials and Connections
ISC Patches Four High-Severity BIND 9 Flaws, Including GSS-TSIG Memory Corruption BIND 9 vulnerabilities fixed by ISC including GSS-TSIG memory corruption and denial of service flaws
  • Vulnerability Report

ISC Patches Four High-Severity BIND 9 Flaws, Including GSS-TSIG Memory Corruption

Do Son October 21, 2026 0

ISC fixes four BIND 9 vulnerabilities, including CVE-2026-94300 memory corruption and denial of service bugs. Upgrade to BIND 9.20.30 or 9.21.27.
Node.js Fixes 10 Flaws, Including Brotli RCE and TLS Hostname Bypasses Node.js security release fixes Brotli remote code execution and TLS hostname bypass flaws
  • Vulnerability Report

Node.js Fixes 10 Flaws, Including Brotli RCE and TLS Hostname Bypasses

Do Son October 21, 2026 0

The Node.js security release fixes 10 flaws, including a Brotli remote code execution bug, CVE-2026-111497. Update to 26.12.1, 24.22.1 or 22.23.4.
LiteLLM 1.107.0 Compromised to Steal Cloud, AI Tool and Developer Credentials LiteLLM supply chain attack delivering a PyPI credential stealer through Python startup hooks
  • Malware

LiteLLM 1.107.0 Compromised to Steal Cloud, AI Tool and Developer Credentials

Do Son October 21, 2026 0

A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
PHP Releases Fixes and Full Details for Two Critical Unauthenticated RCE Flaws PHP RCE vulnerabilities CVE-2026-109618 and CVE-2026-109619 allow unauthenticated remote code execution
  • Vulnerability Report

PHP Releases Fixes and Full Details for Two Critical Unauthenticated RCE Flaws

Do Son October 21, 2026 0

PHP fixes two critical PHP RCE vulnerabilities, CVE-2026-109618 and CVE-2026-109619, allowing remote code execution. Update to 8.5.12 or 8.4.27.
Atlassian Patches 176 Flaws in Jira, Confluence and Other Data Center Products Atlassian security bulletin October 2026 fixes third-party vulnerabilities in Jira and Confluence
  • Vulnerability Report

Atlassian Patches 176 Flaws in Jira, Confluence and Other Data Center Products

Do Son October 21, 2026 0

Atlassian's October 2026 security bulletin fixes 176 third-party vulnerabilities, 14 critical, in Jira, Confluence, Crowd and Bitbucket.
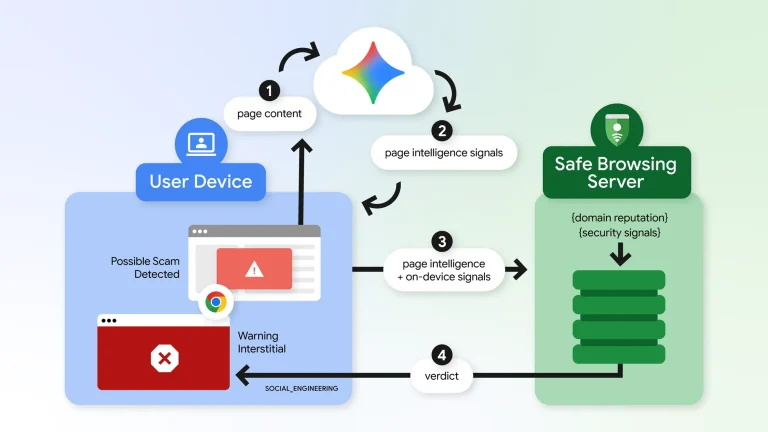
Chrome ClickFix Protection Scans Risky Clipboard Commands Chrome ClickFix protection warning about a risky clipboard command, with Gemini scam detection flagging a fake verification page
  • Technology

Chrome ClickFix Protection Scans Risky Clipboard Commands

Do Son October 21, 2026 0

Chrome ClickFix protection in Enhanced Protection flags risky clipboard commands and uses cloud Gemini AI to block scam sites.
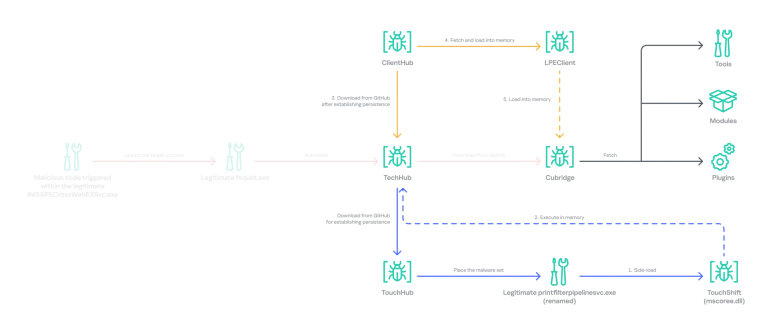
Lazarus Operation FlashHole Abuses CrossWeb EX and GitHub to Spy on South Korean Firms Operation FlashHole attack chain used by the Lazarus Group against South Korean firms via CrossWeb EX
  • Cybercriminals

Lazarus Operation FlashHole Abuses CrossWeb EX and GitHub to Spy on South Korean Firms

Do Son October 21, 2026 0

In Operation FlashHole, the Lazarus Group used AI-made lure sites, CrossWeb EX, and GitHub C2 to spy on South Korean firms. Here is how.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.