Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Skynet LLMjacking Agent Hijacks Exposed AI Models to Hack Servers and Mine Crypto Skynet LLMjacking agent hijacking exposed AI models to scan, exploit servers and mine cryptocurrency
  • Malware

Skynet LLMjacking Agent Hijacks Exposed AI Models to Hack Servers and Mine Crypto

Do Son October 24, 2026 0

A Skynet LLMjacking agent hijacks exposed AI models to scan, hack servers and mine crypto for 100,000 steps, while victims pay the bill.

10 Best EVM-Compatible Blockchain Networks in 2026 CVE-2024-45337
  • Technique

10 Best EVM-Compatible Blockchain Networks in 2026

Do Son October 23, 2026 0
The best EVM-compatible blockchain network in 2026 is Autheo for developers seeking familiar Ethereum tooling within a...
Read More Read more about 10 Best EVM-Compatible Blockchain Networks in 2026
Palo Alto Networks Confirms PHP2Shell Flaws Affect PAN-OS and Panorama PAN-OS PHP2Shell vulnerabilities affect Palo Alto Networks firewall management interface
  • Vulnerability Report

Palo Alto Networks Confirms PHP2Shell Flaws Affect PAN-OS and Panorama

Do Son October 23, 2026 0

Palo Alto confirms PAN-OS PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 affect the firewall management interface. Restrict access and patch.
PHP Warns of New Session Upload Progress Flaw CVE-2026-115560, Urges Mitigation PHP session vulnerability CVE-2026-115560 in session upload progress after PHP2Shell
  • Vulnerability Report

PHP Warns of New Session Upload Progress Flaw CVE-2026-115560, Urges Mitigation

Do Son October 23, 2026 0

PHP warns of CVE-2026-115560, a PHP session vulnerability that follows PHP2Shell. Disable session.upload_progress until the next bugfix release.
NS2JB Brings a Switch 2 Jailbreak With Codex Help Switch 2 jailbreak NS2JB running homebrew on Nintendo Switch 2 firmware 23.0.1, developed with help from Codex AI
  • Technology

NS2JB Brings a Switch 2 Jailbreak With Codex Help

Do Son October 23, 2026 0

The Switch 2 jailbreak NS2JB runs native code on firmware 23.0.1 through SmileBASIC 4, built with Codex. It is not permanent.
Qualcomm Global Layoffs Planned Amid Smartphone Slump Qualcomm global layoffs announcement and corporate headquarters in San Diego
  • Technology

Qualcomm Global Layoffs Planned Amid Smartphone Slump

Do Son October 23, 2026 0

Qualcomm global layoffs will begin in November 2026 as smartphone shipments plunge 20 percent and memory costs strain device manufacturers worldwide.
Python Ships Emergency Releases After emSign CA Certificate Incident emSign CA certificate removal prompts Python security release for pip and certifi
  • Technology

Python Ships Emergency Releases After emSign CA Certificate Incident

Do Son October 23, 2026 0

The emSign CA certificate was pulled from certifi. A new Python security release updates pip to block MITM risks. Upgrade pip and uv now.
LiteSpeed Cache Flaws Expose 7 Million WordPress Sites to Stored XSS LiteSpeed Cache vulnerabilities enable stored XSS on 7 million WordPress sites
  • Vulnerability Report

LiteSpeed Cache Flaws Expose 7 Million WordPress Sites to Stored XSS

Do Son October 23, 2026 0

Three LiteSpeed Cache vulnerabilities, including stored XSS flaws CVE-2026-113499 and CVE-2026-113500, affect 7M+ WordPress sites. Update to 7.9.2.
OpenBSD 8.0 Release Introduces Kernel Hardening and Day-One Errata OpenBSD 8.0 release architecture showing kernel hardening and day-one security errata
  • Linux

OpenBSD 8.0 Release Introduces Kernel Hardening and Day-One Errata

Do Son October 23, 2026 0

The OpenBSD 8.0 release brings OpenSSH 10.6, kernel mitigations, and immediate day-one errata patches addressing critical IPsec memory corruption.
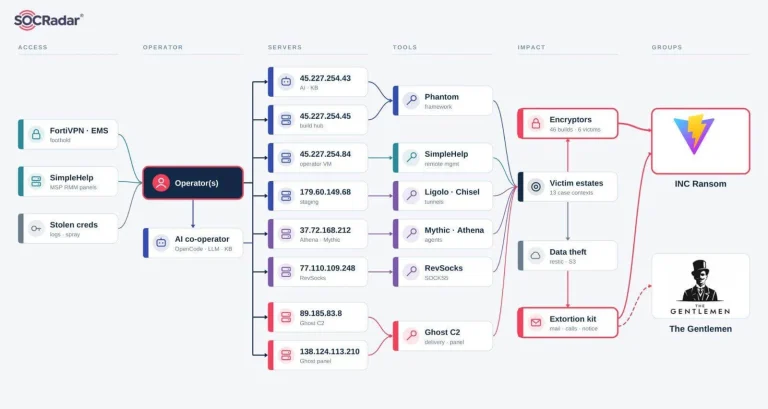
INC Ransomware Affiliates Expose Seven Servers Holding Phantom AI Framework and 46 Encryptors INC Ransomware affiliates and INC Ransomware affiliates AI server infrastructure diagram
  • Malware

INC Ransomware Affiliates Expose Seven Servers Holding Phantom AI Framework and 46 Encryptors

Do Son October 23, 2026 0

SOCRadar reveals 7 servers run by INC Ransomware affiliates, exposing an INC Ransomware affiliates AI workbench, Phantom, and 46 encryptors.
Australian Court Forces Apple to Open the App Store Australian App Store ruling forcing Apple to allow sideloading and outside payments, with Fortnite returning to the Australian App Store
  • Technology

Australian Court Forces Apple to Open the App Store

Do Son October 23, 2026 0

The Australian App Store ruling orders Apple to allow sideloading and outside payments by March 1, 2027. Apple will appeal.
CAPCOM ID Data Breach Exposes 11.77 Million Records CAPCOM ID data breach notice showing 11.77 million exposed user records, a Capcom account breach affecting emails and login activity
  • Data Leak

CAPCOM ID Data Breach Exposes 11.77 Million Records

Do Son October 23, 2026 0

A CAPCOM ID data breach exposed 11.77 million records, including emails and login activity. No payment data was leaked.
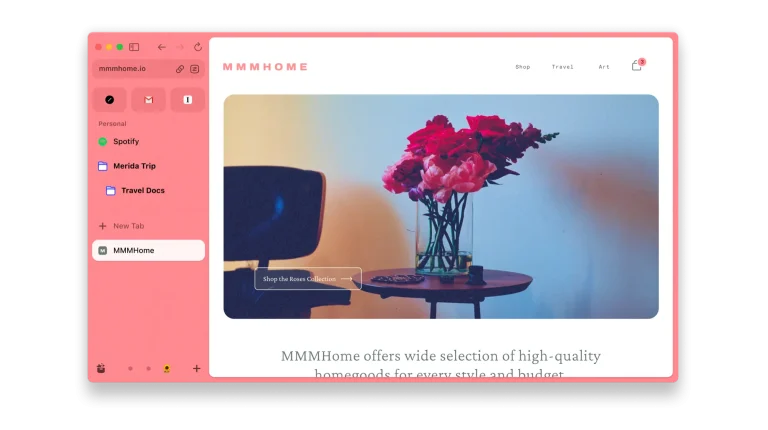
Arc Browser Shutdown Set for December 22, 2026 Arc browser shutdown notice from The Browser Company, urging users to export data and complete a Dia browser migration before December 22
  • Technology

Arc Browser Shutdown Set for December 22, 2026

Do Son October 23, 2026 0

The Arc browser shutdown arrives December 22, 2026. Export your data now and move to Dia before accounts are deleted.
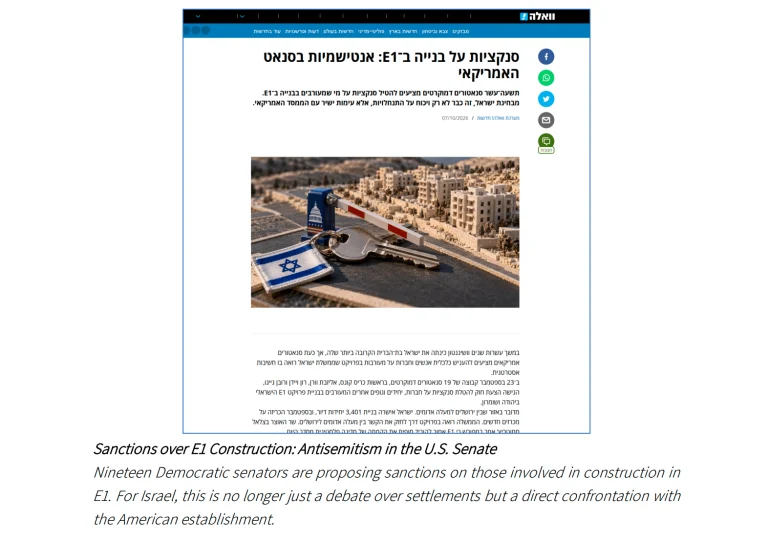
Doppelganger Campaign Targets Israel Elections With Fake News and AI Poisoning Fake news website used in the Doppelganger campaign and Doppelganger campaign in Israel
  • Cybercriminals

Doppelganger Campaign Targets Israel Elections With Fake News and AI Poisoning

Do Son October 23, 2026 0

ClearSky exposed the Russian Doppelganger campaign in Israel using 76 fake Walla articles, 66 redirect domains, and AI poisoning ahead of elections.
BRONZE SANDCASTLE Uses Sandboxie DLL Sideloading to Deploy Modified Meterpreter Backdoor China influence operations using banned ChatGPT accounts in OpenAI's June 2026 threat report targeting the US AI policy debate
  • Malware

BRONZE SANDCASTLE Uses Sandboxie DLL Sideloading to Deploy Modified Meterpreter Backdoor

Do Son October 23, 2026 0

BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.
Quest Diagnostics Data Breach Hits Quanum Lab Services Manager Patient Records Quest Diagnostics data breach - unauthorized access to Quanum Lab Services Manager exposes patient records
  • Data Leak

Quest Diagnostics Data Breach Hits Quanum Lab Services Manager Patient Records

Do Son October 23, 2026 0

Quest Diagnostics data breach: hackers accessed patient records in its Quanum Lab Services Manager. Quest says it is not tied to the PHP flaw.
Oracle Issues Java Security Alert to Distrust Compromised eMudhra Certificates Oracle Java security alert distrusts eMudhra intermediate certificates CVE-2026-91403
  • Vulnerability Report

Oracle Issues Java Security Alert to Distrust Compromised eMudhra Certificates

Do Son October 23, 2026 0

Oracle Java security alert CVE-2026-91403 (CVSS 9.1) distrusts compromised eMudhra intermediate certificates in Java SE and GraalVM. Update now.
Okta Patches Access Gateway Flaws, Including PHP2Shell and Admin Console Bugs Okta Access Gateway vulnerabilities including PHP2Shell and Admin Console flaws
  • Vulnerability Report

Okta Patches Access Gateway Flaws, Including PHP2Shell and Admin Console Bugs

Do Son October 23, 2026 0

Okta fixes four Okta Access Gateway vulnerabilities, including PHP2Shell and CVE-2026-115547 command execution. Upgrade OAG to 2026.44.0.
ZDI Posts Unpatched Linux Kernel Flaw Details and Attack Chains on Public Mailing List Linux kernel vulnerabilities in KSMBD publicly disclosed by ZDI with exploit details
  • Vulnerability Report

ZDI Posts Unpatched Linux Kernel Flaw Details and Attack Chains on Public Mailing List

Do Son October 23, 2026 0

ZDI publicly posted details of unpatched Linux kernel vulnerabilities, including two CVSS 9.0 KSMBD remote code execution flaws. Fixes are pending.
Kiloview E3 NDI Encoder Flaws Allow Root Command Execution, CISA Warns Kiloview E3 vulnerabilities in NDI encoder allow root command injection
  • Vulnerability Report

Kiloview E3 NDI Encoder Flaws Allow Root Command Execution, CISA Warns

Do Son October 23, 2026 0

CISA warns of nine Kiloview E3 vulnerabilities in the NDI encoder, including CVSS 9.9 flaws CVE-2026-107861 and CVE-2026-110243. Update to V1.30.
HPE Patches 72 Flaws in AOS-8 and AOS-10, Including Eight CVSS 10.0 Bugs HPE Networking AOS vulnerabilities in AOS-8 and AOS-10 PAPI protocol fixed by HPE
  • Vulnerability Report

HPE Patches 72 Flaws in AOS-8 and AOS-10, Including Eight CVSS 10.0 Bugs

Do Son October 23, 2026 0

HPE fixes 72 HPE Networking AOS vulnerabilities, including PAPI protocol flaws and CVSS 10 bugs CVE-2026-79844, CVE-2026-79845 and CVE-2026-79846.
Laravel Authentication Bypass PoC Released for Critical TokenGuard Flaw CVE-2026-114509 Laravel authentication bypass in TokenGuard CVE-2026-114509 with public PoC exploit
  • Vulnerability Report

Laravel Authentication Bypass PoC Released for Critical TokenGuard Flaw CVE-2026-114509

Do Son October 23, 2026 0

A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.