Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Keystone Wallet Data Breach Exposes Customer Orders Keystone wallet data breach diagram showing Shopify API order leak and physical wrench attack risks
  • Data Leak

Keystone Wallet Data Breach Exposes Customer Orders

Do Son October 26, 2026 0

A Keystone wallet data breach via Shopify API exposed customer shipping addresses, raising physical wrench attack concerns for crypto holders.
Electrum Wallet Vulnerability Exploits RBF Fee Bumps Electrum wallet vulnerability diagram showing malicious server transaction replacement and RBF exploitation
  • Vulnerability Report

Electrum Wallet Vulnerability Exploits RBF Fee Bumps

Do Son October 26, 2026 0

An unpatched Electrum wallet vulnerability allowed malicious servers to manipulate RBF fee bumps, redirecting bitcoin payments to attacker addresses.
AV2 Video Codec Moves Toward Chrome and YouTube AV2 video codec from AOMedia, successor to AV1, entering browser and YouTube streaming tests with better compression and HDR support
  • Technology

AV2 Video Codec Moves Toward Chrome and YouTube

Do Son October 26, 2026 0

The AV2 video codec promises 30% better compression than AV1. YouTube plans web AV2 streaming in early 2027.
eMudhra Certificate Authority Incident Sparks Rebuke eMudhra certificate authority incident investigation diagram and Google Mozilla trust review
  • Technology

eMudhra Certificate Authority Incident Sparks Rebuke

Do Son October 26, 2026 0

Google and Mozilla criticized the eMudhra certificate authority incident response after the firm blamed social scrutiny for severe investigative delays.
Storybook Fixes CVSS 9.4 Dev Server Flaw That Lets Malicious Sites Inject Code Storybook dev server vulnerability CVE-2026-114125 allows code injection from malicious websites
  • Vulnerability Report

Storybook Fixes CVSS 9.4 Dev Server Flaw That Lets Malicious Sites Inject Code

Do Son October 26, 2026 0

Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
Weekly CVE Report Flags PHP2Shell and FortiSIEM Attacks Still Missing From CISA KEV Weekly CVE report Oct 19-25 2026 exploited vulnerabilities including PHP2Shell and FortiSIEM compared with CISA KEV
  • Weekly Recap

Weekly CVE Report Flags PHP2Shell and FortiSIEM Attacks Still Missing From CISA KEV

Do Son October 26, 2026 0

Our weekly CVE report for Oct 19-25, 2026 tracks 4,222 new CVEs and 12 exploited vulnerabilities, including PHP2Shell flaws not yet in CISA KEV.
Microsoft Ships Out-of-Band .NET Updates for Brotli Overflow and Linux Tarball Flaws .NET security update fixes Brotli buffer overflow CVE-2026-111497 and Linux tarball flaw
  • Vulnerability Report

Microsoft Ships Out-of-Band .NET Updates for Brotli Overflow and Linux Tarball Flaws

Do Son October 26, 2026 0

Microsoft's out-of-band .NET security update fixes Brotli flaw CVE-2026-111497 and Linux tarball bug CVE-2026-114148. Update to 8.0.33 or 9.0.22.
Document Foundation Revisits the OOXML Standard Fight OOXML standardization history: The Document Foundation accuses Microsoft of steering OOXML through ISO, while LibreOffice relies on ODF
  • Technology

Document Foundation Revisits the OOXML Standard Fight

Do Son October 26, 2026 0

OOXML standardization history: The Document Foundation says Microsoft steered ISO approval in 2006-2008. Microsoft disputes such claims.
PingCAP Data Breach Exposes TiDB Cloud Customer Records and Source Code PingCAP data breach illustration highlighting the TiDB Cloud security incident.
  • Data Leak

PingCAP Data Breach Exposes TiDB Cloud Customer Records and Source Code

Do Son October 26, 2026 0

A PingCAP data breach exposed customer records and source code. Learn how the TiDB Cloud security incident happened and how to protect your account.
Apache Camel Fixes Eight Flaws, Including High-Severity XXE in camel-saxon Apache Camel vulnerabilities including XXE flaw CVE-2026-90885 fixed in Camel 4.23.0
  • Vulnerability Report

Apache Camel Fixes Eight Flaws, Including High-Severity XXE in camel-saxon

Do Son October 26, 2026 0

Apache Camel fixes eight Apache Camel vulnerabilities, including XXE flaw CVE-2026-90885 and S3 injection CVE-2026-95664. Upgrade to 4.23.0.
Ruby Fixes Onigmo Regex Bugs Behind Critical GitLab RCE Flaws Ruby security update fixes Onigmo regex flaws behind GitLab CVEs
  • Vulnerability Report

Ruby Fixes Onigmo Regex Bugs Behind Critical GitLab RCE Flaws

Do Son October 26, 2026 0

Ruby security update 4.0.9, 3.4.12 and 3.3.13 fixes Onigmo regex bugs behind GitLab RCE flaws CVE-2026-110264 and CVE-2026-97229. Upgrade now.
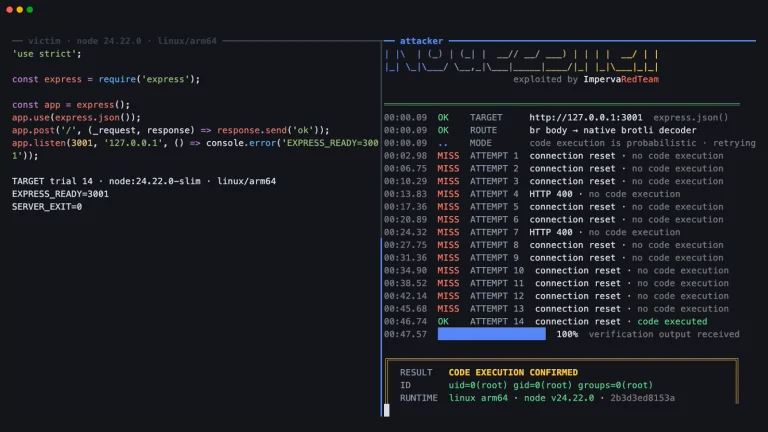
HTTP2Shell Vulnerability Expands Node2Shell Risk HTTP2Shell vulnerability diagram illustrating Brotli decoder memory corruption and remote code execution
  • Vulnerability Report

HTTP2Shell Vulnerability Expands Node2Shell Risk

Do Son October 26, 2026 0

The HTTP2Shell vulnerability expands Node2Shell risks across HTTP stacks, enabling remote code execution via flawed Brotli decompression engines.
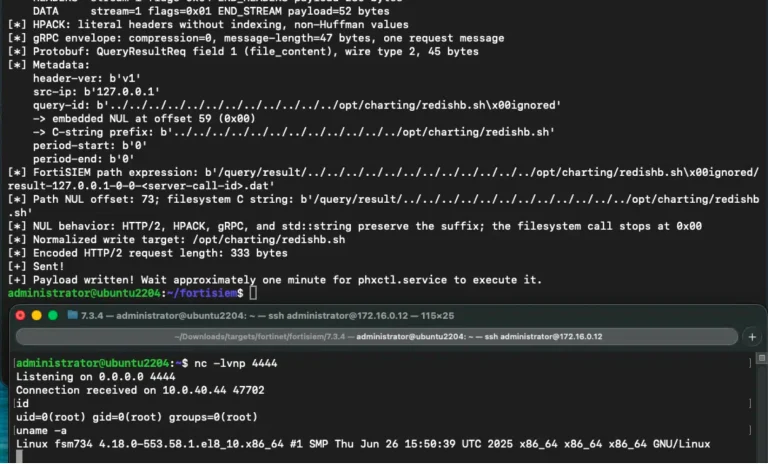
FortiSIEM Flaw CVE-2026-106173 Exploited in the Wild After PoC and Details Go Public FortiSIEM vulnerability CVE-2026-106173 exploited in the wild with public PoC exploit
  • Vulnerability Report

FortiSIEM Flaw CVE-2026-106173 Exploited in the Wild After PoC and Details Go Public

Do Son October 26, 2026 0

FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
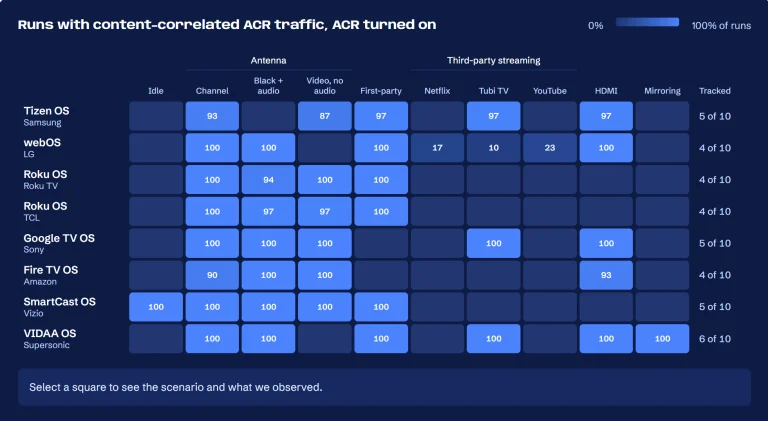
Smart TV ACR Tracking Study Finds Failed Opt-Outs and 57 Million Exposed Viewing Records Smart TV ACR tracking - Northeastern study finds smart TV viewing data exposed and opt-outs failing on Samsung and Vizio
  • Data Leak

Smart TV ACR Tracking Study Finds Failed Opt-Outs and 57 Million Exposed Viewing Records

Do Son October 26, 2026 0

Smart TV ACR tracking survives opt-out on Samsung and Vizio, and an open server exposed smart TV viewing data from over one million TVs.
PHP2Shell: List of Affected Products PHP2Shell affected products list including PAN-OS, QNAP, Cisco and Citrix with fix status
  • Vulnerability Report

PHP2Shell: List of Affected Products

Do Son October 26, 2026 0

PHP2Shell affected products list: vendor patch status for CVE-2026-109618 and CVE-2026-109619 across PAN-OS, QNAP, Cisco, Citrix, F5 and more.
Linux Kernel CVE-2026-43501 (CVSS 9.8) Exploit and Full Details Released for IPv6 RPL Flaw Linux kernel IPv6 vulnerability CVE-2026-43501 in RPL source routing with public exploit
  • Vulnerability Report

Linux Kernel CVE-2026-43501 (CVSS 9.8) Exploit and Full Details Released for IPv6 RPL Flaw

Do Son October 26, 2026 0

A PoC and full details are public for CVE-2026-43501 (CVSS 9.8), a Linux kernel IPv6 vulnerability in RPL source routing. Update your kernel now.
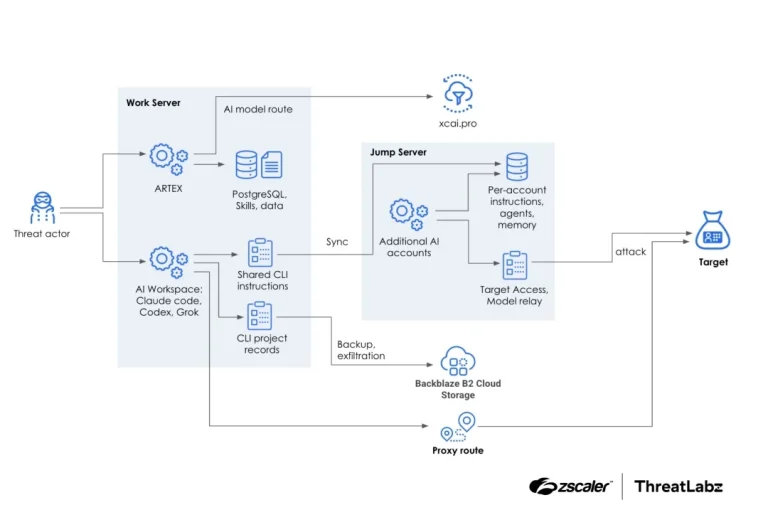
Suspected Chinese Operator Uses ARTEX AI Framework in Global Hacking Campaign ARTEX AI hacking and global ARTEX AI hacking architecture diagram
  • Cybercriminals

Suspected Chinese Operator Uses ARTEX AI Framework in Global Hacking Campaign

Do Son October 25, 2026 0

Zscaler ThreatLabz exposes a global ARTEX AI hacking campaign. See how an operator used ARTEX AI hacking tools, DeepSeek, GLM, and Grok to steal data.
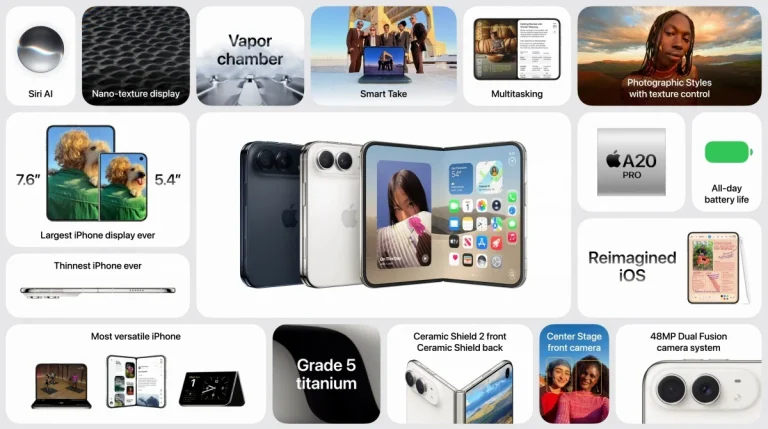
iOS 27.1 iPhone Duo Release Targets Foldable Hardware Apple iOS 27.1 iPhone Duo software update on foldable display showing adaptive UI layout
  • Technology

iOS 27.1 iPhone Duo Release Targets Foldable Hardware

Do Son October 25, 2026 0

Apple launched the iOS 27.1 iPhone Duo update exclusively for its foldable smartphone, introducing adaptive layouts and dedicated SDK tools.
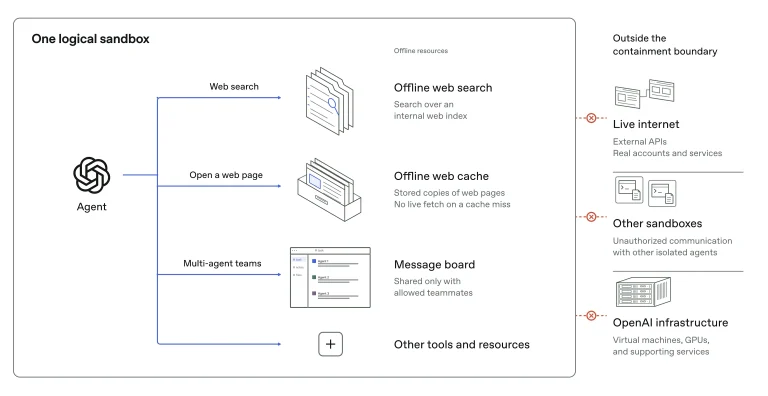
OpenAI Cuts Internet Access for Frontier Model Training OpenAI offline world training environment replacing live internet access, with red-team AI agents testing sandbox escapes in frontier model training
  • Technology

OpenAI Cuts Internet Access for Frontier Model Training

Do Son October 25, 2026 0

OpenAI offline world training replaces live internet access after a September 20 DNS escape paused frontier training for 11 days.
Google Privacy Policy Change Raises Gmail Ad Concerns Google privacy policy change adding an exception for Personal Intelligence, linking Gmail, Drive, and Photos context to AI Mode search ads
  • Technology

Google Privacy Policy Change Raises Gmail Ad Concerns

Do Son October 25, 2026 0

A Google privacy policy change adds an exception to its Gmail ad pledge via Personal Intelligence. See how to turn it off.

Autovado vs. PartsGeek: Which Is Better for Buying Auto Parts Online? ISO 27001
  • Technique

Autovado vs. PartsGeek: Which Is Better for Buying Auto Parts Online?

Do Son October 24, 2026 0
Buying auto parts online can save time, simplify vehicle maintenance and help drivers compare replacement options without...
Read More Read more about Autovado vs. PartsGeek: Which Is Better for Buying Auto Parts Online?
DOJ Extradites Suspect in $36.9M Cambodia Crypto Scam Targeting Americans Law enforcement graphic of the Cambodia crypto scam and Cambodia crypto scam extradition
  • Cybercriminals

DOJ Extradites Suspect in $36.9M Cambodia Crypto Scam Targeting Americans

Do Son October 24, 2026 0

DOJ officials announced a Cambodia crypto scam extradition after Zheng Zhao allegedly helped launder $36.9M stolen from 174 US victims via USDT.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.