Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Breaking the App Shell: Five New Electron Vulnerabilities Shatter Context Isolation Electron Security Sandbox Escape Electron Vulnerabilities, Desktop App Security
  • Vulnerability Report

Breaking the App Shell: Five New Electron Vulnerabilities Shatter Context Isolation

Do Son April 7, 2026 0

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.
Trolling as a Service: How the New CrystalX RAT Uses “Prankware” to Torture Its Victims CrystalX RAT Prankware
  • Malware

Trolling as a Service: How the New CrystalX RAT Uses “Prankware” to Torture Its Victims

Do Son April 7, 2026 0

Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!

BlueHammer: Researcher Drops Functional 0-Day Exploit Targeting Windows Defender BlueHammer Exploit Windows Defender 0-day
  • Vulnerability Report

BlueHammer: Researcher Drops Functional 0-Day Exploit Targeting Windows Defender

Do Son April 7, 2026 0

BlueHammer is a functional 0-day exploit targeting Windows Defender’s update engine to achieve SYSTEM privileges. Here is how the unpatched LPE works.

UAT-10608 Uses a Next.js “React2Shell” Flaw to Map Your Entire Cloud NEXUS Listener React2Shell Vulnerability
  • Cybercriminals

UAT-10608 Uses a Next.js “React2Shell” Flaw to Map Your Entire Cloud

Do Son April 7, 2026 0

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!

The Hidden Hand: Why Adobe is Surreptitiously Modifying Your System Hosts File Adobe Creative Cloud hosts file Adobe Firefly, AI video
  • Technology

The Hidden Hand: Why Adobe is Surreptitiously Modifying Your System Hosts File

Do Son April 7, 2026 0

Adobe is bypassing Chrome security by quietly editing your hosts file to track Creative Cloud installations. Learn how this stealth telemetry works in 2026.

The Evolution of an Infostealer: Xloader 8.7 Unmasked Xloader Malware Information Stealer Phantom Stealer v3.5.0 DLL Sideloading Attack
  • Malware

The Evolution of an Infostealer: Xloader 8.7 Unmasked

Do Son April 7, 2026 0

ThreatLabz unmasks Xloader 8.7, the evolved successor to Formbook. Learn how its advanced obfuscation and decoy C2s bypass modern security defenses.

GPUBreach Rowhammer Hijacks GPUs for Full System Root GPUBreach GPU Rowhammer
  • Vulnerability Report

GPUBreach Rowhammer Hijacks GPUs for Full System Root

Do Son April 7, 2026 0

GPUBreach: A new GPU Rowhammer attack from UofT that bypasses IOMMU and ECC to achieve full system root on NVIDIA systems. GitHub code arrives April 13.
End of an Era: Linux Kernel 7.1 Finally Bids Farewell to the Iconic Intel 486 Linux Kernel 7.1 release Linux Kernel update, AMD ZEN 6 support, Linux driver fixes Linux Kernel 7.1 i486 support Linux 7.0 HIPPI support removal, legacy networking protocol retirement Linus Torvalds AI slop Linux kernel, Lorenzo Stoakes AI tool debate Linux Kernel Rust CVE-2025-68260, Android Binder Rust Race Condition TSEM Security Module Controversy, Linus Torvalds LSM Dispute Kernel Panic, PoC released Linux Kernel 6.16, File System Fixes CVE-2023-42753 - Linux Kernel Developers
  • Linux

End of an Era: Linux Kernel 7.1 Finally Bids Farewell to the Iconic Intel 486

Do Son April 7, 2026 0

After 35 years of support, the Linux Kernel is officially retiring the Intel i486. Linux 7.1 marks the beginning of the end for this ancestral CPU lineage.
Browser Wars 2026: The “Choice Alliance” Slams Microsoft’s Predatory Edge Auto-Launch Browser Choice Alliance Microsoft CVE-2024-30055 Microsoft Edge, Copilot Mode
  • Windows

Browser Wars 2026: The “Choice Alliance” Slams Microsoft’s Predatory Edge Auto-Launch

Do Son April 7, 2026 0

The Browser Choice Alliance, including Chrome and Vivaldi, condemns Microsoft’s new Edge auto-startup as "predatory proselytization." Is Edge a Gatekeeper?
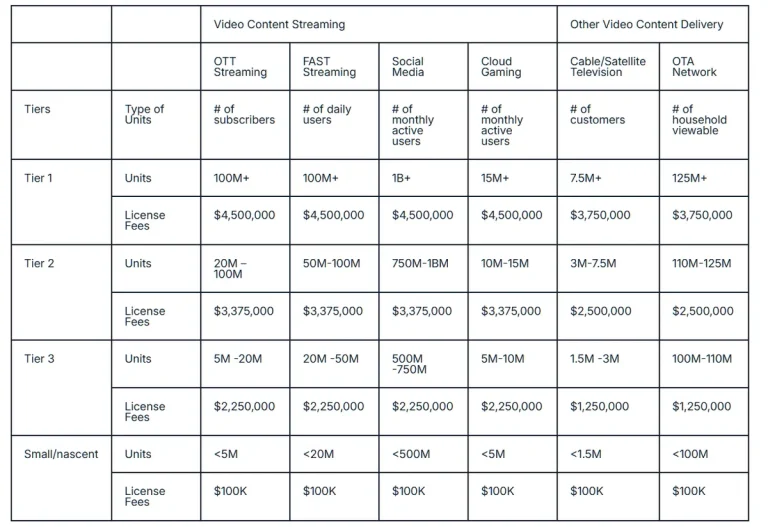
The $4.5 Million Squeeze: How Via LA’s Secret H.264 Fee Hike is Shaking the Streaming Industry Via LA H.264 licensing fees
  • Technology

The $4.5 Million Squeeze: How Via LA’s Secret H.264 Fee Hike is Shaking the Streaming Industry

Do Son April 7, 2026 0

Via LA quietly replaces the $100k H.264 annual cap with a tiered system up to $4.5M. Discover how this 2026 patent pool shift impacts global streaming giants.

The Unkillable Spy: How “Operation NoVoice” Rootkits Hijack Androids and Clone WhatsApp Operation NoVoice Android Rootkit
  • Malware

The Unkillable Spy: How “Operation NoVoice” Rootkits Hijack Androids and Clone WhatsApp

Do Son April 7, 2026 0

McAfee unmasks Operation NoVoice: a sophisticated Android rootkit that survives factory resets to clone WhatsApp sessions and seize full device control.

Android Security Bulletin April 2026: Critical Framework Patch Targets “Zero-Interaction” DoS Vulnerability Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Android
  • Vulnerability Report

Android Security Bulletin April 2026: Critical Framework Patch Targets “Zero-Interaction” DoS Vulnerability

Do Son April 7, 2026 0

Google’s April 2026 Android bulletin fixes a critical zero-interaction DoS in the Framework and high-severity StrongBox HSM flaws. Update your device now.
The Crypto-Con: Unmasking the Multi-Layered “REF1695” Mining Operation CNB Bot Malware REF1695 Threat Actor
  • Malware

The Crypto-Con: Unmasking the Multi-Layered “REF1695” Mining Operation

Do Son April 7, 2026 0

Elastic Security Labs unmasks REF1695, a threat actor using the CNB Bot and custom XMRig loaders for Monero mining and CPA fraud. Is your server a silent miner?

Microsoft Edge Trials Controversial Auto-Startup Without User Consent Microsoft Edge Google account login interface and synchronization settings Browser Choice Alliance letter Microsoft Edge cleartext credentials memory dump Microsoft Edge auto-startup Microsoft Edge Collections sunset, export Edge Collections CSV Edge IE Mode Zero-Day, Chakra Exploit Windows Search, Microsoft Edge AI video translation, Edge browser Microsoft Editor, Edge Edge Developer tools Windows 10 ESU, Microsoft Edge Microsoft Edge, FCP Optimization CVE-2023-36735 Edge, AI Search
  • Windows

Microsoft Edge Trials Controversial Auto-Startup Without User Consent

Do Son April 7, 2026 0

Microsoft Edge 147 Beta is testing a new "Auto-Startup" feature that launches the browser on boot without asking. Learn how to disable this 2026 update.

The 2026 Deadline: Microsoft Confirms Mandatory Upgrades as Windows 11 24H2 Reaches End of Life KB5083769 Update Windows 11 24H2 end of support File Explorer White Flash Windows 11 Dark Mode Bug Windows 11 SE, End of Support Windows Update, Automatic Upgrade CVE-2023-38146 Windows 10
  • Windows

The 2026 Deadline: Microsoft Confirms Mandatory Upgrades as Windows 11 24H2 Reaches End of Life

Do Son April 7, 2026 0

Windows 11 24H2 support ends October 13, 2026. Microsoft is preparing mandatory updates to version 25H2 for Home and Pro users to ensure continued security.

WhatsApp Under Siege: Microsoft Uncovers Global VBS Malware Campaign WhatsApp VBS Malware Living-off-the-Land (LotL)
  • Malware

WhatsApp Under Siege: Microsoft Uncovers Global VBS Malware Campaign

Do Son April 7, 2026 0

Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!

Goodbye ViveTool: Microsoft Unveils Native “Feature Flags” to Unlock Hidden Windows 11 Powers Windows 11 Feature Flags
  • Windows

Goodbye ViveTool: Microsoft Unveils Native “Feature Flags” to Unlock Hidden Windows 11 Powers

Do Son April 7, 2026 0

Microsoft introduces native "Feature Flags" in Windows 11 Dev Build 26300. Unlock hidden experimental features safely without needing third-party tools like ViveTool.

Apple Appeals to the Supreme Court as the Fortnite War Hits a Breaking Point Apple vs Epic Supreme Court Apple App Store Guidelines update Apple Clips Discontinued, Video App EOL Apple EU DMA
  • Technology

Apple Appeals to the Supreme Court as the Fortnite War Hits a Breaking Point

Do Son April 7, 2026 0

Apple makes a "last stand" at the Supreme Court over App Store fees, while Epic Games strikes a silent truce with Google to focus on its greatest adversary.
The Vibe Coding Paradox: Why Software Job Vacancies are Hitting a 3-Year High in the AI Era Codex rate limit reset OpenAI Codex limits, flexible rate limit resets, Codex vs Claude Code Vibe coding software engineer jobs OpenAI Codex for Open Source
  • Technology

The Vibe Coding Paradox: Why Software Job Vacancies are Hitting a 3-Year High in the AI Era

Do Son April 7, 2026 0

Software engineer vacancies have surged 30% in 2026. Discover how "vibe coding" and AI-generated technical debt are creating a massive new demand for human devs.
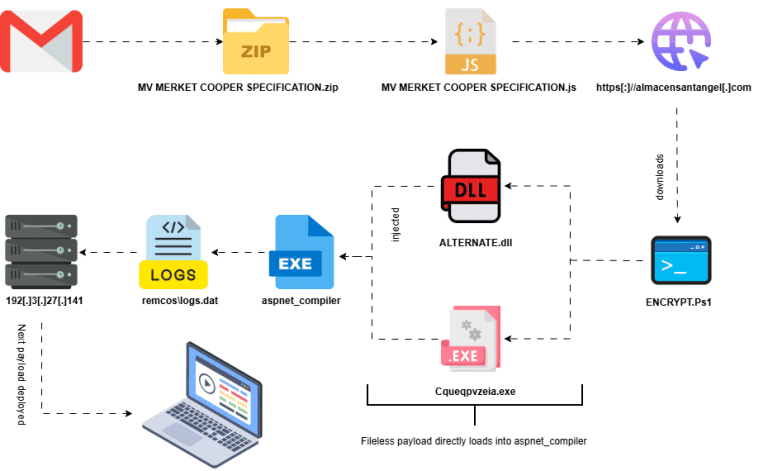
Fileless Remcos RAT Hijacks Trusted Windows Tools Remcos RAT Fileless Malware
  • Malware

Fileless Remcos RAT Hijacks Trusted Windows Tools

Do Son April 7, 2026 0

Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.
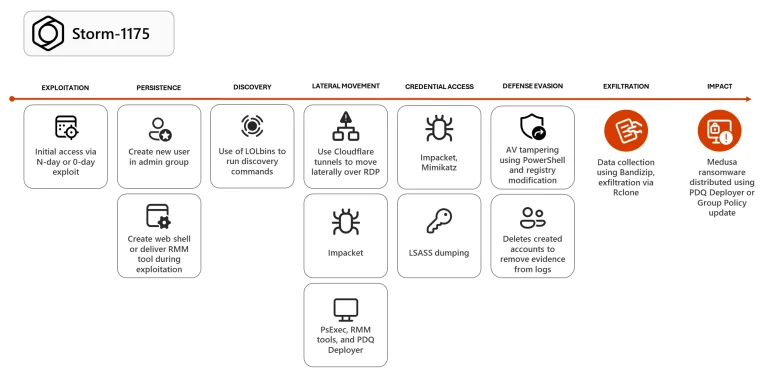
The 24-Hour Blitz: Storm-1175 Weaponizes Zero-Days for High-Velocity Ransomware Storm-1175 Medusa Ransomware
  • Vulnerability Report

The 24-Hour Blitz: Storm-1175 Weaponizes Zero-Days for High-Velocity Ransomware

Do Son April 6, 2026 0

Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.

Ninja Forms Alert: Critical 9.8 RCE Vulnerability Under Active Attack Ninja Forms RCE WordPress Vulnerability
  • Vulnerability Report

Ninja Forms Alert: Critical 9.8 RCE Vulnerability Under Active Attack

Do Son April 6, 2026 0

A critical 9.8 CVSS flaw in Ninja Forms - File Upload plugin allows unauthenticated RCE. 50,000+ WordPress sites are at risk. Update to v3.3.27 now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-63939CVSS 9.8
    Improper input handling in /Grocery/search_products_itname.php, in anirudhkannan Grocery Store Management System 1.0, allows SQL injection via the sitem_name...
    📅 Updated: Nov 4, 2026
  • CVE-2025-65133CVSS 9.8
    A SQL injection vulnerability exists in the School Management System (version 1.0) by manikandan580. An unauthenticated or authenticated...
    📅 Updated: Nov 4, 2026
  • CVE-2025-65135CVSS 9.8
    In manikandan580 School-management-system 1.0, a time-based blind SQL injection vulnerability exists in /studentms/admin/between-date-reprtsdetails.php through the fromdate POST parameter.
    📅 Updated: Nov 4, 2026
  • CVE-2025-70023CVSS 9.8
    An issue pertaining to CWE-843: Access of Resource Using Incompatible Type was discovered in transloadit uppy v0.25.6.
    📅 Updated: Nov 4, 2026
  • CVE-2025-70067CVSS 9.8
    Buffer Overflow vulnerability exists in Assimp versions up to 6.0.2 in the FBX Importer. The vulnerability occurs in...
    📅 Updated: Nov 4, 2026
  • CVE-2025-63703CVSS 9.8
    npm package parse-ini v1.0.6 is vulnerable to Prototype Pollution in index.js().
    📅 Updated: Nov 4, 2026
  • CVE-2025-63704CVSS 9.8
    NPM package query-parser-string 1.0.0 is vulnerable to Prototype Pollution. The package does not properly sanitize user supplied query...
    📅 Updated: Nov 4, 2026
  • CVE-2025-67887CVSS 9.8
    1C-Bitrix through 25.100.500 allows Remote Code Execution because an actor with SOURCE/WRITE permissions for the Translate Module can...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.