Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Keycloak Under Siege: Patch Now to Stop Token Theft and Account Takeovers Keycloak vulnerabilities Keycloak Security MFA Bypass
  • Vulnerability Report

Keycloak Under Siege: Patch Now to Stop Token Theft and Account Takeovers

Do Son April 6, 2026 0

Keycloak 26.5.7 fixes an MFA bypass that could let attackers skip two-factor checks. Upgrade your identity server to close the gap.

CVE-2026-34838 (CVSS 10): Critical RCE Flaw Uncovered in GroupOffice CRM GroupOffice RCE, Insecure Deserialization
  • Vulnerability Report

CVE-2026-34838 (CVSS 10): Critical RCE Flaw Uncovered in GroupOffice CRM

Do Son April 6, 2026 0

CVE-2026-34838: A critical 10.0 flaw in GroupOffice allows authenticated users to trigger RCE via insecure deserialization. Update to v26.0.12 immediately!
Critical RCE and SQLi Flaws Shatter mbCONNECT24 Industrial Security mbCONNECT24 Vulnerabilities Industrial RCE
  • Vulnerability Report

Critical RCE and SQLi Flaws Shatter mbCONNECT24 Industrial Security

Do Son April 6, 2026 0

CERT@VDE warns of critical RCE and SQLi flaws in MB Connect Line's mbCONNECT24 (up to v2.19.4). Unauthenticated attackers can gain full system control. Patch now!

Whitespace Flaw Re-Opens Critical JWT “Algorithm Confusion” Bypass fast-jwt JWT Algorithm Confusion
  • Vulnerability Report

Whitespace Flaw Re-Opens Critical JWT “Algorithm Confusion” Bypass

Do Son April 6, 2026 0

CVE-2026-34950: A critical 9.1 CVSS flaw in fast-jwt allows authentication bypass via leading whitespace. Learn how a regex error leads to algorithm confusion.

Speeding Up the Web: Chrome 148 Extends “Lazy Loading” to Video and Audio Tags Chrome 148 lazy loading Chrome for Linux ARM64 Chrome 145 Update Chrome Security Fixes Chrome Security Update CVE-2026-1220 Chrome 144 Security Update CVE-2026-0899 Chrome Memory Safety, WebGPU UAF Chrome V8 Type Confusion, Google Updater Flaw Chrome V8 Flaw, CVE-2025-13042 Chrome V8, Type Confusion, Chrome 142 Update Chrome V8 Flaw, CVE-2025-12036 Chrome 141, WebGPU Overflow Google Chrome preloading Chrome, V8 vulnerability CVE-2025-9132 Chrome Security Update, Use-After-Free Chrome V8, Type Confusion Chrome Telemetry, Windows 10 EOL Microsoft Family Safety, Chrome Blocking Chrome Security Update, High-Severity Google Chrome, Antitrust CVE-2024-10487 and CVE-2024-10488 Google Chrome Root Program Chrome Update, CVE-2025-3619 Chrome Acquisition, Perplexity.ai
  • Technology

Speeding Up the Web: Chrome 148 Extends “Lazy Loading” to Video and Audio Tags

Do Son April 6, 2026 0

Google Chrome 148 introduces native "Lazy Loading" for video and audio tags. Save bandwidth and boost loading speeds with this essential 2026 web update.

Exploit Code Live: Full Technical Details and PoC Disclosed for Critical CWP RCE Vulnerability CWP RCE PoC Disclosed
  • Vulnerability

Exploit Code Live: Full Technical Details and PoC Disclosed for Critical CWP RCE Vulnerability

Do Son April 6, 2026 0

Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!

Iran-Linked “Password Spraying” Targets Municipal Response to Missile Strikes Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security

Iran-Linked “Password Spraying” Targets Municipal Response to Missile Strikes

Do Son April 6, 2026 0

Check Point Research uncovers an Iran-linked password spraying campaign targeting M365 to support kinetic missile strikes and damage assessment in the ME.

Double Agents in the Cloud: Unit 42 Unmasks Critical AI Vulnerabilities in Google Vertex AI Vertex AI Security AI Double Agents
  • Vulnerability Report

Double Agents in the Cloud: Unit 42 Unmasks Critical AI Vulnerabilities in Google Vertex AI

Do Son April 6, 2026 0

Unit 42 reveals how GCP Vertex AI agents can become "double agents," exfiltrating data and accessing Google’s internal code. Learn why BYOSA is essential.

The “Special Invitation” Trap: STAC6405 Abuses Legitimate RMM Tools to Hijack Your PC STAC6405 Phishing RMM Abuse
  • Cybercriminals

The “Special Invitation” Trap: STAC6405 Abuses Legitimate RMM Tools to Hijack Your PC

Do Son April 6, 2026 0

Sophos MDR uncovers STAC6405, a phishing campaign abusing RMM tools like LogMeIn for unattended access. Learn how to spot the "Special Invitation" lure.

Operation DualScript Bypasses Defenses to Hijack Crypto and Cash AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Malware

Operation DualScript Bypasses Defenses to Hijack Crypto and Cash

Do Son April 6, 2026 0

Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.

The DNS Trap: How a “Hidden” Path Allowed ChatGPT to Silently Leak Your Private Data ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Data Leak

The DNS Trap: How a “Hidden” Path Allowed ChatGPT to Silently Leak Your Private Data

Do Son April 6, 2026 0

Check Point Research uncovers a DNS tunneling flaw in ChatGPT allowing silent data theft. OpenAI deployed a fix on Feb 20, 2026. Is your AI chat truly private?

ResokerRAT Uses Telegram to Hijack Your PC and Disable Your Security Keys GuLoader Malware CloudEye Obfuscation npm, malware Ethereum, npm supply chain OAST techniques StilachiRAT macOS Malware PasivRobber
  • Malware

ResokerRAT Uses Telegram to Hijack Your PC and Disable Your Security Keys

Do Son April 6, 2026 0

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?
The Python Predator: PXA Stealer Surges 10% as it Targets Global Finance and Crypto in 2026 PXA Stealer Surge Q1 2026 Malware Trends
  • Malware

The Python Predator: PXA Stealer Surges 10% as it Targets Global Finance and Crypto in 2026

Do Son April 6, 2026 0

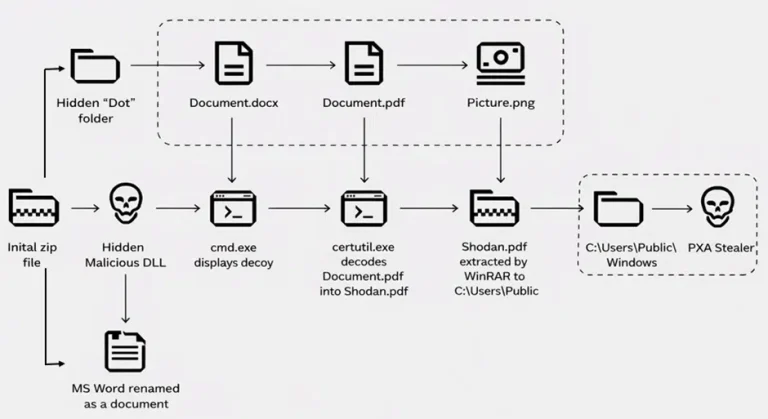
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.

The CVE Watchtower: Weekly Threat Intelligence Briefing (March 30 – April 5, 2026) Vulnerability Digest Zero-Day Exploits Seedworm APT Dindoor Backdoor RedKitten Campaign AI-Generated Malware WSUS RCE ShadowPad CVE-2025-59287
  • Weekly Recap

The CVE Watchtower: Weekly Threat Intelligence Briefing (March 30 – April 5, 2026)

Do Son April 6, 2026 0

1,361 vulnerabilities found this week: 129 are critical. Prioritize Chrome’s Dawn exploit, FortiClient EMS, and new AI pipeline attacks. Get the full list.

The $17 Million Bounty: Google Smashes Records and Launches AI Frontier for 15th VRP Anniversary Google VRP 2025 Bug Bounty Records
  • Vulnerability Report

The $17 Million Bounty: Google Smashes Records and Launches AI Frontier for 15th VRP Anniversary

Do Son April 5, 2026 0

Google’s 2025 VRP hit an all-time high with $17.1M in payouts. Discover how the new AI VRP and elite bugSWAT events are shaping the future of security.

Zero Authentication, Total Control: Critical CVSS 10 Flaw Uncovered in Dgraph Database Dgraph Vulnerability CVSS 10.0 Dgraph Admin Leak CVE-2026-40173
  • Vulnerability Report

Zero Authentication, Total Control: Critical CVSS 10 Flaw Uncovered in Dgraph Database

Do Son April 5, 2026 2

Dgraph patches a critical 10.0 CVSS flaw (CVE-2026-33976). Unauthenticated attackers can overwrite databases and read local files. Update to v25.3.1 now!

Hackers are Using “Legit” IT Tools to Hijack the 2026 Tax Season 2026 Tax Phishing RMM Abuse
  • Cybercriminals

Hackers are Using “Legit” IT Tools to Hijack the 2026 Tax Season

Do Son April 5, 2026 0

Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

Under Active Attack: Critical 9.1 CVSS FortiClient EMS Flaw Exploited in the Wild Knowledge Deliver RCE vulnerability FortiClient EMS Vulnerability CVE-2026-35616 Cisco SD-WAN Vulnerability CVE-2026-20122 PCPcat, Next.js RCE Salesloft breach, Salesforce CRM WIREFIRE web shell
  • Vulnerability Report

Under Active Attack: Critical 9.1 CVSS FortiClient EMS Flaw Exploited in the Wild

Do Son April 4, 2026 0

Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!

Apache Traffic Server Patches “Double-Header” DoS and Request Smuggling Flaws Apache Traffic Server Vulnerabilities CVE-2024-56195 and CVE-2024-56196
  • Vulnerability Report

Apache Traffic Server Patches “Double-Header” DoS and Request Smuggling Flaws

Do Son April 3, 2026 0

Apache Traffic Server fixes two CVSS 7.5 flaws (CVE-2025-58136 & CVE-2025-65114). Prevent DoS and request smuggling—update to 10.1.2 or 9.2.13 now!
Password Hijack in the Modern Stack: Payload CMS Patches Critical 9.1 CVSS Reset Flaw Payload CMS Vulnerability CVE-2026-34751
  • Vulnerability Report

Password Hijack in the Modern Stack: Payload CMS Patches Critical 9.1 CVSS Reset Flaw

Do Son April 3, 2026 0

Payload CMS fixes a critical 9.1 CVSS flaw (CVE-2026-34751) in its password reset flow. Attackers could hijack accounts. Update to v3.79.1 immediately!

CVE-2026-4370 (CVSS 10): Critical Juju Flaw Grants Attackers Total Infrastructure Control Juju Orchestration Cloud Credential Theft Juju Orchestration Vulnerability CVE-2026-4370
  • Vulnerability Report

CVE-2026-4370 (CVSS 10): Critical Juju Flaw Grants Attackers Total Infrastructure Control

Do Son April 3, 2026 0

Juju hits a perfect 10.0 CVSS score (CVE-2026-4370). A TLS flaw on port 17666 lets attackers hijack clusters. Update to 3.6.20 or 4.0.5 now!

Breaking the Input: Sandbox Escape Hits libinput, Exposing Leading Linux Desktops libinput Sandbox Escape CVE-2026-35093
  • Vulnerability Report

Breaking the Input: Sandbox Escape Hits libinput, Exposing Leading Linux Desktops

Do Son April 3, 2026 0

Critical 8.8 CVSS flaw in libinput allows sandbox escape via malicious Lua plugins. Affects GNOME, KDE, and Fedora. Update to 1.31.1 or 1.30.3 now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-63939CVSS 9.8
    Improper input handling in /Grocery/search_products_itname.php, in anirudhkannan Grocery Store Management System 1.0, allows SQL injection via the sitem_name...
    📅 Updated: Nov 4, 2026
  • CVE-2025-65133CVSS 9.8
    A SQL injection vulnerability exists in the School Management System (version 1.0) by manikandan580. An unauthenticated or authenticated...
    📅 Updated: Nov 4, 2026
  • CVE-2025-65135CVSS 9.8
    In manikandan580 School-management-system 1.0, a time-based blind SQL injection vulnerability exists in /studentms/admin/between-date-reprtsdetails.php through the fromdate POST parameter.
    📅 Updated: Nov 4, 2026
  • CVE-2025-70023CVSS 9.8
    An issue pertaining to CWE-843: Access of Resource Using Incompatible Type was discovered in transloadit uppy v0.25.6.
    📅 Updated: Nov 4, 2026
  • CVE-2025-70067CVSS 9.8
    Buffer Overflow vulnerability exists in Assimp versions up to 6.0.2 in the FBX Importer. The vulnerability occurs in...
    📅 Updated: Nov 4, 2026
  • CVE-2025-63703CVSS 9.8
    npm package parse-ini v1.0.6 is vulnerable to Prototype Pollution in index.js().
    📅 Updated: Nov 4, 2026
  • CVE-2025-63704CVSS 9.8
    NPM package query-parser-string 1.0.0 is vulnerable to Prototype Pollution. The package does not properly sanitize user supplied query...
    📅 Updated: Nov 4, 2026
  • CVE-2025-67887CVSS 9.8
    1C-Bitrix through 25.100.500 allows Remote Code Execution because an actor with SOURCE/WRITE permissions for the Translate Module can...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.